
google/oss-fuzz
google/oss-fuzz has 12,949 GitHub stars and 2,992 forks. GitHot measured +4 stars in 24 hours and +30 in 7 days. Last checked 2026-11-12 17:13 UTC. Last push 2026-11-04.
OSS-Fuzz——面向开源软件的持续模糊测试。
实测星标增长
- 24小时
- +4
- 7天
- +30
- 15天
- 正在收集历史
- 1个月
- 正在收集历史
各周期内的星标净变化,周期相互重叠,并非每日新增。缺失的测量保持空白。星标代表关注度,不代表软件质量。
README.md
原文OSS-Fuzz: Continuous Fuzzing for Open Source Software
Fuzz testing is a well-known technique for uncovering programming errors in software. Many of these detectable errors, like buffer overflow, can have serious security implications. Google has found thousands of security vulnerabilities and stability bugs by deploying guided in-process fuzzing of Chrome components, and we now want to share that service with the open source community.
In cooperation with the Core Infrastructure Initiative and the OpenSSF, OSS-Fuzz aims to make common open source software more secure and stable by combining modern fuzzing techniques with scalable, distributed execution. Projects that do not qualify for OSS-Fuzz (e.g. closed source) can run their own instances of ClusterFuzz or ClusterFuzzLite.
We support the libFuzzer, AFL++, and Honggfuzz fuzzing engines in combination with Sanitizers, as well as ClusterFuzz, a distributed fuzzer execution environment and reporting tool.
Currently, OSS-Fuzz supports C/C++, Rust, Go, Python, Java/JVM, JavaScript and Lua code. Other languages supported by LLVM may work too. OSS-Fuzz supports fuzzing x86_64 and i386 builds.
Overview
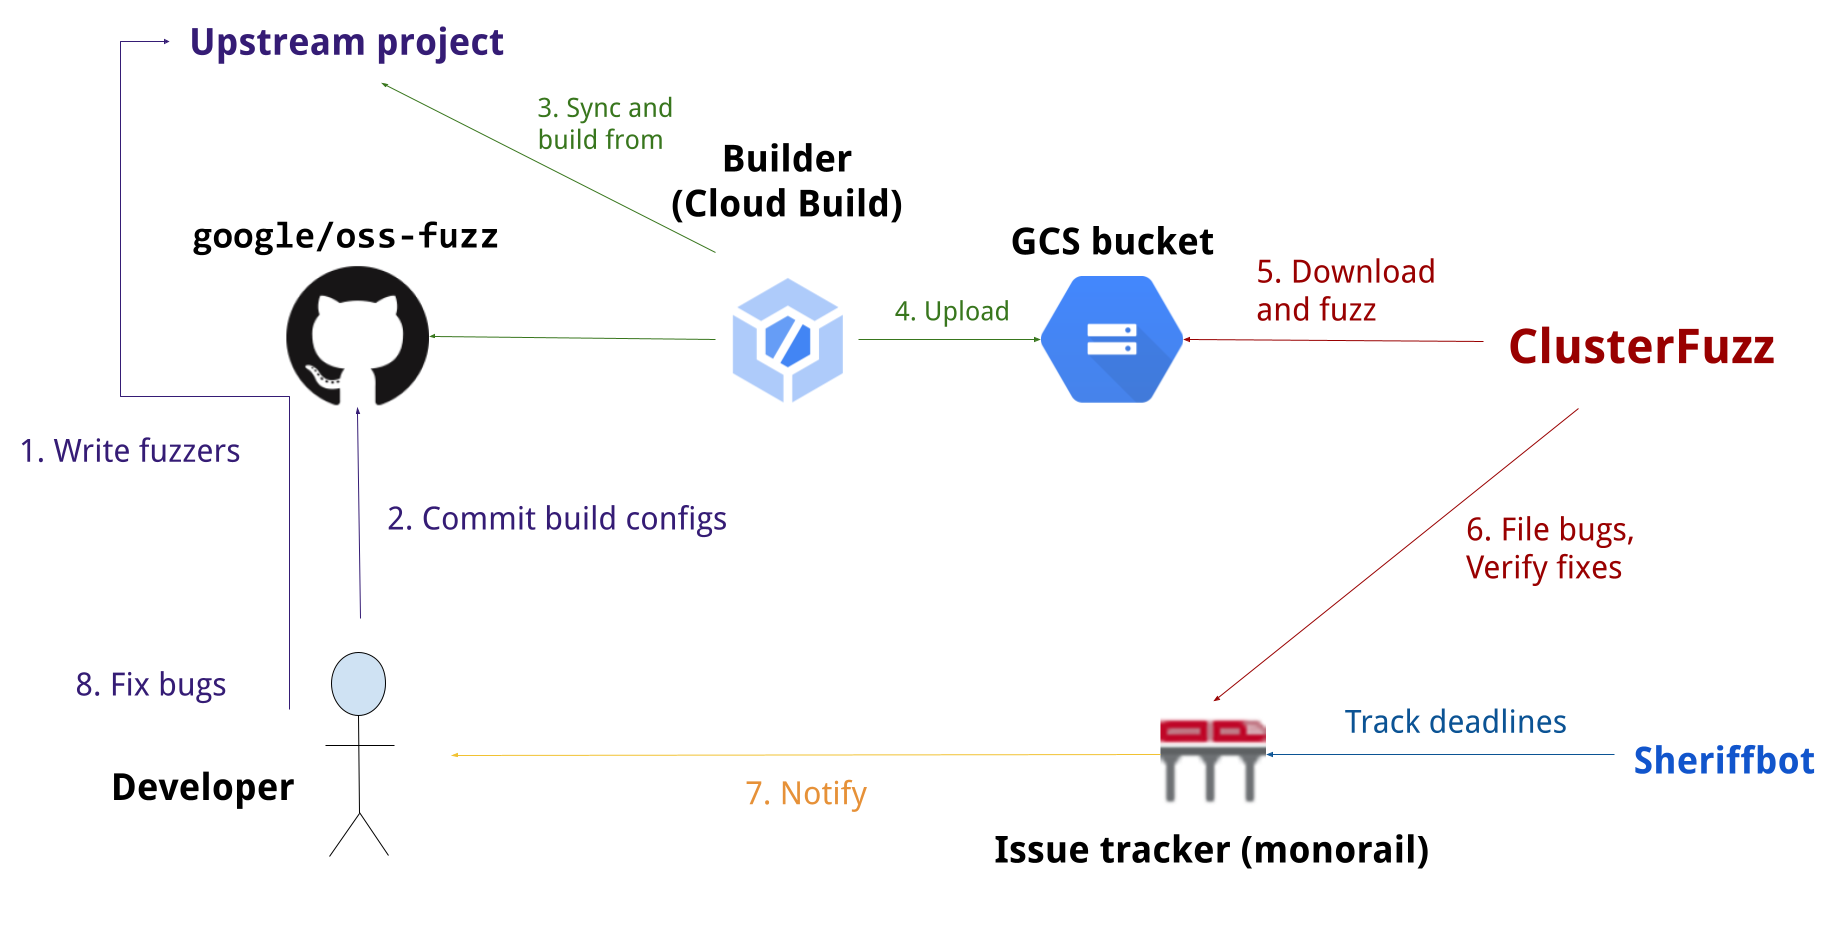
Documentation
Read our detailed documentation to learn how to use OSS-Fuzz.
Trophies
As of May 2025, OSS-Fuzz has helped identify and fix over 13,000 vulnerabilities and 50,000 bugs across 1,000 projects.
Blog posts
- 2024-11-20 - Leveling Up Fuzzing: Finding more vulnerabilities with AI
- 2023-08-16 - AI-Powered Fuzzing: Breaking the Bug Hunting Barrier
- 2023-02-01 - Taking the next step: OSS-Fuzz in 2023
- 2022-09-08 - Fuzzing beyond memory corruption: Finding broader classes of vulnerabilities automatically
- 2021-12-16 - Improving OSS-Fuzz and Jazzer to catch Log4Shell
- 2021-03-10 - Fuzzing Java in OSS-Fuzz
- 2020-12-07 - Improving open source security during the Google summer internship program
- 2020-10-09 - Fuzzing internships for Open Source Software
- 2018-11-06 - A New Chapter for OSS-Fuzz
- 2017-05-08 - OSS-Fuzz: Five months later, and rewarding projects
- 2016-12-01 - Announcing OSS-Fuzz: Continuous fuzzing for open source software
探索相关项目
trimstray/the-book-of-secret-knowledge
汇集各类启发灵感的清单、手册、速查表、博客、技巧、单行命令、CLI/Web 工具等内容。
257,996 星标Hack-with-Github/Awesome-Hacking
面向黑客、渗透测试人员与安全研究人员的各类 Awesome 清单合集。
125,360 星标swisskyrepo/PayloadsAllTheThings
一份用于 Web 应用安全以及渗透测试/CTF 的实用 payload 与绕过方法列表。
82,623 星标caddyserver/caddy
快速、可扩展的跨平台 HTTP/1-2-3 Web 服务器,支持自动 HTTPS
79,020 星标