
aquasecurity/trivy
aquasecurity/trivy has 39,110 GitHub stars and 835 forks. GitHot measured +22 stars in 24 hours, +212 in 7 days, +421 in 15 days, and +796 in 30 days. Last checked 2026-11-08 08:43 UTC. Last push 2026-11-01.
在容器、Kubernetes、代码仓库、云等环境中查找漏洞、错误配置、密钥和 SBOM。
实测星标增长
- 24小时
- +22
- 7天
- +212
- 15天
- +421
- 1个月
- +796
各周期内的星标净变化,周期相互重叠,并非每日新增。缺失的测量保持空白。星标代表关注度,不代表软件质量。
README.md
原文


Trivy (pronunciation) is a comprehensive and versatile security scanner. Trivy has scanners that look for security issues, and targets where it can find those issues.
Targets (what Trivy can scan):
- Container Image
- Filesystem
- Git Repository (remote)
- Virtual Machine Image
- Kubernetes
Scanners (what Trivy can find there):
- OS packages and software dependencies in use (SBOM)
- Known vulnerabilities (CVEs)
- IaC issues and misconfigurations
- Sensitive information and secrets
- Software licenses
Trivy supports most popular programming languages, operating systems, and platforms. For a complete list, see the Scanning Coverage page.
To learn more, go to the Trivy homepage for feature highlights, or to the Documentation site for detailed information.
Quick Start
Get Trivy
Trivy is available in most common distribution channels. The full list of installation options is available in the Installation page. Here are a few popular examples:
brew install trivydocker run aquasec/trivy- Download binary from https://github.com/aquasecurity/trivy/releases/latest/
- See Installation for more
Trivy is integrated with many popular platforms and applications. The complete list of integrations is available in the Ecosystem page. Here are a few popular examples:
- GitHub Actions
- Kubernetes operator
- VS Code plugin
- See Ecosystem for more
Canary builds
There are canary builds (Docker Hub, GitHub, ECR images and binaries) generated with every push to the main branch.
Please be aware: canary builds might have critical bugs, so they are not recommended for use in production.
General usage
trivy <target> [--scanners <scanner1,scanner2>] <subject>
Examples:
trivy image python:3.4-alpine
trivy fs --scanners vuln,secret,misconfig myproject/
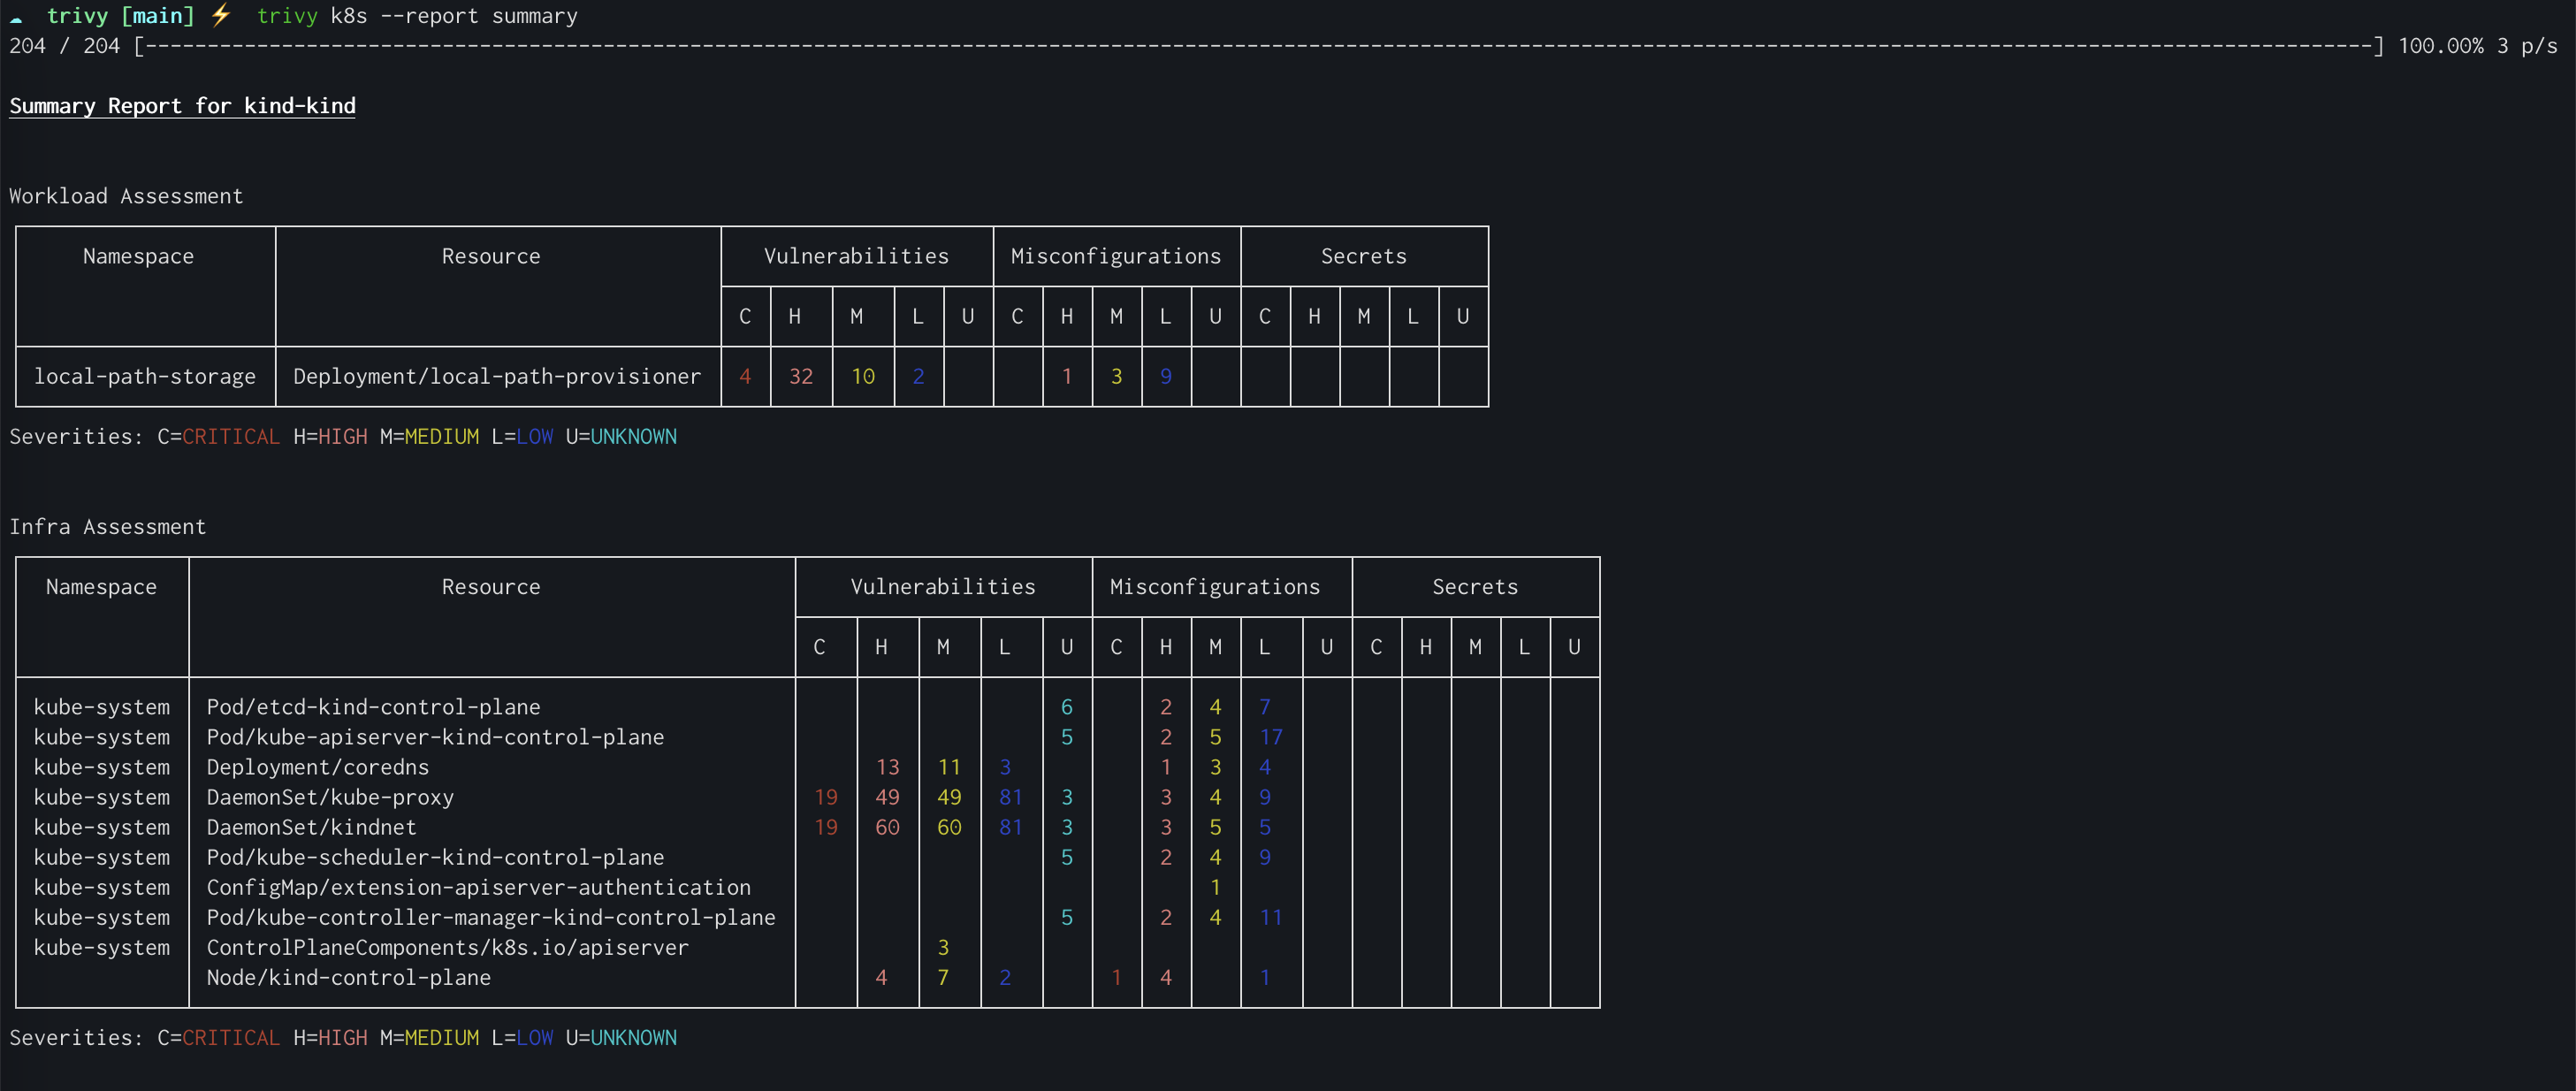
trivy k8s --report summary cluster
Result
FAQ
How to pronounce the name "Trivy"?
tri is pronounced like trigger, vy is pronounced like envy.
Want more? Check out Aqua
If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering.
You can find a high level comparison table specific to Trivy users here.
In addition check out the https://aquasec.com website for more information about our products and services.
If you'd like to contact Aqua or request a demo, please use this form: https://www.aquasec.com/demo
Community
Trivy is an Aqua Security open source project.
Learn about our open source work and portfolio here.
Contact us about any matter by opening a GitHub Discussion here
Please ensure to abide by our Code of Conduct during all interactions.
探索相关项目
trimstray/the-book-of-secret-knowledge
汇集各类启发灵感的清单、手册、速查表、博客、技巧、单行命令、CLI/Web 工具等内容。
256,966 星标Hack-with-Github/Awesome-Hacking
面向黑客、渗透测试人员与安全研究人员的各类 Awesome 清单合集。
125,014 星标swisskyrepo/PayloadsAllTheThings
一份用于 Web 应用安全以及渗透测试/CTF 的实用 payload 与绕过方法列表。
82,475 星标caddyserver/caddy
快速、可扩展的跨平台 HTTP/1-2-3 Web 服务器,支持自动 HTTPS
78,878 星标