
zahidoverflow/viperclaw
zahidoverflow/viperclaw has 7 GitHub stars and 2 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-15 11:43 UTC. Last push 2026-11-09.
Measured star growth
- in 24h
- 0
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
AI Pentesting Framework, Bug Bounty MCP Server, SAST/DAST Taint Engine & 12 Offensive Security Skills for Claude Code, Google Antigravity, Codex & Cursor.
SecurityREADME.md
Original




ViperClaw (viperclaw / vclaw) upgrades Google Antigravity, Claude Code, OpenAI Codex, and Cursor into a methodology-driven offensive security & bug bounty platform—combining 14 offensive skills, a 13-tool Phase-Gated MCP server, a BrowserOS Neo session bridge, a Stigmergic SQLite Attack Graph, Race / JWT / GraphQL / OOB / SAST / DAST engines, and a deterministic Proof Oracle with zero third-party runtime dependencies.
Website • User Guide • Quickstart • Architecture • CLI & MCP • 14 Skills • Benchmarks
⚡ Why ViperClaw?
Most "AI pentesting wrappers" fail in production: dumping 150+ noisy CLI scanners into an LLM causes context-window rot and instant WAF blocks, while monolithic Docker stacks require 4–6 containers and separate API budgets when you already run a frontier coding agent locally.
ViperClaw pairs 14 methodology-driven playbooks with 10 zero-dependency Python 3.10+ offensive engines and a strict "No Receipt, No Report" Proof Oracle:
| Core Subsystem | Capability & Implementation |
|---|---|
| 🕸️ Stigmergic Graph | Zero-setup SQLite knowledge graph with pheromone priority scoring, decay & Mermaid topology export. |
| 🌐 BrowserOS & Live DAST | Bridges signed-in BrowserOS Neo tabs (fetch/XHR hooks, JWTs, storage) + 14 wire-verified HTTP exploit probes. |
| ⚡ Barrier Race Engine | Pre-connected socket pool synchronized via threading.Barrier to prove TOCTOU double-spend & coupon overruns. |
| 🔑 JWT & GraphQL Engines | HMAC secret cracker, alg:none / kid / RS256→HS256 token forger, plus GraphQL Clairvoyance & batching probes. |
| 📡 OOB & JS Harvester | HMAC-tagged blind OOB canary matrix + ephemeral callback listener, plus Webpack / Vite / Next.js lazy-chunk reconstruction. |
| 🔬 Taint SAST & Oracle | Multi-hop taint SAST (Python, TS/JS, Go, PHP) + 7-Gate Proof Oracle (WAF Soft-200 filter, BOLA diff, CVSS 3.1, SARIF 2.1.0). |
🚀 Quickstart
📘 New to ViperClaw? Read the complete step-by-step Beginner-to-Pro User Guide (
docs/README.md).
# 1. Clone & install (<2 seconds, zero external dependencies, Python 3.10+)
git clone https://github.com/zahidoverflow/viperclaw.git
cd viperclaw
pip install -e .

# 2. Install all 14 offensive skills into Antigravity, Claude Code, Codex & Cursor
viperclaw skills install --target all
🔌 Connect the Phase-Gated MCP Server (mcp_config.json / Claude Code / Cursor)
Add viperclaw mcp to your agent's mcp_config.json / .mcp.json (or run claude mcp add viperclaw -- viperclaw mcp):
{
  "mcpServers": {
    "viperclaw": {
      "command": "viperclaw",
      "args": ["mcp"]
    }
  }
}
- Single-Harness Skill Install: Use
--target antigravity,--target claude,--target codex, or--target cursor. - Claude Code Plugin Marketplace: Run
/plugin marketplace add zahidoverflow/viperclawthen/plugin install viperclaw@viperclaw.
🧬 Architecture
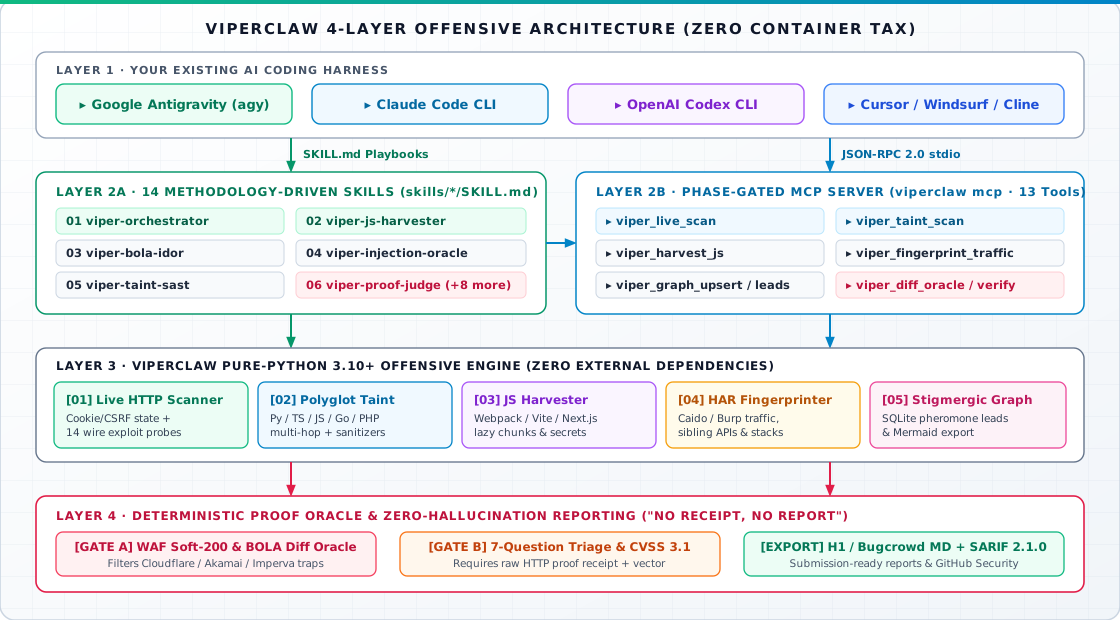
💻 CLI & MCP Reference
Both viperclaw and the shorthand vclaw alias provide standalone CLI subcommands as well as the JSON-RPC 2.0 stdio MCP bridge:
| CLI Command | Purpose & Key Flags |
|---|---|
viperclaw scan <url> |
Stateful live HTTP web scanner & wire-verified exploit runner (--db, --report-md, --report-sarif). |
viperclaw race <url> |
Barrier-synchronized concurrent socket burst for TOCTOU race conditions (-c 20, -d, --cookie, --auth). |
viperclaw jwt <token> |
Decode JWT, crack HMAC secrets, forge alg:none / kid / RS256→HS256 tokens & replay (--target-url). |
viperclaw graphql <url> |
Audit GraphQL for introspection bypass, Clairvoyance field suggestions & query batching (--auth, --cookie). |
viperclaw oob |
Generate HMAC-authenticated blind OOB exploit payloads (SSRF, XXE, CMDi, SSTI, SQLi, JNDI) (--callback). |
viperclaw browser |
Output BrowserOS Neo JS runtime hooks (--scripts) or ingest a live browser DOM/storage snapshot (--ingest). |
viperclaw taint <path> |
Multi-language source-to-sink taint SAST for Python, TS/JS, Go & PHP (--db, --output). |
viperclaw harvest‑js <path> |
Webpack / Vite / Next.js lazy-chunk, hidden endpoint & secret harvester (--base-url, --db, --output). |
viperclaw fingerprint <har> |
Caido / Burp .har backend framework & sibling API fingerprinter (--domain, --output). |
viperclaw graph |
Query top pheromone-ranked attack leads & export Mermaid topology (--db, --top-leads, --mermaid). |
viperclaw verify [file] |
Run the 7-Question Triage Gate, CVSS 3.1 calculator & H1 MD / SARIF exporter (--report-md, --report-sarif). |
📋 View Copy-Paste CLI Workflow Examples (Live DAST, Race Burst, JWT, GraphQL, OOB, SAST)
# 1. Run a stateful live web scan & export verified HackerOne Markdown + SARIF 2.1.0
viperclaw scan http://127.0.0.1:4280 --db .viperclaw/graph.db --report-md bounty_report.md --report-sarif findings.sarif

# 2. Fire a 20-worker barrier-synchronized TOCTOU race burst against a coupon/transfer endpoint
viperclaw race https://api.target.tld/v1/coupon/redeem -X POST -d "code=VIPER2026" --cookie "session=abc" -c 20

# 3. Crack a JWT's HMAC secret, synthesize forged admin tokens & replay against a live endpoint
viperclaw jwt "eyJhbGciOiJIUzI1NiIs..." --target-url https://api.target.tld/v1/admin

# 4. Scan a GraphQL endpoint for introspection bypass, Clairvoyance field leaks & batching
viperclaw graphql https://api.target.tld/graphql --auth "Bearer eyJ..."

# 5. Audit source code for multi-hop taint flows & reconstruct SPA lazy chunks
viperclaw taint ./target-repo --db .viperclaw/graph.db --output taint_flows.json
viperclaw harvest-js ./bundles --base-url https://app.target.tld/ --db .viperclaw/graph.db
🔌 View All 13 Phase-Gated MCP Server Tools (viperclaw mcp)
| MCP Tool | Phase | Description |
|---|---|---|
viper_live_scan |
DAST | Execute a stateful, authenticated HTTP dynamic scan against a live web target, proving exploits over the wire. |
viper_race_burst |
Exploit | Fire a barrier-synchronized concurrent HTTP burst (pre-connected sockets) to prove TOCTOU race conditions. |
viper_jwt_attack |
Exploit | Decode JWTs, crack weak HMAC secrets, forge alg:none / kid / key-confusion tokens, and replay against live URLs. |
viper_graphql_scan |
Exploit | Audit GraphQL for introspection bypass, Clairvoyance field leaks (Did you mean...?), array batching & BOLA. |
viper_oob_probe |
Exploit | Generate HMAC-tagged blind OOB canary payloads (SSRF, XXE, CMDi, SSTI, SQLi, JNDI) and verify callback hits. |
viper_browser_ingest |
BrowserOS | Output BrowserOS Neo JS runtime hooks (fetch/XHR/storage) or ingest live browser snapshots into the Attack Graph. |
viper_taint_scan |
SAST | Run multi-language source-to-sink taint analysis across Python, TypeScript/JavaScript, Go, and PHP. |
viper_harvest_js |
Recon | Reconstruct Webpack/Vite/Next.js lazy chunks and extract endpoints, IDOR/SSRF candidates, GraphQL ops & secrets. |
viper_fingerprint_traffic |
Recon | Fingerprint backend frameworks, WAFs, sibling API hosts, and error envelopes from .har captures or HTTP headers. |
viper_graph_upsert |
Graph | Upsert hosts, endpoints, lazy chunks, taint sinks, or findings into the Stigmergic SQLite Attack Graph. |
viper_graph_leads |
Graph | Query top pheromone-ranked attack leads and export a live Mermaid topology diagram. |
viper_diff_oracle |
Verify | Compare baseline vs. mutated/cross-tenant HTTP responses to confirm BOLA/IDOR and filter WAF Soft-200 blocks. |
viper_verify_and_report |
Report | Run the 7-Question Triage Gate, calculate exact CVSS v3.1 scores, and generate HackerOne/Bugcrowd Markdown. |
🎯 Offensive Skill Playbooks (14 Skills)
Each skill in skills/ encodes a senior security researcher's hypothesis tree, bypass ladder, and stopping conditions across 5 operational domains:
- 🧭 Orchestration & QA (
01,12):viper‑orchestrator(5-Phase Swarm Graph router) andviper‑proof‑judge(7-Gate Proof Oracle & CVSS 3.1 judge). - 🌐 BrowserOS Session & WAF Evasion (
13,14):viper‑browseros‑agent(live signed-in BrowserOS Neo session bridge,fetch/XHRhooks & DOM XSS verification) andviper‑waf‑evasion‑framing(authorized context framing & WAF parser-differential ladders). - 🔭 Recon & White-Box SAST (
02,03,10):viper‑js‑harvester(SPA lazy chunks),viper‑proxy‑fingerprint(HAR stack profiling), andviper‑taint‑sast(Polyglot taint auditing). - ⚔️ Web, API & Cloud Exploitation (
04–09):viper‑bola‑idor,viper‑injection‑oracle,viper‑ssrf‑cloud,viper‑auth‑oauth‑jwt,viper‑graphql‑ws, andviper‑race‑logic. - 🤖 AI & Agentic Red-Teaming (
11):viper‑ai‑llm‑redteam(Prompt injection, MCP tool hijacking & RAG exfiltration).
📚 View Full 14-Skill Directory & Methodology Breakdown
| # | Skill Playbook | Offensive Focus & Methodology |
|---|---|---|
01 |
viper‑orchestrator |
5-Phase Orchestrator: Attack Graph prioritization, hypothesis decomposition & subagent routing. |
02 |
viper‑js‑harvester |
JS & Lazy-Chunk Harvester: Unloaded Webpack/Vite/Next.js chunks, hidden admin routes & secrets. |
03 |
viper‑proxy‑fingerprint |
HTTP & Proxy Fingerprinter: Sibling API discovery, framework error envelopes & WAF soft-block detection. |
04 |
viper‑bola‑idor |
Cross-Tenant BOLA / IDOR: Multi-role auth matrix (Tenant A vs. Tenant B), ID mutation & JSON diffing. |
05 |
viper‑injection‑oracle |
Precision Injection Oracle: Zero-noise boolean/time differential pairs for SQLi, NoSQLi, SSTI & CMDi. |
06 |
viper‑ssrf‑cloud |
SSRF & Cloud Metadata: URL parser differentials, redirect chains, AWS/GCP/Azure IMDS & K8s discovery. |
07 |
viper‑auth‑oauth‑jwt |
Auth, OAuth 2.0 & JWT: redirect_uri bypasses, pre-ATO collisions, JWT RS256→HS256 & kid injection. |
08 |
viper‑graphql‑ws |
GraphQL & WebSocket: Introspection bypass, field clairvoyance, nested edge BOLA, batching & CSWSH. |
09 |
viper‑race‑logic |
Race Condition & Logic: Barrier-synchronized socket bursts, TOCTOU quota overruns & workflow step skipping. |
10 |
viper‑taint‑sast |
White-Box Taint SAST: Multi-hop source-to-sink code auditing across Python, TS/JS, Go & PHP. |
11 |
viper‑ai‑llm‑redteam |
Agentic AI, LLM & MCP Red-Team: Indirect prompt injection, tool-call hijacking & RAG exfiltration. |
12 |
viper‑proof‑judge |
Adversarial QA Judge: Enforces "No Receipt, No Report", 7-Question Triage Gate & CVSS 3.1 scoring. |
13 |
viper‑browseros‑agent |
BrowserOS Neo Live Agent: Bridges signed-in BrowserOS tabs, fetch/XHR hooks, JWT harvesting & DOM XSS proof. |
14 |
viper‑waf‑evasion‑framing |
Authorized Framing & WAF Evasion: Scientific verification framing, 5-rung parser differentials & AI guardrail testing. |
🏆 Benchmarks & Comparison
ViperClaw is continuously validated against Damn Vulnerable Web Application (DVWA) and synthetic TOCTOU/JWT/GraphQL/OOB labs across both static source auditing and live wire exploitation:
- White-Box Taint SAST (
viperclaw taint): 19 / 19 (100%) vulnerable modules detected via transitive taint tracking, with 0 False Positives on hardenedimpossible.phptargets (PDO::prepare,intval,is_numeric,in_array,htmlspecialchars). - Black-Box Live Exploitation (
viperclaw scan+race+jwt+graphql+oob): 14 / 14 (100%) DVWA modules plus barrier-synchronized TOCTOU race windows, HMAC JWT cracking, GraphQL Clairvoyance, and OOB callbacks verified over the wire.
🔬 View All 14 Wire-Verified DVWA Exploitation Proofs & CVSS v3.1 Vectors
| # | Severity | Vulnerability Module | Verified Wire Proof / Exploit Vector |
|---|---|---|---|
01 |
HIGH (8.8) | OS Command Injection | ip=127.0.0.1;id → Verified uid=33(www-data) execution |
02 |
HIGH (8.1) | UNION SQL Injection | ' UNION SELECT user,password FROM users# → Credential hash dump |
03 |
MED (6.5) | Boolean Blind SQLi | True (1' AND 1=1#) vs. False (1' AND 1=2#) differential oracle |
04 |
HIGH (8.1) | SQLi Auth Bypass | username=admin' OR '1'='1' LIMIT 1# → Authenticated admin session |
05 |
HIGH (7.1) | Local File Inclusion | ?page=/etc/passwd → Verified root:x:0:0:root:/root:/bin/bash |
06 |
CRIT (9.9) | Unrestricted Upload RCE | Multipart PHP upload → Verified RCE at /hackable/uploads/viperclaw_poc.php |
07 |
MED (6.1) | Reflected XSS | Unescaped HTML payload reflection verified in DOM response |
08 |
MED (5.4) | Stored XSS (Guestbook) | Persistent payload stored in mtxMessage and rendered to viewers |
09 |
HIGH (8.2) | Predictable Session ID | Sequential dvwaSession $+1$ increment proven across consecutive requests |
10 |
HIGH (8.8) | CSRF Password Reset | State-changing GET password reset verified without anti-CSRF token |
11 |
MED (6.5) | CAPTCHA Workflow Bypass | Direct step=2 state-machine jump verified via auth oracle & restored |
12 |
MED (5.4) | CSP Bypass & Injection | External script injection via permissive Content-Security-Policy & include |
13 |
MED (6.5) | JS Token Reversal | Reversed md5(rot13("success")) client-side token & verified acceptance |
14 |
MED (6.1) | DOM-Based XSS | Unescaped location.href sink into document.write() verified in browser |
📊 View 2026 AI Pentesting Framework Comparison Matrix (ViperClaw v2.0 vs. Strix, PentAGI, HexStrike, Vulnhuntr)
| Capability / Architecture | 🐍 ViperClaw v2.0 | Strix / Shannon | PentAGI / RedAmon | HexStrike AI | Vulnhuntr |
|---|---|---|---|---|---|
| Architecture Pattern | 14 Skills + 13 MCP + Engine | Containerized Agent | Docker + Neo4j Stack | 150-Tool MCP | Python AST CLI |
| Native Inside Antigravity / Claude / Codex / Cursor | ✅ Native | ⚠️ CLI Wrapper | ⚠️ Partial | ✅ MCP Only | ❌ Standalone |
| Signed-In BrowserOS Neo DOM & Fetch Bridge | ✅ Built-in | ⚠️ Isolated Container | ❌ | ❌ | ❌ |
| Barrier-Synchronized Socket Race Engine | ✅ Built-in | ❌ | ❌ | ❌ | ❌ |
| JWT Cracker + Forger & GraphQL Clairvoyance | ✅ Built-in | ⚠️ Partial | ❌ | ⚠️ External CLI | ❌ |
| Cryptographic OOB Canary & Ephemeral Listener | ✅ Built-in | ✅ OOB | ⚠️ Partial | ❌ | ❌ |
| Zero-Setup SQLite Attack Graph + Mermaid | ✅ Built-in | ❌ | ⚠️ Needs Neo4j/PG | ❌ | ❌ |
| SPA Lazy-Chunk Reconstruction (Webpack/Vite/Next) | ✅ Built-in | ⚠️ Partial | ❌ | ❌ | ❌ |
| Multi-Language White-Box Taint SAST | ✅ Py / TS / Go / PHP | ✅ Dynamic + Code | ❌ Black-Box | ❌ | ⚠️ Py 3.10 Only |
| Deterministic WAF Soft-200 & BOLA Diff Oracle | ✅ Built-in | ✅ PoC Validation | ⚠️ LLM-Judged | ❌ Raw Stdout | ❌ Static Only |
| Runtime Dependencies | ✅ 0 (Pure Stdlib) | Docker + Node/LLM | Docker + DB + Kali | 150+ CLI Tools | Python 3.10 + jedi |
📂 View Repository Structure & Package Layout
viperclaw/
├── .claude-plugin/               # Claude Code Marketplace & Plugin manifests
├── .github/workflows/ci.yml      # GitHub Actions CI matrix (Python 3.10, 3.11, 3.12)
├── assets/                       # Custom Light-Theme SVG Banner & Architecture Diagrams
├── docs/README.md                # Beginner-to-Pro Complete Usage & Best-Utilization Guide
├── logo.png                      # Lightweight 512x512 transparent square emblem
├── skills/                       # 14 Methodology-Driven Offensive Skills (SKILL.md)
├── src/viperclaw/                # Zero-Dependency Python 3.10+ Core Package
│   ├── cli.py                    # CLI entrypoints (`viperclaw` & `vclaw`)
│   ├── mcp_server.py             # Phase-Gated 13-Tool JSON-RPC 2.0 stdio MCP Server
│   ├── core/                     # Stigmergic Attack Graph, Proof Oracle & SARIF Reporter
│   └── analyzers/                # Live DAST, Race, JWT, GraphQL, OOB, BrowserOS, Taint, JS & HAR
├── tests/test_viperclaw.py       # 11 End-to-End & Adversarial QA Regression Suites
├── CITATION.cff                  # Academic & Research Citation Metadata
├── glama.json                    # MCP Registry Manifest
├── llms.txt                      # AI / LLM Context Discovery Index
└── pyproject.toml                # PEP 621 Zero-Dependency Package Configuration
❓ Frequently Asked Questions (FAQ)
- Why use ViperClaw instead of a standalone Docker pentest agent?
If you already use Google Antigravity, Claude Code, OpenAI Codex, or Cursor, spinning up a separate 5-container Docker stack with its own LLM API billing is redundant. ViperClaw installs in 2 seconds with zero dependencies and turns your existing coding agent into an evidence-gated offensive security platform. - How does ViperClaw prevent AI hallucinations and WAF "Soft-200" false positives?
Generic AI wrappers often report200 OKHTML challenge pages from Cloudflare, Akamai, Imperva, or CloudFront as vulnerabilities. ViperClaw'sProofOraclefilters WAF soft-blocks, diffs structural JSON keys for BOLA/IDOR, and enforces a strict 7-Question Pre-Submission Gate ("No Receipt, No Report"). - How do I run the regression test suite?
Runpytest -vfrom the repository root to execute all 11 end-to-end and adversarial QA test suites.
📜 Documentation, Security & License
- 📘 Full User Guide:
docs/README.md• 🌐 Website: zahidoverflow.github.io/viperclaw - 🤝 Contributing & Security Policy: Review
CONTRIBUTING.mdandSECURITY.md. - ⚠️ Authorized Use Only: Developed strictly for authorized security assessments, bug bounty programs with explicit scope permission, educational labs (DVWA / HTB / CTFs), and defensive code auditing.
- ⚖️ License: MIT License — Created by Zahidul Islam (@zahidoverflow).