
ys1231/MoveCertificate
ys1231/MoveCertificate has 2,009 GitHub stars and 192 forks. GitHot measured +1 stars in 24 hours. Last checked 2026-11-07 23:53 UTC. Last push 2026-11-01.
支持Android7-17移动证书,兼容magiskv20.4+/kernelsu/APatch, Support Android7-17, compatible with magiskv20.4+/kernelsu/APatch
Measured star growth
- in 24h
- +1
- in 7 days
- Update delayed
- in 15 days
- Update delayed
- in 1 month
- Update delayed
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.en.md
OriginalMoveCertificate
A Magisk/KernelSU/APatch module for moving user certificates to system certificates. Supports Android 7-16.
If your phone has an official image, you might need this module. If you compile your own ROM, you can either build it in or manually move it using remount.
Usage
- Prefer installing through system settings, no need to deal with encoding issues
- After exporting the certificate, simply
pushit to your phone and install it normally through system settings, then restart. No format conversion needed. - Can be used with appproxy VPN proxy tool.
Manual Certificate Installation to System Certificate Directory
- This method will overwrite existing certificates, designed for multiple computers and built-in certificates
- Normally, this scenario is not needed.
- The HASH.0 directly exported by Reqable may not always work. It is recommended to export the crt and install it normally through system settings, or use the commands below to convert it. Otherwise, even if the certificate file is moved successfully, the system won't recognize it due to encoding issues.
If the certificate has been moved before or built into the source code, you'll find that direct installation through the system doesn't actually install the certificate. This scenario needs to be preserved.
Export the packet capture software certificate and convert it to pem format
Get the der certificate
# For pem certificates (Android system uses der, so the moved certificate needs to be converted to der)
## 1. Calculate pem
openssl x509 -inform PEM -subject_hash_old -in cacert.pem
## 2. Convert to der
openssl x509 -in cacert.pem -outform der -out cacert.der
### Or from crt
openssl x509 -in cacert.crt -outform der -out cacert.der
mv cacert.der 02e06844.0

# For der certificates
## 1. Calculate der
openssl x509 -in cacert.der -inform der -subject_hash_old -noout
## 2. Rename certificate to hash.0
mv cacert.der 02e06844.0
# Or directly extract the certificate from the user directory after installing it on the phone, no need to worry about calculation and format conversion.
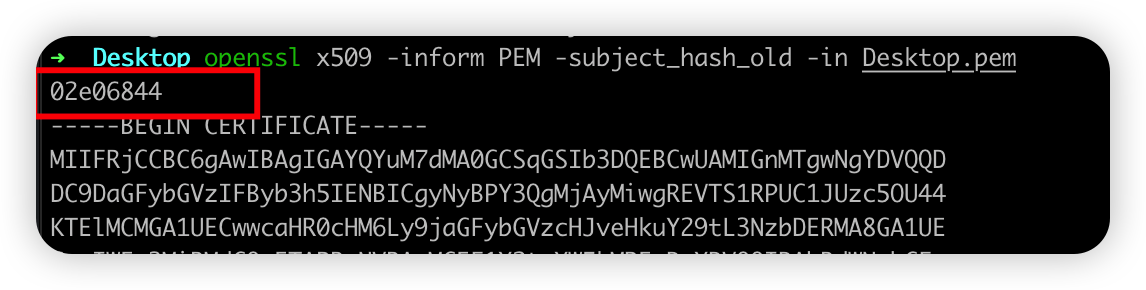
- Get the der certificate
02e06844.0, or coexist as02e06844.1 adb push 02e06844.0 /data/local/tmp/cert/- Restart and it's done.
MoveCertificate web
- A web page for the MoveCertificate module to display the list of installed certificates.
- It can also view detailed information about certificates installed by the module.
- Long press to delete installed certificates.
Build Command
./buildzip.sh all
Test Results
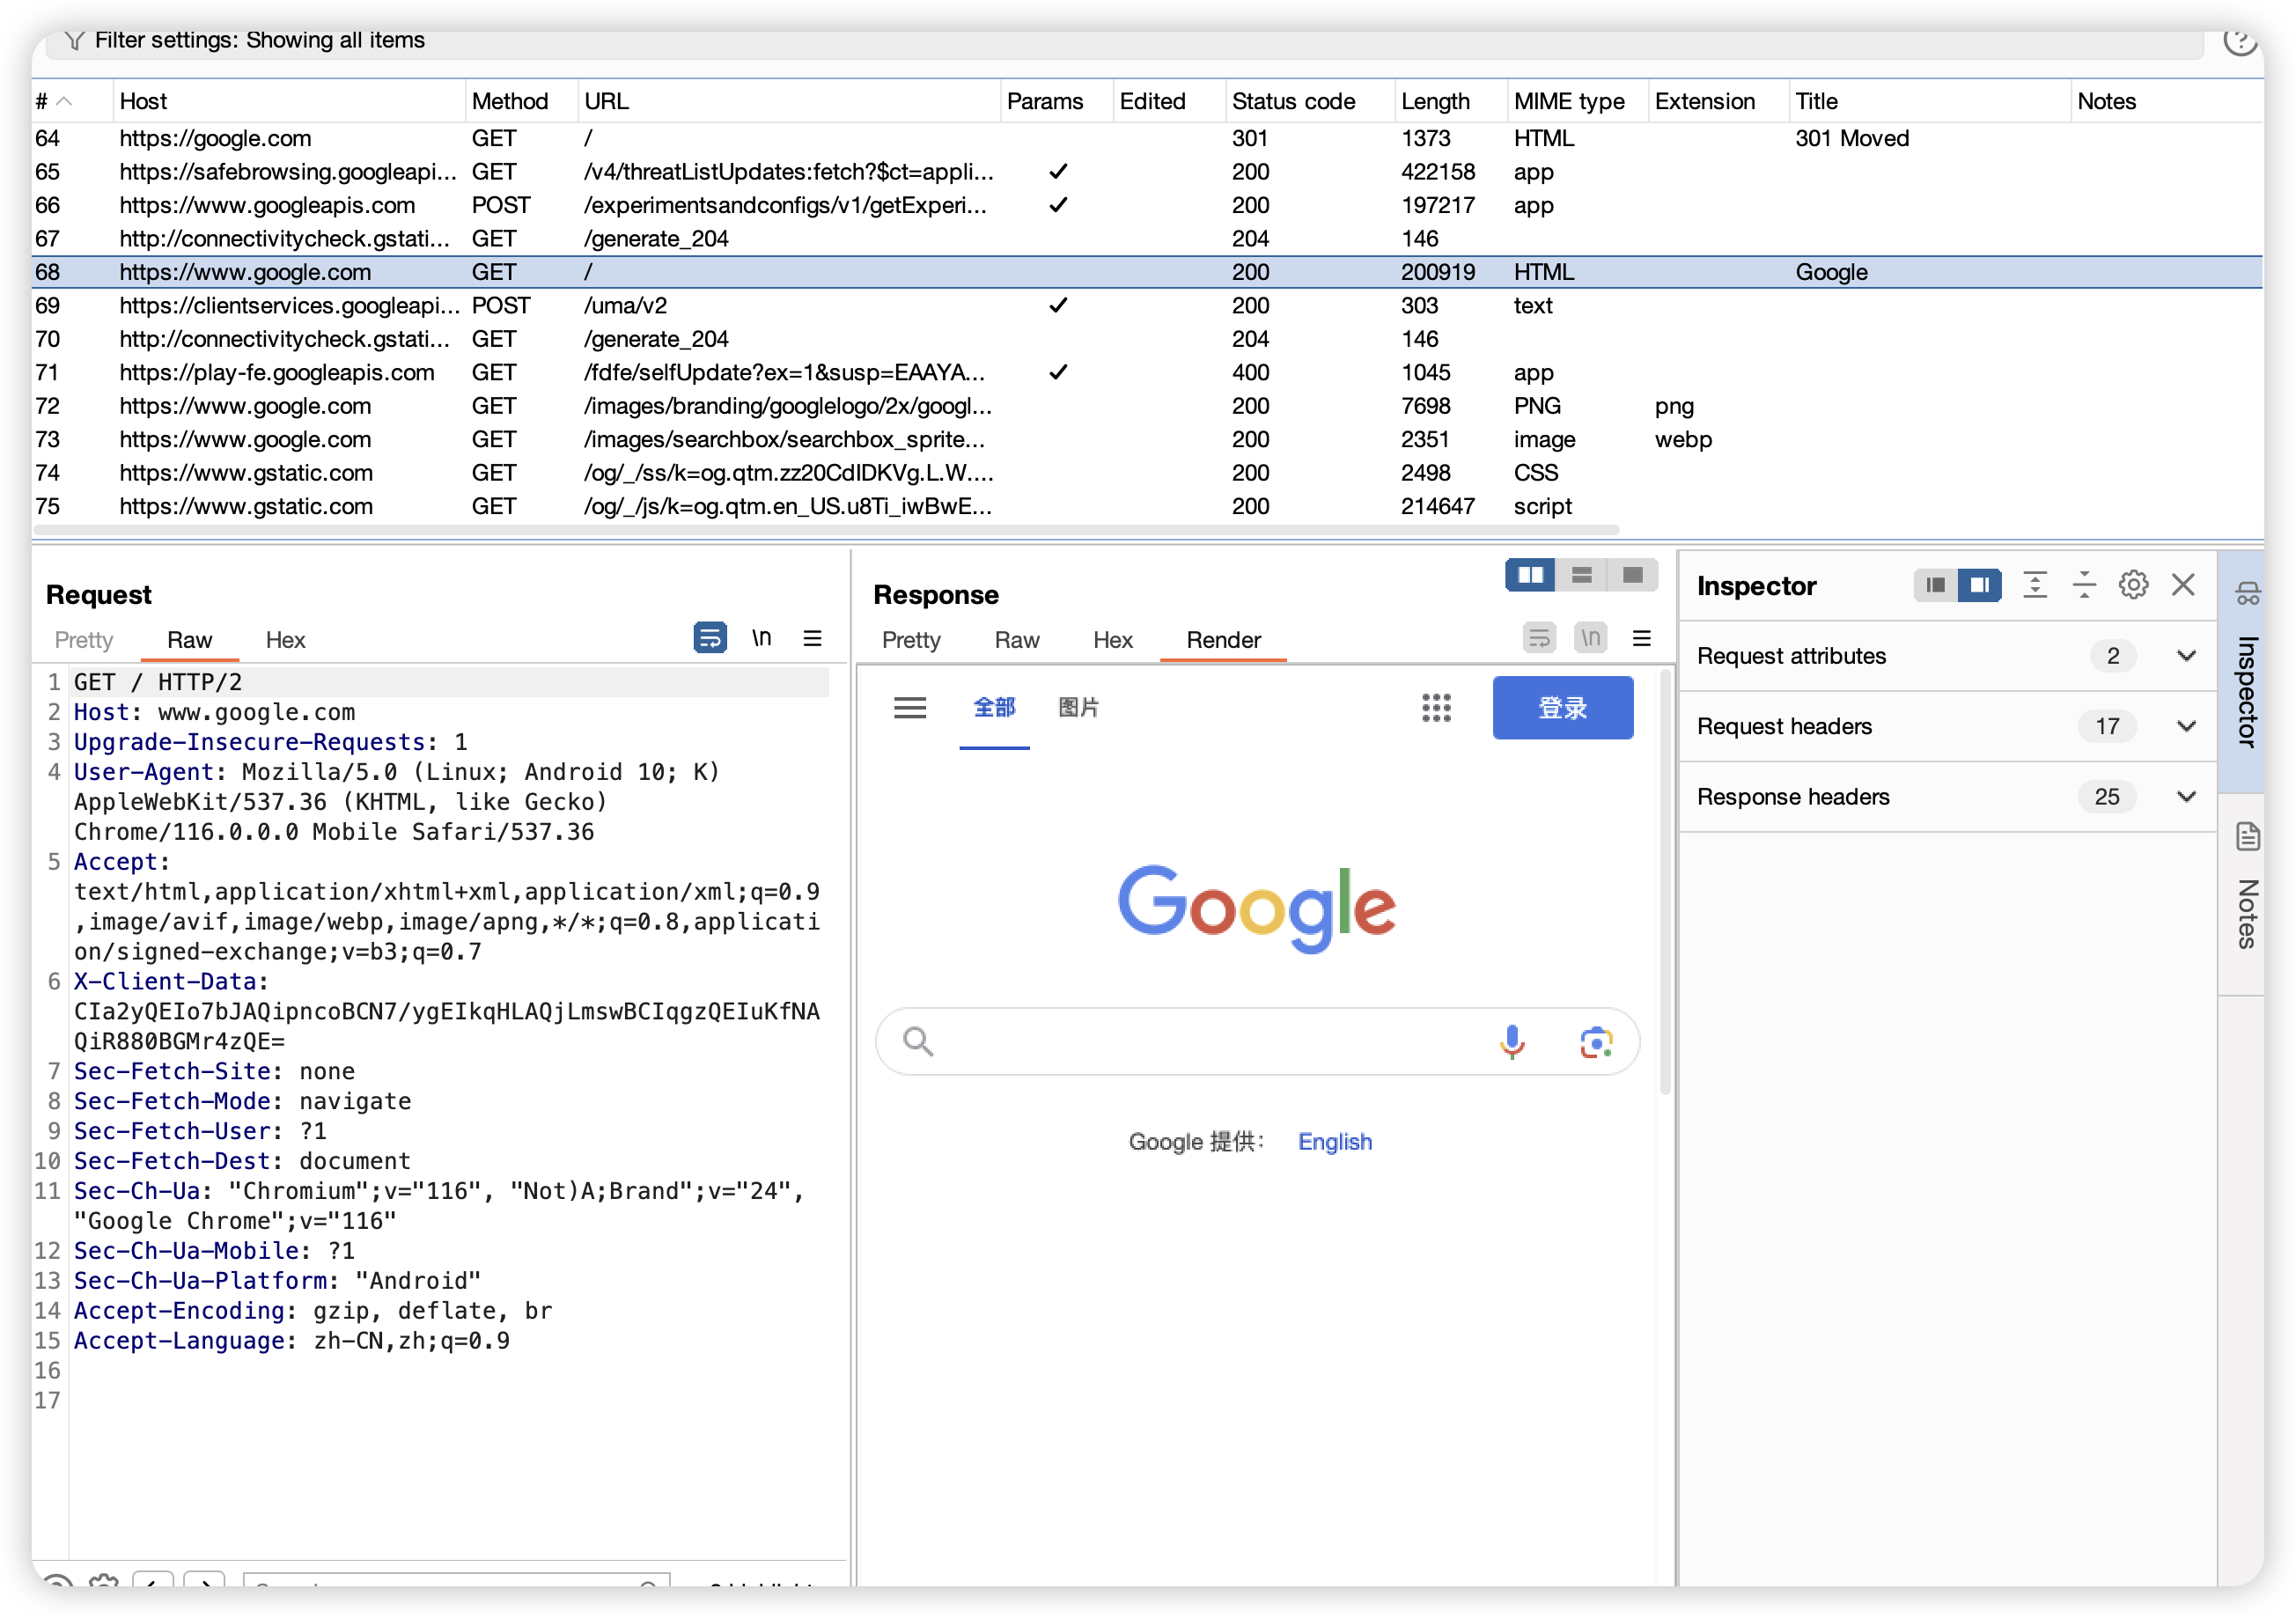
Star History
References:
- http://www.zhuoyue360.com/crack/60.html
- https://topjohnwu.github.io/Magisk/guides.html#boot-scripts
- https://github.com/Magisk-Modules-Repo/movecert
- https://github.com/andyacer/movecert
- https://book.hacktricks.xyz/v/cn/mobile-pentesting/android-app-pentesting/install-burp-certificate#android-14-zhi-hou
- https://kernelsu.org/zh_CN/guide/module.html
Explore related projects
codecrafters-io/build-your-own-x
Master programming by recreating your favorite technologies from scratch.
560,935 starspublic-apis/public-apis
A collective list of free APIs
497,198 starsmorluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
442,535 starsopenclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
394,178 stars