
wshm-dev/wshm has 89 GitHub stars and 11 forks. Star changes are not measured yet. Last checked 2026-11-07 07:06 UTC. Last push 2026-11-07.
AI-powered repository agent for GitHub, GitLab, Gitea, Azure DevOps. Issue triage, PR analysis, merge queue, notifications, dashboard, backup. Self-hosted, multi-provider.
Measured star growth
- in 24h
- Collecting history
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
Original
wshm
Your repo's wish is my command.
Five tools in one binary. AI code review, merge queue, issue auto-fix, workflow automation, and triage — all in a single self-hosted Rust binary.
Works with GitHub, GitLab, Gitea, and Azure DevOps. Plug in Claude Max, OpenAI, or a local Ollama — your call. Your AI keys. Your data. No SaaS dependency.
Runs on Linux (x86_64 & ARM64) and Windows (x86_64).
🧪 Built and battle-tested at RTK-ai Labs — born out of the daily backlog pain on rtk-ai/rtk (Rust Token Killer), now used in production by the team to run its own repos.


Why wshm?
You shipped the code. Now you spend your Mondays triaging a hundred stale issues, hunting duplicate bug reports, babysitting the merge queue, and writing the same "thanks for the report, can you share a reproduction?" reply for the tenth time.
wshm does the boring parts so you can stay in flow.
Five tools, one binary
| Need | wshm |
|---|---|
| AI code review | included |
| Merge queue | included |
| Issue auto-fix | included |
| Workflow automation | included |
| Issue triage | automated |
One binary, self-hosted, your AI keys. Your data stays yours.
Pain → gain
| Pain | wshm |
|---|---|
| Stale backlog, no one labels issues | AI triage classifies + labels new issues in seconds, with confidence scores |
| "Is this PR safe to merge?" review paralysis | PR risk analysis surfaces low/medium/high risk + a review checklist |
| Merge queue is a shared Notion doc | Scored merge queue auto-promotes green PRs above your threshold |
| Duplicates and zombie PRs pile up | PR health flags duplicates, stale, and zombie PRs automatically |
Secrets leak into .env and config |
Key vault integration (HashiCorp Vault, AWS, GCP) in Enterprise |
| SaaS tools hold your data hostage | Self-hosted, single Rust binary, SQLite (PostgreSQL multi-pod in Enterprise) — your data stays yours |
| OpenAI subscription fatigue | Claude Max / Pro / Team OAuth login — reuse your existing plan |
How it works
flowchart LR
    subgraph forges[" Git forges  "]
        direction TB
        gh["GitHub"]
        gl["GitLab"]
        gt["Gitea / Forgejo"]
        az["Azure DevOps"]
    end

    subgraph daemon[" wshm daemon — single Rust binary  "]
        direction TB
        sync["Sync engine<br/>(webhooks + polling)"]
        pipes["Pipelines<br/>• Triage<br/>• PR analysis<br/>• Merge queue<br/>• PR health<br/>• Auto-fix · Review"]
        store["Storage<br/>SQLite (OSS) / Postgres (Enterprise)<br/>+ FTS5 search index<br/>+ AES-256-GCM secret vault"]
    end

    subgraph ai[" AI providers — your keys  "]
        direction TB
        claude["Claude Max / Pro / Team<br/>(OAuth, no API key)"]
        api["Anthropic · OpenAI · Google · Mistral<br/>Groq · DeepSeek · xAI · OpenRouter<br/>Cohere · Together · Fireworks · Perplexity"]
        local["Ollama / llama.cpp<br/>(local, zero data leaves)"]
    end

    subgraph clients[" You  "]
        direction TB
        web["Web dashboard<br/>(triage, queue, search, settings)"]
        tui["Terminal UI"]
        cli["CLI / scripts"]
    end

    forges -- "issues, PRs,<br/>comments, events" --> sync
    sync --> pipes
    pipes -- "classify,<br/>summarise,<br/>review" --> ai
    ai -- "structured<br/>verdicts" --> pipes
    pipes -- "labels, comments,<br/>merges, fix PRs" --> forges
    pipes <--> store
    store --> web
    store --> tui
    store --> cli
    web -- "actions<br/>(apply / dismiss)" --> pipes
The daemon is the only piece that runs continuously. It syncs your repos, fans events into pipelines, calls whichever AI provider you configured, and persists everything locally — your data never transits a SaaS. The web dashboard, TUI, and CLI all read the same store and trigger the same pipelines.
See it in action
$ wshm triage --apply
Syncing issues... 247 issues loaded
Classifying with claude-sonnet-4-6 (OAuth: Claude Max)...

  #412  "App crashes on M1 when opening settings"
        → type: bug, priority: high, confidence: 0.94
        → labels applied: bug, platform:macos, priority:high

  #413  "Would love dark mode support"
        → type: feature, priority: medium, confidence: 0.87
        → labels applied: enhancement, ui

  #414  "how do i install this???"
        → type: question, priority: low, confidence: 0.91
        → labels applied: question, needs-docs
        → auto-reply posted: link to docs/getting-started.md

Triage complete: 23 issues labeled, 4 auto-replied, 1 flagged as duplicate of #398
Merge queue view (TUI):
$ wshm queue
Rank  PR    Title                             Risk   Score  CI   Reviews  Action
 1    #891  fix: race in token refresh        low    94     OK   2/2      AUTO-MERGE
 2    #885  feat: add --json flag to queue    low    88     OK   2/2      READY
 3    #879  refactor: split notify module     med    71     OK   1/2      WAIT
 4    #902  chore: bump tokio                 low    66     OK   0/2      WAIT
 5    #876  feat: webhook retries             high   42     FAIL 0/2      BLOCKED
Try it in 30 seconds
# Homebrew (macOS / Linux)
brew tap wshm-dev/tap && brew install wshm
# …or one-shot install with SHA256 verification (Linux x86_64/aarch64, Windows via Git Bash)
curl -fsSL https://raw.githubusercontent.com/wshm-dev/wshm/main/install.sh | sh

cd your-repo
wshm config init
export GITHUB_TOKEN=ghp_xxxxx
wshm login              # pick Claude Max, API key, or any supported provider
wshm sync
wshm triage             # dry-run — no --apply yet, just see what it would do
Bring your own AI
wshm never ships an AI provider you have to pay extra for. Use whatever you already have.
- Claude Max / Pro / Team — OAuth login via the
claudeCLI, no API key, no separate billing - Any API provider — Anthropic, OpenAI, Google, Mistral, Groq, DeepSeek, xAI, OpenRouter, Azure, Together, Fireworks, Cohere, Perplexity
- Local models — Ollama or llama.cpp, zero cost, zero data leaves your machine
  Anthropic   OpenAI   Google   Mistral   Groq    DeepSeek   xAI
  OpenRouter  Ollama   Azure    Together  Fireworks Cohere   Perplexity
Deploy anywhere
One static binary. No SaaS dependency. Runs where your code lives.
| Platform | How |
|---|---|
| VM / VPS | systemd service, auto-update via Homebrew, any Linux |
| Docker | docker run innovtech/wshm:latest — multi-arch (amd64 + arm64) |
| Compose | cp .env.example .env && docker compose up -d — dashboard on :3000 |
| Kubernetes | Helm chart, Kustomize overlays, or raw Job/CronJob manifests under deploy/ |
| Local dev | wshm tui / wshm triage — works offline with Ollama |
A GitHub Action is planned — follow #22.
Forge support: GitHub (personal + org), GitLab (.com + self-managed), Gitea / Forgejo / Codeberg, Azure DevOps (Services + Server).
Origin story
wshm was born out of a real need: triaging the growing backlog of issues and pull requests on rtk-ai/rtk (Rust Token Killer). What started as a weekend script to auto-classify GitHub issues grew into a full repo agent — the tool we wished existed, now battle-tested on rtk itself before shipping to other repos.
Features
Open source (this repo, Apache-2.0)
Everything a team needs to run wshm on its repositories is in this repo, with no license key:
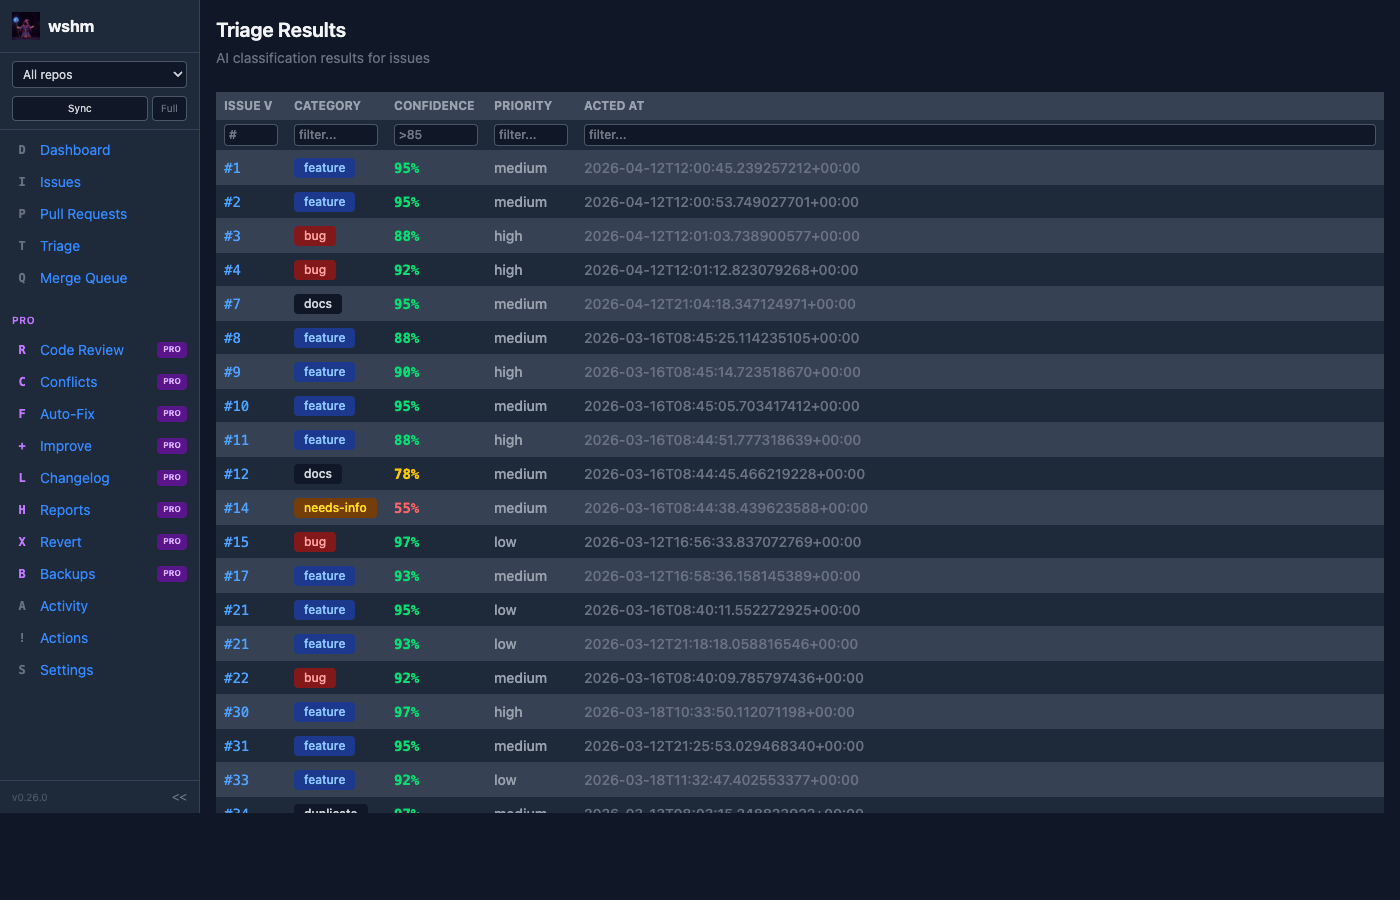
- Issue triage — AI classification (bug/feature/question/etc.), priority, confidence scoring, auto-labeling
- PR analysis — risk level (low/medium/high), type (feature/fix/docs), summary, review checklist
- Inline code review — line-by-line AI review on PR diffs, optionally posted as PR comments
- Auto-fix — generate fix PRs from issue descriptions (Claude Code / Codex / rootless container)
- Conflict detection — list PRs that conflict with their base branch
- Improvement proposals — analyze the codebase and open refactor/testing/performance issues
- Merge queue — scoring, auto-merge above threshold, conflict detection
- PR health — duplicate detection, stale/zombie PR flagging
- Reports — repo health reports with SLA metrics (Markdown, HTML, PDF)
- Changelog — AI-generated changelog from merged PRs (Markdown, JSON)
- Metrics dashboard — static HTML dashboard with charts
- Action plan — prioritized plan of issues across repos
- Notifications —
wshm notify/wshm runsummary to Discord, Slack, Teams; generic HTTP webhook export sink (HMAC-signed) - Sync — full / incremental fetch of issues and PRs from your forge
- Run — one-command cycle: sync + triage + analyze + queue + conflict detection
- Backup / Restore — snapshot your
.wshm/data for safe migration - Revert — undo all wshm actions (remove comments, labels, clear analyses)
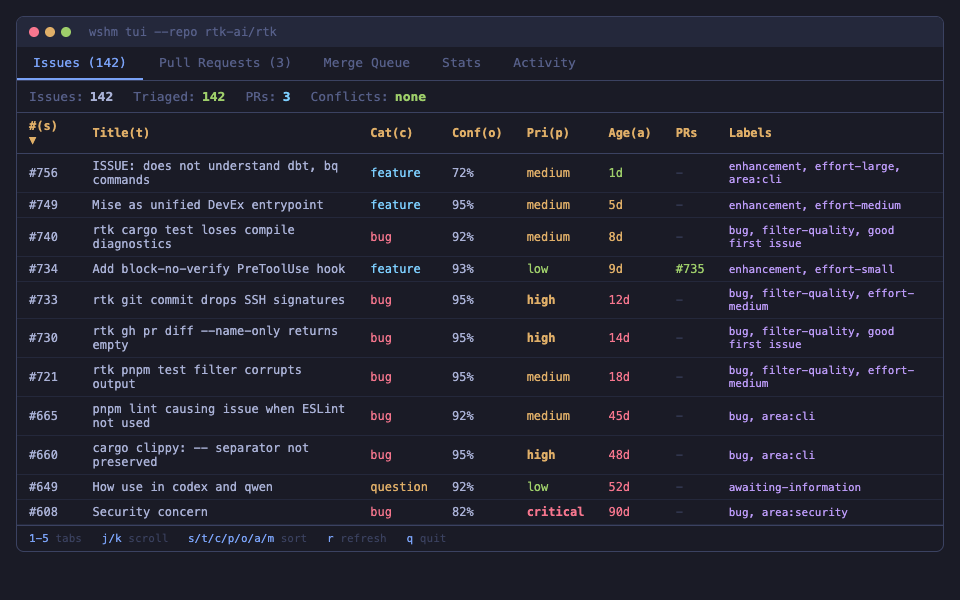
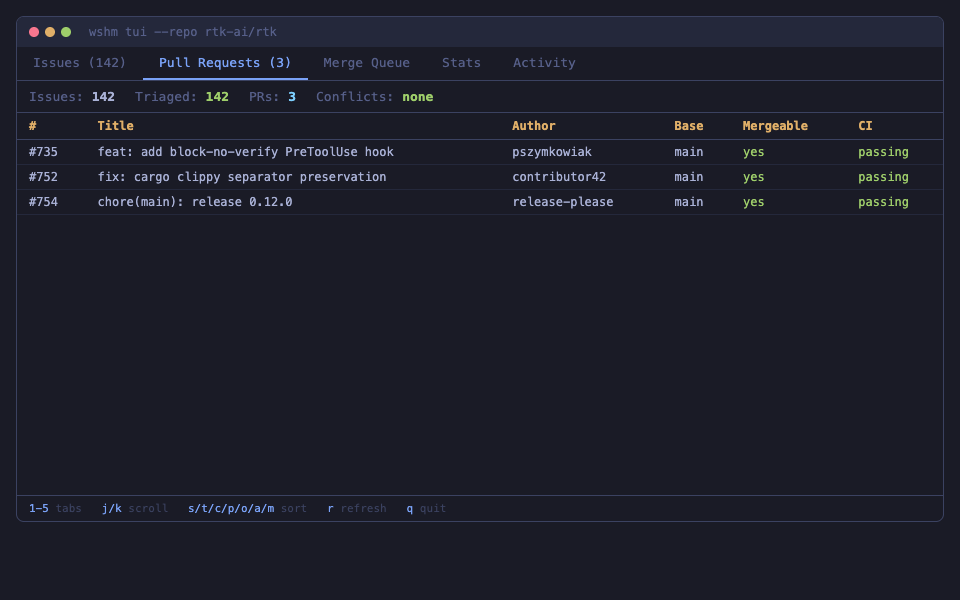
- TUI — rich interactive terminal UI (issues, PRs, queue, stats)
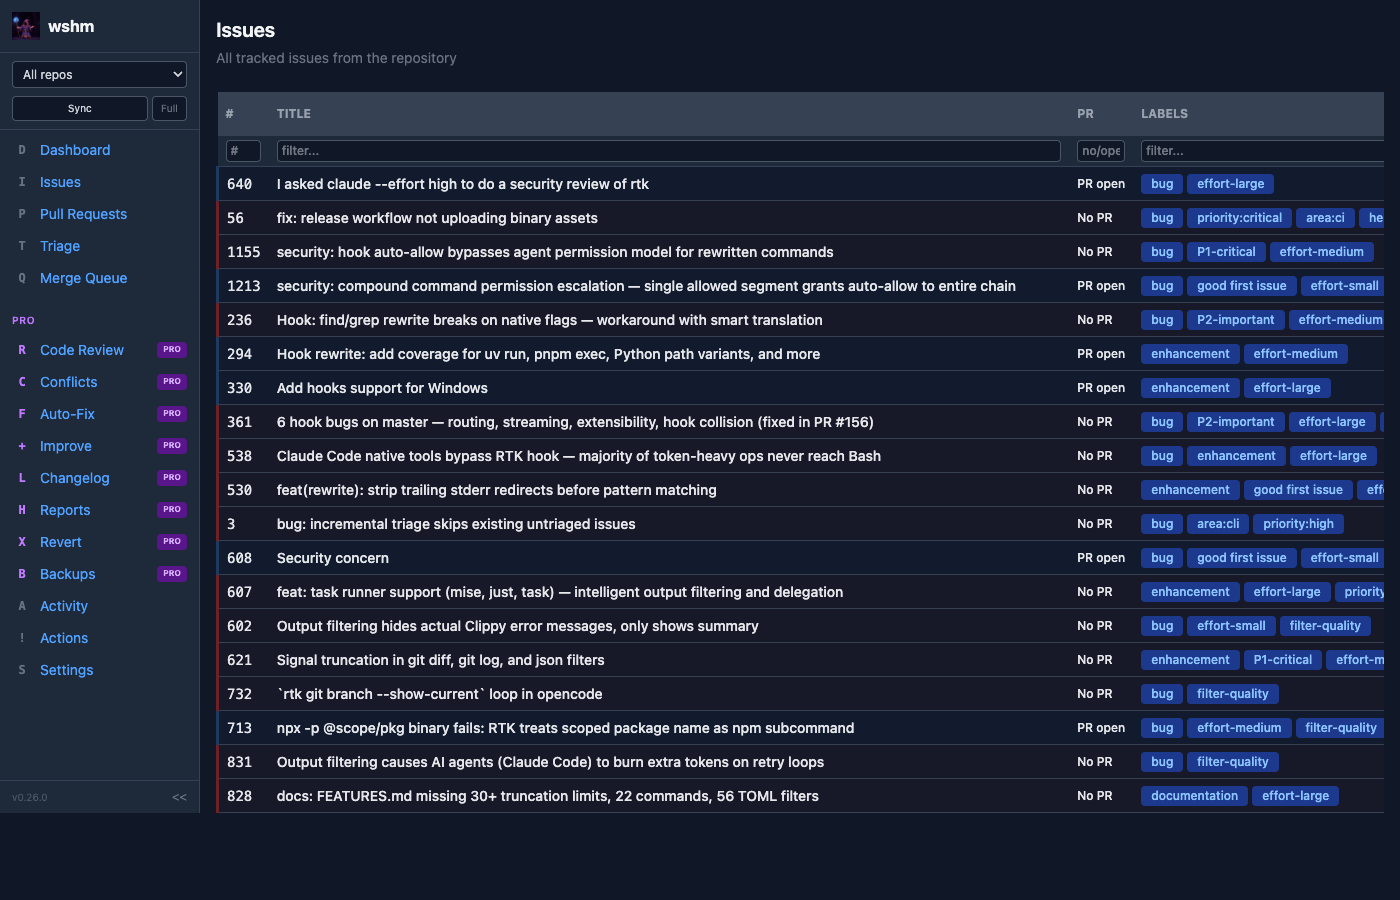
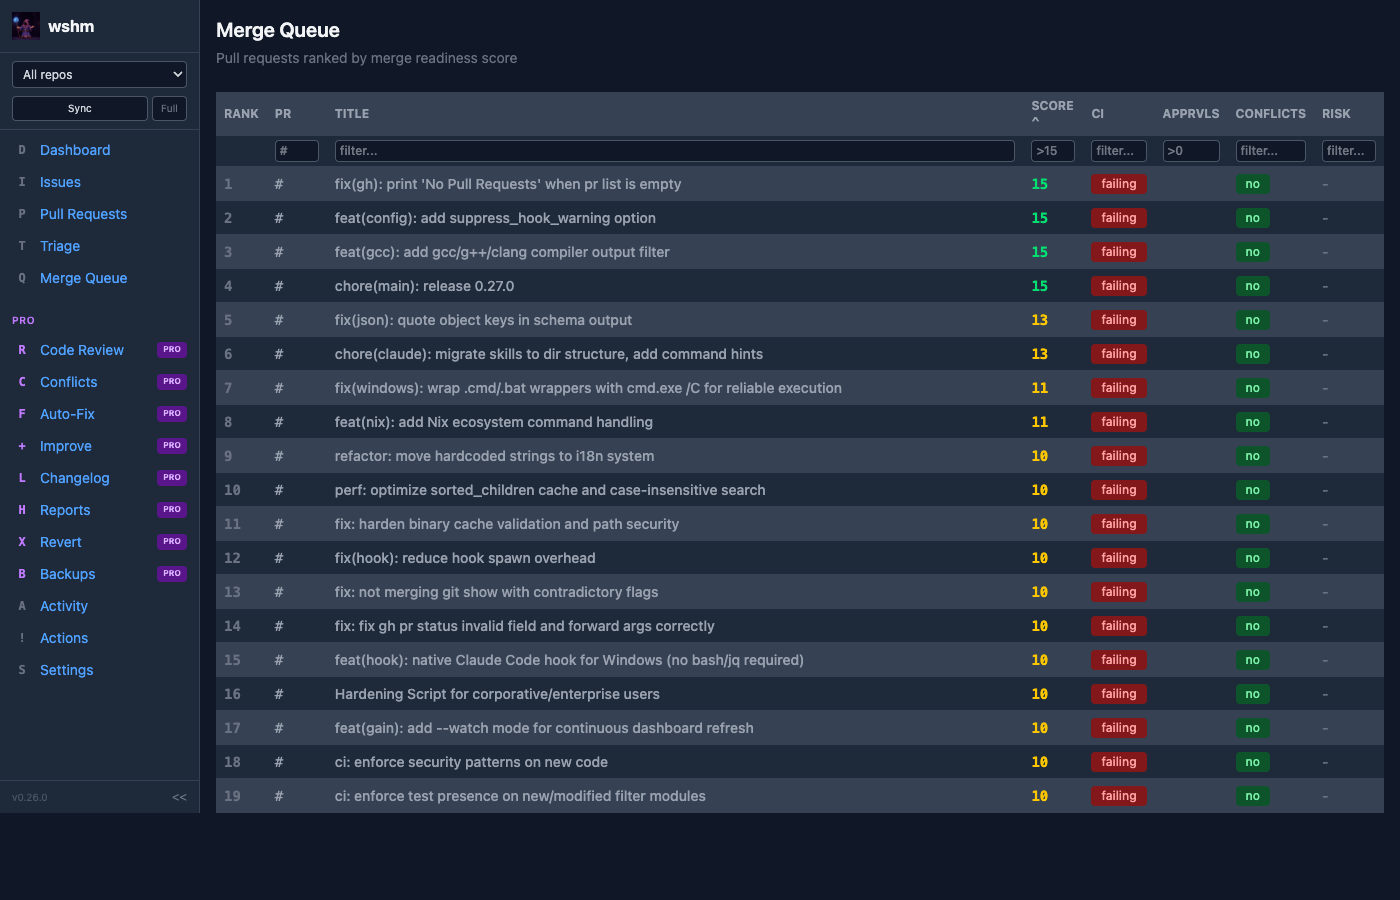
- Daemon + Web dashboard — persistent multi-repo background service with an embedded Svelte web UI: issues, PRs, code review, auto-fix candidates, conflicts, improvements, PR and issue insights, usage, reports, search, settings
- Context export — dump repo context as LLM-ready markdown
- 14 AI providers — Anthropic, OpenAI, Google, Mistral, Groq, DeepSeek, xAI, Ollama (local), llama.cpp, and more
- Claude Max / Pro / Team subscription — OAuth login via your existing Claude plan (no separate API key billing needed)
- 4 Git providers — GitHub, GitLab, Gitea, Azure DevOps (self-hosted friendly)
- Storage — SQLite (zero setup, bundled)
- Users & roles — local users, four roles (viewer, member, operator, admin) enforced server-side,
/api/v1/usersAPI - Encrypted secret store — tokens stored encrypted in SQLite (
WSHM_MASTER_KEY) - SSO via your auth proxy (OIDC) — put wshm behind oauth2-proxy, Cloudflare Access or a similar proxy (
WSHM_TRUST_PROXY_AUTH)
Enterprise (self-hosted)
The wshm-pro binary, for companies that self-host wshm at scale. Contact us at [email protected].
- User management page (
/users) and a PostgreSQL user store shared by every replica - PostgreSQL multi-pod — PostgreSQL primary backend for several stateless daemon replicas
- Secrets — encrypted secret store in PostgreSQL;
vault()placeholders from HashiCorp Vault, AWS Secrets Manager, GCP Secret Manager (license featurevault) - Exports — object storage (S3, GCS, Azure Blob) and databases (Elasticsearch, OpenSearch, MongoDB, MySQL) (license feature
exports) - Hosted PR diagram pages (license feature
diagram_hosting) - Support
Only vault(), exports and hosted diagram pages check the license at runtime.
Upgrading from an open-source release before the open-core split
Some settings had no effect in the open-source wshm binary and now run. Check them before upgrading:
review_prs = true(repo features): inline review runs on PR events. With the daemon in apply mode andreview_post_comments = true(the default), review comments are posted on the PR.[triage] auto_fix = true:wshm triage --apply(and the daemon in apply mode) now starts auto-fix and opens draft PRs.[notify] on_run = true:wshm runnow sends the notification summary.wshm runnow also runs conflict detection (read-only).
wshm-pro installs are not affected: these settings already ran there.
Interfaces
wshm ships four interfaces out of the box, all in OSS: CLI, TUI, daemon, and an embedded Svelte web dashboard.
CLI (Free)
wshm sync               # fetch issues + PRs
wshm triage --apply     # classify and label open issues
wshm pr analyze --apply # analyze and label open PRs
wshm queue              # show ranked merge queue
wshm run --apply        # full cycle
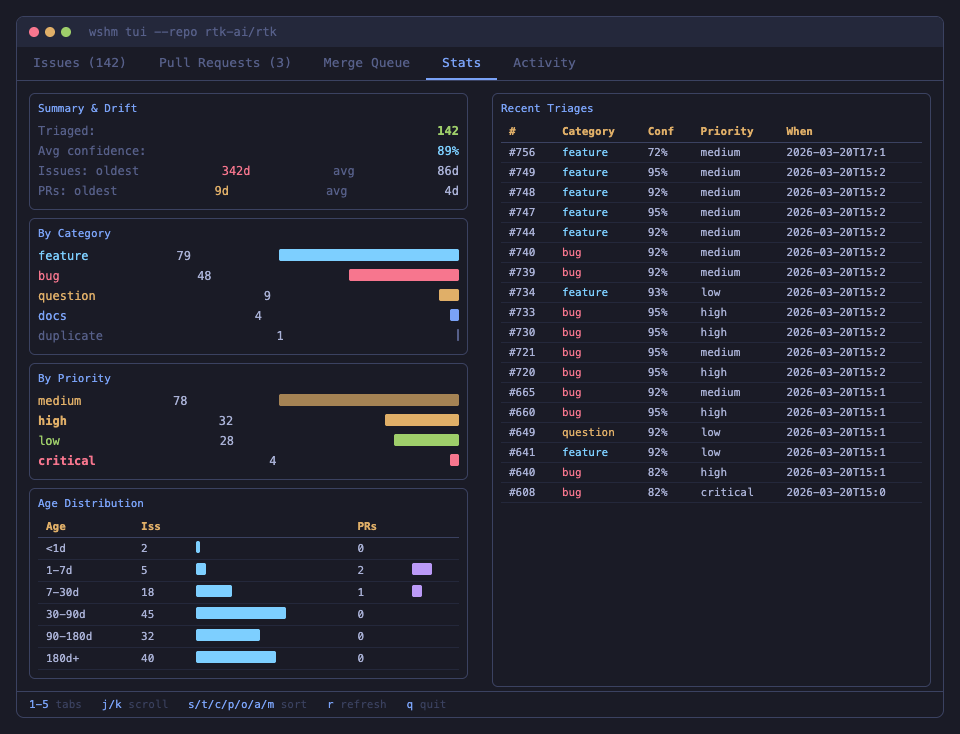
TUI (Free)
Rich interactive terminal UI — browse issues, PRs, merge queue, and stats without leaving the terminal.
wshm tui
Daemon + Web dashboard (Free)
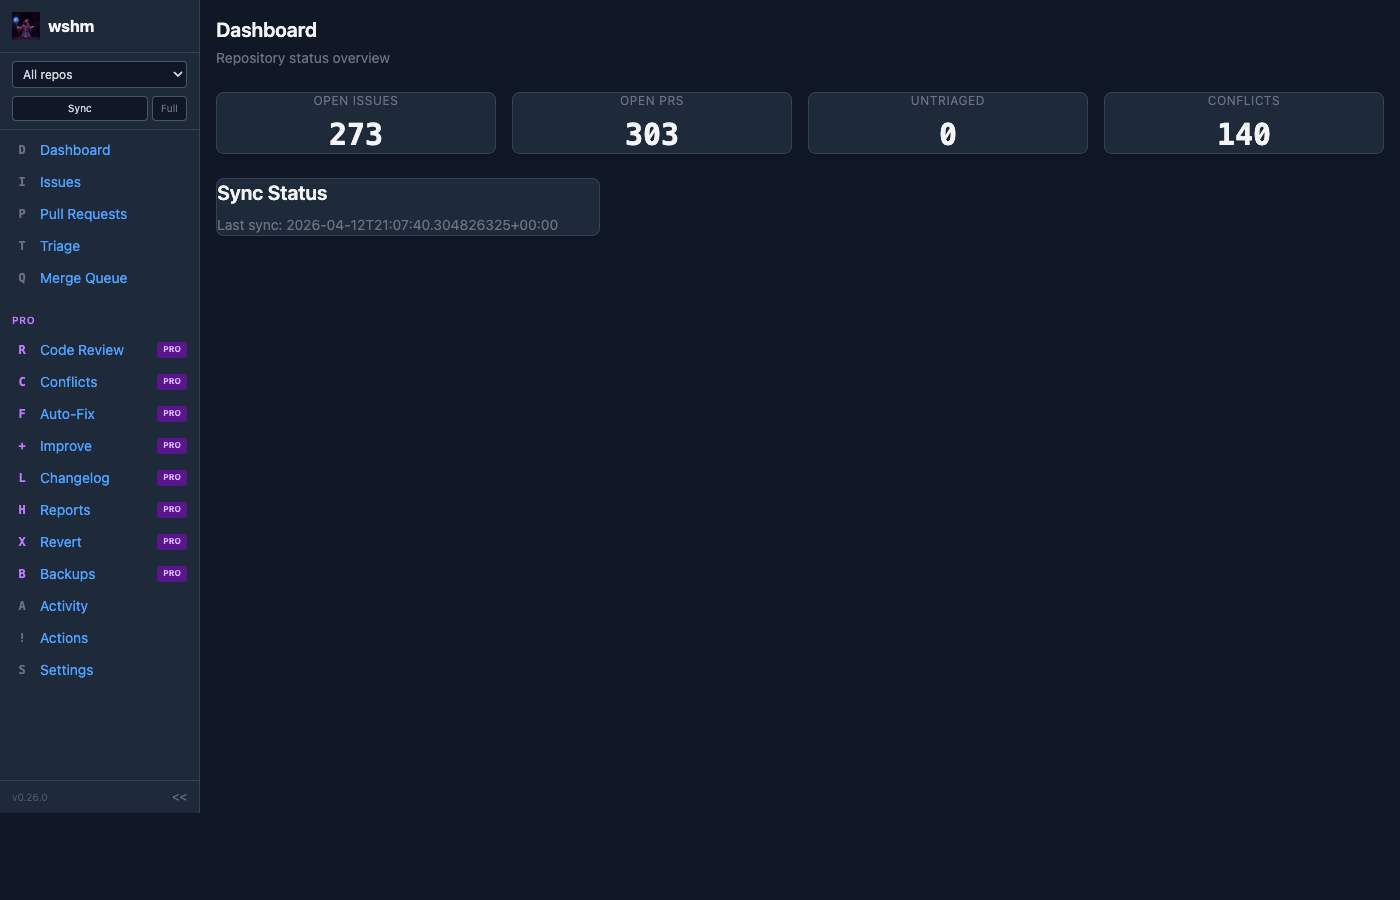
The daemon is a long-running multi-repo service: webhook server, scheduled triage, inline review and auto-fix, and an embedded Svelte web dashboard served on https://127.0.0.1:3000.
wshm daemon --config /etc/wshm/global.toml --poll
Quick Start
Install
Linux / macOS — Homebrew
brew tap wshm-dev/tap
brew install wshm
The Homebrew formula currently ships Linux bottles only (x86_64 + arm64); macOS support is tracked in #22.
Linux — install script (SHA256-verified)
curl -fsSL https://raw.githubusercontent.com/wshm-dev/wshm/main/install.sh | sh
Re-run to upgrade. Pin a version with sh -s -- --version v0.28.3. Every download is verified against the release's checksums.txt.
Linux — .deb (amd64 / arm64)
# amd64
curl -LO https://github.com/wshm-dev/wshm/releases/latest/download/wshm_$(curl -s https://api.github.com/repos/wshm-dev/wshm/releases/latest | grep tag_name | cut -d'"' -f4 | tr -d v)_amd64.deb
sudo dpkg -i wshm_*_amd64.deb
Windows x86_64 — direct download
Invoke-WebRequest -Uri https://github.com/wshm-dev/wshm/releases/latest/download/wshm-x86_64-pc-windows-msvc.zip -OutFile wshm.zip
Expand-Archive wshm.zip -DestinationPath $env:USERPROFILE\.wshm\bin
# then add %USERPROFILE%\.wshm\bin to your PATH
Release pipeline
| Target | Binary | .deb |
|---|---|---|
x86_64-unknown-linux-gnu |
✓ | ✓ |
aarch64-unknown-linux-gnu |
✓ | ✓ |
x86_64-pc-windows-msvc |
✓ | — |
x86_64-apple-darwin |
— | — |
aarch64-apple-darwin |
— | — |
Configure
cd your-repo
wshm config init        # creates .wshm/config.toml
export GITHUB_TOKEN=ghp_xxxxx
wshm login              # interactive auth setup
wshm login supports three auth paths for Anthropic:
- Claude Max / Pro / Team subscription — OAuth login (reuses
~/.claude/.credentials.jsonfrom theclaudeCLI; no extra billing) - Anthropic API key —
export ANTHROPIC_API_KEY=sk-ant-xxxxx - Any of the 13 other providers — OpenAI, Google, Mistral, Groq, DeepSeek, xAI, Ollama (local), llama.cpp, …
Run
wshm sync               # fetch issues + PRs from GitHub
wshm triage --apply     # classify and label open issues
wshm pr analyze --apply # analyze and label open PRs
wshm queue              # show ranked merge queue
wshm run --apply        # full cycle: sync → triage → analyze → queue
wshm backup             # snapshot state.db
wshm restore <file>     # restore from snapshot
Pipelines
Pipeline 1 — Issue Triage
New Issue → AI Classification → Label + Priority + Comment
                                  ├── duplicate? → close with link
                                  ├── needs-info? → ask for details
                                  ├── simple bug? → auto-fix (draft PR)
                                  └── feature? → label + backlog
Pipeline 2 — PR Analysis
New PR → Fetch diff + CI status → AI Analysis → Summary + Risk + Checklist
                                                  └── Auto-label + comment
Pipeline 3 — Merge Queue
Open PRs → Score (CI, reviews, age, risk, conflicts) → Ranked list
                                                         └── Auto-merge if above threshold
Pipeline 4 — Conflict Detection
Open PRs → Check mergeable → Conflicting? → Listed (no automatic rebase or resolution)
Daemon Mode (H24)
wshm can run as a persistent daemon that reacts to GitHub events in real-time.
Webhook Mode (recommended)
wshm daemon --apply --secret "whsec_your_webhook_secret"
Then configure a GitHub webhook on your repo:
- URL:
http://your-server:3000/webhook - Content type:
application/json - Secret: same as
--secret - Events: Issues, Pull requests, Issue comments
Polling Mode (no public IP needed)
wshm daemon --apply --poll --no-server
| Flag | Description |
|---|---|
--apply |
Perform actions (dry-run by default) |
--poll |
Enable GitHub Events API polling |
--poll-interval <N> |
Polling interval in seconds (default: 30) |
--no-server |
Disable the HTTP webhook server |
--bind <addr> |
Bind address (default: 0.0.0.0:3000) |
--secret <s> |
Webhook HMAC secret |
What the Daemon Does
| Trigger | Action |
|---|---|
| New issue opened | Auto-triage (classify, label, comment) |
| New/updated PR | AI analysis (type, risk, review checklist) |
/wshm triage comment |
Re-triage the issue |
/wshm analyze comment |
Re-analyze the PR |
/wshm review comment |
Post inline AI code review |
/wshm label <name> |
Add a label |
/wshm unlabel <name> |
Remove a label |
/wshm queue |
Show merge queue position |
/wshm health |
PR health check |
/wshm help |
List available commands |
| Every 5 min (scheduler) | Incremental sync + triage untriaged issues |
Authentication
Interactive Login
wshm login              # Setup GitHub + AI provider
wshm login --github     # GitHub only (uses gh auth login)
wshm login --ai         # AI provider only (prompts for API key)
wshm login --status     # Show current auth status
Credentials are stored in .wshm/credentials (chmod 600, gitignored).
Token Priority
| Priority | GitHub | AI |
|---|---|---|
| 1 | GITHUB_TOKEN / WSHM_TOKEN env var |
ANTHROPIC_API_KEY env var |
| 2 | gh auth token (gh CLI) |
— |
| 3 | .wshm/credentials (from wshm login) |
.wshm/credentials |
Supported AI Providers
| Provider | Env Var | Local |
|---|---|---|
anthropic (default) |
ANTHROPIC_API_KEY |
— |
openai |
OPENAI_API_KEY |
— |
google |
GOOGLE_API_KEY |
— |
mistral |
MISTRAL_API_KEY |
— |
groq |
GROQ_API_KEY |
— |
deepseek |
DEEPSEEK_API_KEY |
— |
xai |
XAI_API_KEY |
— |
ollama |
— | yes |
local |
— | yes (phi4-mini, smollm3-3b, qwen3-4b) |
Claude Subscription (no API key needed)
wshm login --claude # Uses your existing Claude Max/Pro/Team subscription
CLI Reference
| Command | Description |
|---|---|
wshm |
Show status from cache (instant) |
wshm sync |
Force full sync from GitHub |
wshm login |
Authenticate with GitHub + AI provider |
wshm triage [--issue <N>] |
Classify issues (or single issue) |
wshm pr [--pr <N>] |
Analyze PRs (or single PR) |
wshm queue |
Show ranked merge queue |
wshm conflicts |
Detect conflicting PRs |
wshm run |
Full cycle: triage + analyze + queue + conflicts |
wshm review [--pr <N>] |
Inline AI code review on PR diffs |
wshm health |
PR health: duplicates, stale/zombie PRs |
wshm fix --issue <N> |
Auto-generate a fix PR from an issue |
wshm report |
Generate report (md/html/pdf) |
wshm changelog |
Generate changelog from merged PRs |
wshm dashboard |
Generate metrics dashboard (HTML + charts) |
wshm notify |
Send priority summary (Discord/Slack/Teams/webhook) |
wshm daemon |
Start persistent daemon (webhook + polling) |
wshm backup |
Backup the local SQLite database |
wshm backup --output <path> |
Backup to a specific file |
wshm restore <file> |
Restore from a backup file |
wshm config init |
Create .wshm/config.toml template |
wshm model list |
List available local AI models |
wshm model pull <name> |
Download a model for local inference |
Global Flags
| Flag | Description |
|---|---|
--apply |
Perform actions (dry-run by default) |
--offline |
Skip GitHub sync, use cached data only |
--verbose / -v |
Detailed output |
--json |
JSON output for scripting |
--repo <owner/repo> |
Override detected repo |
Configuration
Everything is configured in .wshm/config.toml:
[ai]
provider = "anthropic"
model = "claude-sonnet-4-20250514"

[triage]
enabled = true
auto_fix = false
auto_fix_confidence = 0.85
retriage_interval_hours = 24

[pr]
enabled = true
auto_label = true
risk_labels = true

[queue]
enabled = true
merge_threshold = 15
strategy = "rebase"              # merge, rebase, squash

[assign]
enabled = true

[[assign.issues]]
user = "alice"
weight = 70

[[assign.prs]]
user = "bob"
weight = 50

labels_blacklist = ["do-not-touch", "manual-only"]

[branding]
name = "my-bot"
url = "https://my-project.dev"
command_prefix = "/my-bot"

[notify]
on_run = true

[[notify.discord]]
url = "https://discord.com/api/webhooks/ID/TOKEN"

[[notify.slack]]
url = "https://hooks.slack.com/services/YOUR/WEBHOOK/URL"

[[notify.teams]]
url = "https://outlook.office.com/webhook/YOUR/WEBHOOK/URL"
Auto-Fix with Podman Sandbox
# Build the sandbox image
podman build -f Dockerfile.sandbox -t wshm-sandbox:latest .

# Run Claude Code in Podman sandbox
wshm fix --issue 42 --docker --apply

# Use Codex instead
wshm fix --issue 42 --docker --tool codex --apply
Notifications
wshm notify          # send summary now
wshm run --apply     # full cycle + notify (if on_run = true); the daemon does not notify
The summary includes: open issues, untriaged count, high-priority issues, open PRs, high-risk PRs, and merge conflicts. Formatted natively for each platform (Discord embeds, Slack blocks, Teams adaptive cards).
Reports
wshm report --format md
wshm report --format html --output report.html
wshm report --format pdf --output report.pdf
GitHub Action
name: wshm
on:
  issues:
    types: [opened]
  pull_request:
    types: [opened, synchronize]
  issue_comment:
    types: [created]
  schedule:
    - cron: '0 */6 * * *'

jobs:
  wshm:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - uses: wshm-dev/wshm@main
        with:
          github-token: ${{ secrets.GITHUB_TOKEN }}
          ai-api-key: ${{ secrets.ANTHROPIC_API_KEY }}
Deploy on a VM
# Install via Homebrew, the SHA256-verified script, or the .deb package — see Quick Start above.
brew tap wshm-dev/tap && brew install wshm
wshm login
wshm config init
wshm daemon --apply --poll
Systemd Service
# /etc/systemd/system/wshm.service
[Unit]
Description=wshm daemon
After=network.target

[Service]
Type=simple
User=deploy
WorkingDirectory=/home/deploy/repo
ExecStart=/home/deploy/.cargo/bin/wshm daemon --apply --poll
Restart=always
RestartSec=10
Environment=RUST_LOG=info

[Install]
WantedBy=multi-user.target
Backup & Restore
wshm stores all its state in .wshm/state.db (SQLite). Back it up before upgrades or migrations.
# Backup (atomic via VACUUM INTO, includes WAL checkpoint)
wshm backup                        # → ~/.wshm/backups/state-20260422T143000.db
wshm backup --output my-backup.db  # custom path

# Restore
wshm restore ~/.wshm/backups/state-20260422T143000.db
# The existing DB is automatically saved as state.db.pre-restore before overwrite
From the TUI: press b to backup instantly, B to restore (prompts for file path).
From the web API (daemon mode):
| Method | Endpoint | Action |
|---|---|---|
GET |
/api/v1/backups |
List available backup files |
POST |
/api/v1/backup |
Create a new backup |
POST |
/api/v1/restore |
Restore from a backup ({"path": "..."}) |
Backup & Restore
wshm stores all its state in .wshm/state.db (SQLite). Back it up before upgrades or migrations.
wshm backup                        # → ~/.wshm/backups/state-20260422T143000.db
wshm backup --output my-backup.db  # custom path
wshm restore ~/.wshm/backups/state-20260422T143000.db
# the existing DB is saved as state.db.pre-restore before overwrite
TUI: b = backup instantly, B = restore (prompts for file path).
Web API (daemon): GET /api/v1/backups · POST /api/v1/backup · POST /api/v1/restore
Safety
- Dry-run by default —
--applyrequired to perform actions - Confidence gates — never acts autonomously below threshold (default 0.85)
- Never force-pushes — auto-fix pushes a new
wshm/fix-<N>branch and opens a draft PR - Idempotent — re-running = same result, no duplicate comments
- Token security — always from env vars, never in config files
- Transparent — every action posts a comment explaining what and why
Architecture
See CLAUDE.md for the full architecture document.
License
wshm is open source under the Apache License 2.0.
- Use it for any purpose (personal, commercial, enterprise), self-host it, modify it, redistribute it
- Read, study, and audit every line of code that touches your repositories
- Contributions are accepted under the same license (Apache 2.0, section 5) — no CLA required
- The wshm name and logo are trademarks of wshm-dev and are not covered by the license (section 6): forks are welcome, but please don't pass them off as wshm
Enterprise (self-hosted) features (user management page and PostgreSQL user store, PostgreSQL multi-pod, vault placeholders and PostgreSQL secret store, exports, hosted diagram pages, support) live in the separate, proprietary wshm-pro crate. Contact us at [email protected].
Disclaimer
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY ARISING FROM THE USE OF THIS SOFTWARE.
Precompiled binaries: Official precompiled binaries are provided for convenience via GitHub Releases and Homebrew. These binaries are built from the exact source code available in this repository. However, they are distributed as-is with no warranty. If you require full reproducibility or have security concerns, you are encouraged to build from source using the instructions above. By downloading and using a precompiled binary, you acknowledge that you do so at your own risk.
AI-generated actions: wshm uses AI models to classify issues, analyze
pull requests, and suggest code fixes. All automated actions are dry-run by
default and require explicit --apply to take effect. AI outputs may
contain errors — always review before applying. wshm-dev is not responsible
for any actions taken by the AI on your repositories.
Secret management / Key vaults (Enterprise)
Any config value can be sourced from a secret vault using a vault() placeholder — license keys, webhook secrets, database URIs, API keys stay out of config files.
[license]
key = "vault(secret/wshm/license-key)"

[[export.webhooks]]
secret = "vault(secret/wshm/webhook-hmac)"

[export.database]
uri = "vault(secret/wshm/elastic-uri)"
Supported providers: HashiCorp Vault, AWS Secrets Manager, GCP Secret Manager. Full guide: docs/vault.md.
Documentation
Full guides in docs/:
- Getting Started
- Configuration
- CLI Reference
- Deployment — Helm, Kustomize, Docker, install script
- Daemon & Web UI
- License & Activation
- Vault / Key Vault Integration (Enterprise)
- Open source vs Enterprise
- SSO & RBAC
- Troubleshooting
Architecture
┌─────────────────────────────────────────────┐
│         wshm-core (this repo, OSS)          │
│                                              │
│  CLI ── Daemon ── Web UI ── TUI              │
│    │        │        │       │              │
│    └────────┴────────┴───────┘              │
│              │                               │
│     OSS pipelines                            │
│     (triage, pr_analysis, merge_queue,       │
│      review, autogen, conflict detection,    │
│      improve, report, changelog, dashboard,  │
│      plan, notify, pr_health, backup)        │
│              │                               │
│    ┌─────────┴─────────┐                     │
│    ▼                   ▼                     │
│  SQLite      PostgreSQL (Enterprise)         │
└─────────────────────────────────────────────┘
Enterprise features live in a separate crate (wshm-pro, not open source) and attach via runtime hooks.
Contributing
Issues and PRs welcome. For substantial changes, please open an issue first to discuss.
See docs/getting-started.md for the development setup.
Disclaimer
wshm is provided "AS IS", without warranty of any kind, express or implied, including but not limited to the warranties of merchantability, fitness for a particular purpose, and noninfringement. In no event shall the authors or copyright holders be liable for any claim, damages, or other liability, whether in an action of contract, tort, or otherwise, arising from, out of, or in connection with wshm or the use or other dealings in wshm.
You use wshm at your own risk. wshm interacts with your GitHub/GitLab/Gitea/Azure DevOps repositories. It can create, modify, delete issues, pull requests, labels, and comments. Always run in dry-run mode first (without --apply) to verify the intended actions. The authors are not responsible for any data loss, incorrect labeling, unwanted PR merges, accidental comments, API rate-limit exhaustion, AI provider bills, or any other consequences of running this software.
AI classifications and suggestions can be wrong. wshm uses LLMs (Anthropic, OpenAI, Google, local models, etc.) for automated analysis. AI outputs are probabilistic, may contain hallucinations, and should never be considered authoritative. Always review AI-generated PRs, comments, and labels before trusting them in production workflows.
Your data, your responsibility. wshm is self-hosted. The authors have zero access to your data, tokens, API keys, or analysis results. Secure your .wshm/ directory, protect your GitHub tokens, and follow standard security practices for your infrastructure.
By using wshm you acknowledge that you have read, understood, and agreed to these terms.
License
Apache-2.0 — Copyright © 2025-2026 wshm-dev
Explore related projects
codecrafters-io/build-your-own-x
Master programming by recreating your favorite technologies from scratch.
560,676 starspublic-apis/public-apis
A collective list of free APIs
496,925 starsmorluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
440,064 starsopenclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
394,108 stars