
webkubor/vite-plugin-agent-eyes
webkubor/vite-plugin-agent-eyes has 105 GitHub stars and 4 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-16 19:49 UTC. Last push 2026-11-11.
Measured star growth
- in 24h
- 0
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
Vite 运行时遥测插件:为 AI agent 提供结构化日志、错误快照、本地 Cookie 修复与提交前检查。 / Vite telemetry plugin for AI agents with structured logs, error snapshots, local cookie repair, and pre-commit checks.
AIREADME.en.md
Original
👀 vite-plugin-agent-eyes
Give your AI agent eyes on the running website. Errors, requests, routes, and screenshots become readable evidence. Humans get a visual panel right on the page.


中文 · Documentation · Changelog
See it in 30 seconds
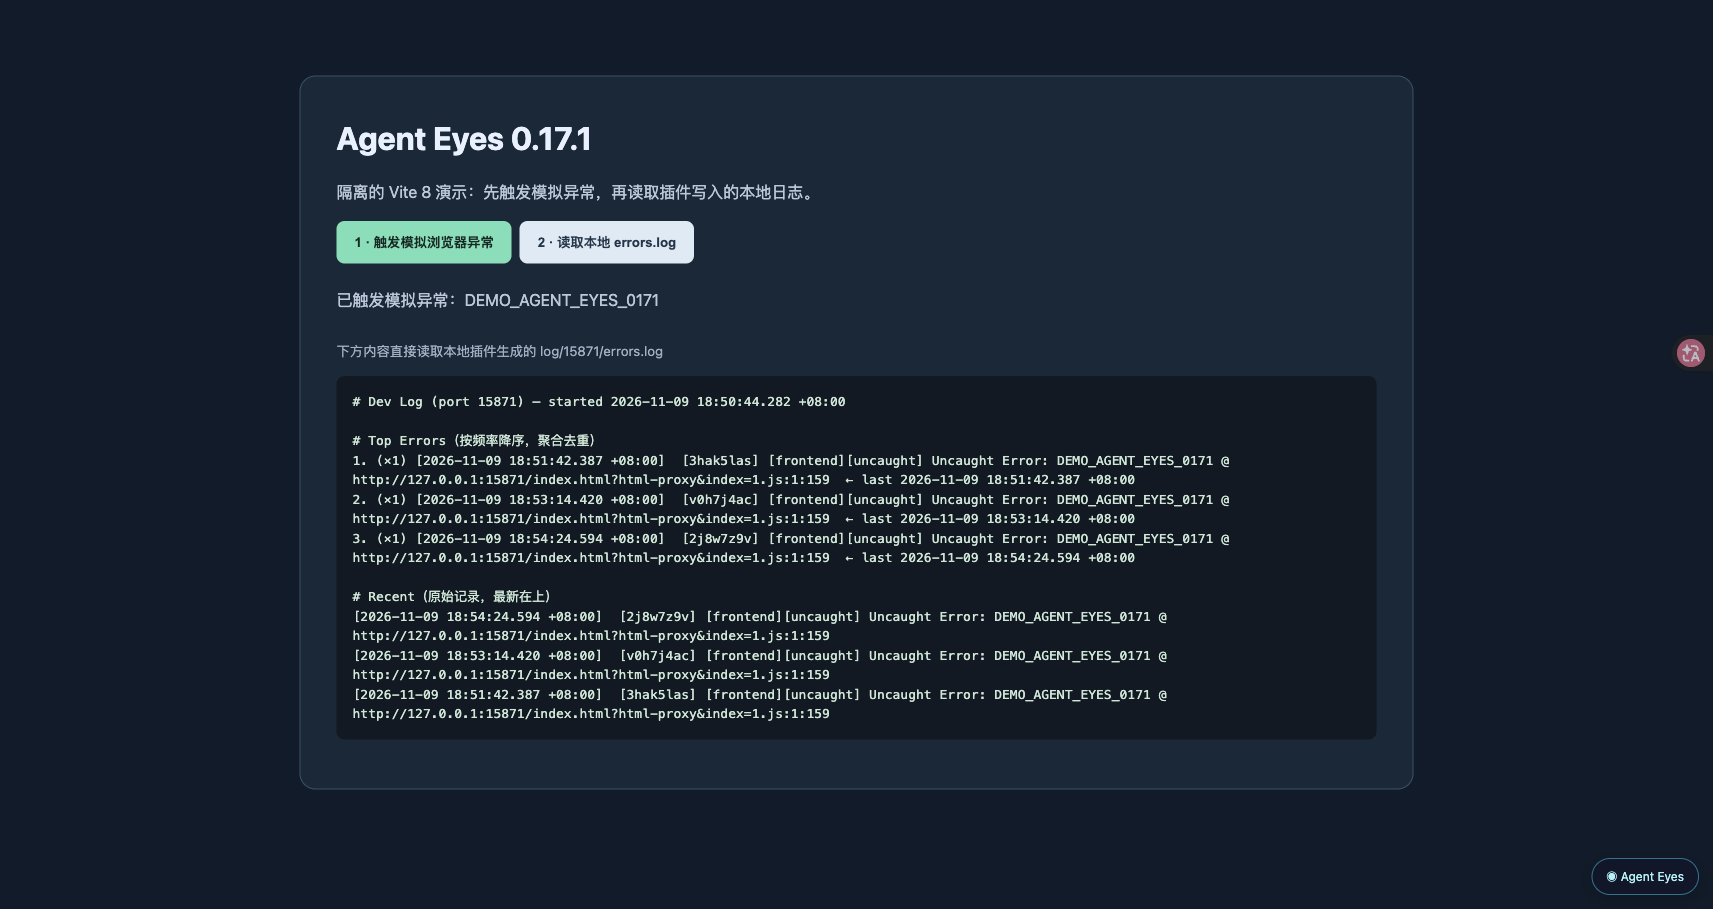
The npm release 0.17.1 running in an isolated Vite 8 example: after a simulated browser error, the page reads the plugin's actual local
errors.log. Capture details.
https://github.com/user-attachments/assets/e039b812-c366-421f-9f08-afdee5ea428a
| Before | With Agent Eyes |
|---|---|
| Send an agent a screenshot and explain which page it came from | Match the project and route, then label the screenshot with project, route, and time |
| Guess the environment and API target from config files | Read the startup banner: mode, proxies, aliases, and stack |
| Check robots, sitemap, and llms.txt by hand | Inspect them from the page; source files alone do not prove search indexing |
| Reproduce a bug and sift through scattered console and network output | Let the agent read structured errors, API calls, interactions, and proxy logs |
| Discover an env-flagged feature only after it ships | Commit guard blocks env-file drift: non-addressing vars must match across environments |
One setup, on by default. Chrome screenshots need a CDP-enabled browser; other capabilities work out of the box. Turn off individual features if you don't need them.
Start in a minute
pnpm add -D vite-plugin-agent-eyes
// vite.config.ts
import { defineConfig } from 'vite'
import { agentEyes } from 'vite-plugin-agent-eyes'

export default defineConfig({
  plugins: [...agentEyes()],
})
Run vite dev. A project summary appears in your terminal; the Agent Eyes entry appears at the bottom-right of the page. Already have a Vite proxy and need cookie or proxy diagnostics? Wrap its target with agentProxy(). A proxy is optional for the basic setup.
Works with React, Vue, Svelte, Solid, and plain JS. CI verifies Vite 4–8; the peer range is vite >=4 <10 (Vite 9 has not entered the matrix).
A real 401, without guesswork
A login request succeeds, then the next call returns 401. Browser fetch cannot show the complete proxy Set-Cookie / Cookie exchange. agentProxy() records the actual request and response cookie attributes and repairs common Domain / Secure / SameSite problems in local HTTP development. See the case study.
Explore further
Visual panel and screenshots · Reading the logs · Environment and engineering checks · Pre-commit guard · Full API
Screenshots require one uniquely matching CDP page for the current project and route. Finding robots or a sitemap locally does not prove they are publicly reachable or indexed. Logs, panel, and screenshots are dev-only; the version stamp also applies to builds. Installation notes and switches.
Leave the detailed debugging to AGENT_GUIDE.md and the generated log/README.md. To teach an agent to discover the tool on its own, use AGENT_BOOTSTRAP.md.
Star History
MIT · Issues
Design token guard (0.18.0+)
designTokens warns by default when staged additions contain hardcoded hex colors, numeric CSS color functions, or Tailwind arbitrary colors. Enable blocking with agentGit({ guard: { checks: { designTokens: 'block' } } }); global level: 'warn' still downgrades it.
For exceptions use designTokens: { level: 'warn', tokenFiles: ['**/tokens.*', '**/*tokens*.css', '**/theme.*', '**/design-tokens/**', '**/styles/variables.*'], allowValues: ['#000'] }. tokenFiles replaces the defaults and supports *, **, and ?; allowed values match case-insensitively after trimming. Token declarations, comments, tests, fixtures, and SVG assets are exempt. This is a lightweight added-line check, not a CSS/JS parser: multiline functions, computed expressions, and named colors are outside its scope. Restart dev after upgrading to regenerate the hook. See the API guide.