
prox0959/CyberCodex
prox0959/CyberCodex has 28 GitHub stars and 0 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-14 22:54 UTC. Last push 2026-11-07.
Measured star growth
- in 24h
- 0
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
Autonomous 23-Source Zero-Cost OSINT, Binary Image Forensics (EXIF/GPS/Stego), Data Breach/Leak & Threat Intelligence Engine in Pure Python
SecurityREADME.md
Original🛡️ Part of the Prox Security Ecosystem: Check out ProxSuite v3.0 — our 35-in-1 Native x64 Windows EDR, Live Memory Forensics & SIEM Command Center (100% Free & Open-Source under MIT License | 0/0 Windows Defender Clean).
🌐 CyberCodex (v3.2 - 22-Source Full-Spectrum Edition)
Author: Çınar (@prox0959) · 📧 [email protected]



CyberCodex (developed by Çınar / @prox0959) is an autonomous, self-updating, 22-Source Zero-Cost OSINT, Data Breach/Leak & Threat Intelligence Engine, Unbiased Cyber Warfare Encyclopedia (Incident Codex), MITRE ATT&CK Knowledge Base, and Dual-Perspective Technical Lexicon engineered for Windows CMD, PowerShell, and Linux terminals with zero external dependencies.
📡 22 Zero-Cost Public Intelligence & Leak Sources (No API Keys Required)
| # | Intelligence Source | Endpoint / Protocol | Telemetry Extracted | Cost / Key |
|---|---|---|---|---|
| 1 | HaveIBeenPwned Breaches | haveibeenpwned.com/api/v3/breaches |
Latest leak date, largest leak volume (PwnCount), leaked DataClasses & incident summary |
$0 / No Key |
| 2 | Hudson Rock Cavalier | cavalier.hudsonrock.com/api/json/v2 |
Real-world Infostealer (RedLine, Raccoon, Vidar) compromises, stolen URLs, AVs & password stats |
$0 / No Key |
| 3 | ProxyNova COMB (3.2B) | api.proxynova.com/comb |
3.2 Billion Compilation of Many Breaches credential exposure lookup & sample dump | $0 / No Key |
| 4 | HIBP K-Anonymity Passwords | api.pwnedpasswords.com/range/{sha1[:5]} |
850M+ breached password frequency check (only 5 SHA-1 hex chars transmitted) | $0 / No Key |
| 5 | HTTP Security & RFC 9116 | Live HTTPS + /.well-known/security.txt |
HSTS, CSP, X-Frame-Options, Server banner & Security Posture Grade (A+ to F) |
$0 / No Key |
| 6 | Shodan InternetDB | internetdb.shodan.io/{ip} |
Open ports, CPEs, hostnames, tags, exposed CVEs | $0 / No Key |
| 7 | FIRST.org EPSS | api.first.org/data/v1/epss |
30-day exploitation probability (%) & percentile | $0 / No Key |
| 8 | MITRE CVE AWG v5 | cveawg.mitre.org/api/cve/{id} |
Official CVE description, CVSS v3.1/v4.0 metrics | $0 / No Key |
| 9 | CIRCL.lu CVE API | cve.circl.lu/api/cve/{id} |
Secondary CVE metadata & CVSS fallback | $0 / No Key |
| 10 | GitHub Exploit/PoC Hunter | api.github.com/search/repositories |
Live public Proof-of-Concept (PoC) exploit repos & stars | $0 / No Key |
| 11 | CISA KEV Catalog | cisa.gov/.../known_exploited_vulnerabilities.json |
1,300+ actively exploited CVEs & ransomware campaign use | $0 / No Key |
| 12 | abuse.ch Feodo C2 | feodotracker.abuse.ch/.../ipblocklist |
Active QakBot, Emotet, Pikabot, Dridex C2 servers | $0 / No Key |
| 13 | abuse.ch ThreatFox | threatfox-api.abuse.ch/api/v1/ |
Malware SHA256/MD5 hash & C2 IOC attribution | $0 / No Key |
| 14 | CyberCodex Malware Vault | Local + Live Hash Engine | Instant attribution of famous APT/wiper SHA-256 hashes | $0 / No Key |
| 15 | Official Tor Exit List | check.torproject.org/torbulkexitlist |
Live verification against ~1,500 active Tor Exit Nodes | $0 / No Key |
| 16 | RIPE NCC Stat BGP | stat.ripe.net/data/network-info |
Announced BGP CIDR prefix & Origin ASN routing | $0 / No Key |
| 17 | ip-api / RDAP Telemetry | ip-api.com / rdap.arin.net |
ASN, ISP, Organization, Reverse DNS, Datacenter/Proxy | $0 / No Key |
| 18 | Cloudflare DoH DNS/DMARC | cloudflare-dns.com/dns-query |
Live MX, NS, SPF, DMARC & Email Spoofing vulnerability audit | $0 / No Key |
| 19 | Live TLS/SSL Socket | Native X.509 TCP/443 Handshake | SHA-256 cert fingerprint, serial, TLS version & C2 heuristics | $0 / No Key |
| 20 | crt.sh CT Logs | crt.sh/?q=%.{domain}&output=json |
SSL Certificate Transparency subdomain discovery | $0 / No Key |
| 21 | Wayback Machine CDX | web.archive.org/cdx/search/cdx |
Historical archived URLs and direct raw snapshot links | $0 / No Key |
| 22 | Ransomware & PhishStats | api.ransomware.live / phishstats.info |
Real-time global ransomware victims & active phishing URLs | $0 / No Key |
| 23 | PixelTrace Image OSINT & Nominatim | Binary EXIF/GPS + nominatim.openstreetmap.org |
Raw TIFF/EXIF/GPS rational parsing, live street reverse-geocoding, C2PA AI provenance & Post-EOF stego carving | $0 / No Key |
🚀 Quick Start & Usage (CMD / PowerShell / Terminal)
git clone https://github.com/prox0959/CyberCodex.git
cd CyberCodex

# 1. Synchronize live threat feeds (CISA KEV, Feodo C2, Tor Exit Nodes, Live Ransomware, MITRE)
python cybercodex.py update --lang tr

# 2. Run 23-source zero-cost OSINT, Breach/Leak, Stealer & Security Header scan on any Website/IP
python cybercodex.py intel linkedin.com --lang tr
python cybercodex.py intel adobe.com --lang en

# 3. Dedicated Data Breach History, Infostealer Exposure, COMB & K-Anonymity Password Leak Audit
python cybercodex.py leak adobe.com --lang tr
python cybercodex.py leak adobe.com --download --lang tr
python cybercodex.py leak user:admin --lang tr
python cybercodex.py leak pass:password123 --lang tr

# 4. PixelTrace Image OSINT: Extract Binary EXIF, GPS Street Address, AI Provenance & Hidden EOF Stego
python cybercodex.py image https://raw.githubusercontent.com/ianare/exif-samples/master/jpg/gps/DSCN0010.jpg --lang tr
python cybercodex.py image C:\path\to\suspect_photo.jpg --json report.json

# 5. Analyze any CVE with MITRE + FIRST EPSS + CISA KEV + Live GitHub PoC Exploit Hunter
python cybercodex.py cve CVE-2024-3094 --lang tr

# 6. Hunt Malware Hashes (SHA256 / MD5) & C2 Indicators via ThreatFox & Malware Vault
python cybercodex.py ioc 32519b85c0b422e4656de6e6c41878e95fd95026267daab4215ee59c107d6c77 --lang tr

# 7. Query Official MITRE ATT&CK Enterprise Techniques & SOC Detection Logic
python cybercodex.py mitre T1055.012 --lang tr

# 8. Read unbiased forensic engineering anatomy of major cyber operations
python cybercodex.py attack solarwinds --lang tr
python cybercodex.py compare stuxnet notpetya --lang tr

# 9. Query APT Threat Actor dossiers & Live Global Ransomware feed
python cybercodex.py apt lazarus --lang tr
python cybercodex.py ransom --lang de

# 10. Lookup technical OSINT, DFIR, Red/Blue Team & LOLBAS concepts
python cybercodex.py dict catroot-winsxs --lang tr

# 11. Generate OSINT Dorks (Google, GitHub, Shodan) & SIEM Rules (Wazuh, Sigma, KQL, Splunk)
python cybercodex.py dork example.com --lang ja

# 12. Launch Interactive Metasploit-style Console (`codex [TR] >`)
python cybercodex.py shell
🛰️ Embedded Image OSINT, Binary EXIF/GPS & Stego Engine (image Module)
CyberCodex includes a built-in, 100% Python Standard Library (core/image_osint.py) digital image forensics engine that dissects local image files (.jpg, .png, .webp, .gif, .tiff, .bmp) or remote image URLs directly in RAM without external libraries (Pillow or exiftool are not required):
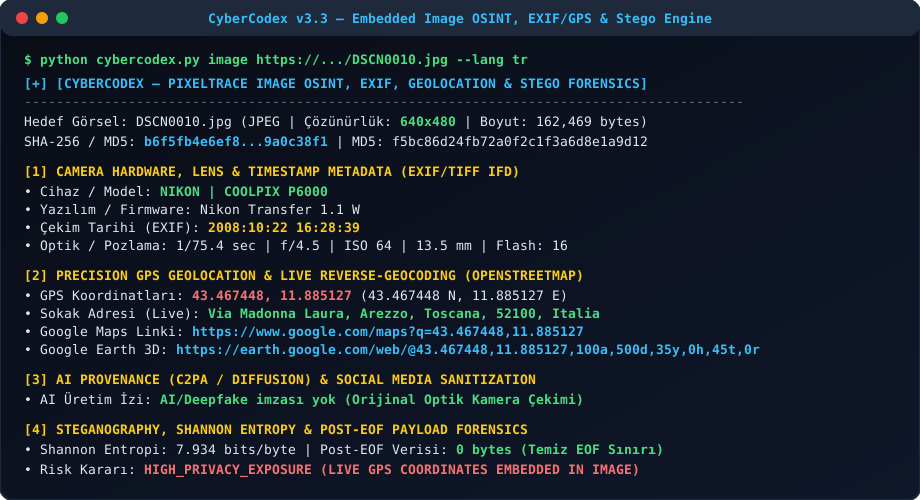
- Raw Binary TIFF / EXIF / IFD0 / GPSIFD Rational Parser: Unpacks Little-Endian (
II) and Big-Endian (MM) rational pointer arrays to extract Camera Make/Model, Lens, Serial Numbers, Exposure/Optical telemetry, and original timestamps. - Live Street-Level Reverse-Geocoding: Converts
GPSIFDDMS rational tuples into signed Decimal Coordinates and queries OpenStreetMap Nominatim to resolve the exact country, city, neighborhood, and street address alongside direct Google Maps and Google Earth 3D pivot links. - Post-EOF Steganography & Polyglot Carving: Calculates exact JPEG (
FF D9) and PNG (IEND) structural end boundaries and carves hidden archives (ZIP/PK), executables (MZ/ELF), PDFs, or cleartext strings appended after EOF. - AI Provenance & Social Media Stripping Detection: Detects
C2PA / JUMBFContent Credentials, Stable Diffusion (Automatic1111), ComfyUI, Midjourney, and DALL-E generation prompts, as well as WhatsApp / Instagram / Telegram metadata sanitization patterns.
🧪 Running the Test Suite
python -m unittest discover -s tests -v
📄 License
Released under the MIT License. Engineered by Çınar (prox0959).