
matthart1983/netwatch
matthart1983/netwatch has 3,584 GitHub stars and 167 forks. GitHot measured +3 stars in 24 hours. Last checked 2026-11-08 16:38 UTC. Last push 2026-11-01.
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
Measured star growth
- in 24h
- +3
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
Original
NetWatch
Network diagnostics in your terminal.




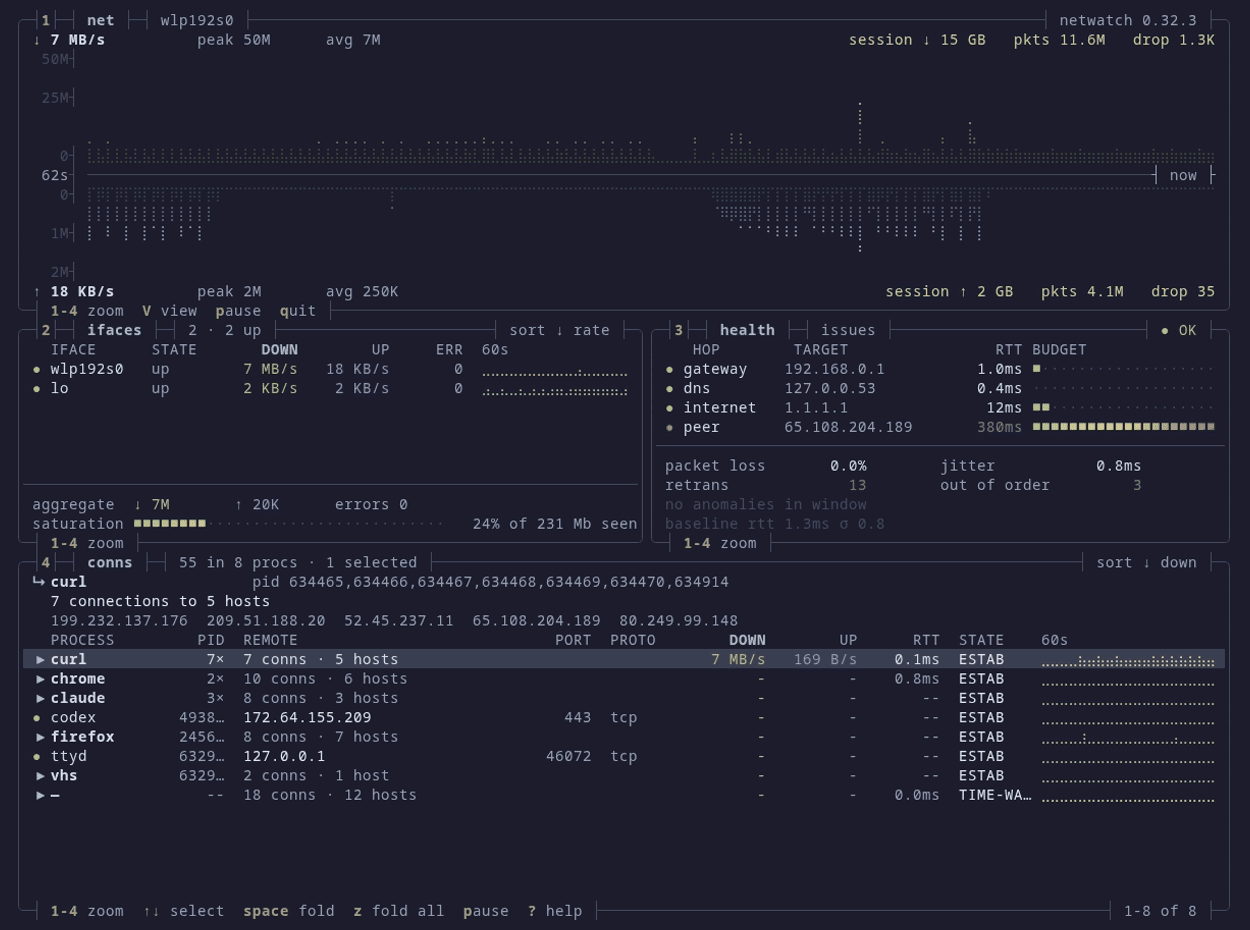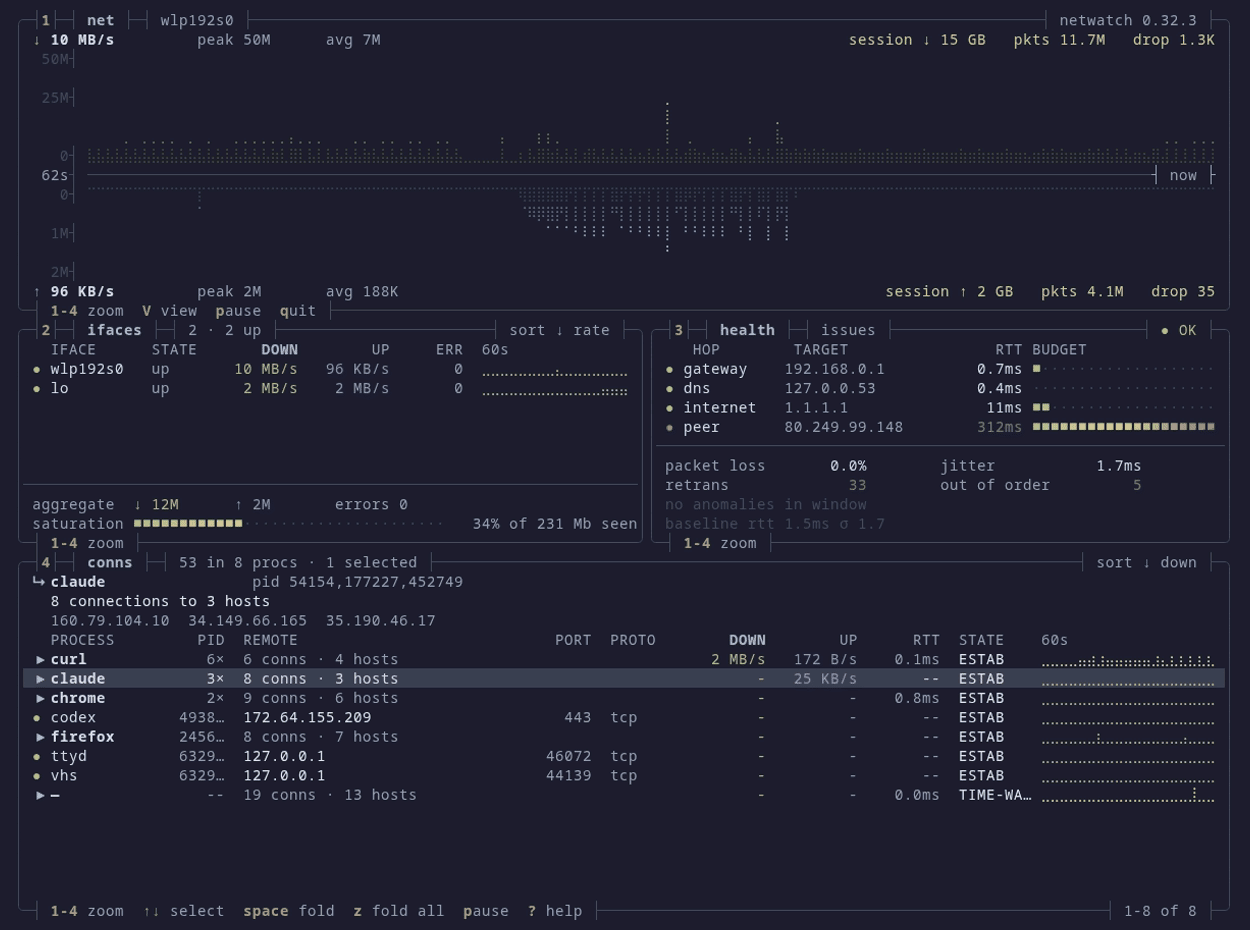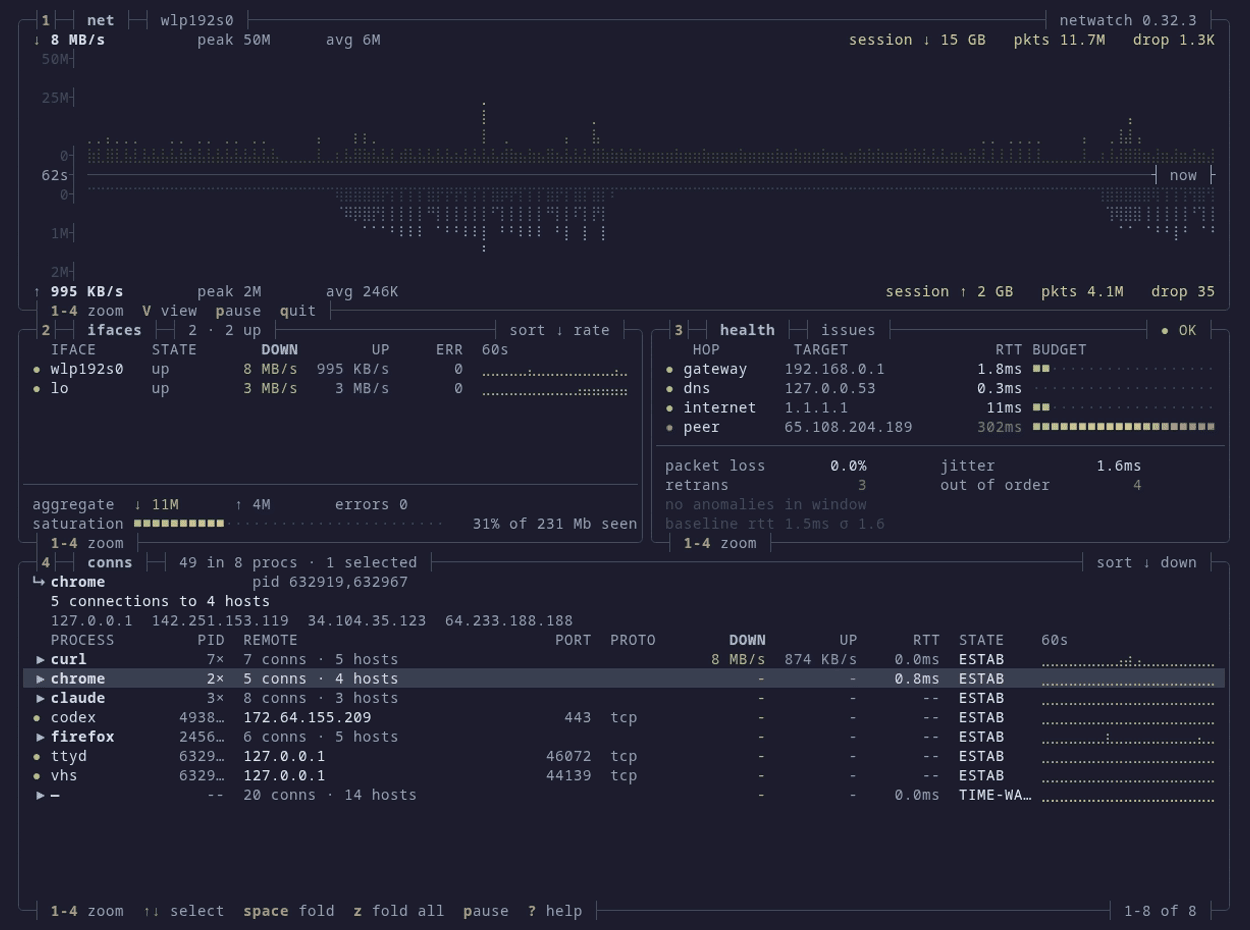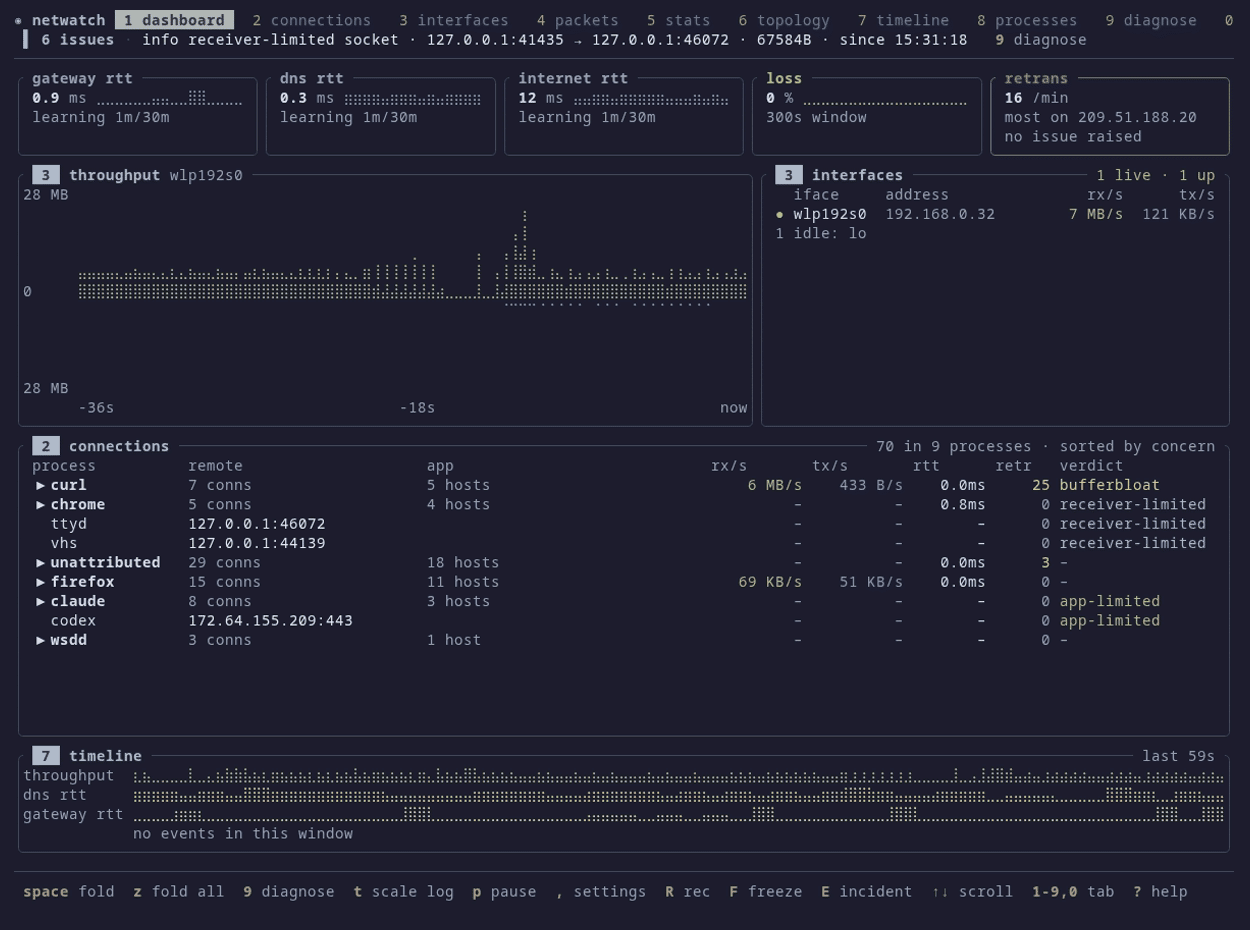
netwatch --view dense. Four boxes, no chrome, every keybind on a border. Download grows up from the axis, upload grows down.
Featured in 35 Self-Hosted Projects on GitHub by Github Awesome.
One binary, no config. netwatch with capture permissions gives you live capture with L7 decode, process attribution where available, and a diagnostic engine that opens an issue when a learned baseline breaks and closes it when the fix holds.
Install
brew install netwatch                 # macOS / Linux
scoop install netwatch                # Windows (needs Npcap)
cargo binstall netwatch-tui           # prebuilt binary (needs cargo-binstall)
cargo install netwatch-tui            # build from source, anywhere with Rust
paru -S netwatch-tui                  # Arch (AUR)
nix-shell -p netwatch                 # NixOS / Nix
conda install -c conda-forge netwatch # conda / mamba (Linux, macOS)
Debian / Ubuntu (apt repository):
curl -fsSL https://matthart1983.github.io/netwatch/apt/netwatch.gpg \
  | sudo tee /usr/share/keyrings/netwatch.gpg >/dev/null
echo "deb [signed-by=/usr/share/keyrings/netwatch.gpg] \
https://matthart1983.github.io/netwatch/apt stable main" \
  | sudo tee /etc/apt/sources.list.d/netwatch.list
sudo apt update && sudo apt install netwatch
Fedora: sudo dnf copr enable matthart1983/netwatch && sudo dnf install netwatch
Container: docker run --rm -it --net=host --pid=host --cap-add=NET_RAW ghcr.io/matthart1983/netwatch
Binaries for macOS, Linux (x86_64, aarch64, armv5te), FreeBSD (x86_64) and
Windows are on the
releases page, with
.deb, .rpm, checksums and signed provenance. The Linux builds are static and
need nothing installed; Windows needs Npcap.
FreeBSD is best-effort. netwatch-freebsd-x86_64 is built on FreeBSD 13.5 and
dynamically links the base system's libc and libpcap, so it needs FreeBSD 13 or
newer (it cannot be static). On anything older, build from source with
cargo install netwatch-tui.
Verifying a download ·
every channel.
Run
Packet capture needs elevated access. On Linux, grant cap_net_raw,cap_bpf,cap_perfmon+eip to a binary restricted to a netwatch group, or run the systemd unit. sudo netwatch works, but as root the sandbox is defence in depth only and containment is limited. See the threat model.
netwatch              # interfaces, connections, config. No privileges.
sudo netwatch         # works; root containment is limited
netwatch --lite       # one 80x24 screen
netwatch --view dense # four boxes, 130x44 or larger
1 to 9 and 0 switch tabs, V cycles the three views, ? shows every key.
Without the TUI
netwatch doctor                          # what netwatch can see on this host, and why not
netwatch diagnose run --budget 30s       # one bounded diagnosis; exit 0 clean, 1 issue, 2 no evidence
netwatch diagnose run --format json      # the same, for scripts
netwatch daemon --metrics                # headless; Prometheus /metrics on 127.0.0.1:9464
netwatch uptime --since 7d               # outages this week: when, how long, and which hop failed
netwatch geoip update                    # download the offline GeoIP databases
netwatch --demo                          # replay a recorded Diagnose incident, no capture needed
daemon runs the same collectors with no screen; a systemd unit and a launchd agent ship with it, and Prometheus export lists the metrics. --remote URL with NETWATCH_API_KEY streams snapshots to a backend you run. Both stay accepted through 1.x, and what they do is experimental: the wire format may change. So are AI Insights, netwatch resolver set and recover, and the JSON in PCAPNG packet comments: what that covers. Every command and flag.
The tabs
| # | Tab | Shows |
|---|---|---|
| 1 | Dashboard | Latency tiles, mirrored throughput, the link carrying it, connections rolled up per process |
| 2 | Connections | Every socket with process, PID, state, GeoIP, RTT, retransmits |
| 3 | Interfaces | Addresses, MTU, rates, errors, drops |
| 4 | Packets | Live decode, TLS 1.3 decryption, JA4, stream tracking, display filters, PCAPNG and PCAP export |
| 5 | Stats | Protocol breakdown and handshake-timing histogram |
| 6 | Topology | Machine, gateway, DNS, top hosts, traceroute, how long the connection has been up |
| 7 | Timeline | Connections by TCP state, with alerts |
| 8 | Processes | Bandwidth per process |
| 9 | Diagnose | Issue, cause, fix, verified close. report.md from the same objects |
| 0 | Egress | Learned destinations, promoted policy, drift |
Every keybinding, display filters, decoders, themes, configuration.
Views
V cycles all three without a restart; the collectors keep running.
| View | Size | For |
|---|---|---|
| Full | any | The ten tabs above |
Lite (--lite) |
80x24 | An SSH session to a Pi, or a tmux split |
Dense (--view dense) |
130x44+ | The hero image: four boxes, braille throughput, kernel TCP detail |
Docs
| Reference | Keys, filters, decoders, configuration, permissions |
| Stability | What 1.0 promises, and what stays experimental |
| Diagnose | Baselines, the 30 rules, ranked causes, verified closes |
| TLS decryption | Point SSLKEYLOGFILE at netwatch and read your own traffic |
| Egress linting | Observe destinations, promote a policy, alert on what you block |
| Security and forensics | Beaconing, scans, DNS tunnelling, JA4, the flight recorder |
| Capability matrix | Platform differences, diagnostic limits and verification scope |
| Attribution evidence | Identity, freshness, coverage denominators and controlled results |
| Doctor command | Read-only setup report, JSON capabilities and optional capture check |
| Design 0.30 | Why the screens look the way they do |
| Architecture | Runtime, source map, permissions model, how to build and verify |
| AI Insights | Optional LLM commentary inside Diagnose, off by default. Experimental |
| Prometheus export | Exposed metrics and scrape config |
| Packaging | Every channel, and what updates it |
| Changelog | Every release |
Diagnose misread your network? Open an issue with what you saw and the output of netwatch diagnose run --format json. It names your gateway and resolver addresses, so edit those out if you'd rather.
Related
SysWatch and DiskWatch share the chrome. ESSH is a Rust SSH client with the same look. NetWatch Cloud is hosted fleet monitoring built on the MIT agent, SDK and dashboard.
Thanks
Much of the packaging is other people's work. Dominiquini and kemelzaidan maintain netwatch-tui and netwatch-tui-bin on the AUR, tomasrivera the nixpkgs package, scillidan the Scoop entry, pavelzw the conda-forge feedstock, and the Homebrew maintainers took the formula into core. File packaging problems with them and netwatch bugs here.
@lamchau, @fdncred and @PeteE sent patches. Everyone who opened an issue with a repro or argued with a design decision is the reason the output is right on more terminals than mine.
Contributing
Discussions, issues, CONTRIBUTING.md.
License
MIT
Explore related projects
codecrafters-io/build-your-own-x
Master programming by recreating your favorite technologies from scratch.
561,103 starspublic-apis/public-apis
A collective list of free APIs
497,339 starsmorluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
444,048 starsopenclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
394,214 stars