
laugiov/scambuster
laugiov/scambuster has 28 GitHub stars and 4 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-14 22:54 UTC. Last push 2026-11-05.
Measured star growth
- in 24h
- 0
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven AI engagement. Multi-agent LLM architecture with adaptive strategy selection.
AIREADME.md
Original
Automated Scambaiting Honeypot & Threat Intelligence Platform


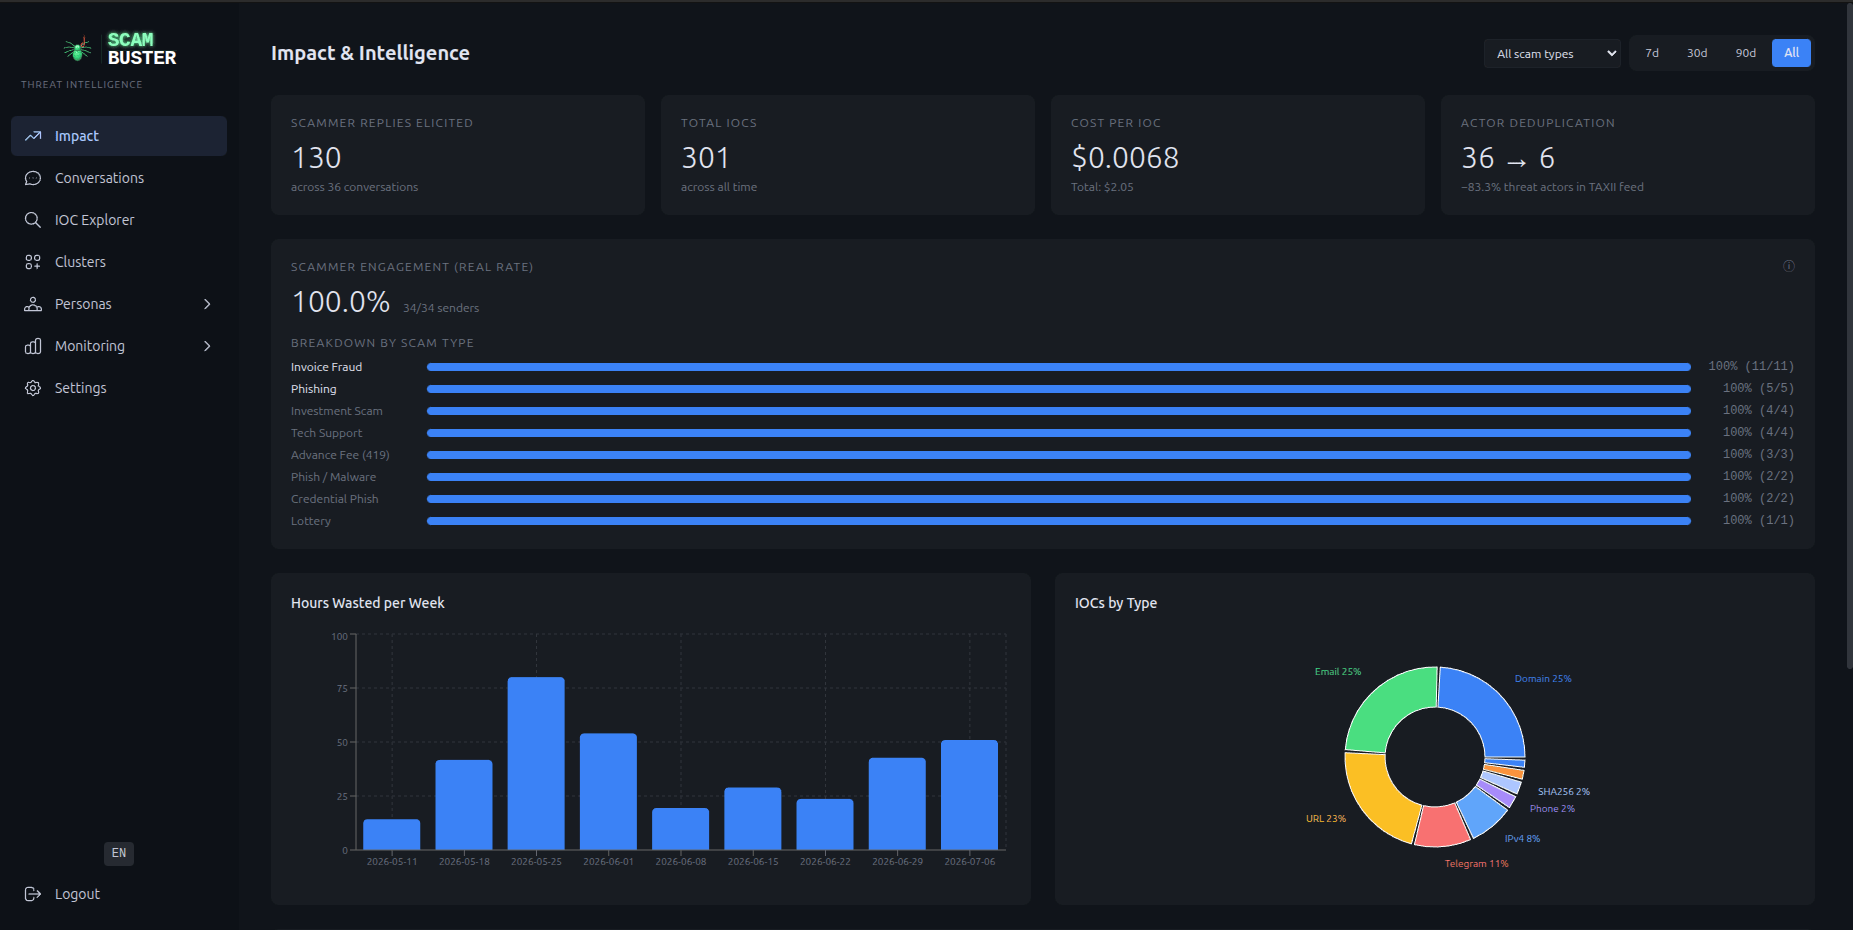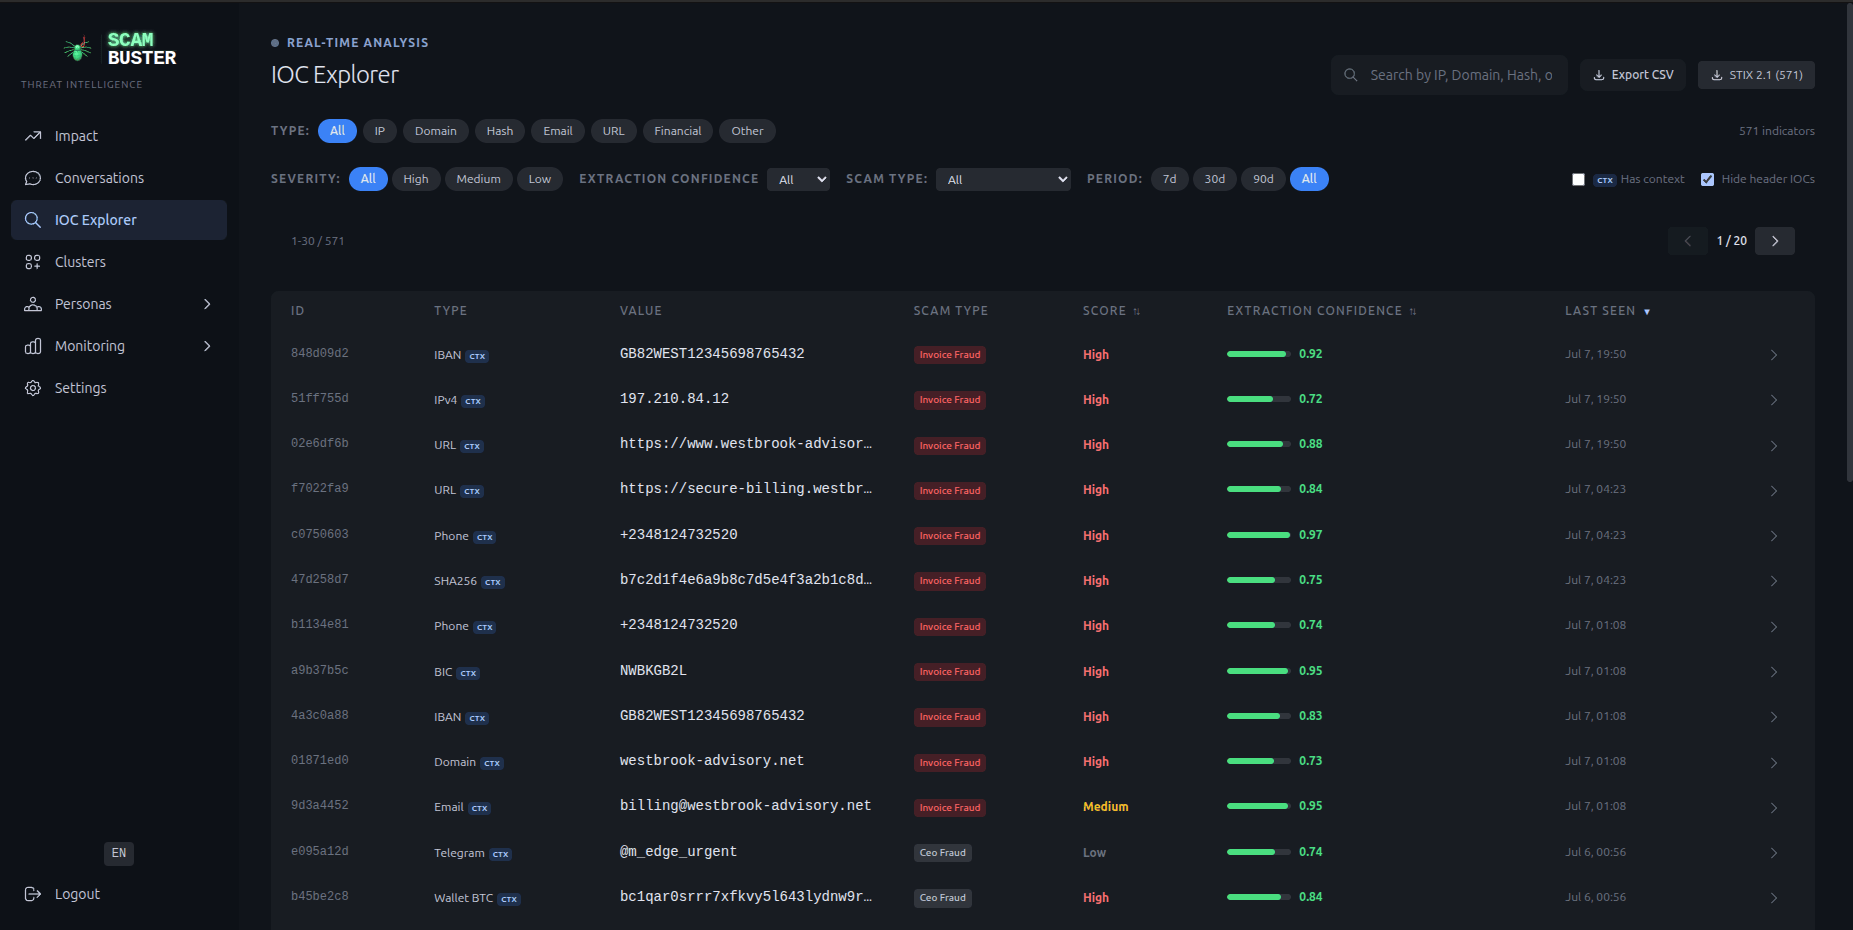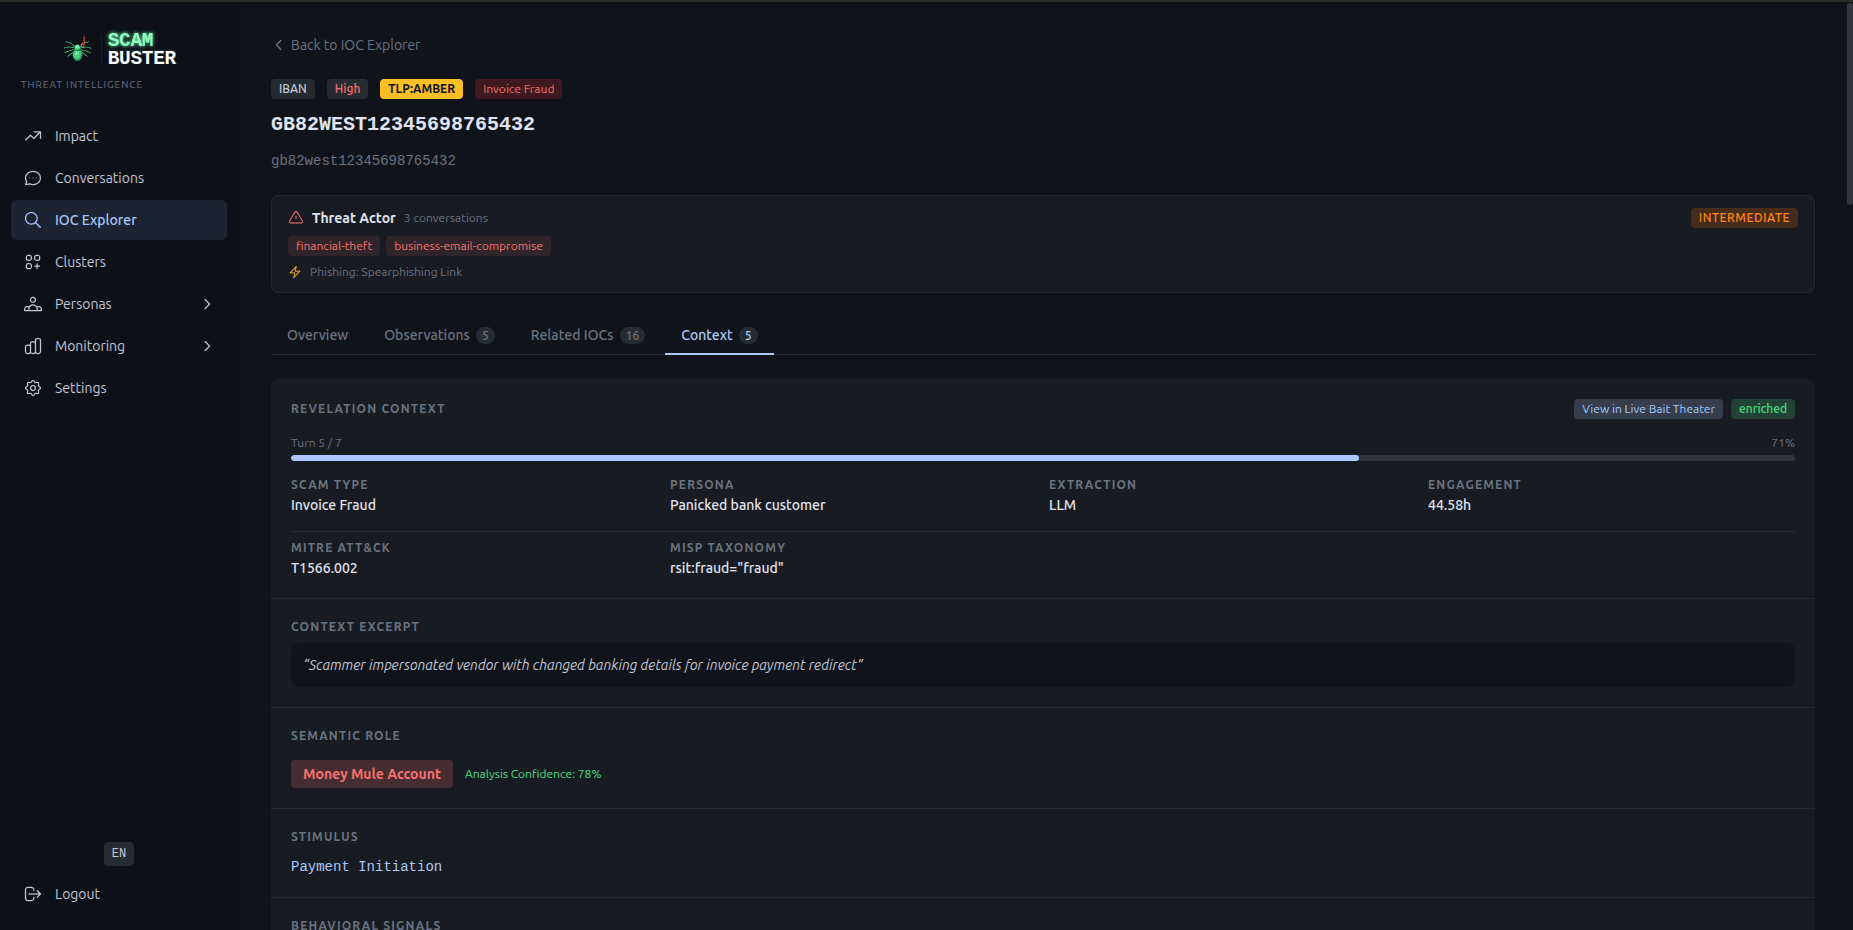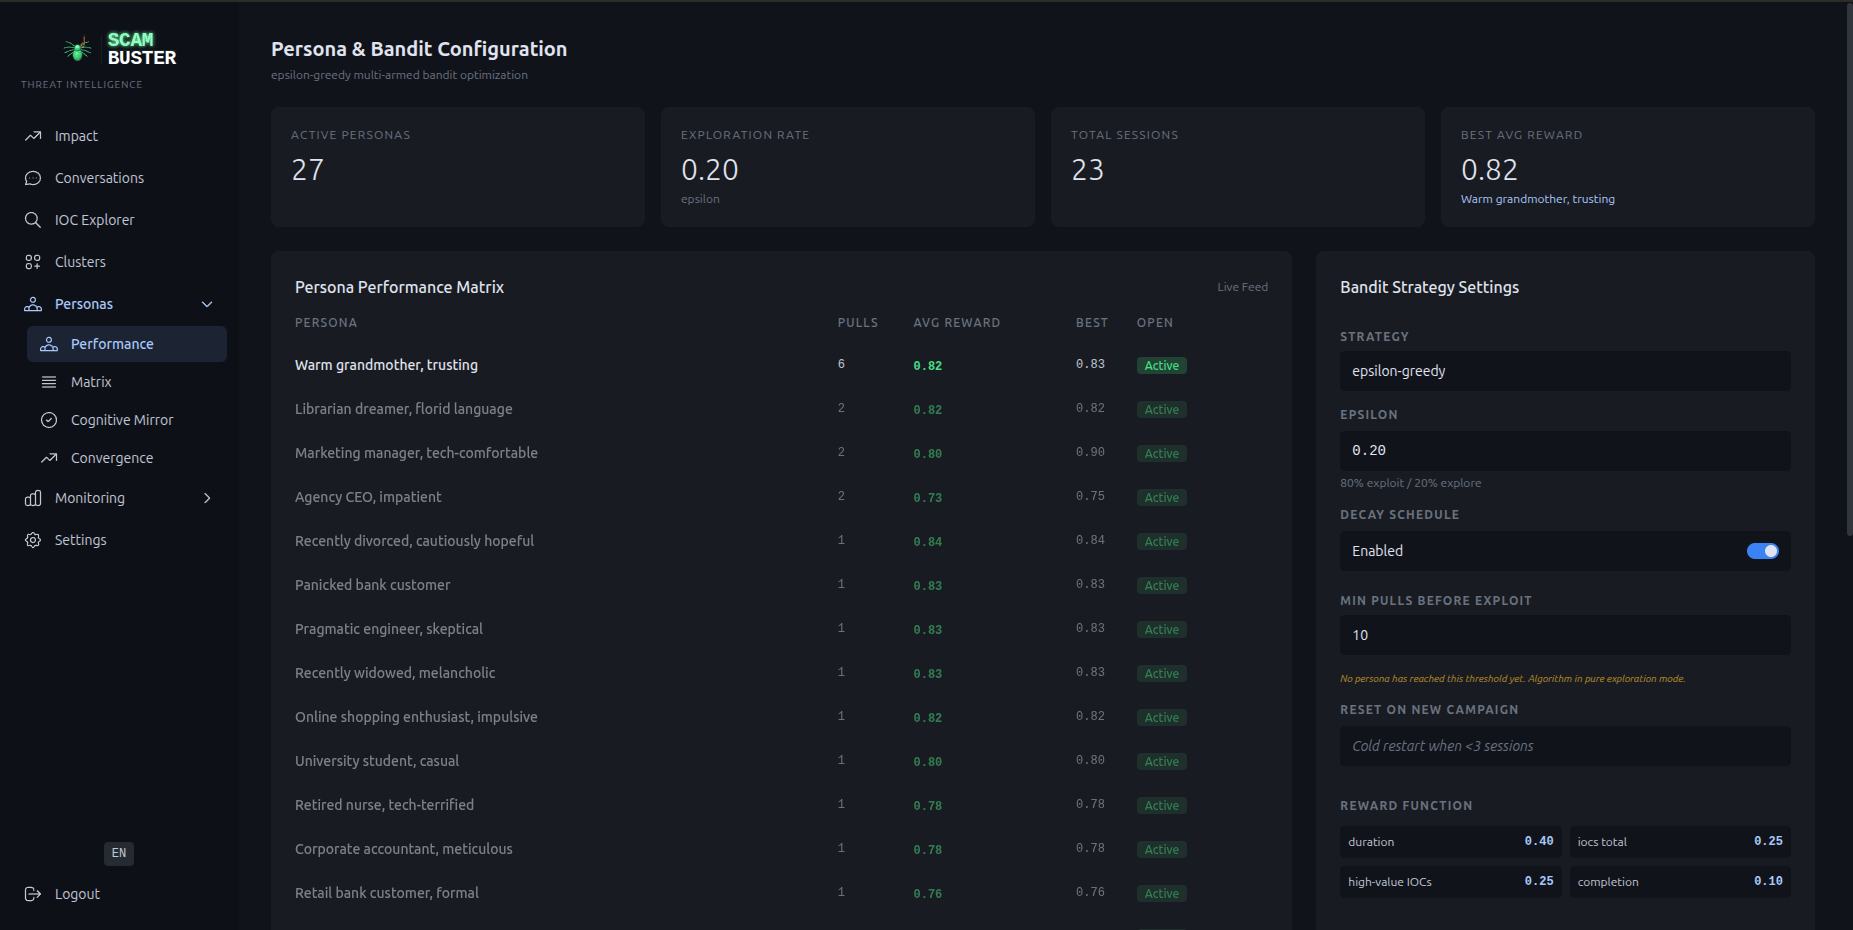
Most security programs block and forget: the mail goes, the attacker's infrastructure and money rails stay unobserved. ScamBuster engages instead, inbound-only and under policy, turning the exchange into IOCs, actor profiles and tagged tactics (why).
ScamBuster was presented at Black Hat USA 2026 in the Human Factor track.
Try it
Hosted demo -- demo.scambuster.ai, login [email protected] / Un1que$trongPassword2024.
Local demo -- make demo-up, then http://localhost:3002: no API key, no account, no mailbox (guide).
How it works
| Agent | Role |
|---|---|
| ScamClassifier | Categorizes the scam (13 types), detects language |
| IocExtractor | Extracts 36 IOC types with context |
| Generator | Writes the persona-driven reply |
| Validator | Safety and quality gate (PolicyGuard + LLM) |
| ConversationDirector | Reads the thread, steers each turn |
| Orchestrator | Runs the pipeline, tracks cost and traces |
| InjectionDetector | Two-layer prompt injection analysis |
| TtpExtractor | Tags scammer tactics, closed taxonomy |
Persona choice is adaptive: epsilon-greedy with UCB1 learns which persona yields most per scam type.
Multilingual by design: detection rules and persona prompts carry non-English content on purpose, so it answers scammers in their own language (details).
What it produces
- STIX 2.1 bundle per conversation -- indicators, threat-actor, sightings, observed-data, attack-patterns, relationships
- TAXII 2.1 server with delta sync
- MISP Event JSON export
- SIEM export in CEF, ECS or JSON, file or syslog
Standards, not per-vendor connectors. Verified end to end against OpenCTI (what lands where); the other three follow the same standards, untested live.
Each conversation produces a threat-actor:
{
  "type": "threat-actor",
  "name": "ScamBuster Actor - INVESTMENT #02114290",
  "sophistication": "minimal",
  "goals": ["financial-theft"],
  "primary_motivation": "personal-gain",
  "threat_actor_types": ["criminal"],
  "description": "Criminal actor operating investment scam."
}
Actors carry ATT&CK mapping, indicates relationships to every IOC, and a psychological profile (profiling, TTPs, API).
Quick start
git clone https://github.com/laugiov/scambuster.git
cd scambuster
cp .env.dist .env    # edit it first, see below
make quickstart      # build, start, migrate, seed, JWT keys, n8n
Fill these 4 in .env before real use:
| Variable | What to do |
|---|---|
LLM_API_KEY |
OpenAI key (or LLM_PROVIDER=mock, no key) |
HONEYPOT_IMAP_USER |
Honeypot mailbox (IMAP, receives scams) |
HONEYPOT_IMAP_PASSWORD |
App password, not the account password |
MAILER_DSN |
SMTP for replies, @ written as %40 |
Left as placeholders, it boots in demo mode and says so. Quickstart · demo · AI install · production · architecture · roadmap · all docs.
Limitations
- Email only, inbound only. No SMS, chat or voice; it never writes first.
- Not a control. It blocks and filters nothing; it does not replace mail security.
- One verified export path. OpenCTI; TAXII, MISP and SIEM are untested live.
- No published metric for the TTP module -- it postdates the evaluation window; precision awaits an operator-run audit.
- Read-only review. The TTP queue is triage only; campaign attribution stays manual.
- Output depends on the model. Mock replies are synthetic; personas and rules are seed data you tune; demo data is seeded, not live output.
- One host, your risk. Docker Compose on one machine, no HA; local legality is yours to establish.
Security & ethics
ScamBuster is a defensive research tool, not an offensive weapon.
- Inbound-only: engages only after the scammer makes contact
- No unauthorized access: never accesses attacker systems
- Content filtering: PolicyGuard blocks threats, illegal content, real PII
- Rate limiting: hard limits on conversations, messages and LLM calls
- Kill switch: halt at workflow, API, database or infrastructure level
- GDPR: data minimization, retention policies, encryption at rest
Responsible use is the operator's responsibility. Confirm your deployment is legal where you operate, keep it inbound-only, and never use it to initiate contact, target individuals, harass, or dox. Read the Disclaimer & Responsible Use before deploying.
More: Security & Guardrails, SECURITY.md.
License
Code MIT; docs and dataset CC BY-NC-SA 4.0.
Contributing
See CONTRIBUTING.md, Discussions and Issues.
Contact
Laurent Giovannoni -- scambuster.ai · LinkedIn · SECURITY.md.