
kdwils/envoy-proxy-crowdsec-bouncer
kdwils/envoy-proxy-crowdsec-bouncer has 52 GitHub stars and 8 forks. Star changes are not measured yet. Last checked 2026-11-13 22:52 UTC. Last push 2026-11-09.
What you can do
- Block malicious IPs streamed via CrowdSec decisions
- Bouncer metrics reporting
- Request inspection via CrowdSec AppSec
- Google reCAPTCHA v2
Measured star growth
- in 24h
- Collecting history
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
A lightweight Crowdsec remediation component for envoy proxy and envoy gateway
SecurityREADME.md
Original


CrowdSec Envoy Proxy Bouncer
CrowdSec bouncer for Envoy Proxy using the ext_authz filter.
[!WARNING] This project is in active development and has not been tested in production environments. Use at your own risk. Breaking changes may occur between releases. For the most stable experience, use a tagged release rather than the
mainbranch.
Features
- Block malicious IPs streamed via CrowdSec decisions
- Bouncer metrics reporting
- Request inspection via CrowdSec AppSec
- CAPTCHA challenges for suspicious IPs with support for:
- Google reCAPTCHA v2
- Cloudflare Turnstile
- Crowdsec AppSec bot challenges
Supported CrowdSec Versions
The following CrowdSec versions have been tested. Other versions may work but have not been validated.
| CrowdSec Version | Status |
|---|---|
| v1.7.0 | ✅ |
| v1.7.2 | ✅ |
| v1.7.3 | ✅ |
| v1.7.4 | ✅ |
| v1.7.6 | ✅ |
| v1.7.7 | ✅ |
| v1.7.8 | ✅ |
| v1.8.0 | ✅ |
| v1.8.1 | ✅ |
| v1.8.2 | ✅ |
How It Works
Integrates with Envoy as an external authorization service. Each request is evaluated by:
- Extracting client IP from forwarded headers
- Checking CrowdSec decision cache for IP-based ban or captcha decisions
- Inspecting request with CrowdSec AppSec WAF (if enabled)
- Enforcing decisions:
- Allow: request proceeds
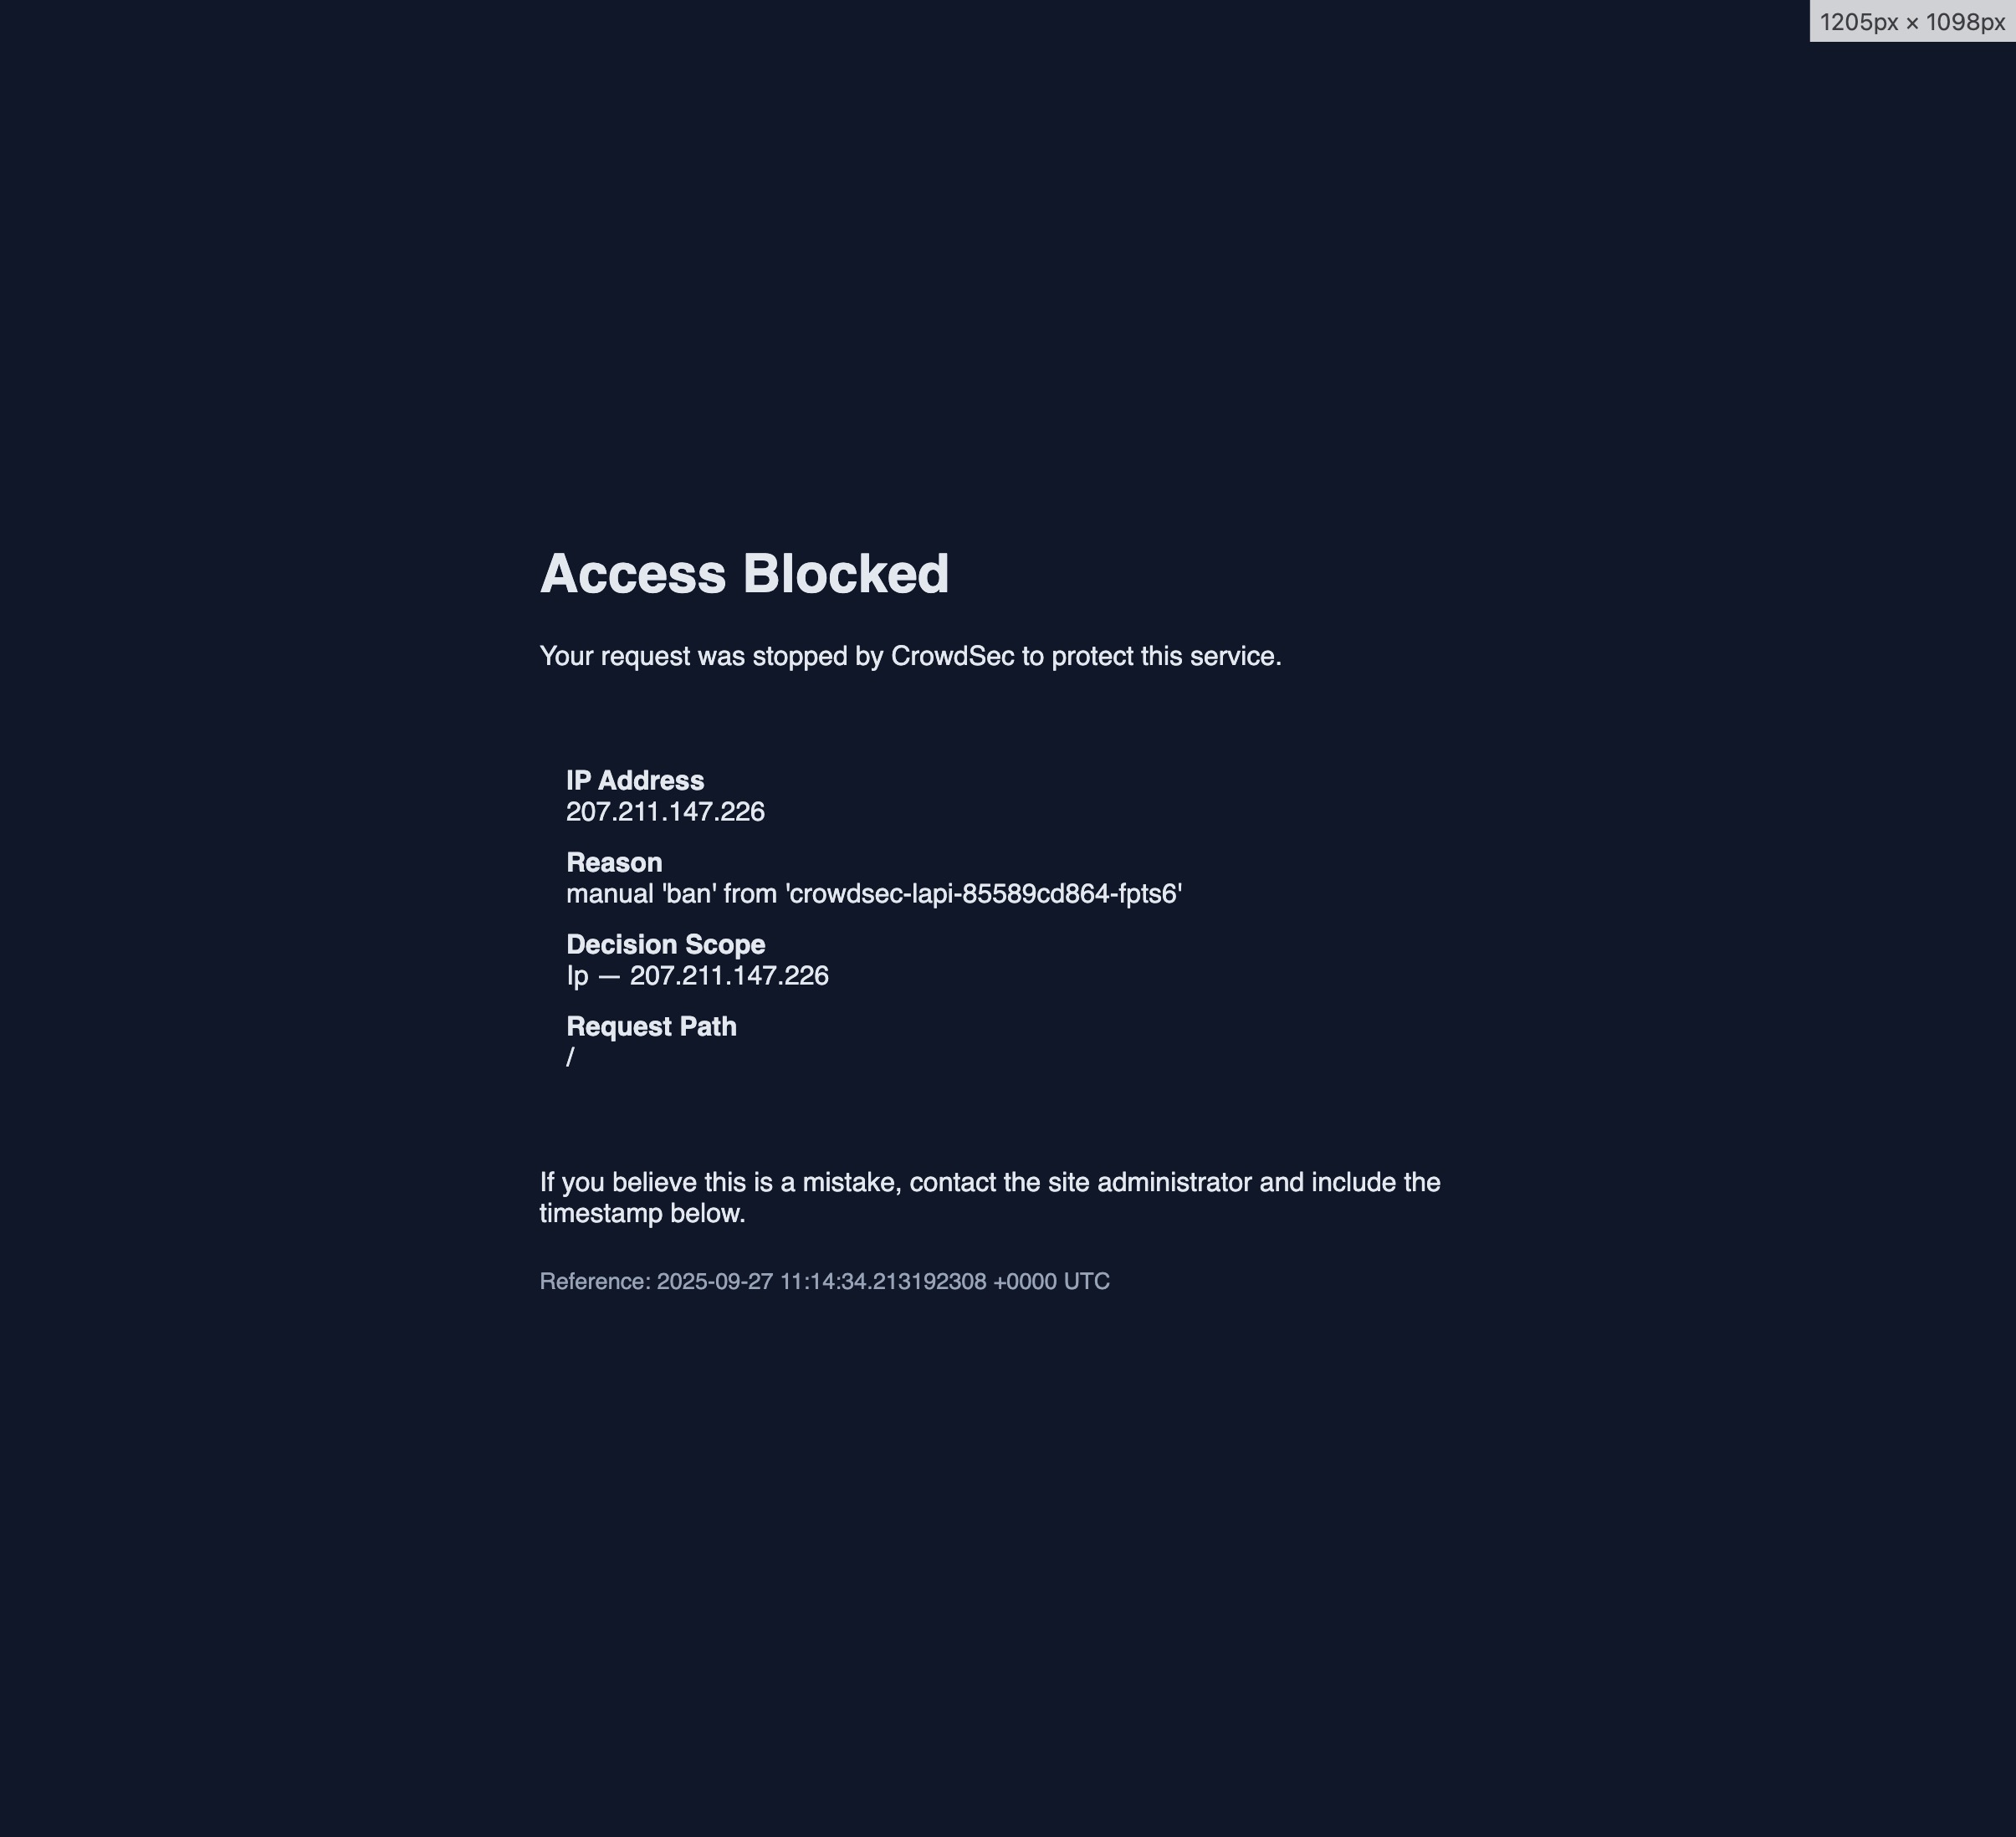
- Ban: return 403 with ban page
- Captcha: redirect to challenge page
- Challenge: pass AppSec's bot challenge page through to the client
Documentation
- Installation
- Configuration Reference
- CrowdSec Integration
- CAPTCHA Integration
- Webhooks
- Custom Templates
- Signing Key Generation
- Deployment Guide
Examples
Acknowledgments
- Helm schema generated with helm-values-schema-json
- Helm docs generated with helm-docs
Explore related projects
trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
258,271 starsHack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers
125,451 starsswisskyrepo/PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
82,660 starscaddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
79,026 stars