
itszeeshan/subdomainx
itszeeshan/subdomainx has 28 GitHub stars and 1 forks. GitHot measured 0 stars in 24 hours and 0 in 7 days. Last checked 2026-11-14 11:13 UTC. Last push 2026-08-08.
Measured star growth
- in 24h
- 0
- in 7 days
- 0
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
About
Subdomain enumeration & reconnaissance framework for bug bounty and pentesting — 20+ tools & APIs, HTTP fingerprinting, port scanning, and subdomain takeover detection in one CLI.
SecurityREADME.md
Original
SubdomainX
Subdomain Enumeration & Reconnaissance Framework
Open-source recon framework for bug bounty, pentesting, and attack surface mapping — 20+ tools & APIs, HTTP fingerprinting, port scanning, and subdomain takeover detection in one CLI.


SubdomainX is a subdomain-focused reconnaissance framework. It started as a subdomain enumerator and grew into a full recon pipeline: it combines 20+ enumeration tools and API services into a single CLI, resolves and fingerprints live hosts (httpx), scans ports (smap), and flags subdomain takeover risks — then exports to JSON, HTML, CSV, or directly into Burp Suite, OWASP ZAP, and Nessus. Run one command and get deduplicated results from subfinder, amass, crt.sh, SecurityTrails, VirusTotal, and more.
Install
go install github.com/itszeeshan/subdomainx/v2@latest
Or download a pre-built binary from the releases page.
Already installed? Update to the latest version with:
subdomainx update
Usage
# Enumerate subdomains with subfinder + HTTP probing
subdomainx --subfinder --httpx example.com

# Multiple tools + API sources
subdomainx --subfinder --amass --crtsh --securitytrails --virustotal example.com

# Multiple domains from a file
subdomainx --wildcard domains.txt --format html

# Export to security tools
subdomainx --subfinder --httpx --format burp example.com   # Also: zap, nessus, csv
Flags go before the domain:
subdomainx --subfinder example.com
Features
Enumeration — subfinder, amass, findomain, assetfinder, sublist3r, knockpy, dnsrecon, fierce, massdns, altdns, waybackurls, linkheader
API Sources — SecurityTrails, VirusTotal, Censys, crt.sh, URLScan.io, HackerTarget
Scanning — HTTP probing via httpx, port scanning via smap
Screenshots — Capture screenshots of discovered subdomains with --screenshot
Tech Fingerprinting — Detect technologies running on subdomains with --tech
Takeover Detection — Check for subdomain takeover vulnerabilities with --takeover
Diff/Monitoring — Compare scans over time with --diff to track changes
Notifications — Get alerts via Slack, Discord, Telegram, or Email with --notify
Interactive TUI — Real-time dashboard with --tui
REST API Server — Run as an API server with subdomainx serve
Reports — HTML, JSON, TXT, CSV, plus Burp Suite, Nessus, and OWASP ZAP formats
Checkpointing — Resume interrupted scans with --resume
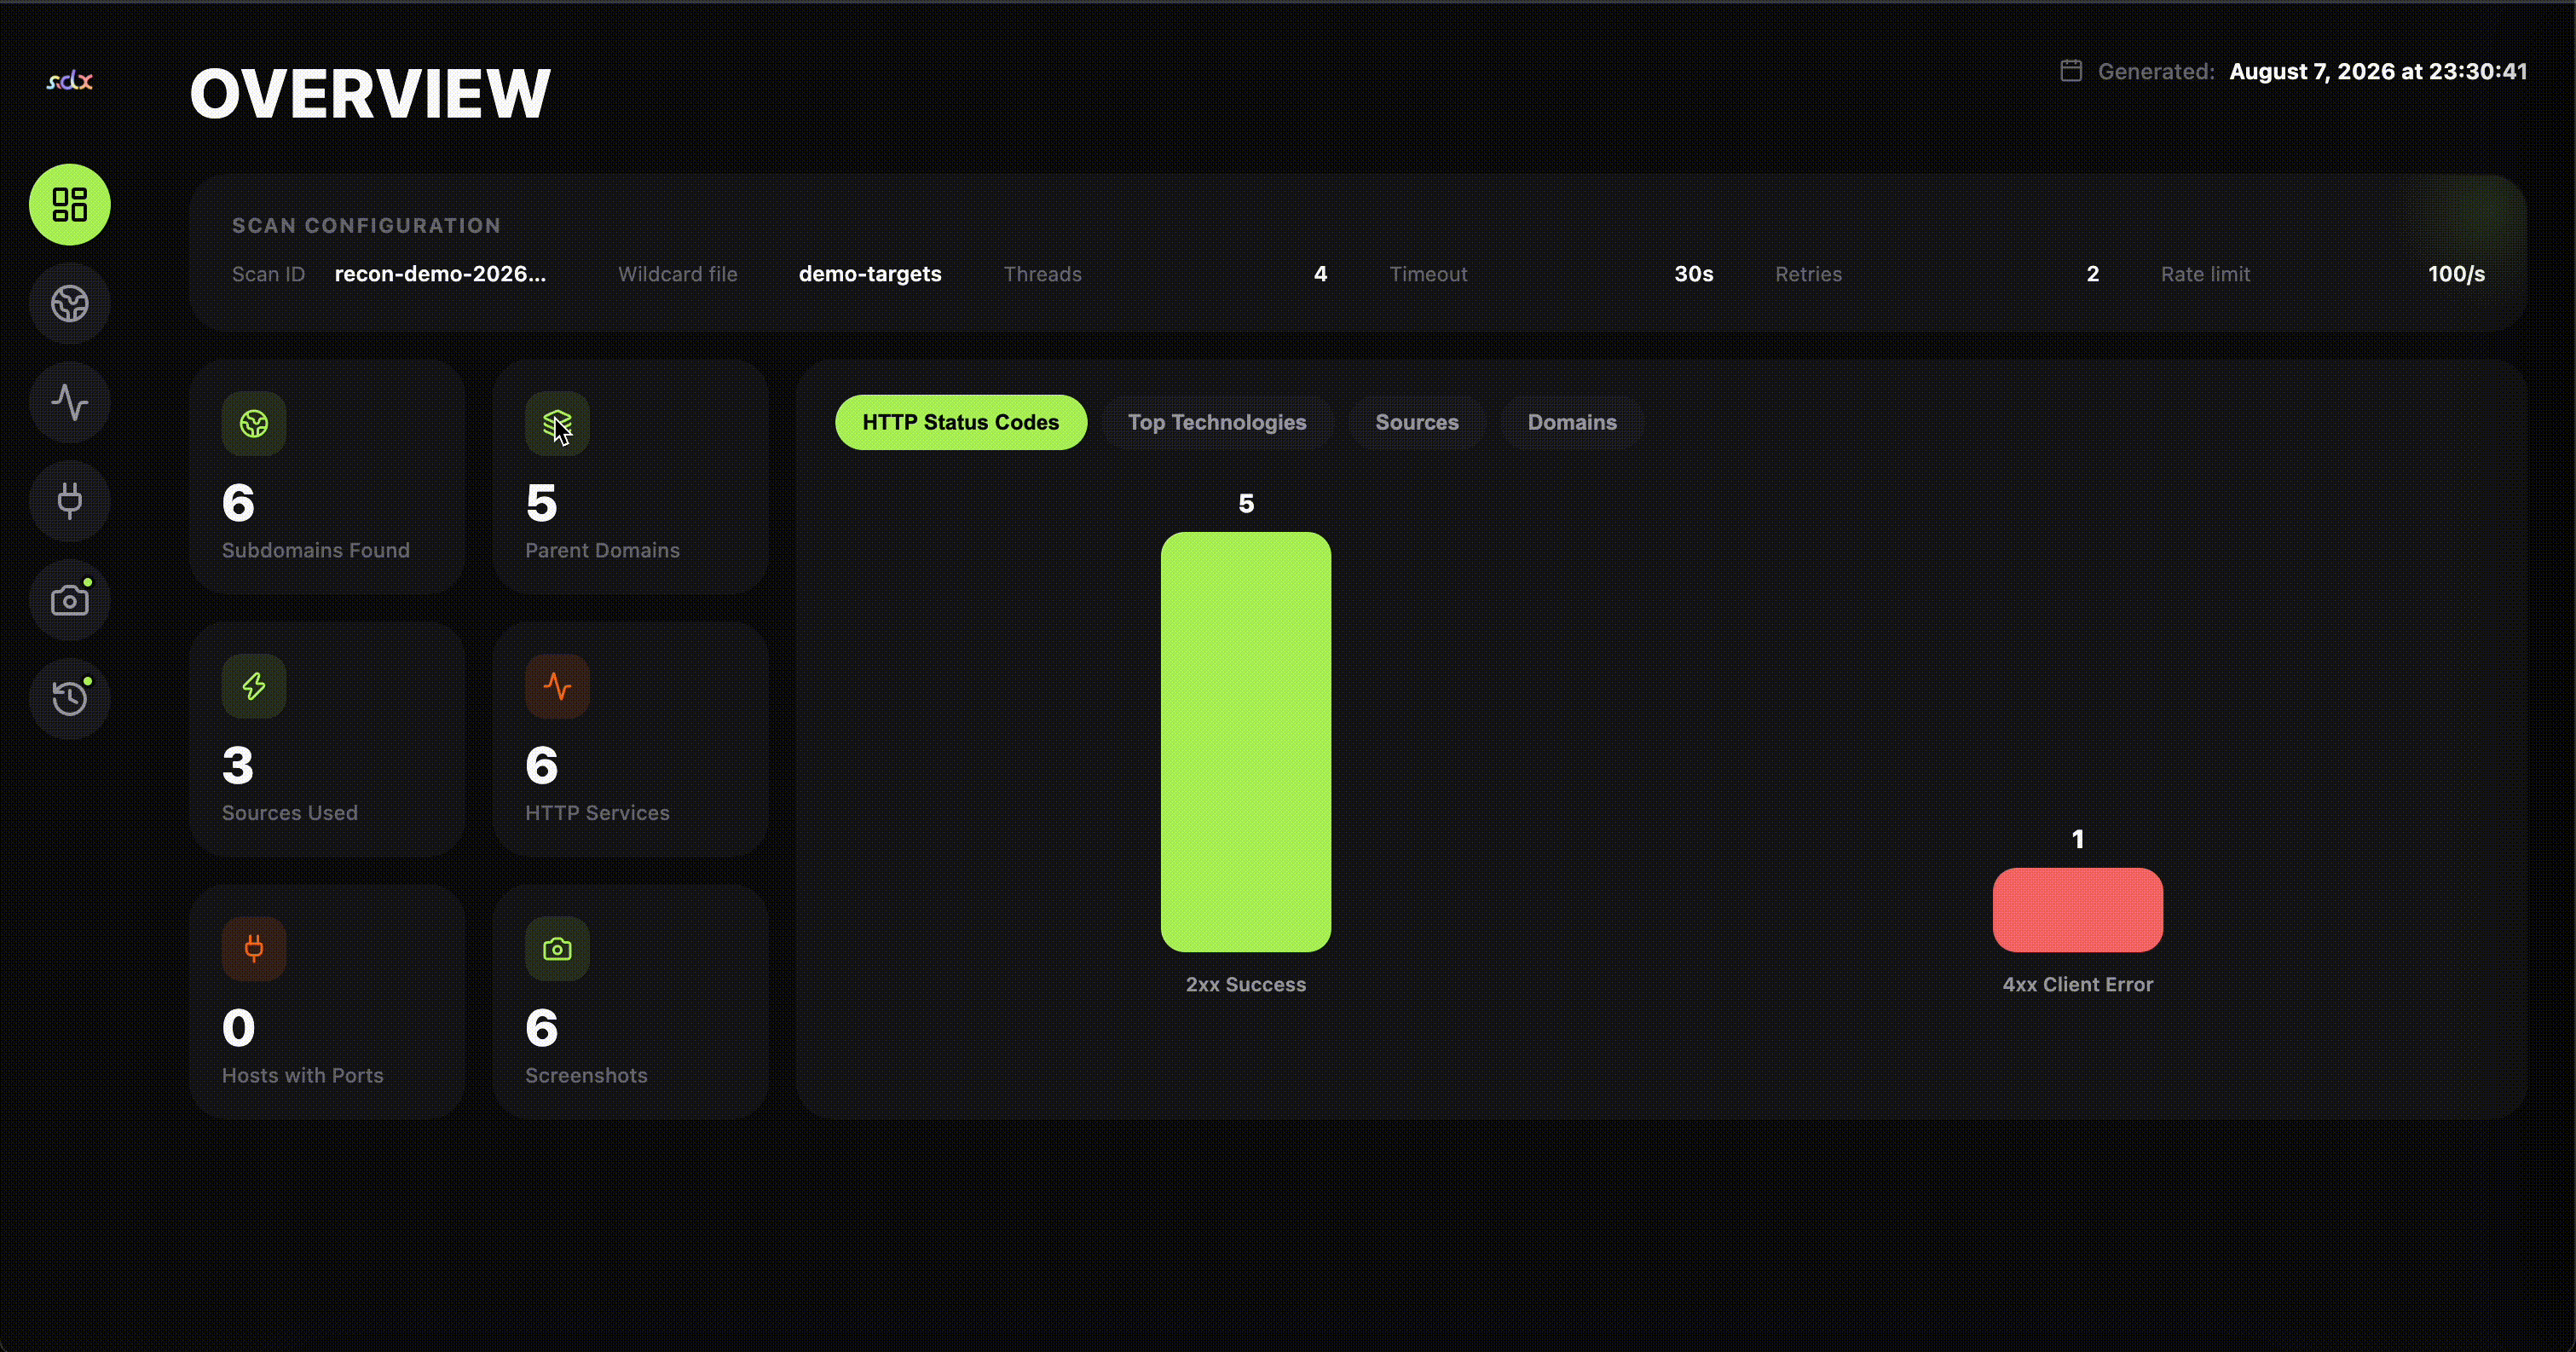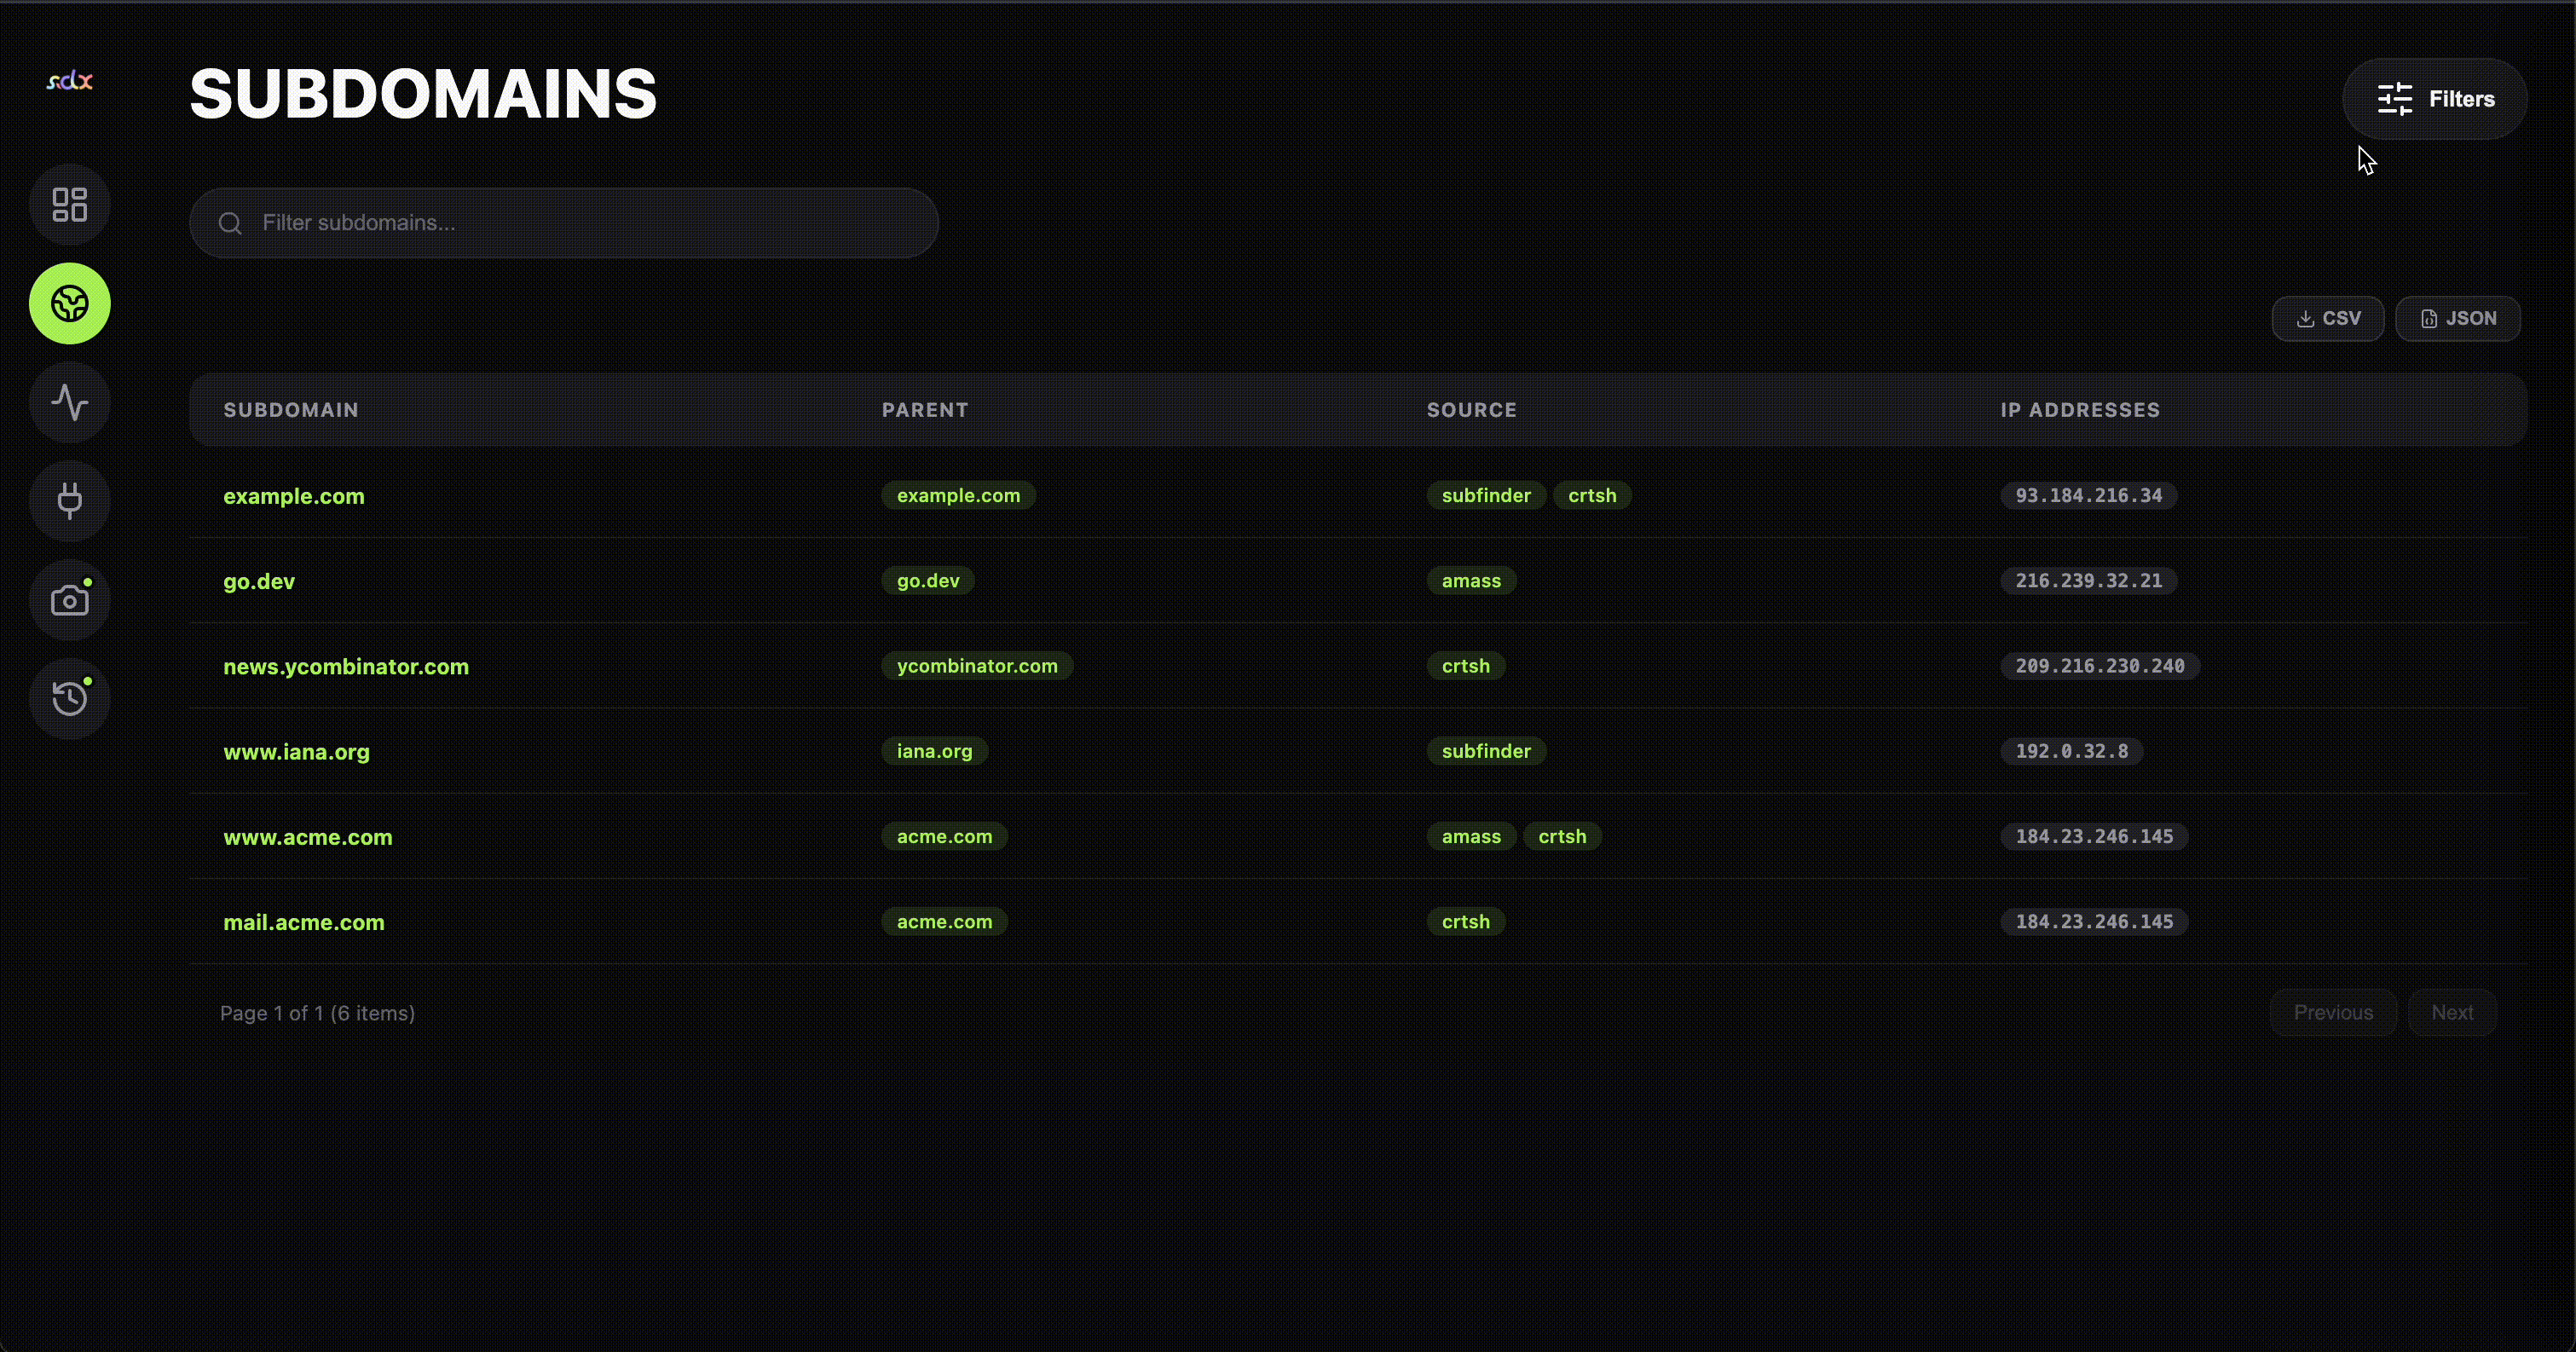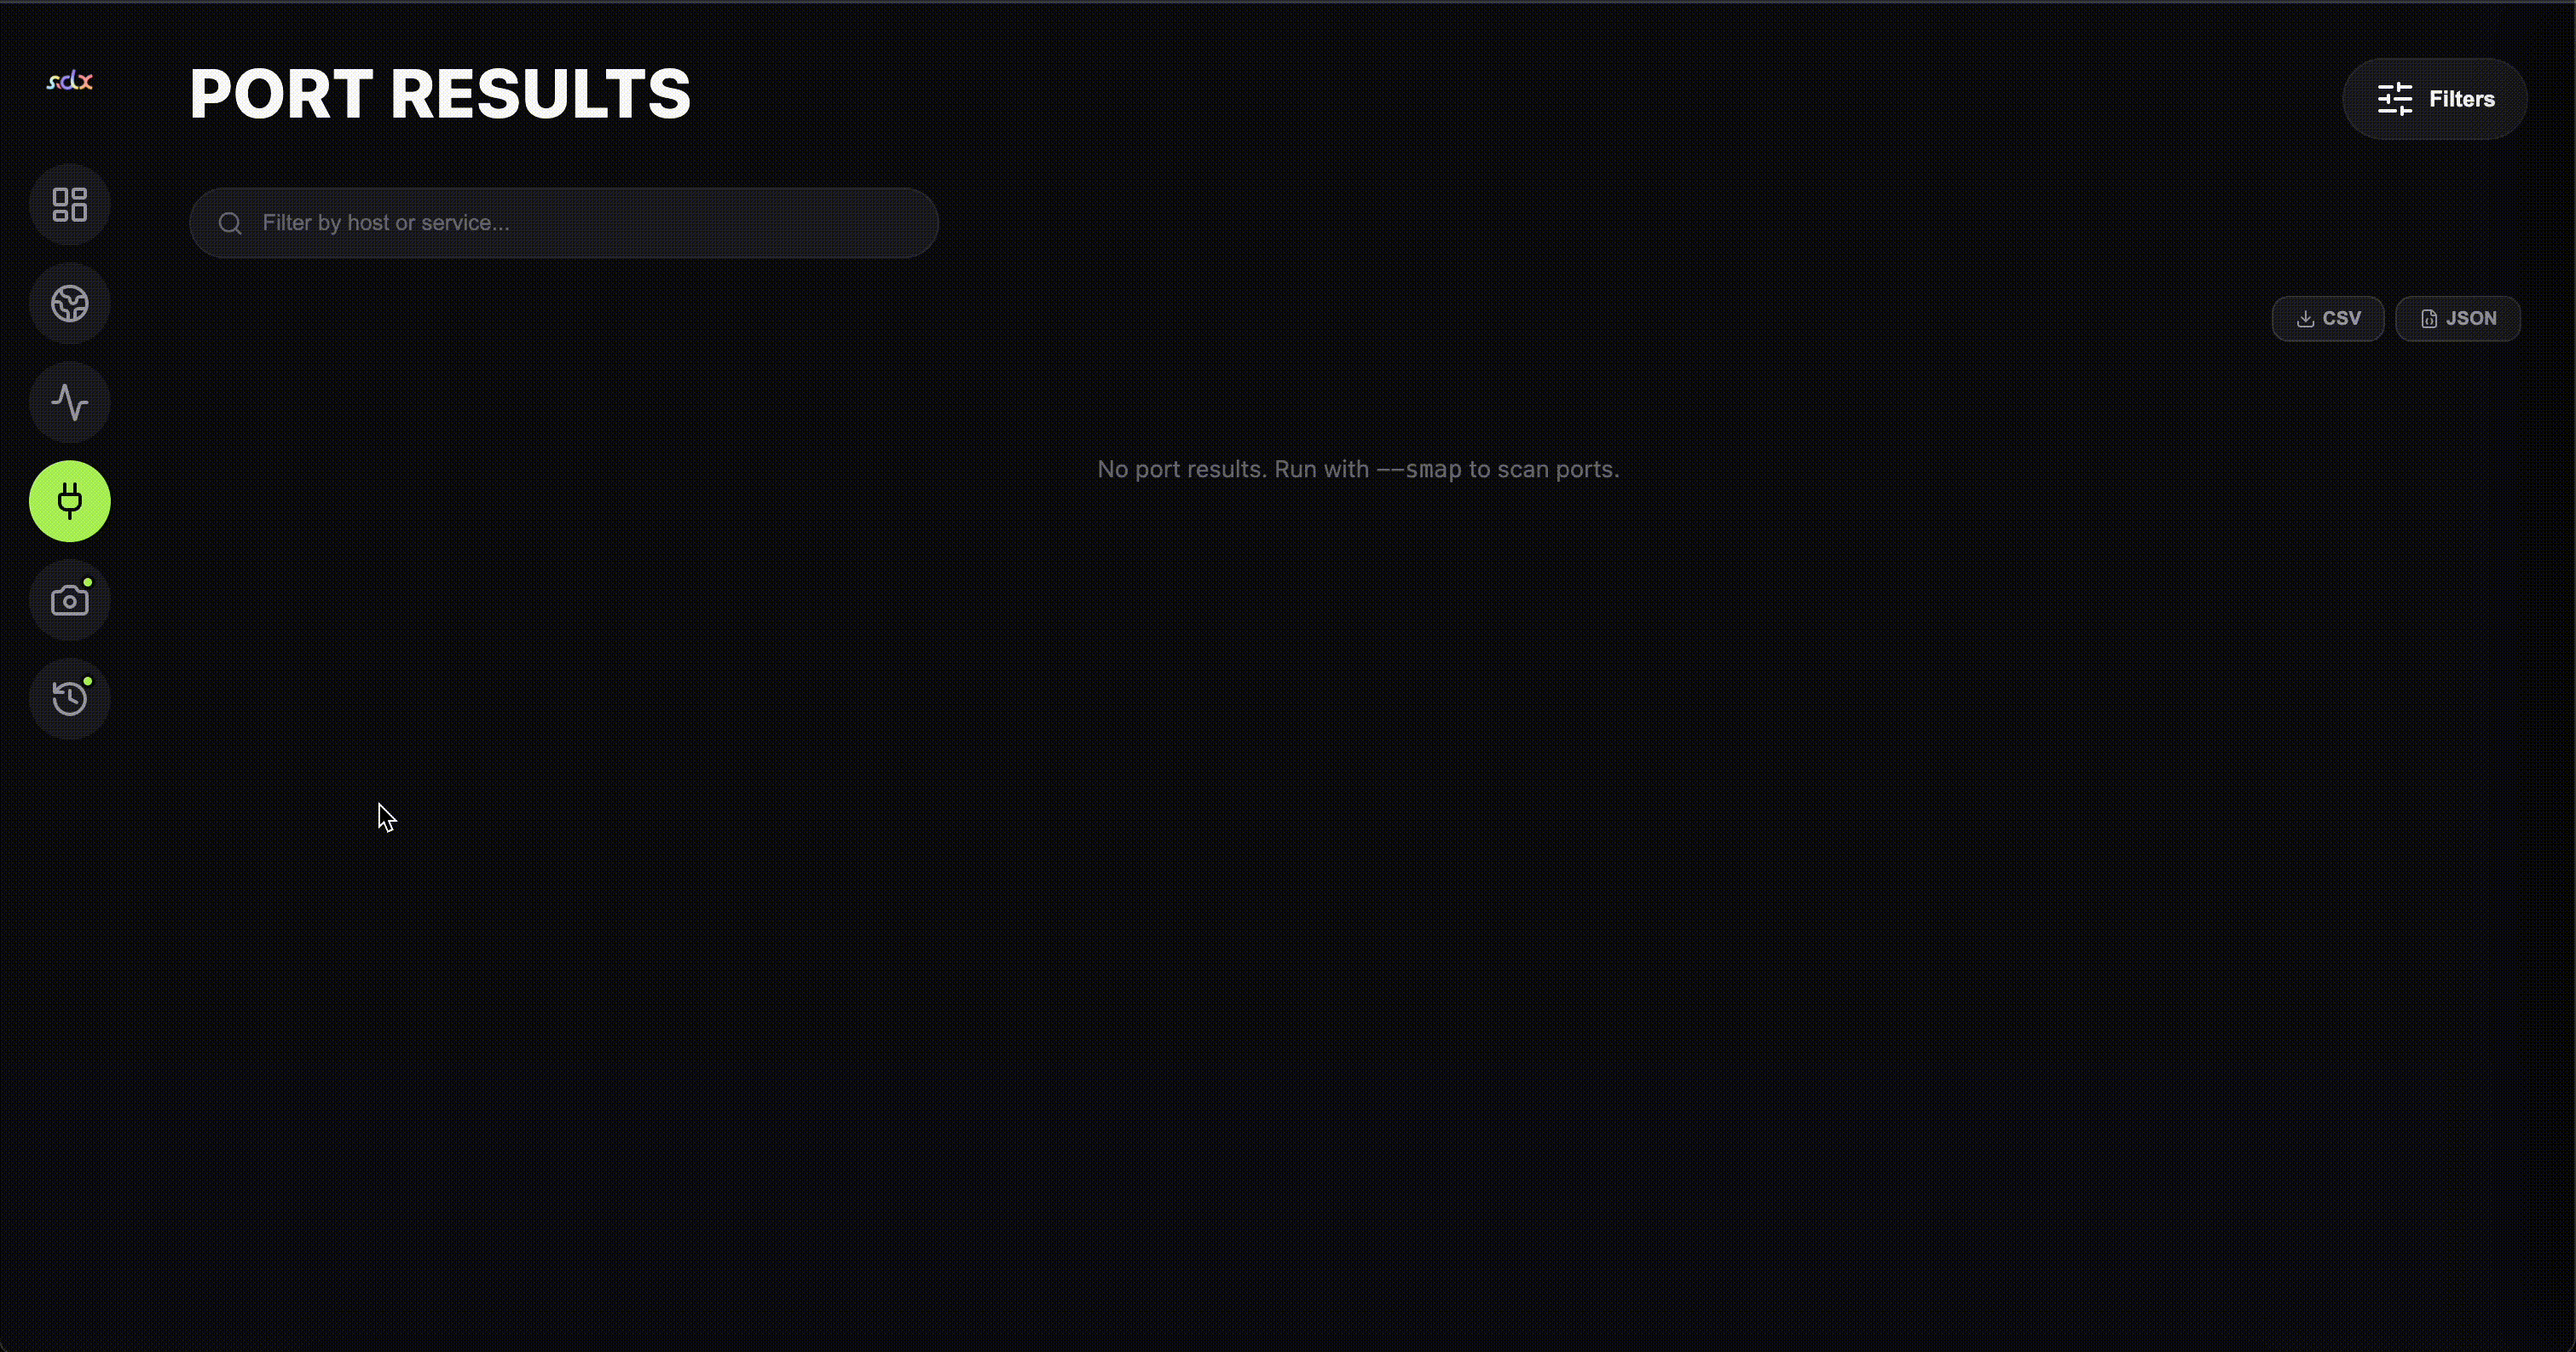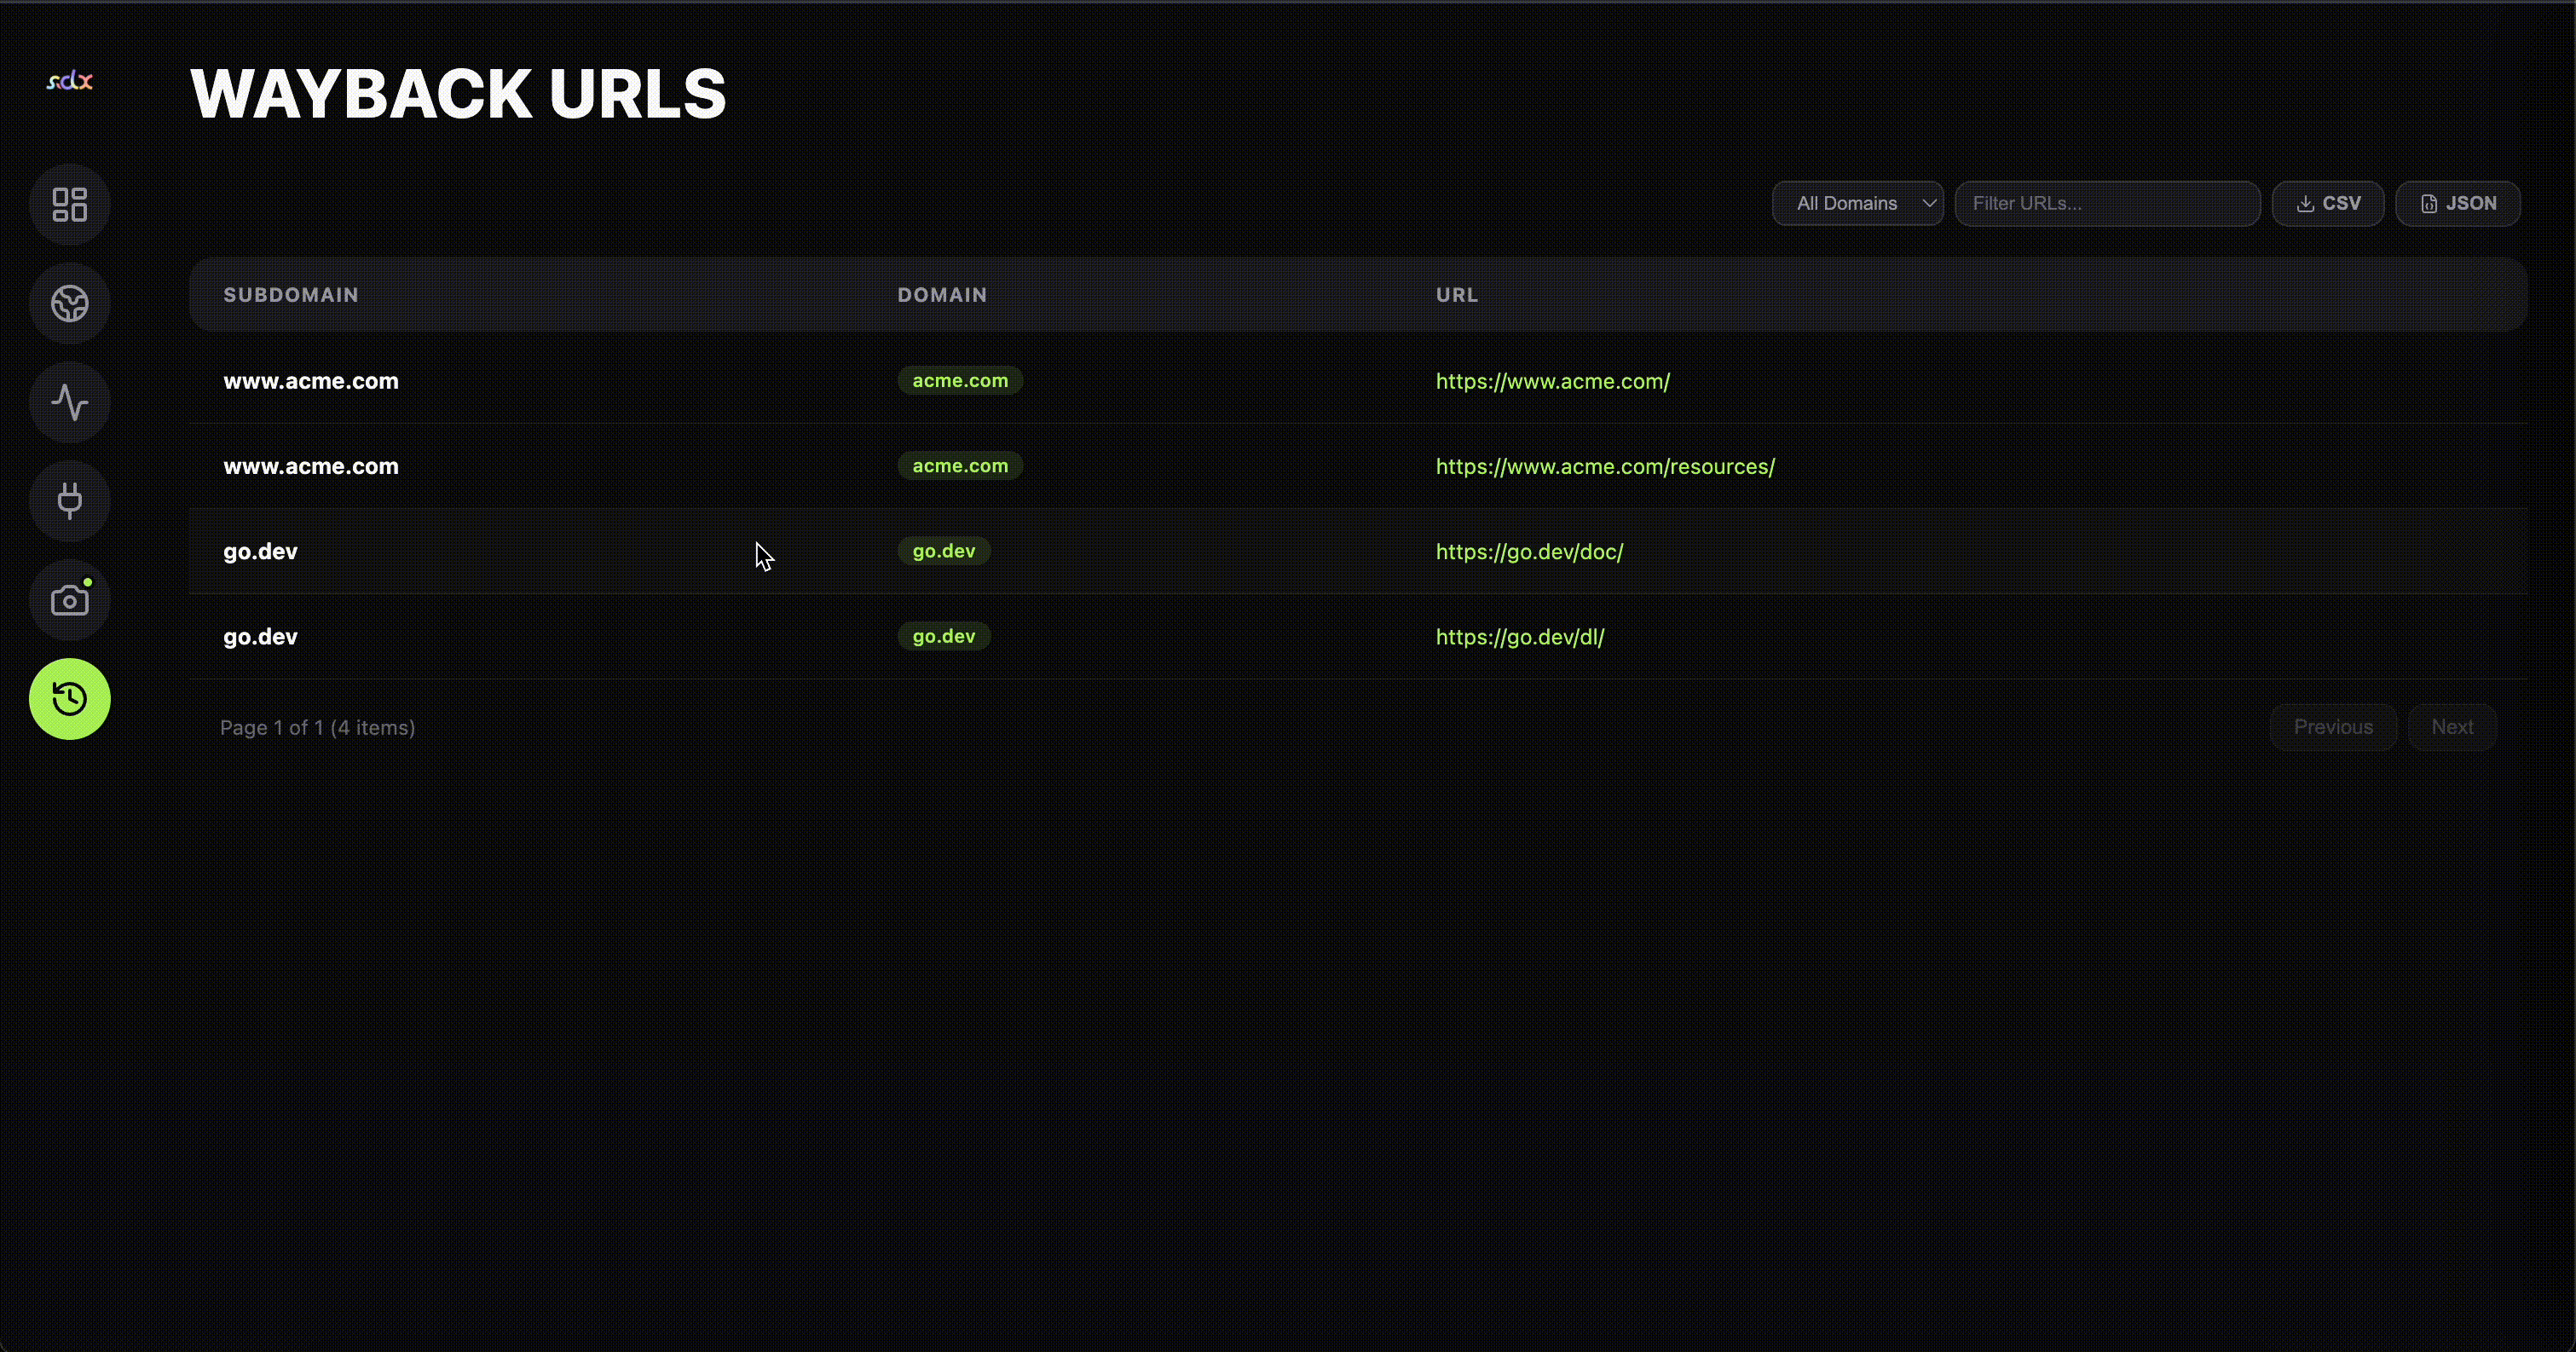
Interactive HTML report
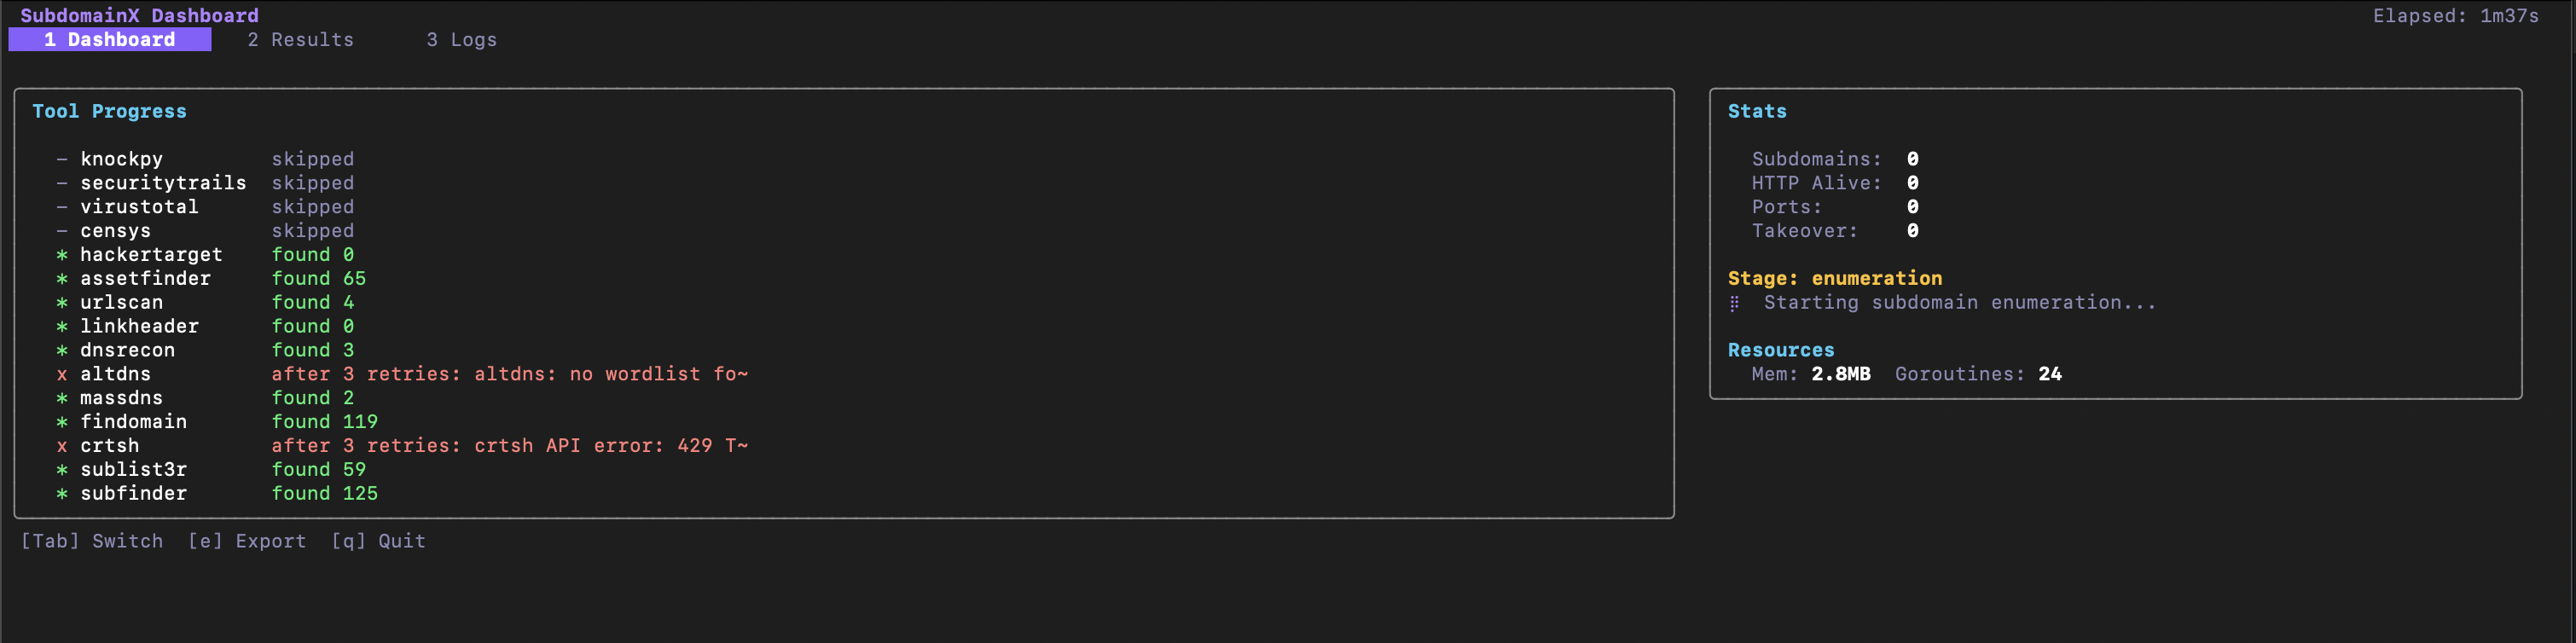
Interactive TUI Dashboard
Documentation
Contributing
We welcome contributions! Here's how you can help:
- Report Bugs: Create an issue
- Suggest Features: Start a discussion
- Submit PRs: Fork the repo and submit pull requests
- Improve Docs: Help us make the documentation better
- Star the Repo: Show your support!
Development Setup
git clone https://github.com/itszeeshan/subdomainx.git
cd subdomainx
go mod download && go build -o subdomainx .
License
MIT — see LICENSE.
SubdomainX is designed for authorized security testing and research purposes only.
- Always ensure you have proper authorization before scanning any domain
- Respect rate limits and terms of service of target systems
- Use responsibly and ethically
- The authors are not responsible for any misuse of this tool
Acknowledgments
- All the amazing open-source tools that make SubdomainX possible
- The security community for continuous feedback and improvements
- Contributors and users who help make this tool better
Happy Hunting! 🎯
Made with ❤️ by Zeeshan
Explore related projects
trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
258,393 starsHack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers
125,487 starsswisskyrepo/PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
82,671 starscaddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
79,034 stars