
grepstrength/malsnitch
grepstrength/malsnitch has 43 GitHub stars and 1 forks. Star changes are not measured yet. Last checked 2026-11-11 04:19 UTC. Last push 2026-08-09.
Secrets scanner with a twist... this is for getting threat actor credentials from MALWARE. Acquire TA creds from FLOSS exports, memdumps, Binja exports, etc. to get C2 credentials, embedded API keys, crypto material, or hardcoded passwords.
What you can do
- Detects embedded crypto keys (AES-128, AES-256, RC4)
- Detects C2 infrastructure
- Detects exfil channel creds (Discord webhooks, Telegram bot tokens)
- Detects hardcoded credentials (SMTP, FTP, HTTP, etc)
Measured star growth
- in 24h
- Update delayed
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
Original
malsnitch
- Reversing some malware?
- Tired of eyeballing string dumps for hardcoded creds?
- Short on time?
Look no further!
malsnitch is a CLI tool meant to assist RE workflows by scanning artifacts like string dumps, FLOSS output, or Binja exports. It extracts embedded secrets malware authors put in their binaries.
- C2 creds
- crypto keys
- API tokens
- exfil channel configs
- more!
TO BE CLEAR - this is not another developer secrets scanner. Tools like TruffleHog or Gitleaks catch API keys being committed to legitimate repos. malsnitch gets the RC4 key buried in .rdata or the SMTP password to a random C2 server.
(Also, I'm proud of myself for not shoehorning in "Go" anywhere in the title.)
AI Disclaimer
Note: All code, infrastructure, and technical work here is mine. I used limited AI assistance to help draft the README and test data.
Features
- Detects embedded crypto keys (AES-128, AES-256, RC4)
- Detects C2 infrastructure
- Detects exfil channel creds (Discord webhooks, Telegram bot tokens)
- Detects hardcoded credentials (SMTP, FTP, HTTP, etc)
- Detects API keys (GitHub PATs, AWS, Stripe, Slack, SendGrid, Mailgun)
- Memory dump scanner
- Auto deduplication and substring suppression
- Structured JSON output to stdout
- Supports multiple input formats:
text: raw strings dump (e.g. strings.exe or FLOSS raw output)floss: FLOSS JSON outputbinja: Binary Ninja export JSON (via the includedbn_export.py)
Usage
- Clone the repo OR install the Go package:
git clone https://github.com/grepstrength/malsnitch.git
cd malsnitch
OR
go install github.com/grepstrength/malsnitch@latest
- Build:
go build -o malsnitch.exe .
- Run against a strings dump:
.\malsnitch.exe -file strings_output.txt -type text
- Run against FLOSS JSON output:
.\malsnitch.exe -file floss_report.json -type floss
- Run against a Binary Ninja export:
.\malsnitch.exe -file bn_export.json -type binja
- Run against a memory dump:
.\malsnitch.exe -file memdump.bin -type memdump
- Pipe JSON output to a file:
.\malsnitch.exe -file sample_strings.txt > <FILENAME>.json
- Save the results to a CSV:
.\malsnitch.exe -file sample_strings.txt -type text -output csv > <FILENAME>.csv
Examples
Try It Yourself
.\malsnitch.exe -file examples\test_strings.txt -type text
.\malsnitch.exe -file examples\test_binja.json -type binja
.\malsnitch.exe -file examples\test_floss.json -type floss
.\malsnitch.exe -file examples\test_memdump.bin -type memdump
Output
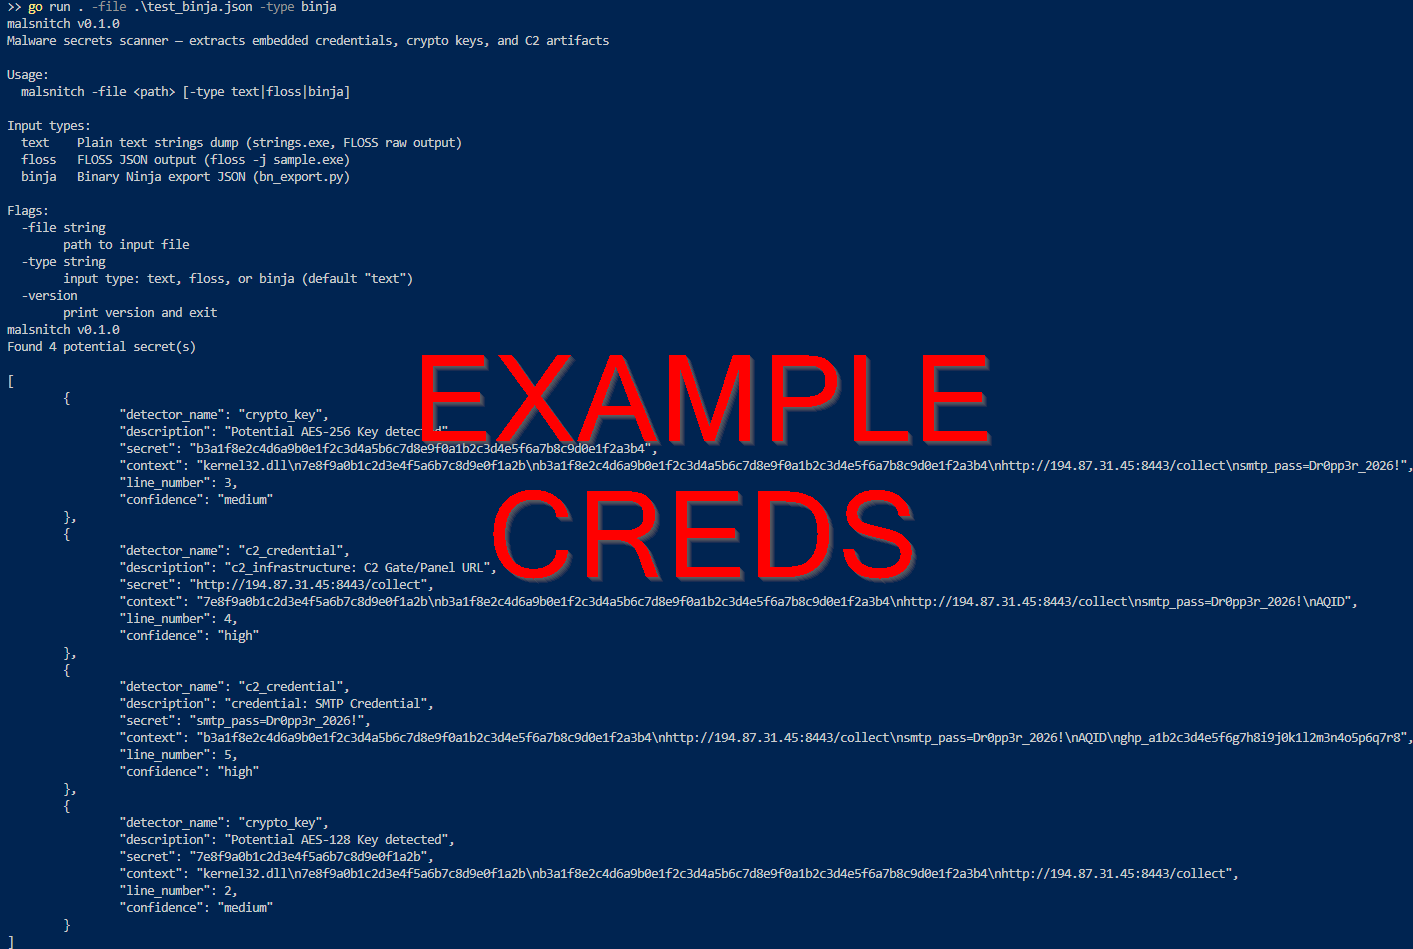
Binary Ninja Plugin
A python export script is included in scripts/bn_export.py. You can run this inside Binja's script console or headless:
python bn_export.py sample.exe output.json
This produces the JSON format that malsnitch consumes with -type binja.
Exit Codes
| Code | Meaning |
|---|---|
| 0 | Secrets found |
| 1 | Error (bad input, missing file, etc.) |
| 2 | Clean scan, no secrets detected |
Future Roadmap
- PCAP input
- MITRE ATT&CK mapping
License
MIT license. No restrictions.
Explore related projects
codecrafters-io/build-your-own-x
Master programming by recreating your favorite technologies from scratch.
561,646 starspublic-apis/public-apis
A collective list of free APIs
498,023 starsmorluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
450,553 starsopenclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
394,312 stars