
anchore/grype
anchore/grype has 13,188 GitHub stars and 934 forks. GitHot measured +10 stars in 24 hours. Last checked 2026-11-06 00:03 UTC. Last push 2026-11-04.
A vulnerability scanner for container images and filesystems
What you can do
- Scan container images, filesystems, and SBOMs for known vulnerabilities (see the docs for a full list of supported scan targets)
- Supports major OS package ecosystems (Alpine, Debian, Ubuntu, RHEL, Oracle Linux, Amazon Linux, and more)
- Supports language-specific packages (Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust, and more)
- Supports Docker, OCI, and Singularity image formats
Measured star growth
- in 24h
- +10
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
Original

Grype
A vulnerability scanner for container images and filesystems.



Features
- Scan container images, filesystems, and SBOMs for known vulnerabilities (see the docs for a full list of supported scan targets)
- Supports major OS package ecosystems (Alpine, Debian, Ubuntu, RHEL, Oracle Linux, Amazon Linux, and more)
- Supports language-specific packages (Ruby, Java, JavaScript, Python, .NET, Go, PHP, Rust, and more)
- Supports Docker, OCI, and Singularity image formats
- Threat & risk prioritization with EPSS, KEV, and risk scoring (see interpreting the results docs)
- OpenVEX support for filtering and augmenting scan results
[!TIP] New to Grype? Check out the Getting Started guide for a walkthrough!
Installation
The quickest way to get up and going:
curl -sSfL https://get.anchore.io/grype | sudo sh -s -- -b /usr/local/bin
[!TIP] See Installation docs for more ways to get Grype, including Homebrew, Docker, Chocolatey, MacPorts, and more!
The basics
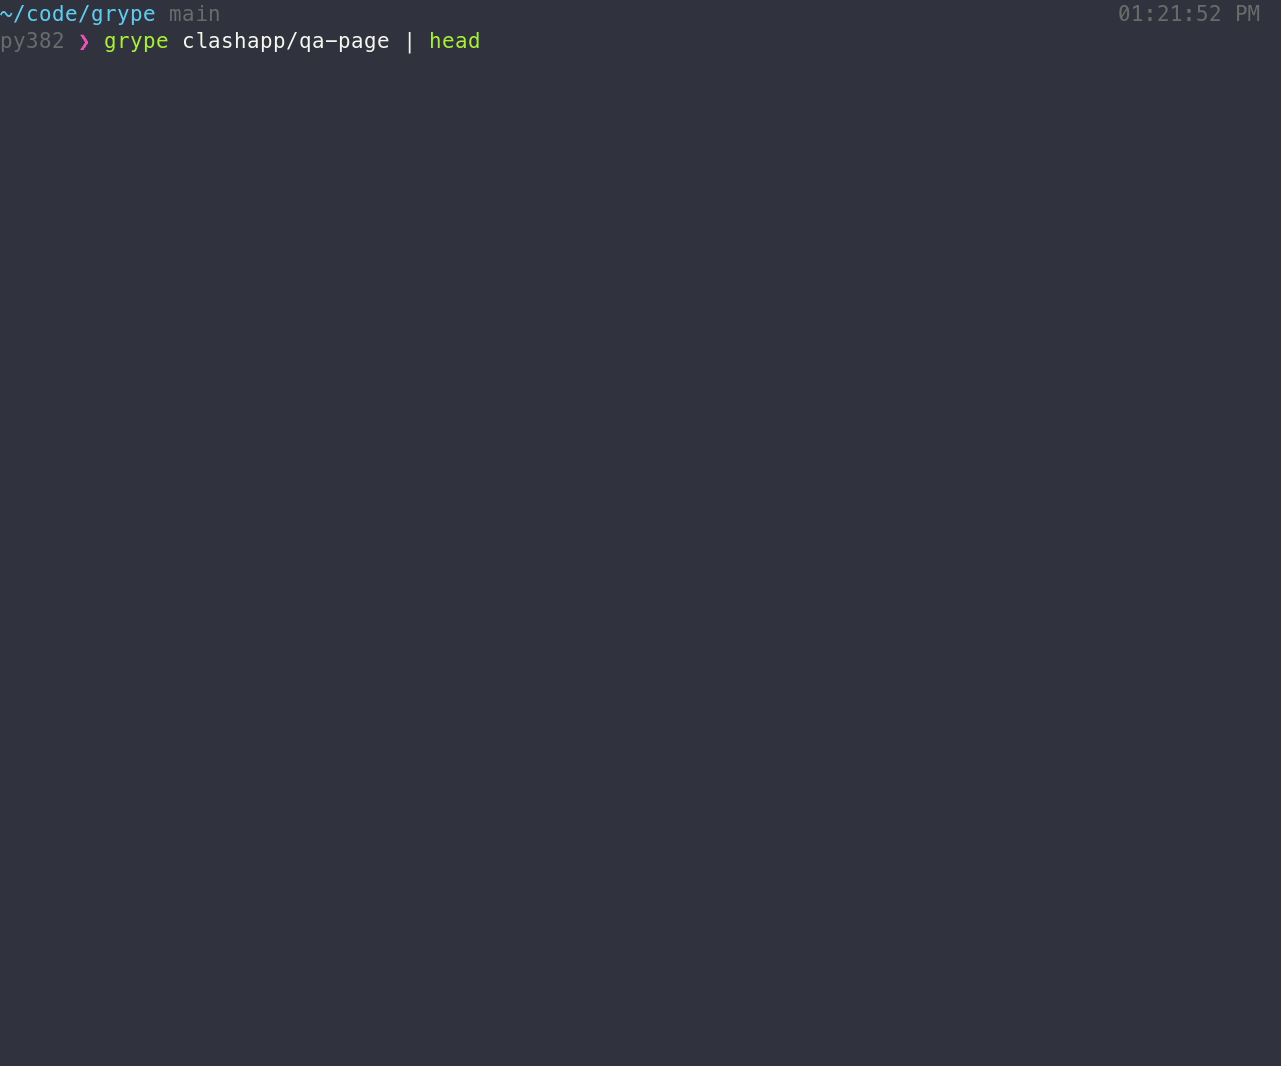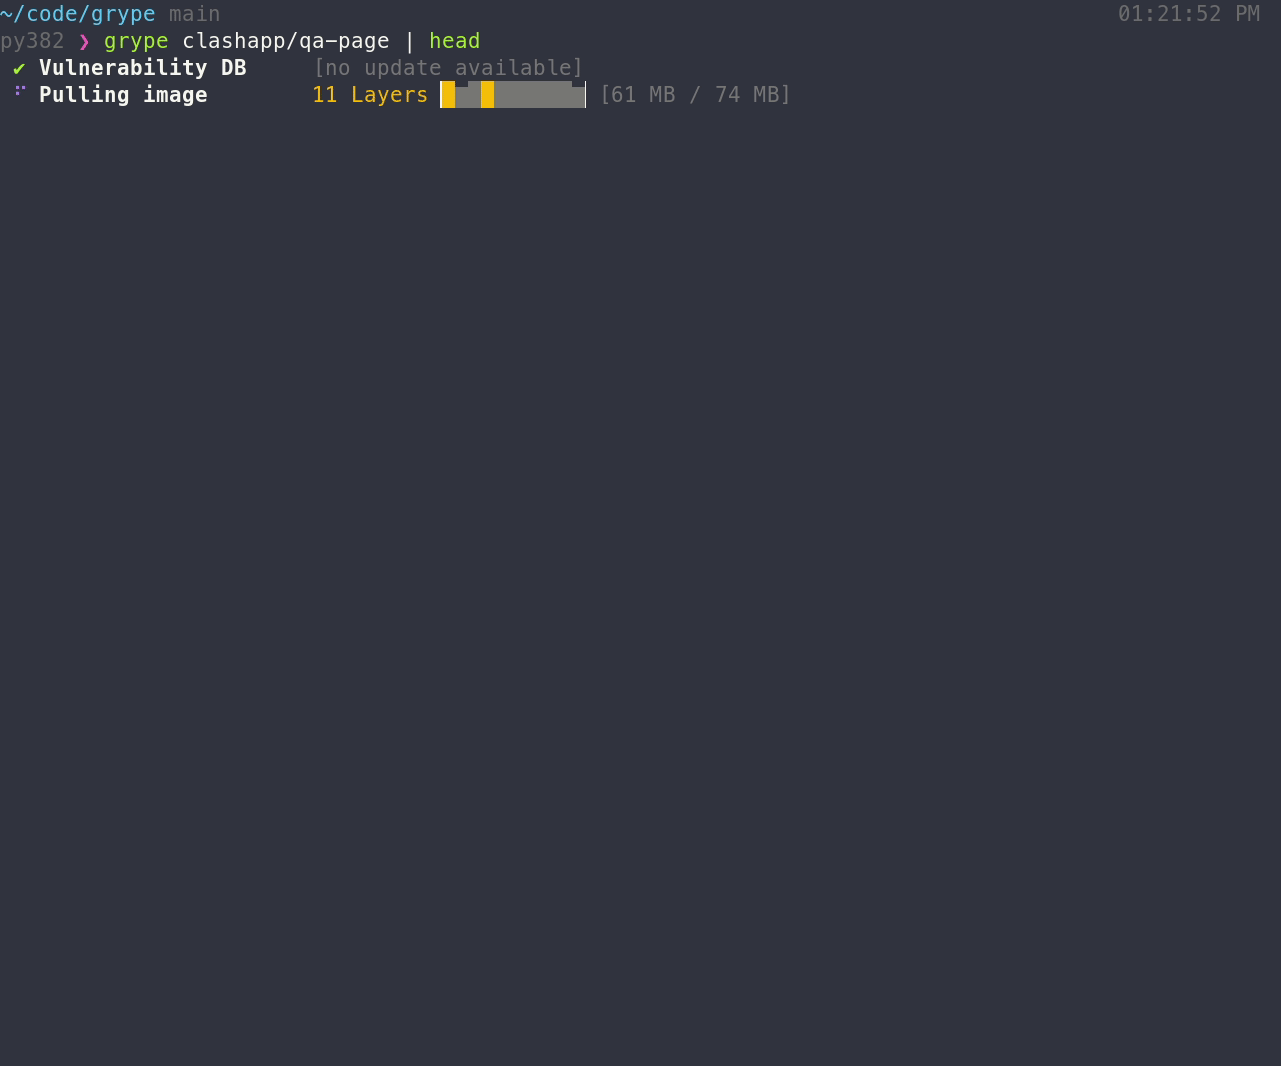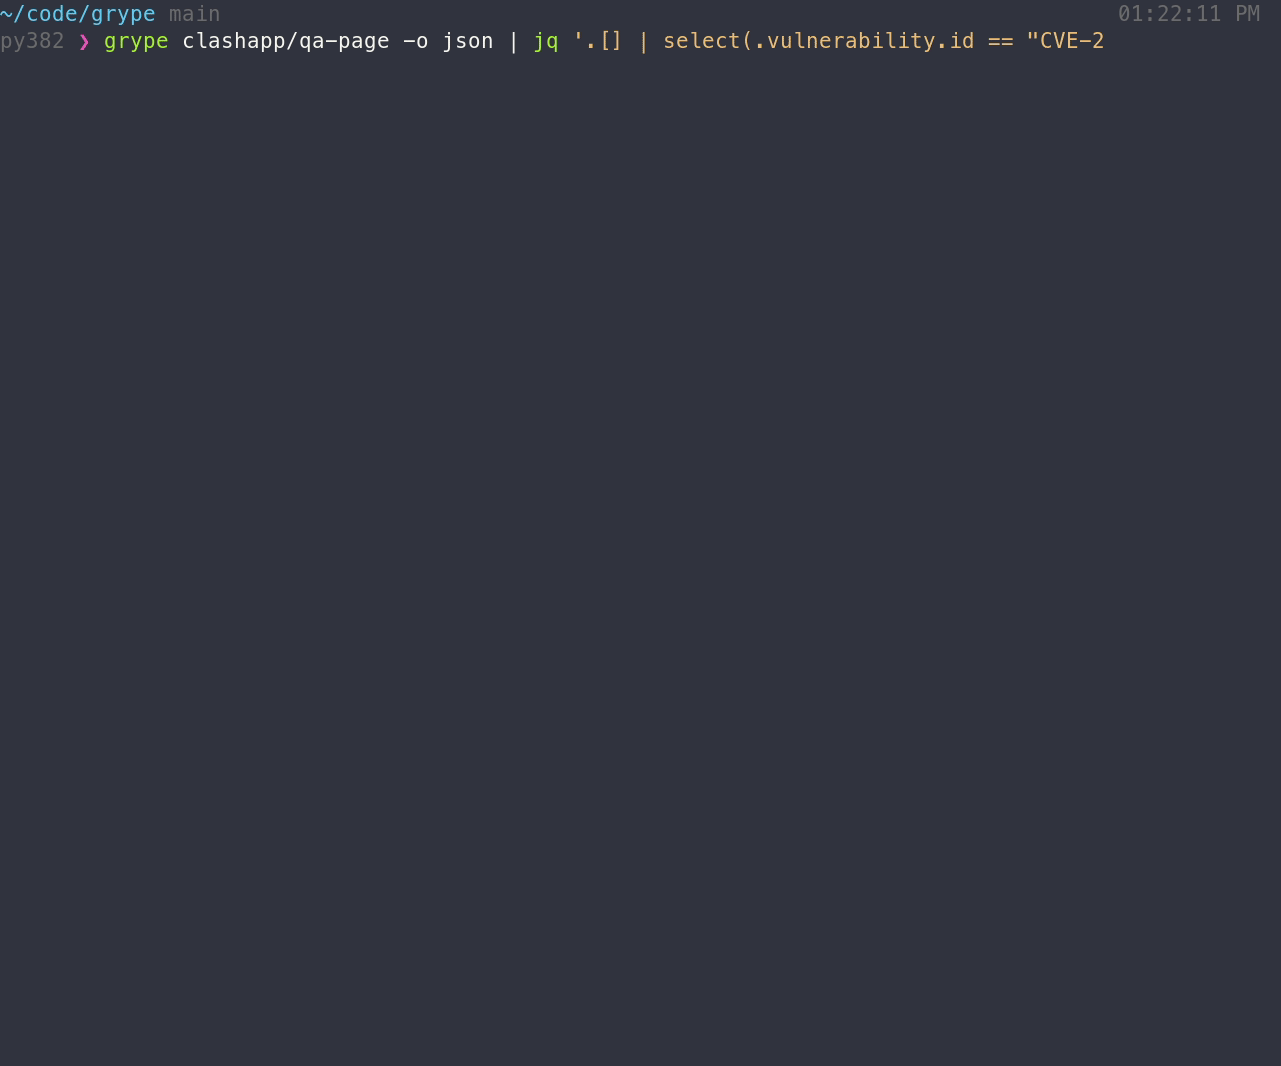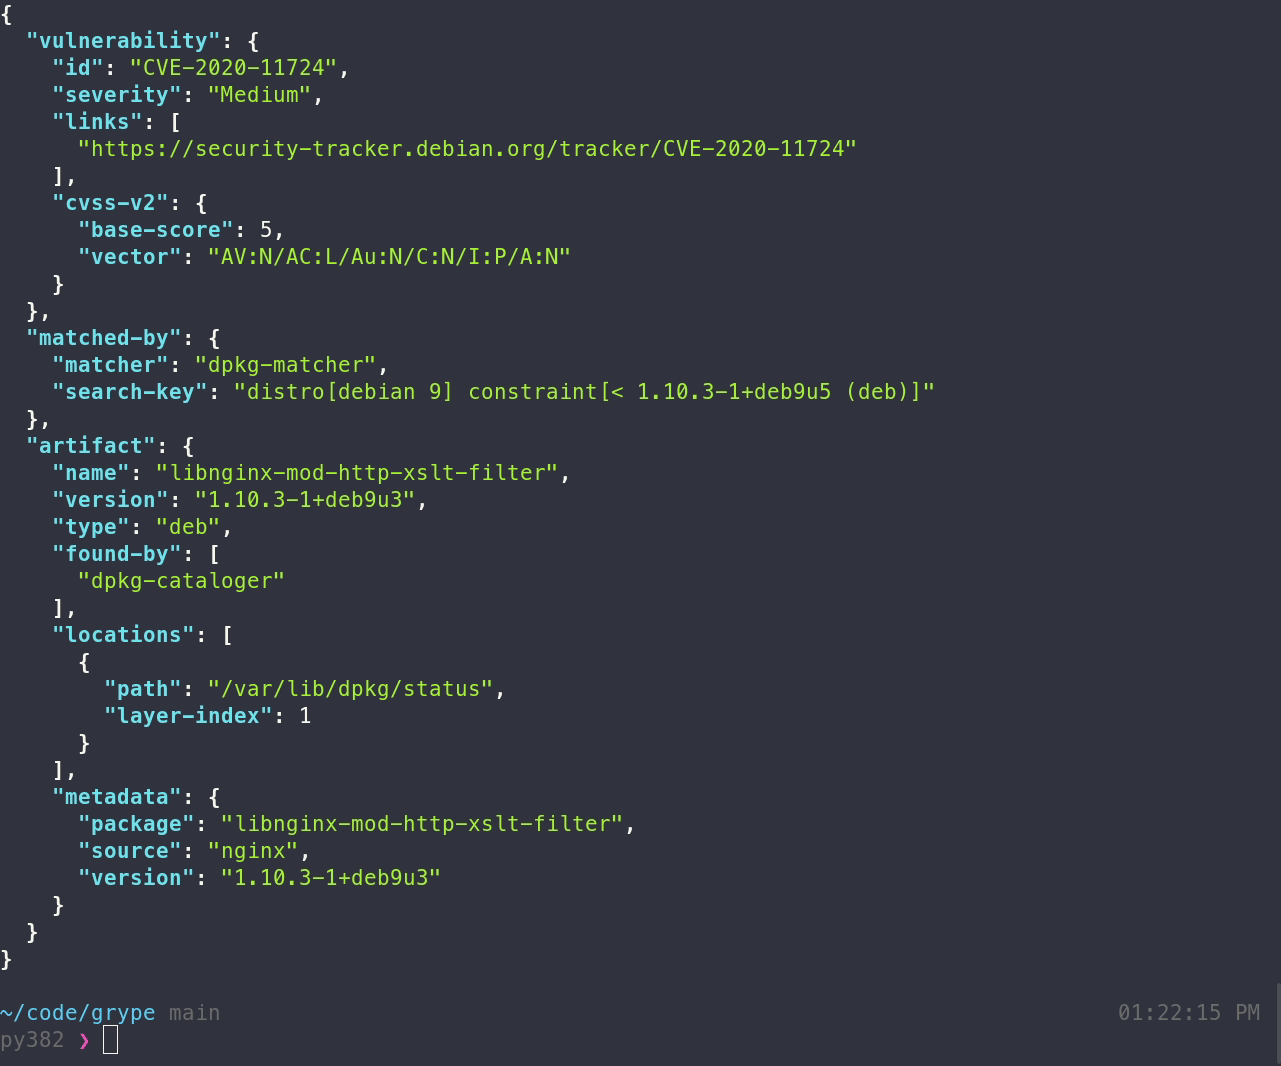
Scan a container image or directory for vulnerabilities:
# container image
grype alpine:latest

# directory
grype ./my-project
Local containers-storage images
On Linux, grype can scan images from a local containers-storage store (e.g. built with Buildah or Podman) when asked explicitly; plain image references never look there:
grype --from containers-storage localhost/myimage:latest

# rootless stores must be read from inside the builder's user namespace
podman unshare grype --from containers-storage localhost/myimage:latest
This is included in the Linux release binaries. When building from source, add -tags containers_image_openpgp,exclude_graphdriver_btrfs.
Scan an SBOM for even faster vulnerability detection:
# scan a Syft SBOM
grype sbom:./sbom.json

# pipe an SBOM into Grype
cat ./sbom.json | grype
[!TIP] Check out the Getting Started guide to explore all of the capabilities and features.
Want to know all of the ins-and-outs of Grype? Check out the CLI docs and configuration docs.
Contributing
We encourage users to help make these tools better by submitting issues when you find a bug or want a new feature. Check out our contributing overview and developer-specific documentation if you are interested in providing code contributions.
Grype development is sponsored by Anchore, and is released under the Apache-2.0 License.
The Grype logo by Anchore is licensed under CC BY 4.0

For commercial support options with Syft or Grype, please contact Anchore.
Come talk to us!
The Grype Team holds regular community meetings online. All are welcome to join to bring topics for discussion.
- Check the calendar for the next meeting date.
- Add items to the agenda (join this group for write access to the agenda)
- See you there!
Explore related projects
trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
256,224 starsHack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers
124,736 starsswisskyrepo/PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
82,418 starscaddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
78,832 stars