
TheKingOfDuck/burpFakeIP
TheKingOfDuck/burpFakeIP has 1,666 GitHub stars and 231 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-07 03:23 UTC. Last push 2022-09-29.
服务端配置错误情况下用于伪造ip地址进行测试的Burp Suite插件
Measured star growth
- in 24h
- 0
- in 7 days
- Collecting history
- in 15 days
- Collecting history
- in 1 month
- Collecting history
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
OriginalburpFakeIP
下载使用:Releases
2021/09/24
- 修复M00nBack反馈的一个bug。
- 添加了AutoXFF的开关,并将AutoXFF默认设置不开启,如需让插件给每个请求头添加一个随机的XFF请求头可在右键菜单中选择ON开启
2021/05/21
使用Java重构,增加了issue中提到的功能特性,新增给每个请求自动添加XFF头以及随机IP的功能,具体可见右键菜单AutoXFF,默认情况下自动添加的xff头为X-Forwarded-For,值为生成的随机IP,均可自定义。
2020/04/25
优化代码,新增9种请求头。
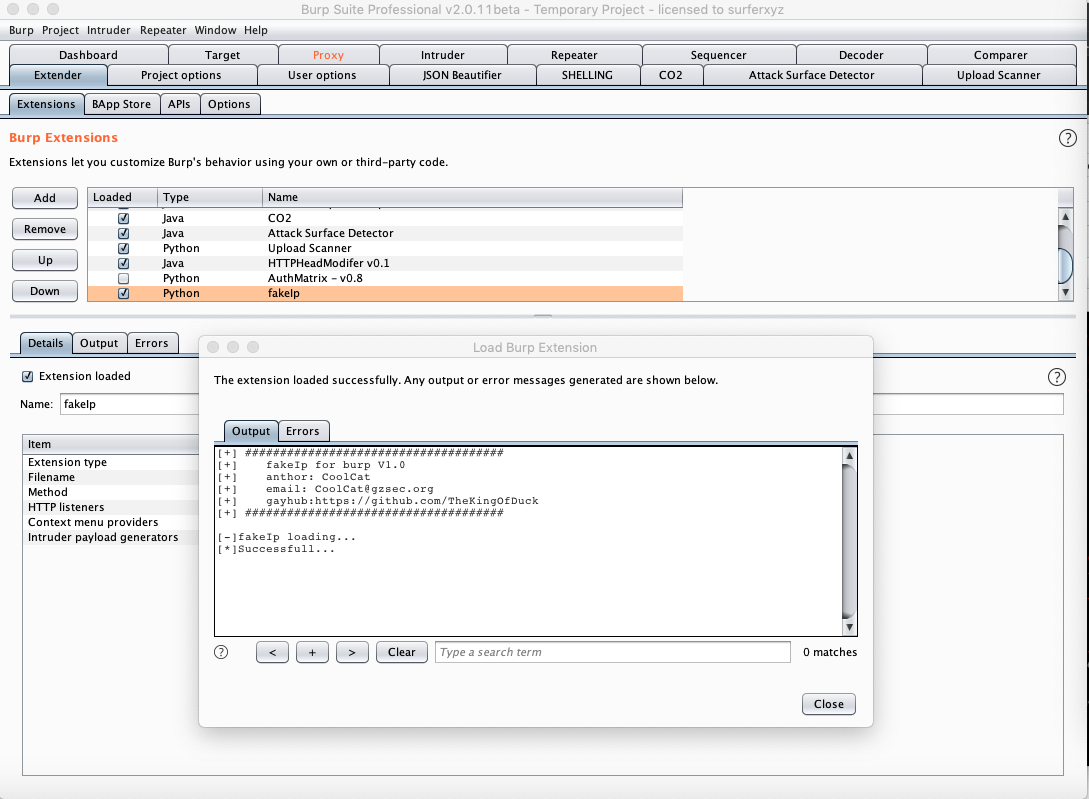
四个小功能
- 伪造指定ip
- 伪造本地ip
- 伪造随机ip
- 随机ip爆破
0x01 伪造指定ip
在Repeater模块右键选择fakeIp菜单,然后点击inputIP功能,然后输入指定的ip:
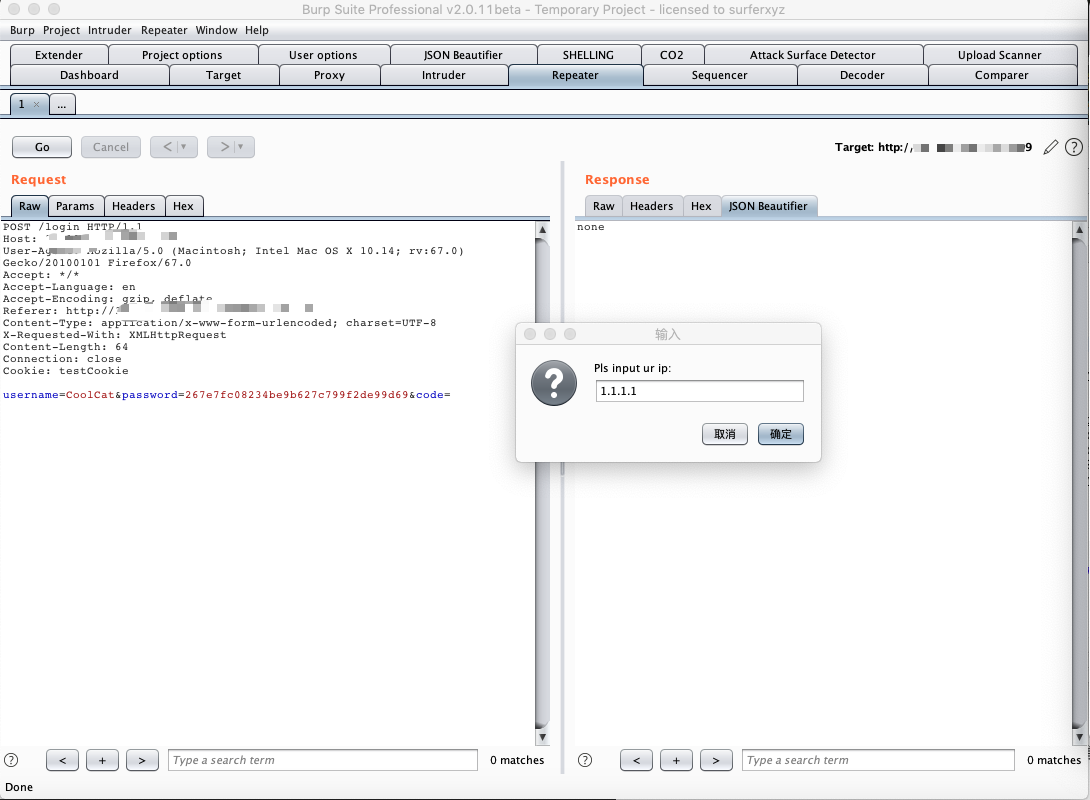
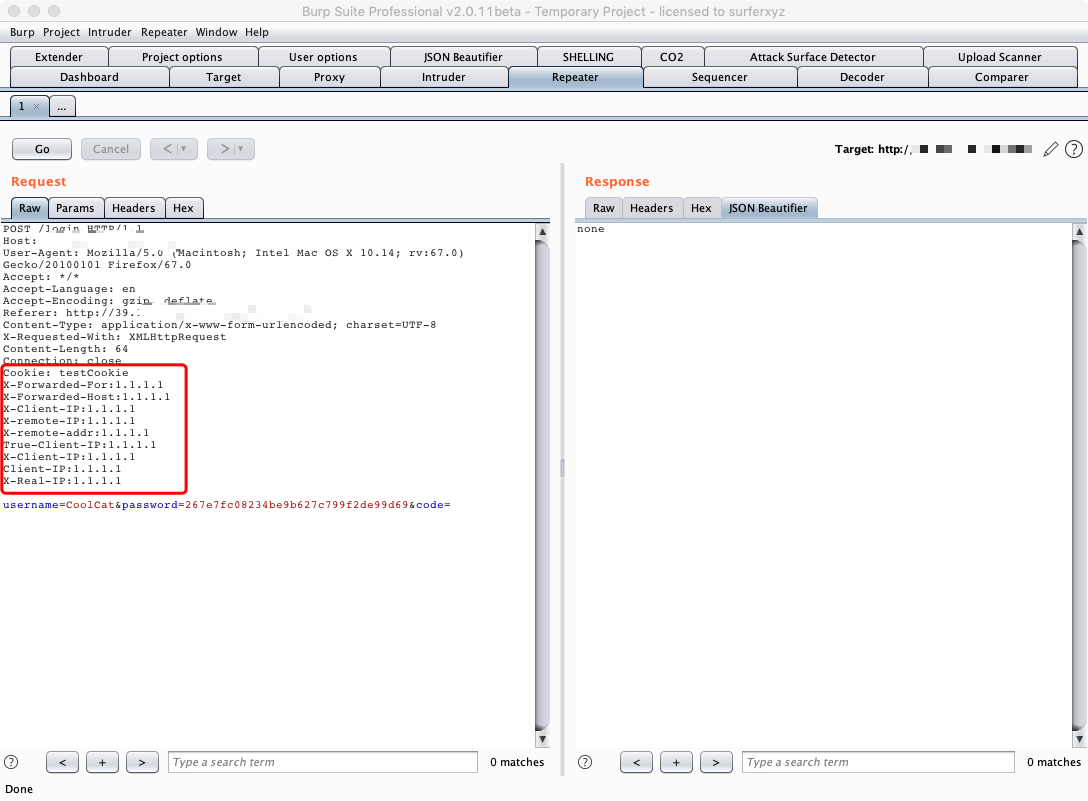
程序会自动添加所有可伪造得字段到请求头中。
0x02 伪造本地ip
在Repeater模块右键选择fakeIp菜单,然后点击127.0.0.1功能:
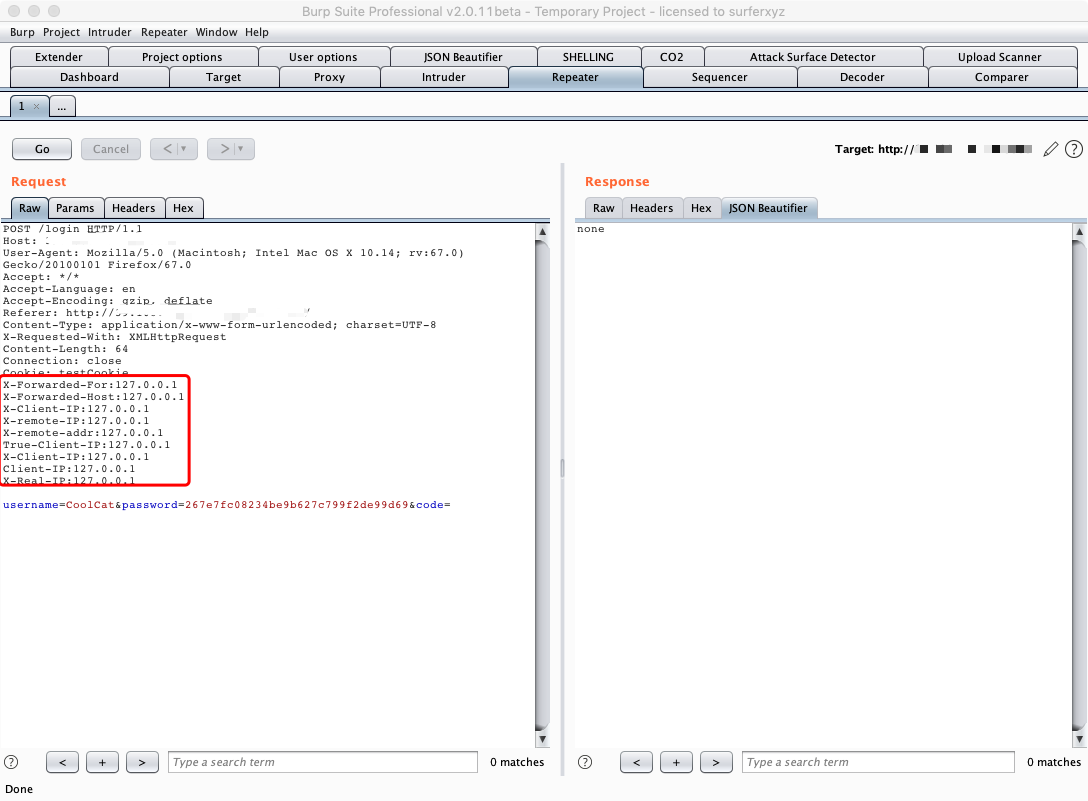
0x03 伪造随机ip
在Repeater模块右键选择fakeIp菜单,然后点击randomIP功能:
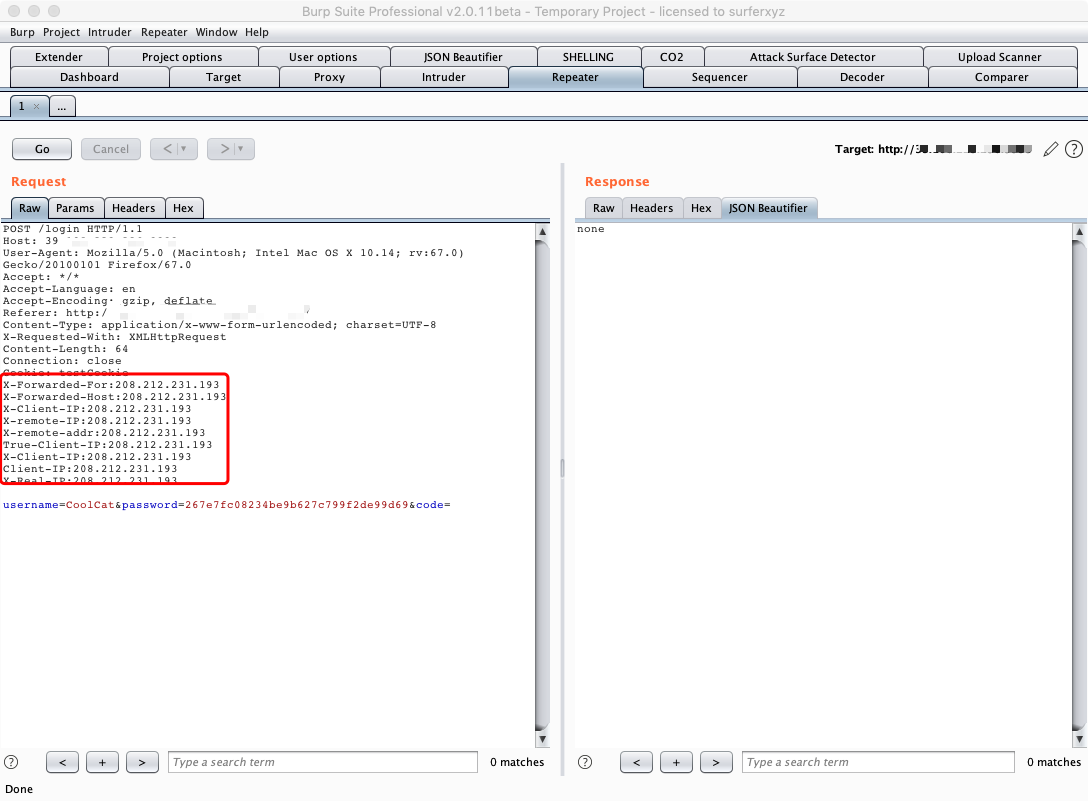
0x04 随机ip爆破
伪造随机ip爆破是本插件最核心的功能。
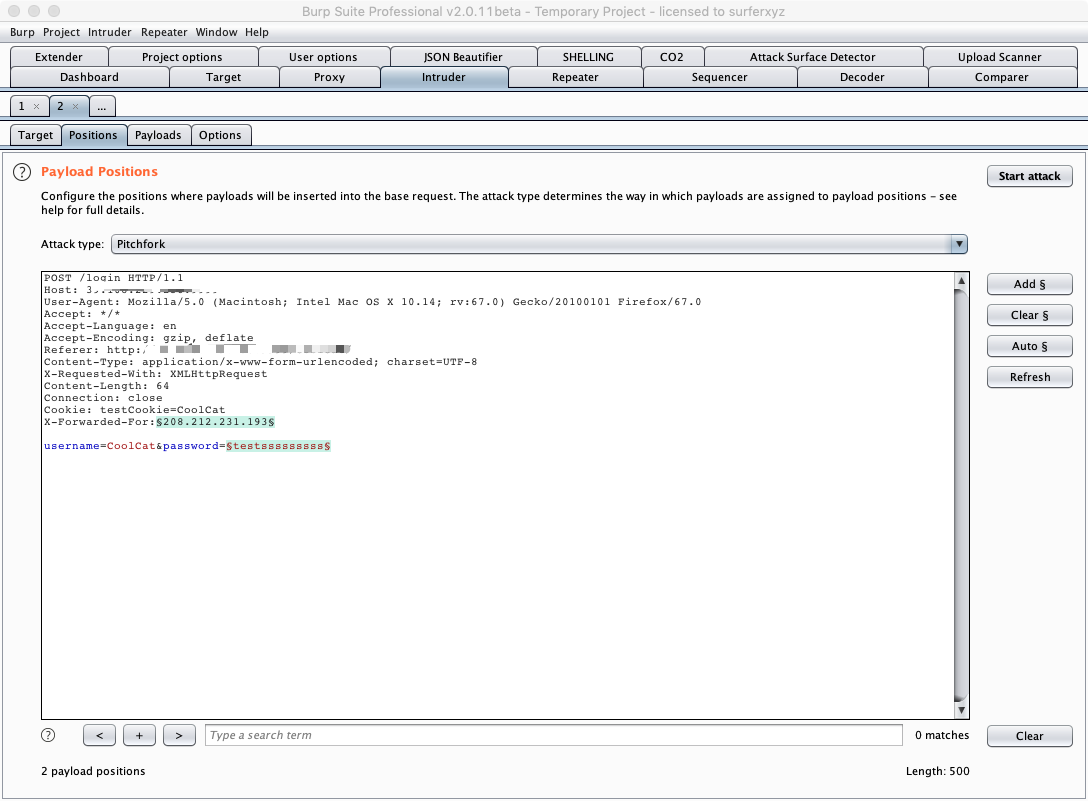
将数据包发送到Intruder模块,在Positions中切换Attack type为Pitchfork模式,选择好有效的伪造字段,以及需要爆破的字段:
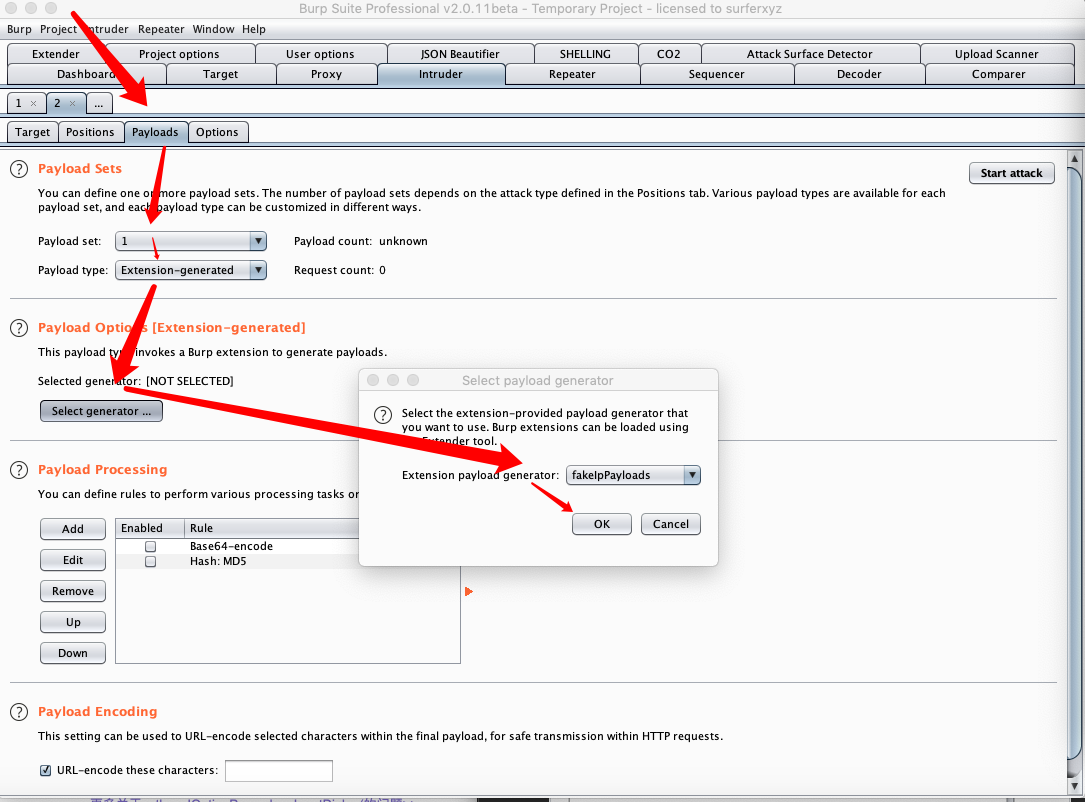
按照箭头顺序将Payload来源设置为Extensin-generated,并设置负载伪fakeIpPayloads,然后设置第二个变量。
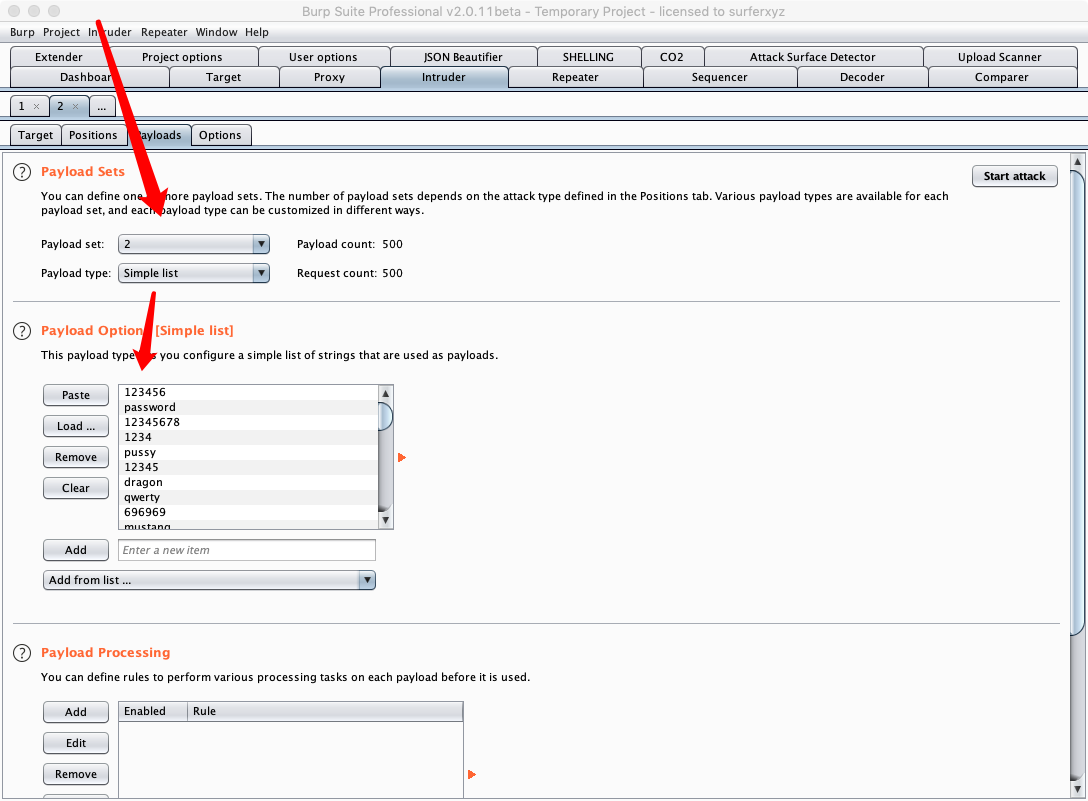
点击Start attack开始爆破.
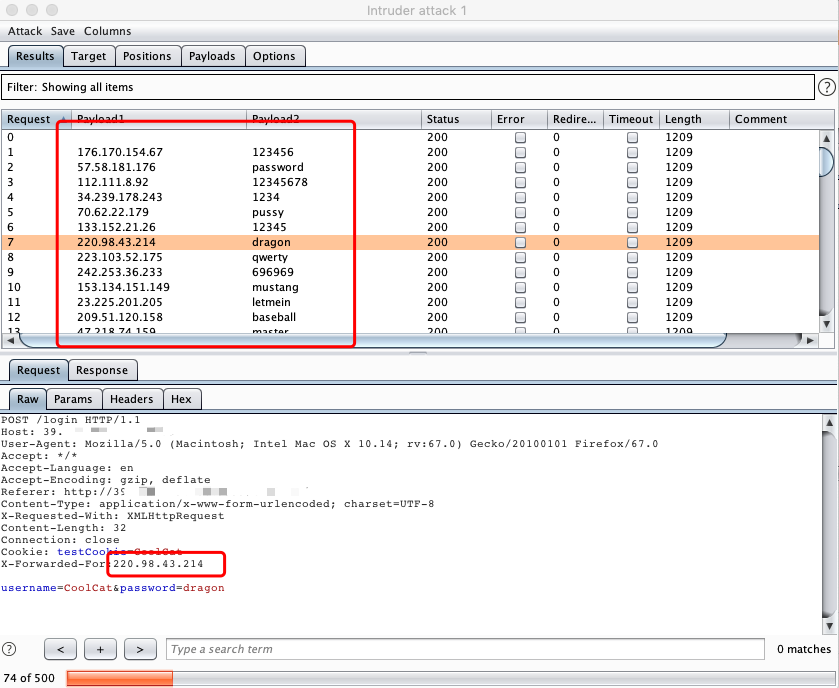
如上图,实现每次爆破都使用不同的伪ip进行,避免被ban。
PS:伪造随机ip爆破的先决条件可以伪造ip绕过服务器限制。
Explore related projects
codecrafters-io/build-your-own-x
Master programming by recreating your favorite technologies from scratch.
560,509 starspublic-apis/public-apis
A collective list of free APIs
496,801 starsmorluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
438,679 starsopenclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
394,087 stars