
Aryma-f4/gulpsuite
Aryma-f4/gulpsuite has 40 GitHub stars and 1 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-11 17:49 UTC. Last push 2026-10-28.
Gulp it before burp — Ultra-fast native Rust web security testing, DAST scanner & HTTP/HTTPS/WebSocket proxy suite
Measured star growth
- in 24h
- 0
- in 7 days
- Update delayed
- in 15 days
- Update delayed
- in 1 month
- Update delayed
Net star changes over overlapping periods, not daily totals. Missing measurements are left blank. Stars measure attention, not software quality.
README.md
Original
Gulpsuite (v0.1.0)
"Gulp it before burp"
Ultra-Fast, Lightweight Native Rust Web Security Testing, DAST Vulnerability Scanner, Nuclei YAML Engine & HTTP/HTTPS/WebSocket Interception Proxy Suite







Download v0.1.0 Installers · What's New in v0.1.0 · Screenshots · Performance Benchmarks · Contributing · Security Policy
Overview
"Gulp it before burp"
Gulpsuite is a native, cross-platform web application security testing workbench, MITM HTTP/1.1, HTTP/2, TLS & WebSocket interception proxy, automated DAST vulnerability scanner, native ProjectDiscovery Nuclei YAML template engine, worldwide CVE/OSV auditor, fuzzer, and request manipulation suite written 100% in Rust (eframe / egui + tokio + rustls + rcgen).
Designed for bug bounty hunters, penetration testers, red teams, and AppSec engineers who want a full-featured desktop security suite that launches in < 0.2 seconds and uses ~50 MB of RAM without runtime garbage-collection pauses or multi-gigabyte memory bloat.
✨ What's New in v0.1.0
- Official Gulpsuite Brand Identity: Crisp orange
#F56700"g"application icon integrated across native OS windows, macOS.appbundles (.icns), Windows executables/shortcuts (.ico), Linux desktop entries, and the graphical Setup Wizard. - Worldwide CVE, Retire.js & Real-Time OSV.dev Vulnerability Audit:
- 477 Built-in Client-Side JS & npm Library Rules: Detects vulnerable versions of jQuery, Bootstrap, Angular, React, Vue, Lodash, Moment.js, Handlebars, DOMPurify, Axios, Next.js, Vite, Webpack, and hundreds more via URI, filename, file-content regex, and global variable probes.
- Live OSV.dev API Querying: Queries
https://api.osv.dev/v1/queryin real time for discovered libraries and backend packages, enriching findings with every publishedCVE-*andGHSA-*advisory. - Active High-Impact Infrastructure CVE Probes: Non-destructive active checks for
CVE-2021-41773/CVE-2021-42013(Apache path traversal),CVE-2022-22965(Spring4Shell),CVE-2021-44228(Log4Shell OOB),CVE-2023-46604/CVE-2024-23897/CVE-2024-4577, and exposed.git/HEAD&.envsecrets.
- Native ProjectDiscovery Nuclei YAML Template Engine:
- Load single
.yamltemplates or entirenuclei-templates/directories directly inside Scanner → Nuclei templates. - Supports
http:/requests:blocks,raw:requests,payloads:(batteringram,pitchfork,clusterbomb),matchers:(word,regex,status,binary,dsl), andextractors:.
- Load single
- Dockable
Inspector&NotesSide Panel:- Collapsible vertical rail in Repeater and Proxy → Intercept with recursive multi-step
Selectiondecode/re-encode chains (URL,Base64,HTML,ASCII hex) and live editable tables forRequest attributes,Query parameters,Body parameters,Request cookies, andRequest headers.
- Collapsible vertical rail in Repeater and Proxy → Intercept with recursive multi-step
- Automatic Gzip / Deflate / Chunked HTTP & WebSocket (
permessage-deflate) Decompression:- Transparently inflates
Content-Encoding: gzip | deflate | x-gzipand unchunksTransfer-Encoding: chunkedpayloads for human-readable inspection and syntax highlighting while preserving raw wire bytes. - Dedicated Proxy → WebSockets history master table + split detail pane with automatic RFC 7692
permessage-deflatedecompression.
- Transparently inflates
- Upgraded Settings Dialog & 5-Tab Proxy Listener Editor:
- Hierarchical
Tools,Project,Sessions,Network,User interface,Suite, andExtensionsnavigation tree withAll | User | Projectfilter pills,Project setting/User settingbadges, and the 5-tabAdd / Edit proxy listenermodal (Binding,Request handling,Certificate,TLS Protocols,HTTP).
- Hierarchical
Why Gulpsuite? (Performance & Memory Benchmarks)
| Metric | Gulpsuite (v0.1.0 Native Rust) |
Traditional JVM-Based Security Suites | Advantage |
|---|---|---|---|
| Idle Memory (RSS) | ~50 MB | ~850 MB – 2.2 GB+ | ~20× – 40× lower RAM |
| Active Scan / Fuzzing Memory | ~55 – 120 MB (bounded ring buffers) | 2 GB – 6 GB+ | Zero GC pauses or OOM freezes |
| Idle CPU Usage | 0.0% – 0.4% (reactive immediate-mode UI) | 3% – 12% | Cooler laptop & longer battery life |
| Standalone Binary Size | ~20 MB | ~650 MB – 820 MB | 40× smaller footprint |
| Cold Startup Time | < 0.2 seconds | 4 – 10 seconds | Instant launch |
Cross-Platform Installers (v0.1.0)
Download pre-built native installers directly from GitHub Releases (v0.1.0):
| Platform | Architecture | Installer Packages | Format |
|---|---|---|---|
| macOS (Apple Silicon) | arm64 |
Gulpsuite-0.1.0-macos-arm64.dmg / Gulpsuite-0.1.0-macos-arm64-setup.pkg |
macOS Disk Image (.dmg) & Native GUI Setup Package (.pkg) |
| macOS (Intel) | x86_64 |
Gulpsuite-0.1.0-macos-x64.dmg / Gulpsuite-0.1.0-macos-x64-setup.pkg |
macOS Disk Image (.dmg) & Native GUI Setup Package (.pkg) |
| Windows | x86_64 |
Gulpsuite-0.1.0-windows-x64-setup.exe |
Self-Contained Windows Graphical Setup Wizard + Bundled Chromium (.exe) |
| Linux (CachyOS / Arch / Universal) | x86_64 |
Gulpsuite-0.1.0-x86_64.AppImage / gulpsuite-0.1.0-1-x86_64.pkg.tar.gz |
FUSE-free Portable AppImage (.AppImage) & Native CachyOS/Arch Package (.pkg.tar.gz) |
| Linux (Debian / Ubuntu / Setup) | x86_64 |
Gulpsuite-0.1.0-linux-x64-setup.run / gulpsuite_0.1.0_amd64.deb |
Self-Extracting Setup Installer (.run) & Debian/Ubuntu Package (.deb) |
Quick Start on CachyOS / Arch Linux (AppImage or pacman)
# Option 1: Run Portable AppImage directly (FUSE-free — works out of the box on CachyOS)
chmod +x Gulpsuite-0.1.0-x86_64.AppImage
./Gulpsuite-0.1.0-x86_64.AppImage

# Optional: Integrate AppImage into CachyOS desktop launcher & ~/.local/bin/gulpsuite
./Gulpsuite-0.1.0-x86_64.AppImage --install

# Option 2: Install native CachyOS / Arch Linux pacman package
sudo pacman -U gulpsuite-0.1.0-1-x86_64.pkg.tar.gz
📸 Visual Tour & Screenshots
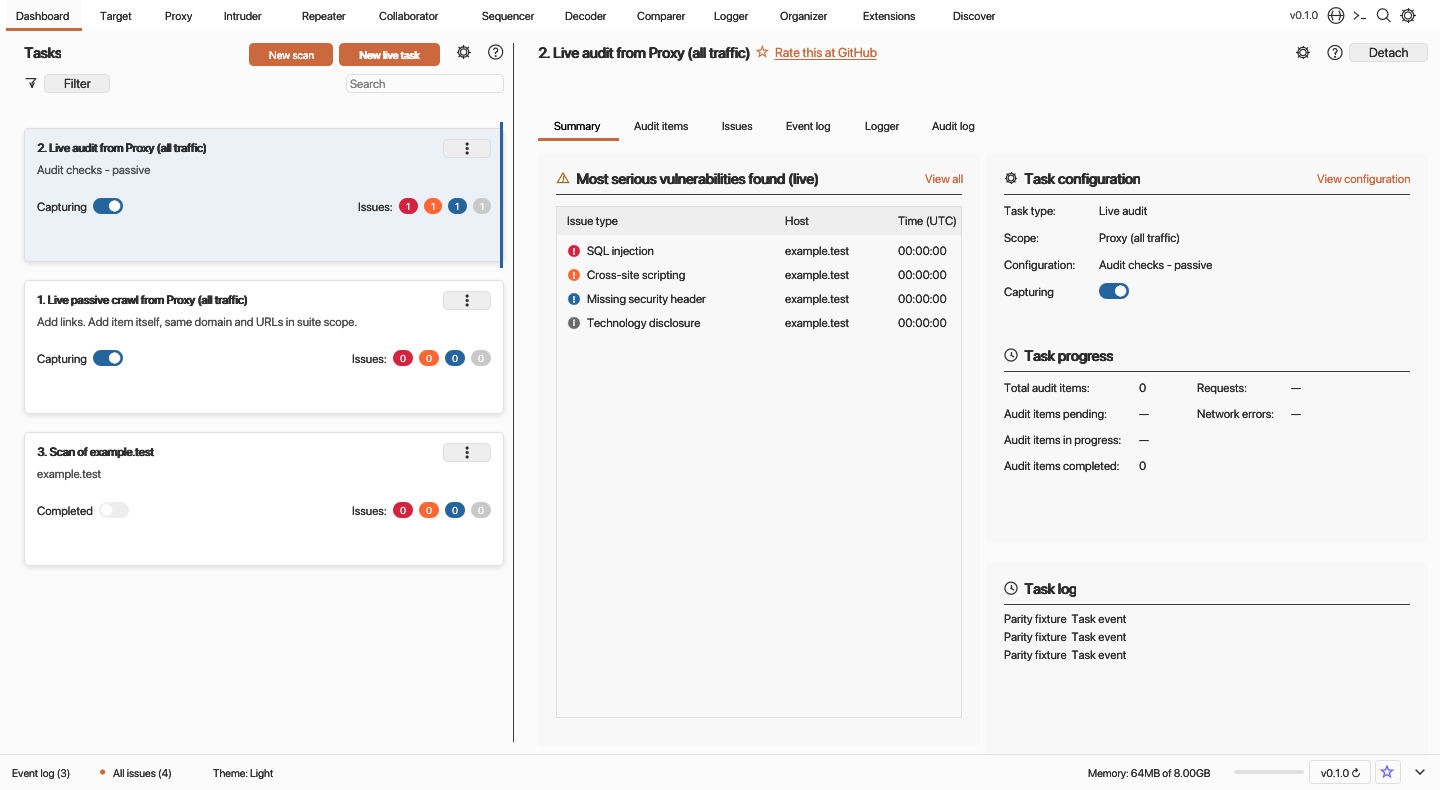
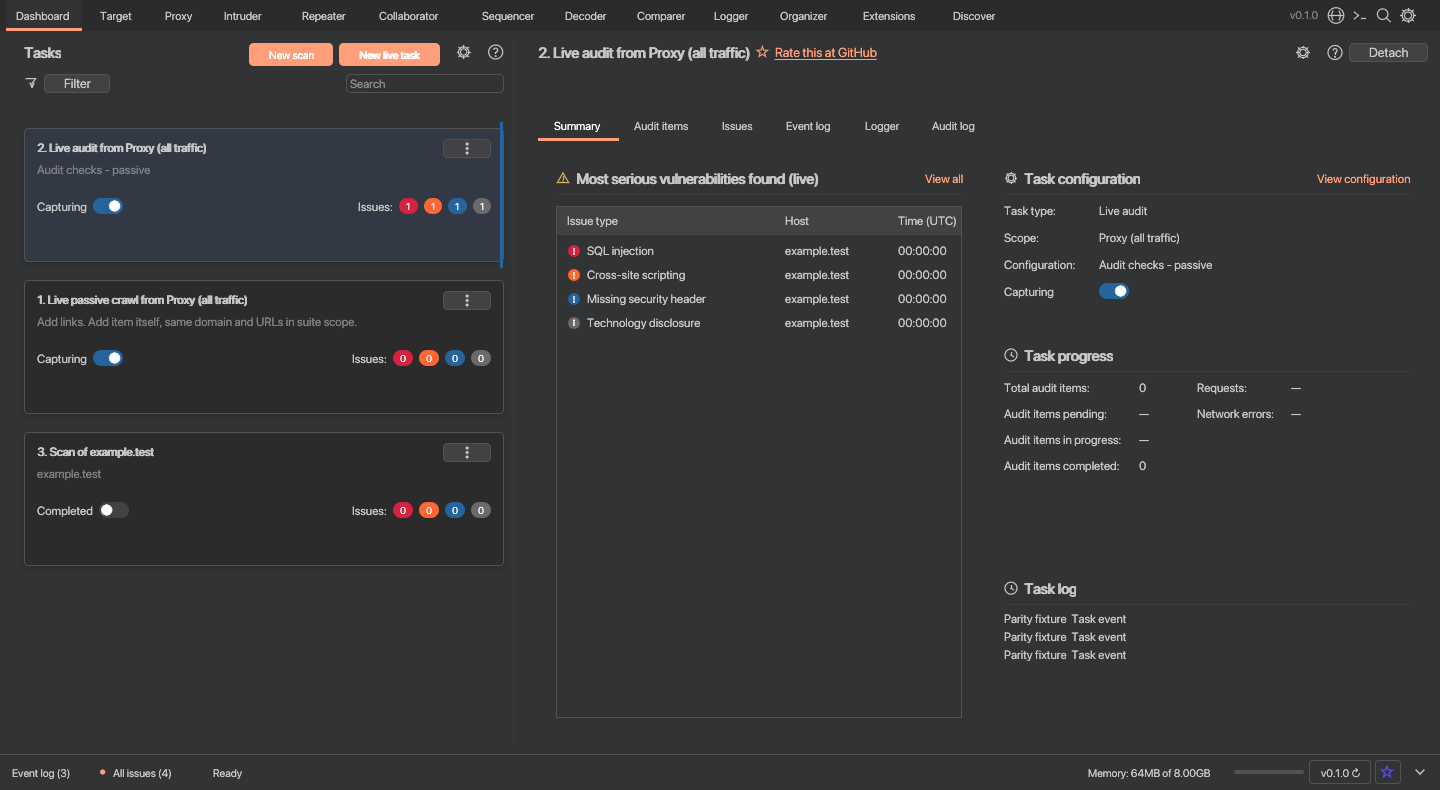
1. Dashboard (Light & Dark Themes)
Live task orchestration (Live passive crawl from Proxy, Live audit from Proxy, active/crawl scan tasks), fixed-width progress bars, categorized Issue activity with severity & confidence badges, interactive Advisory & Request/Response evidence tabs, and bottom Event log / All issues drawers.
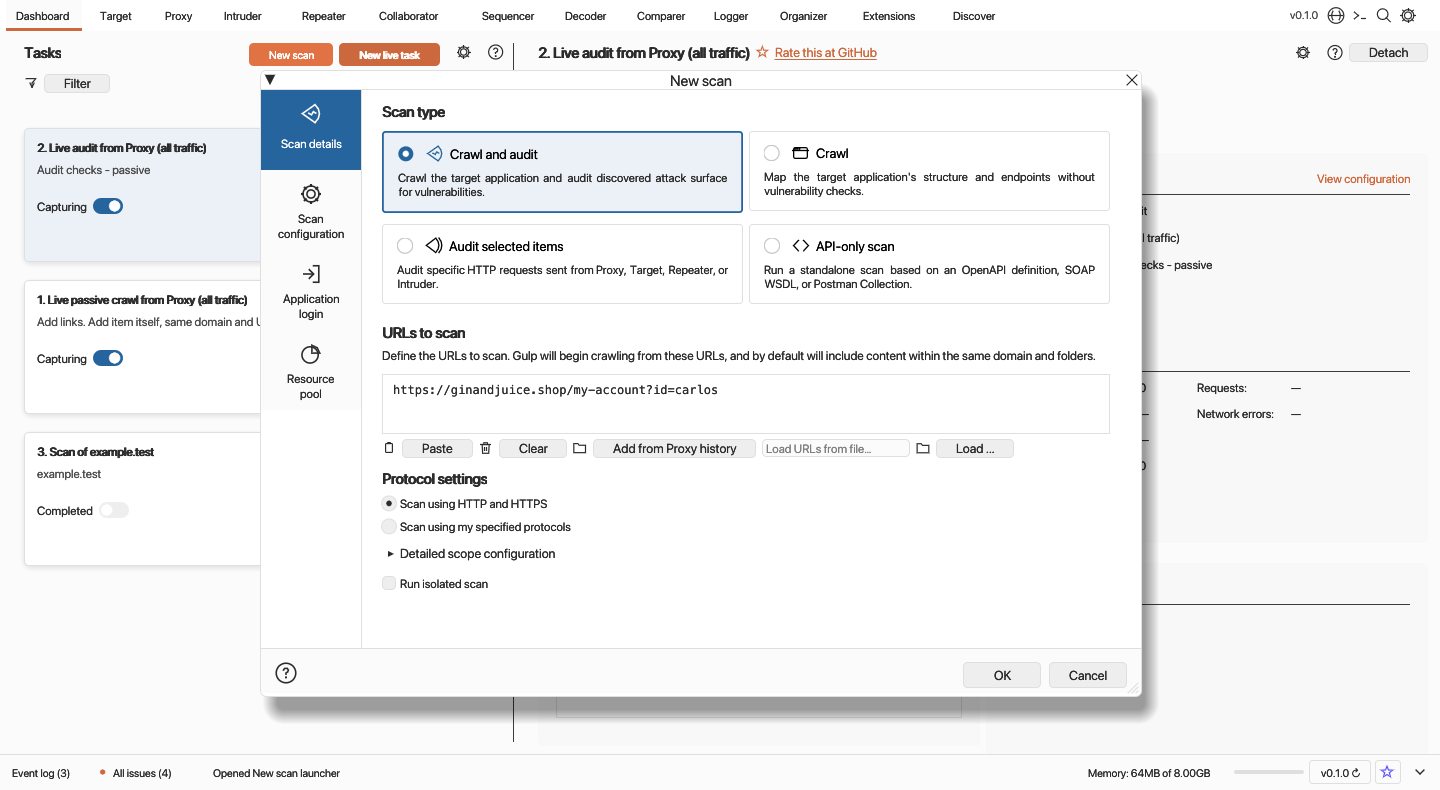
2. New Scan Launcher (Crawl and audit / Crawl / Audit selected items / API-only scan)
Standalone scan configuration window featuring #26649D navigation tiles (Scan details, Scan configuration, Application login, Resource pool), full-card clickable scan type and preset cards (Crawl strategy: Fastest / Faster / More complete / Most complete & Audit coverage: Critical issues only / Light / Medium / Thorough), OpenAPI/SOAP/Postman API definition parser, custom .bcheck checks, and ProjectDiscovery Nuclei YAML templates.
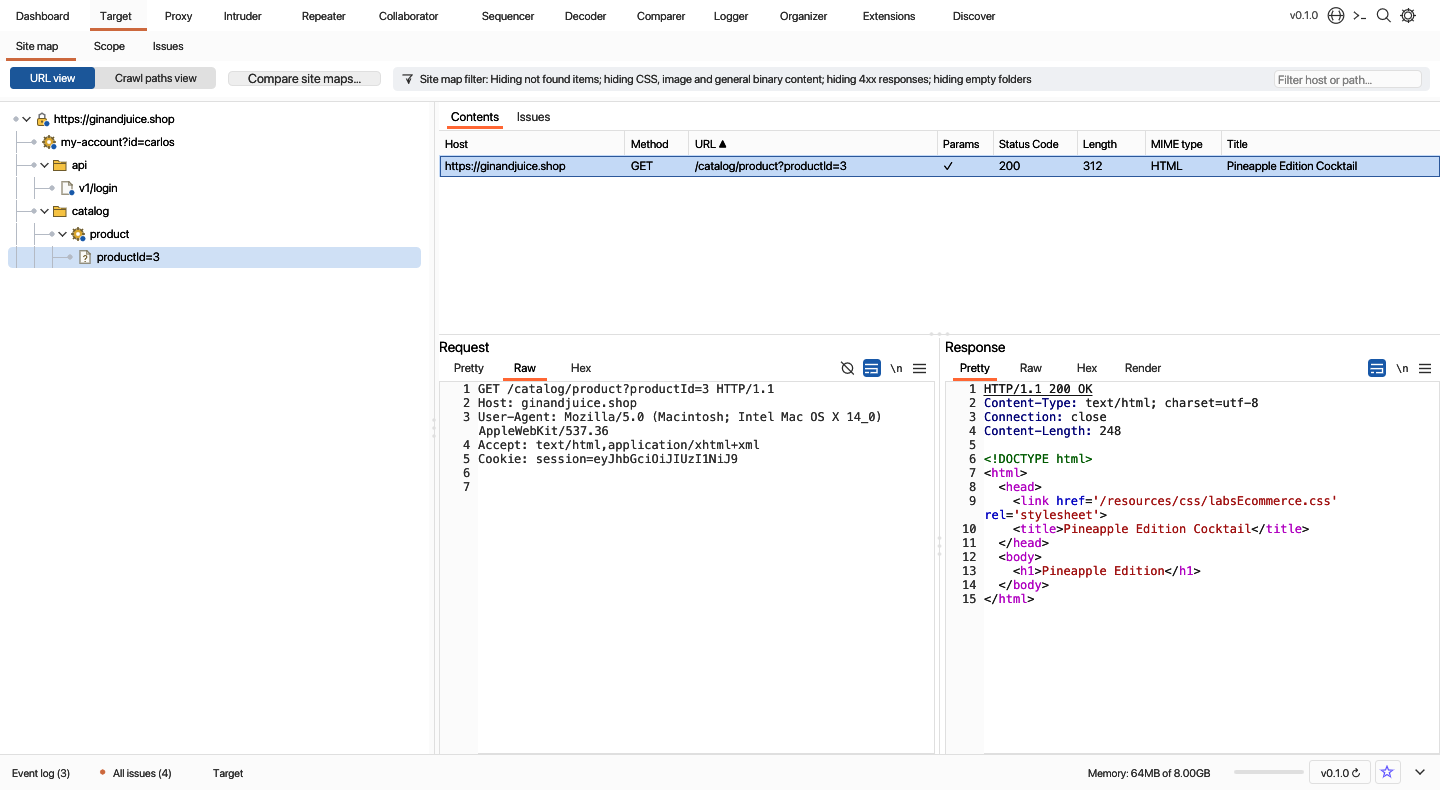
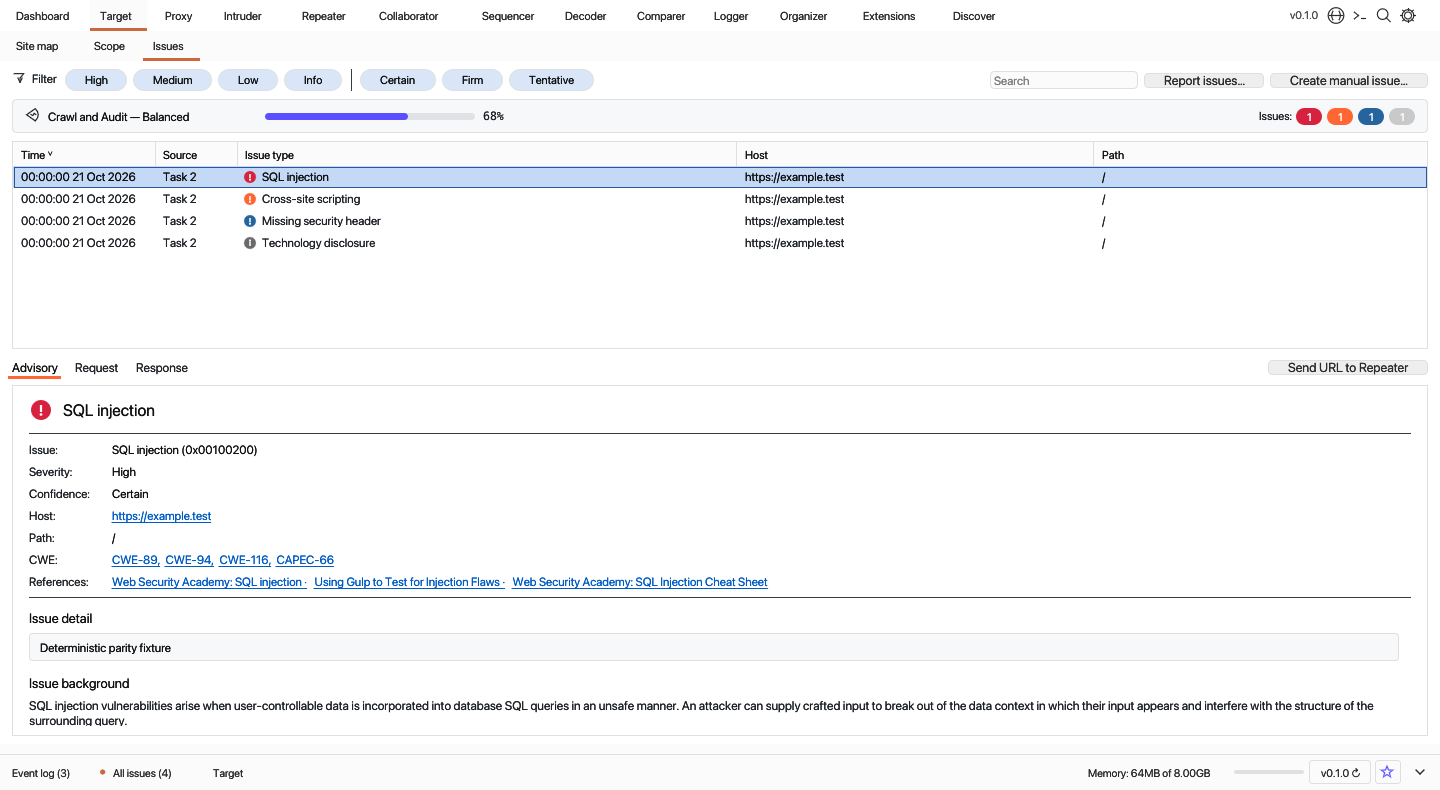
3. Target (Site map / Scope / Issues & 183-Type Knowledge Base)
Collapsible hierarchical host/folder/endpoint tree with custom vector node icons, responsive Contents & Issues split views, target scope inclusion/exclusion rules, #5B4FFF scanner progress bar with severity pills, baseline differential active/passive vulnerability verification, and a 183-entry vulnerability knowledge base with clickable CWE/CAPEC/reference hyperlinks.
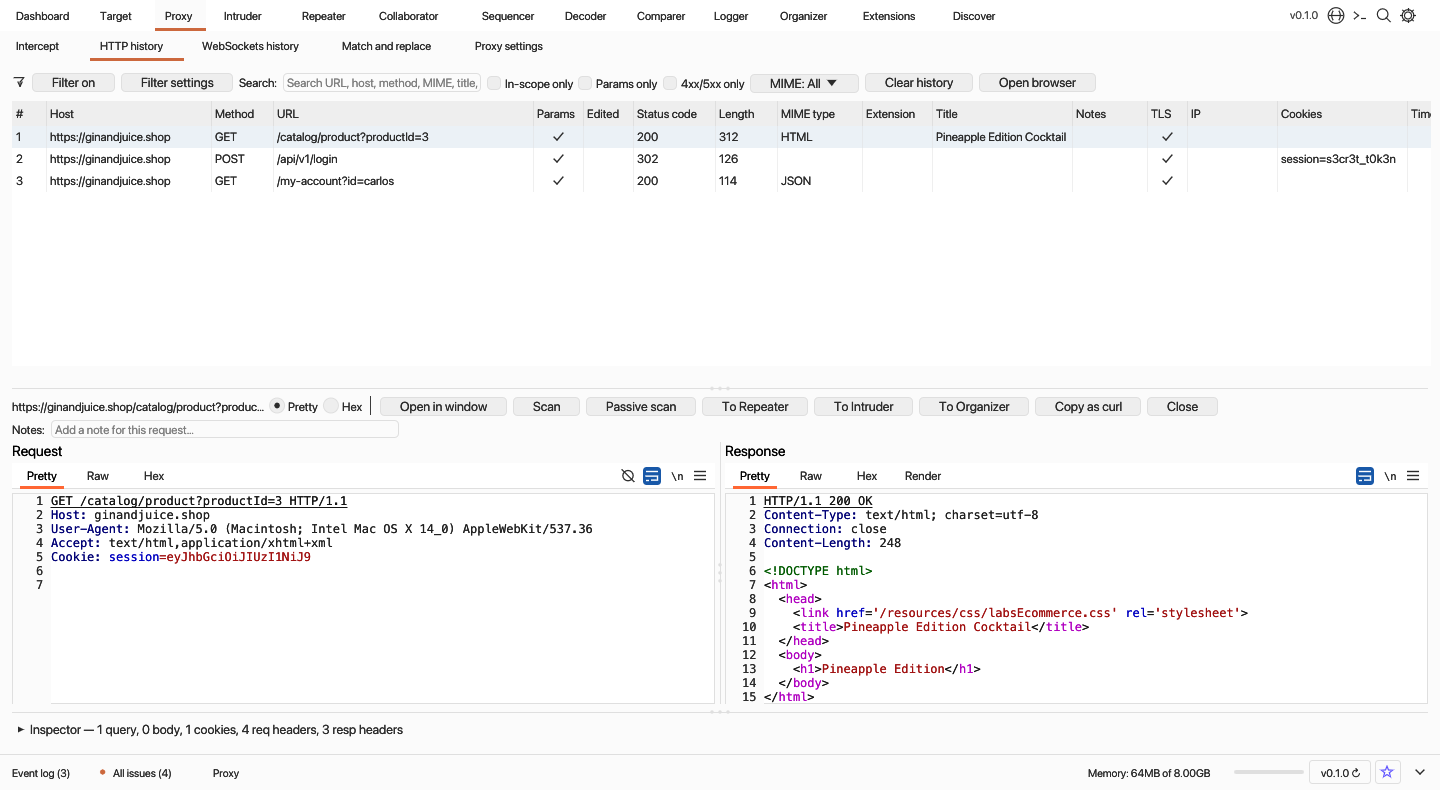
4. Proxy (Intercept / HTTP history / WebSockets history / Proxy settings)
MITM HTTP/1.1, HTTP/2, TLS (dynamic per-host X.509 certificate minting via rcgen + rustls with shared client/server config caches), and WebSocket interception proxy with live Intercept queue, dockable Inspector & Notes sidebar, Configure filter modal (Settings mode & Bambda script mode), automatic gzip/deflate/chunked decoding, and 9-section Proxy settings.
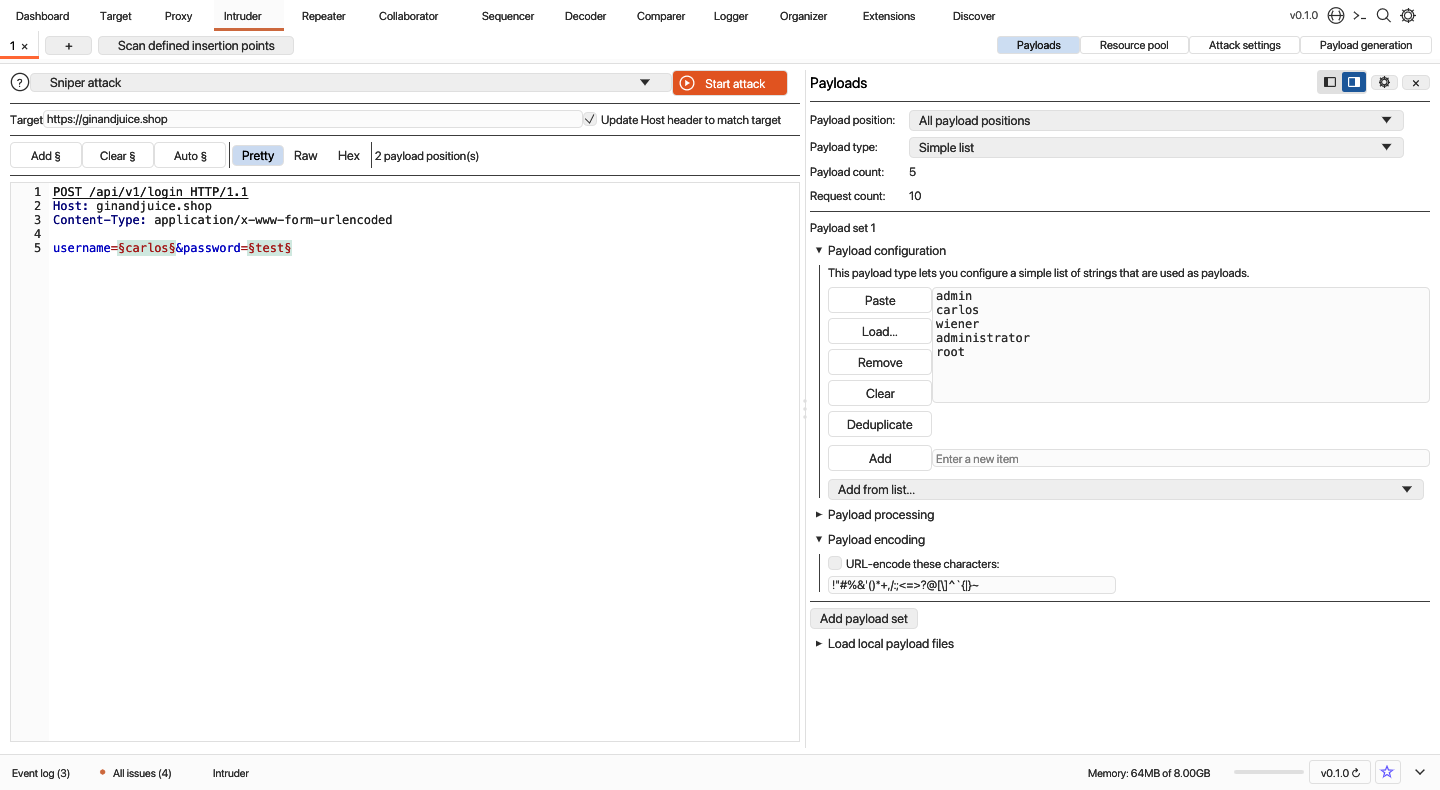
5. Intruder (Sniper / Battering ram / Pitchfork / Cluster bomb)
Multi-tab automated fuzzing and brute-force workbench with § payload position markers (Add §, Clear §, Auto § with mint-green #CFE8DF highlight spans), 19 payload generator types, 13-rule Payload processing pipeline, Payload encoding, Resource pool concurrency & throttling, Grep - match / extract / payloads, and real-time results table.
6. Repeater (Getting started & Multi-Tab Request/Response Workbench)
Interactive HTTP request manipulation and replay across multiple grouped tabs, featuring:
- 50/50 Getting Started guide when first opened
- Single-row Action Toolbar:
Send+▼group send (sequence single connection,sequence separate connections,parallel),Cancel,</History ▼/>with per-tab exchange history,Follow redirection, tab-specific gear connection/header/redirect settings, andTarget:/Override SNIconfiguration - Dockable
Inspector&NotesSide Panel: Inspect and re-encode selected bytes across multiple layers or edit query/body parameters, cookies, and headers in place - Line-numbered
Request&Responseeditors/viewers with[ Pretty | Raw | Hex | Render ] [\n] [≡]pill bars, full HTTP/HTML/JSON/JS syntax highlighting, and in-place right-clickConvert selection.
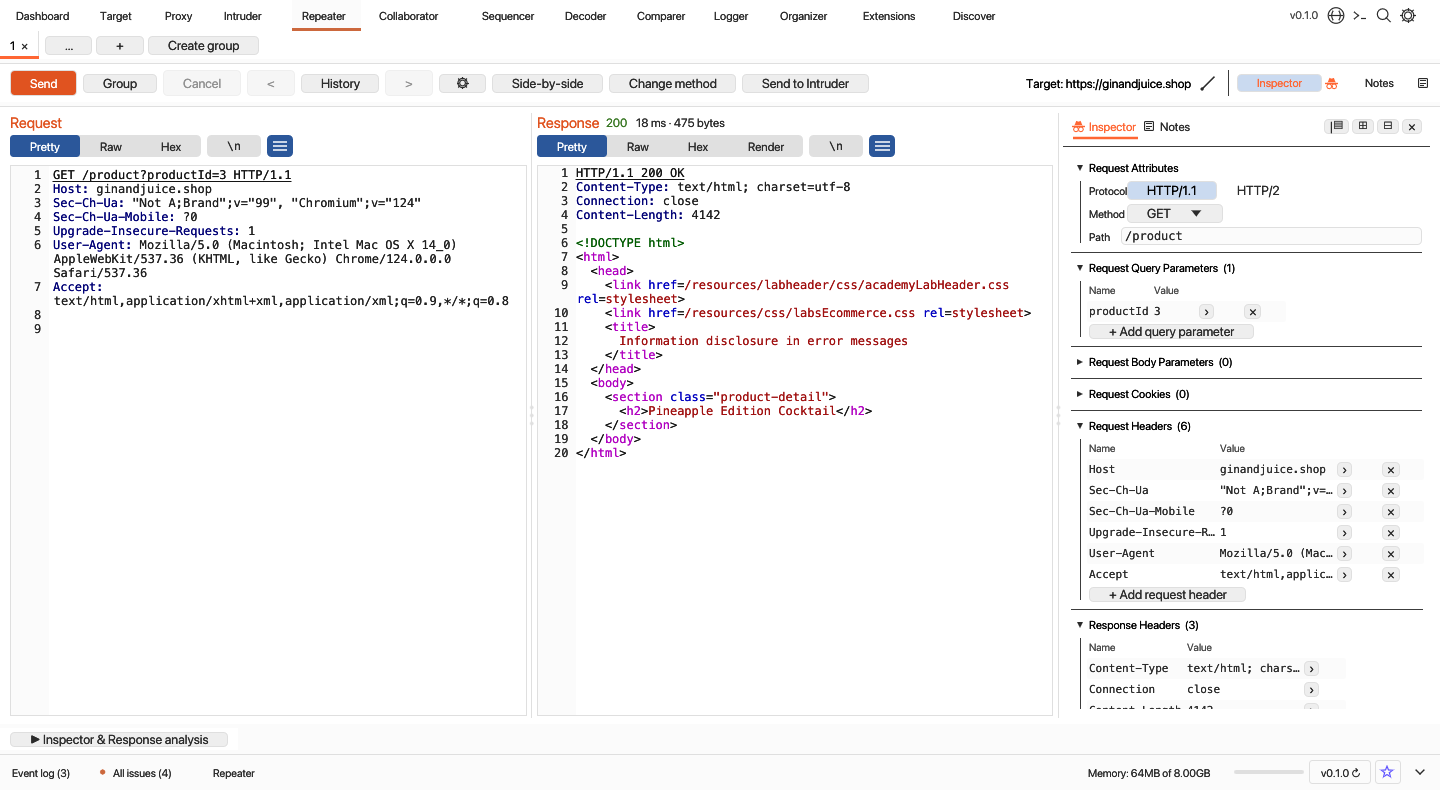
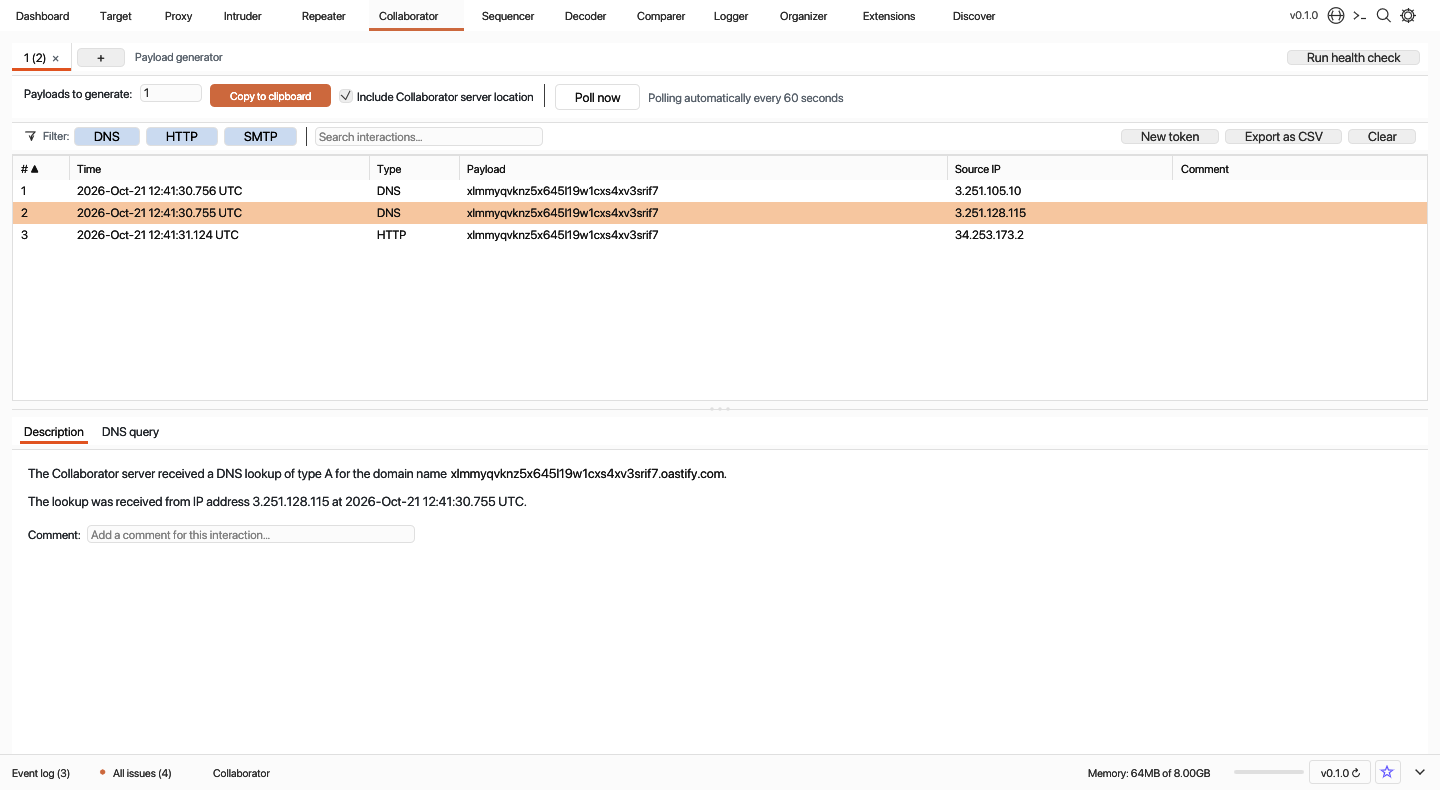
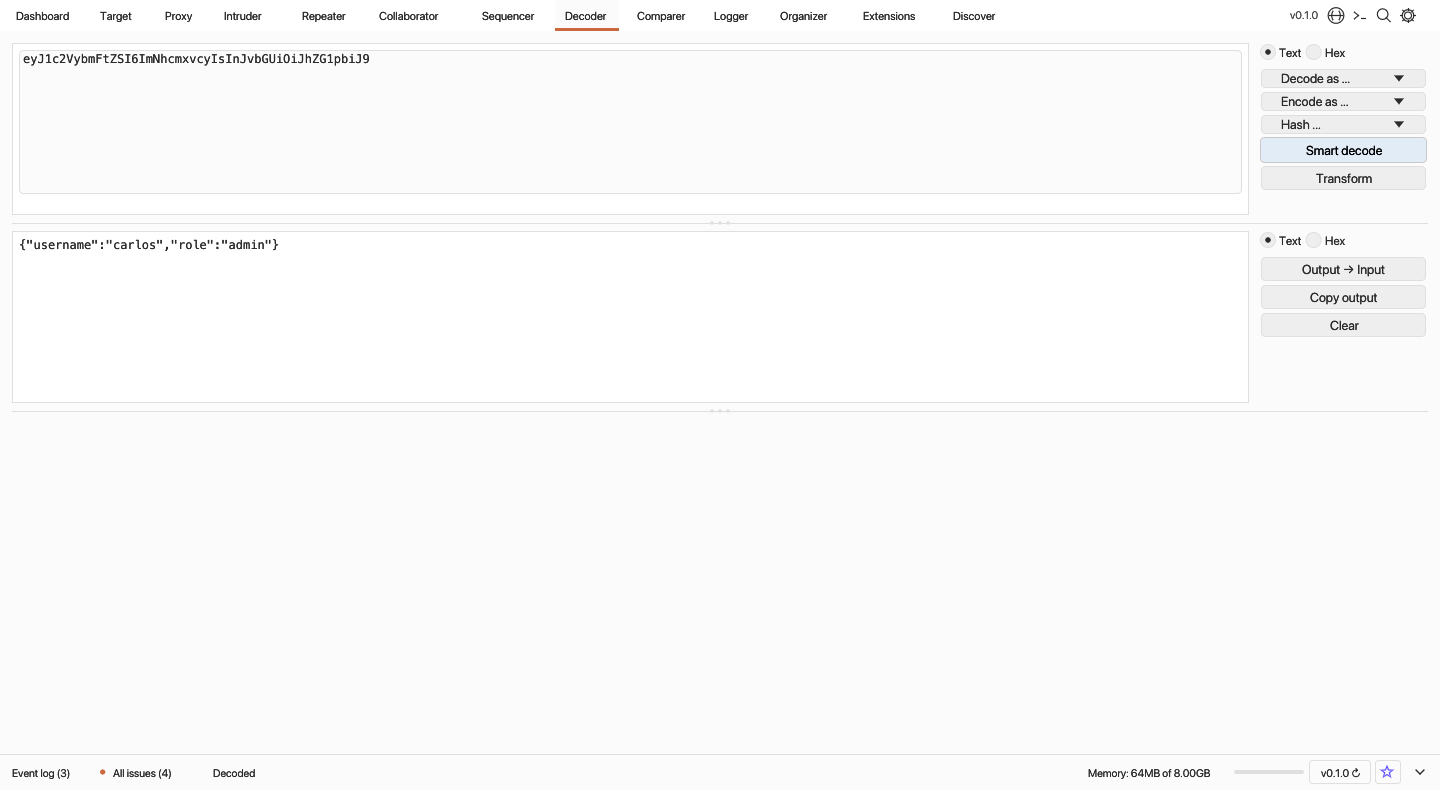
7. Decoder, Comparer, Sequencer, Collaborator, Logger, Organizer, Extensions & Discover
- Decoder: Multi-layer
Smart decode, URL, HTML, Base64, ASCII hex, Gzip, and SHA-256/SHA-512/MD5 transformations with live Text & Hex dump views and in-place selection conversion. - Comparer: Word-level and Byte-level visual diff engine for comparing any two requests or responses.
- Sequencer: FIPS-style token randomness and entropy analyzer (character-level & bit-level uniformity across live captures or manual token lists).
- Collaborator: Multi-tab out-of-band (OOB) DNS, HTTP, and SMTP interaction client & local listener server with payload generator, automatic 60s polling, protocol filters, health check probes, Base64 CSV export, and
Description/DNS query/Request to Collaborator/Response from Collaboratorinspection. - Logger: Full-fidelity stream of HTTP, WebSocket, DNS, and SMTP traffic across all tools.
- Organizer: Long-term request/response storage with collections, notes, and search.
- Extensions (Bambda): Live HTTP traffic filter and transformation scripting engine.
- Discover: Threaded directory and content discovery scanner.
- In-App Auto-Updater: Automatic startup & on-demand (
Help -> Check for updates…,Settings -> Suite -> Software Updates,Extensions -> Updates) GitHub Releases checker with SHA-256 verification and 1-click native installer launch across macOS, Windows, and Linux.
Building from Source
Prerequisites
- Rust toolchain (
rustup,cargo1.78+) - Python 3 (for cross-platform installer packaging)
Build Release Binaries & Run Full Test Suite
CARGO_PROFILE_DEV_DEBUG=0 CARGO_INCREMENTAL=0 ./build.sh
This compiles the optimized release binaries (./gulpsuite and ./gulpsuite-setup) and runs all unit, integration, and headless egui_kittest UI parity tests.
Cross-Platform Installation
- macOS / Linux:
./install.sh # or launch the graphical setup wizard: ./gulpsuite-setup - Windows:
install.bat
REM or launch the graphical setup wizard:
gulpsuite-setup.exe
Launch Gulpsuite
./gulpsuite       # macOS / Linux
gulpsuite.exe     # Windows
Build macOS .app Bundle
./bundle.sh
open Gulpsuite.app
Keyboard Shortcuts
| Shortcut | Action |
|---|---|
Cmd/Ctrl + R |
Send selected request to Repeater (or send active Repeater tab) |
Cmd/Ctrl + I |
Send selected request to Intruder (or toggle Proxy Intercept) |
Cmd/Ctrl + K / Cmd/Ctrl + F |
Open Command Palette & Global Search |
Cmd/Ctrl + , |
Open Global & Project Settings |
Alt + D / T / P / N / R / O / S / E / C / L / G / X / I |
Switch directly to Dashboard, Target, Proxy, Intruder, Repeater, Collaborator, Sequencer, Decoder, Comparer, Logger, Organizer, Extensions, or Discover |
Community & Governance
- Everyone Can Contribute: Pull requests, issues, vulnerability checks, and platform improvements are welcome from anyone! See the Contributing Guide.
- Code of Conduct
- Security Policy
License
Licensed under the permissive open-source MIT License — Copyright (c) 2026 Aryma-f4 and Gulpsuite Contributors. Provided for authorized security testing, research, and educational use.
Explore related projects
trimstray/the-book-of-secret-knowledge
A collection of inspiring lists, manuals, cheatsheets, blogs, hacks, one-liners, cli/web tools and more.
257,856 starsHack-with-Github/Awesome-Hacking
A collection of various awesome lists for hackers, pentesters and security researchers
125,254 starsswisskyrepo/PayloadsAllTheThings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
82,583 starscaddyserver/caddy
Fast and extensible multi-platform HTTP/1-2-3 web server with automatic HTTPS
78,959 stars