
gost
vulsio
150스타
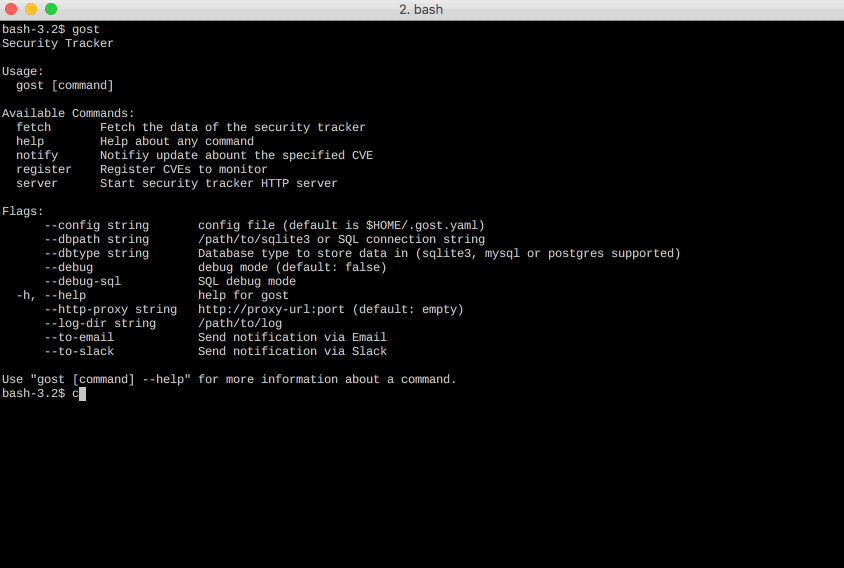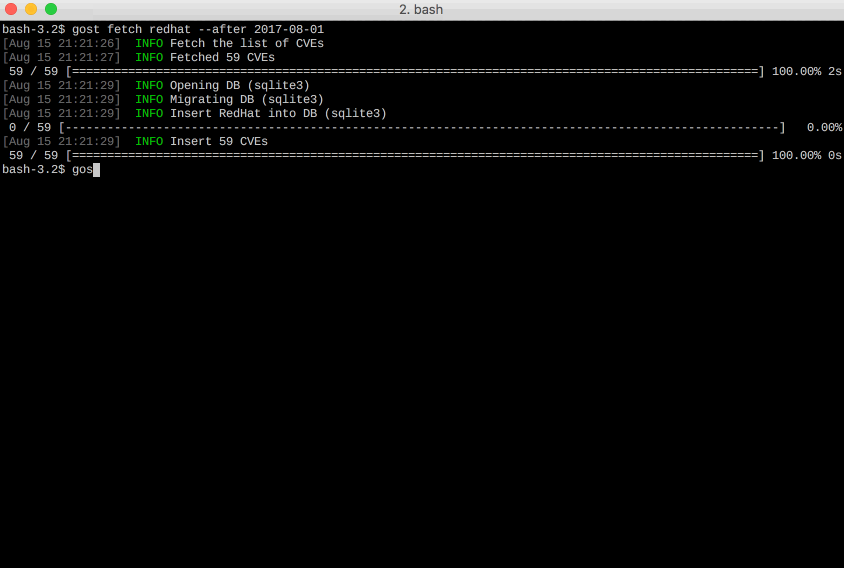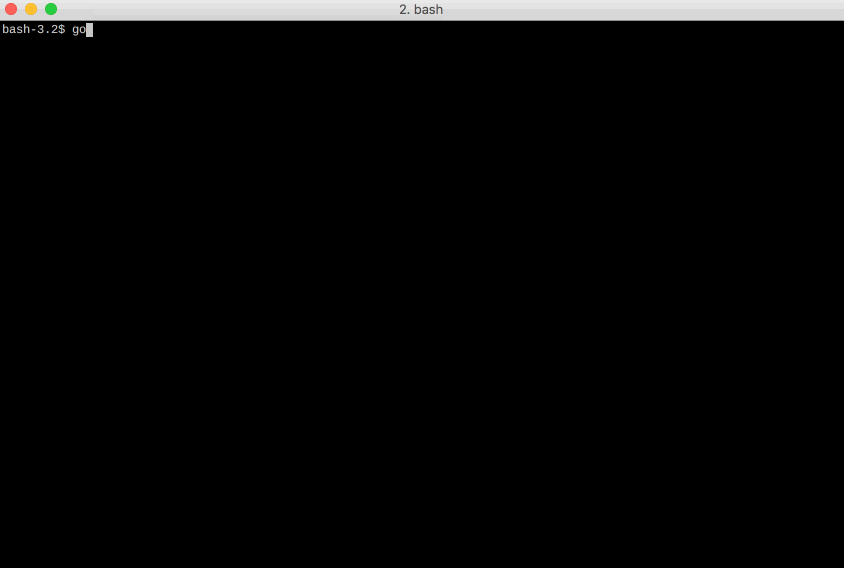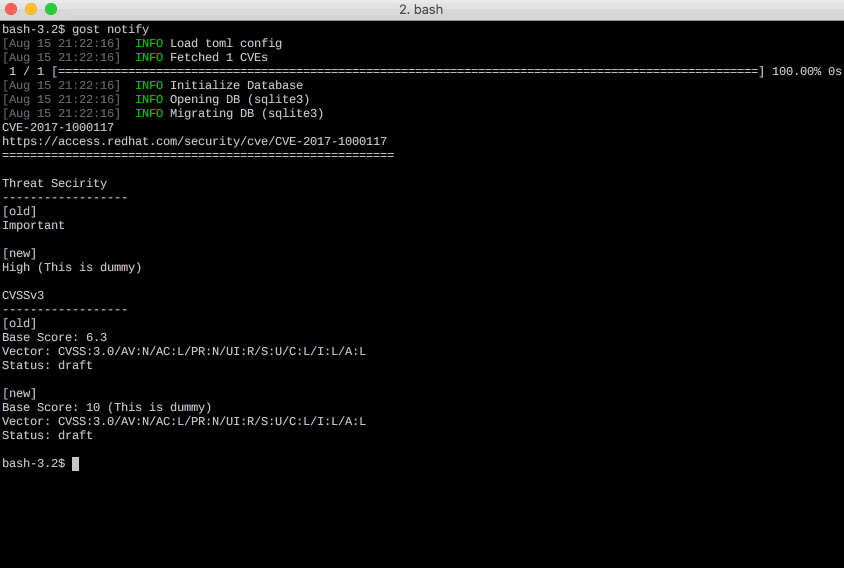
Build a local copy of Security Tracker. Notify via E-mail/Slack if there is an update.
- Build a local copy of Security Tracker
- A server mode for easy querying
취약점 탐지, 시스템 보호, 개인정보 보호 도구를 찾아보세요.
vulsio
Build a local copy of Security Tracker. Notify via E-mail/Slack if there is an update.

vuvuzela

Private messaging system that hides metadata

vxfemboy
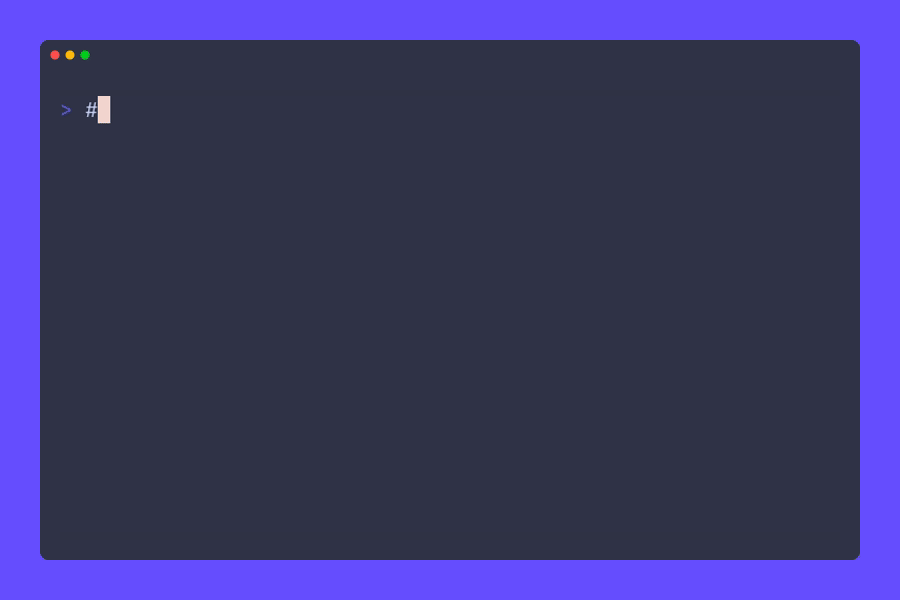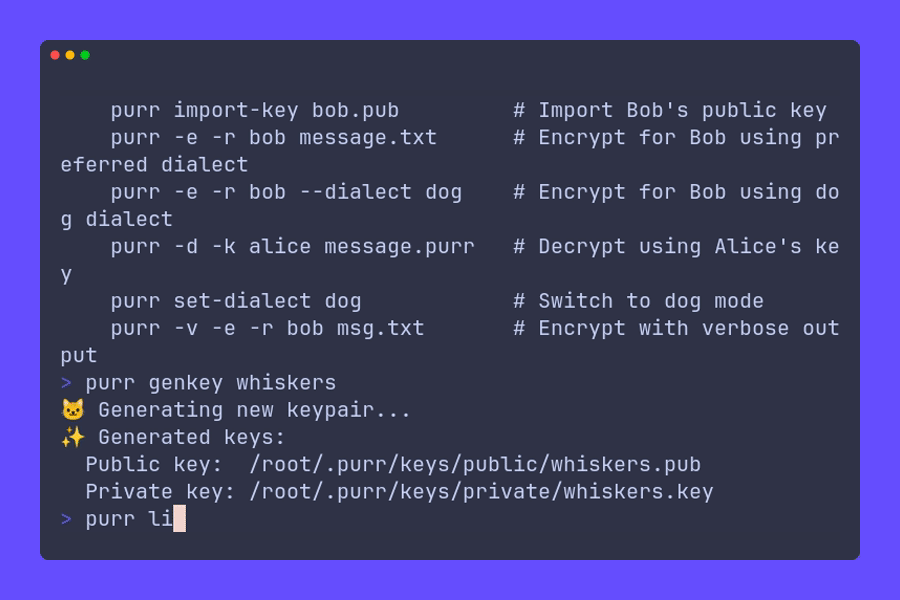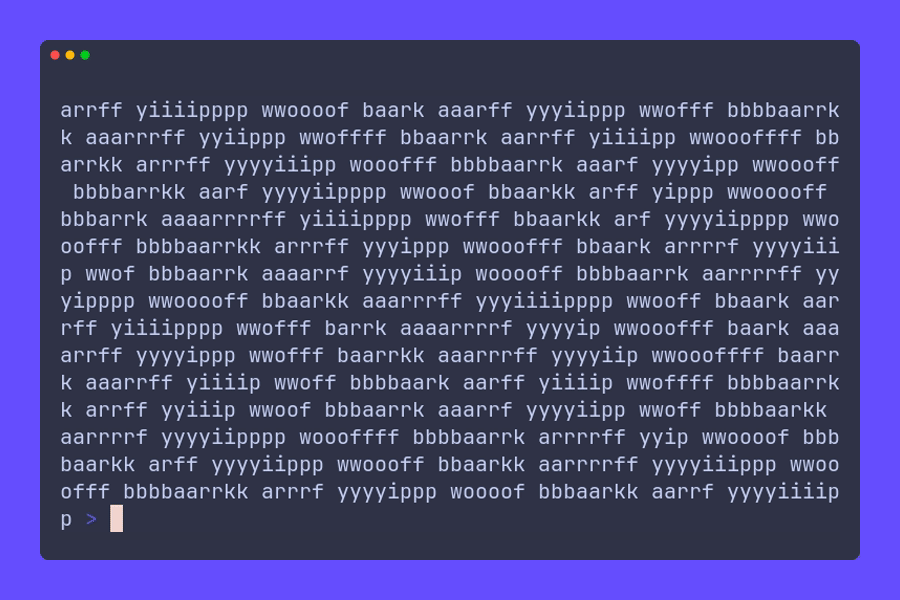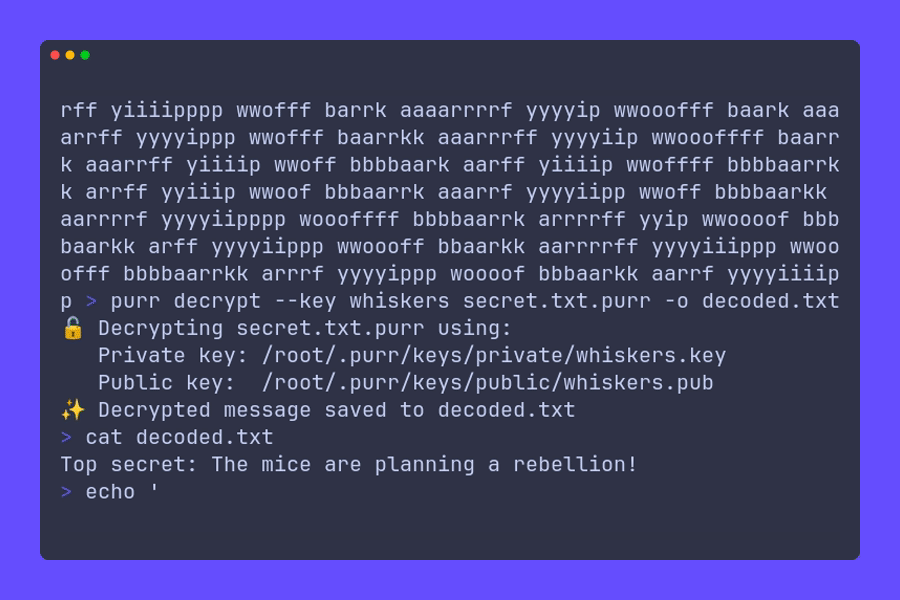
A fur-ociously secure encryption tool that encodes your secrets as adorable cat and dog sounds, using real elliptic curve cryptography with a playful disguise.

vxlang

protector & obfuscator & code virtualizer

vypdev
Android library to reveal or obfuscate strings and assets at runtime

W-A-LEE
Best Robux Balance and Transaction Privacy Hider Tool 2026

w-digital-scanner
Passive Security Scanner (被动式安全扫描器)

w0h1v
MCP server for Shodan — search internet-connected devices, IP reconnaissance, DNS lookups, and CVE/CPE vulnerability intelligence. Works with Claude Code, Codex, Gemini CLI, and Claude Desktop.
w0h1v
MCP server for VirusTotal API — analyze URLs, files, IPs, and domains with comprehensive security reports, relationship analysis, and pagination support.

w3h
ICS/SCADA Security Resource(整合工控安全相关资源)

w3h
ISF(Industrial Security Exploitation Framework) is a exploitation framework based on Python.

Wack0
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability

WADComs

WADComs is an interactive cheat sheet, containing a curated list of offensive security tools and their respective commands, to be used against Windows/AD environments.

wafpassproject
Analysing parameters with all payloads' bypass methods, aiming at benchmarking security solutions like WAF.

wagiro
Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and passive scanner by means of personalized rules through a very intuitive graphical interface.

wagov
WA Cyber Security Unit (DGOV Technical) site

wagslane
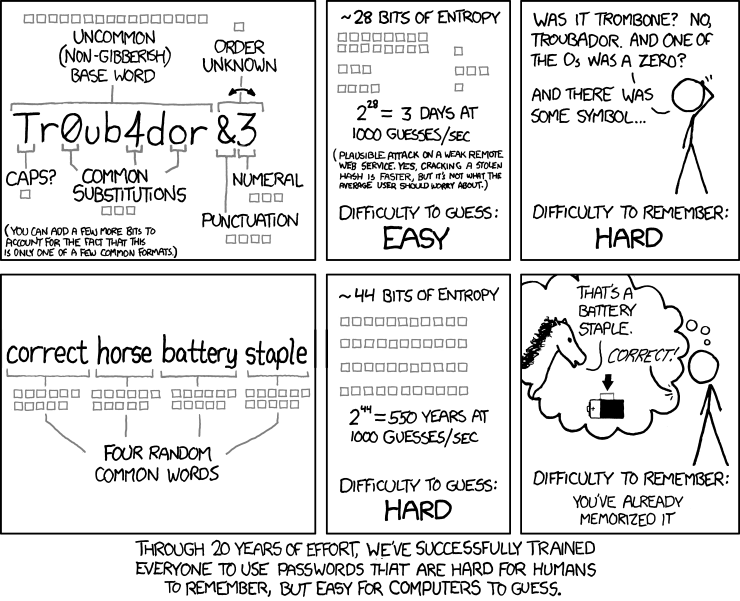
Validate the Strength of a Password in Go

waldo-van-der-code
Claude Code skill for German DSGVO/GDPR compliance — code audit, URL scan, data flow mapping, policy drafting. Grounded in live German federal law via rechtsinformationen.bund.de MCP.

walidshaari

Curated resources help you prepare for the CNCF/Linux Foundation CKS 2021 "Kubernetes Certified Security Specialist" Certification exam. Please provide feedback or requests by raising issues, or making a pull request. All feedback for improvements are welcome. thank you.

wallarm
🔥 A curated list of awesome links related to application security related to the environments with NGINX or Kubernetes Ingres Controller (based on NGINX)
wallarm

An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses

WalletWasabi
This is the Wasabi documentation, an archive of knowledge about the open-source, non-custodial and privacy-focused Bitcoin wallet for desktop.

wanglian

Slack alternative, email integrated, build with Meteor

warpnet
Gain insights into MS-RPC implementations that may be vulnerable using an automated approach and make it easy to visualize the data. By following this approach, a security researcher will hopefully identify interesting RPC services in such a time that would take a manual approach significantly more.