
smallstep/cli has 4,365 GitHub stars and 327 forks. GitHot measured +1 stars in 24 hours and +7 in 7 days. Last checked 2026-11-05 08:37 UTC. Last push 2026-10-30.
🧰 X509, OAuth, JWT, OATH OTP 등을 다루기 위한 제로 트러스트 스위스 아미 나이프.
What you can do
- Create, revoke, validate, lint, and bundle X.509 certificates.
- Install (and remove) X.509 certificates into your system's (and browser's) trust store.
- Validate certificate deployment and renewal status for automation
- Create key pairs (RSA, ECDSA, EdDSA) and certificate signing requests (CSRs)
측정된 스타 증가
- in 24h
- +1
- in 7 days
- +7
- in 15 days
- 기록 수집 중
- in 1 month
- 기록 수집 중
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
README.md
OriginalStep CLI


step is an easy-to-use CLI tool for building, operating, and automating Public Key Infrastructure (PKI) systems and workflows.
It's also a client for the step-ca online Certificate Authority (CA) server.
You can use it for many common crypto and X.509 operations—either independently, or with an online CA.
Questions? Ask us on GitHub Discussions or Discord.
Website | Documentation | Installation | Basic Crypto Operations | Contributor's Guide
Features
Step CLI's command groups illustrate its wide-ranging uses:
step certificate: Work with X.509 (TLS/HTTPS) certificates.- Create, revoke, validate, lint, and bundle X.509 certificates.
- Install (and remove) X.509 certificates into your system's (and browser's) trust store.
- Validate certificate deployment and renewal status for automation
- Create key pairs (RSA, ECDSA, EdDSA) and certificate signing requests (CSRs)
- Sign CSRs
- Create RFC5280 and CA/Browser Forum-compliant certificates that work for TLS and HTTPS
- Create CA certificates (root and intermediate signing certificates)
- Create self-signed & CA-signed certificates
- Inspect and lint certificates on disk or in use by a remote server
- Install root certificates so your CA is trusted by default (issue development certificates that work in browsers)
step ca: Administer and use astep-caserver, or any ACMEv2 (RFC8555) compliant CA server. ACME is the protocol used by Let's Encrypt to automate the issuance of HTTPS certificates.- Initialize an X.509 and/or SSH CA in one command
- Authenticate and obtain a certificate using any enrollment mechanism supported by
step-ca - Securely distribute root certificates and bootstrap PKI relying parties
- Renew and revoke certificates issued by
step-ca - Submit CSRs to be signed by
step-ca - With an ACME CA,
stepsupports thehttp-01challenge type
step crypto: A general-purpose crypto toolkit- Work with JWTs (RFC7519) and other JOSE constructs
- Sign, verify, and inspect JSON Web Tokens (JWTs)
- Sign, verify, and inspect arbitrary data using JSON Web Signature (JWS)
- Encrypt and decrypt data and wrap private keys using JSON Web Encryption (JWE)
- Create JWKs and manage key sets for use with JWT, JWE, and JWS
- Generate and verify TOTP tokens for multi-factor authentication (MFA)
- Work with NaCl's high-speed tools for encryption and signing
- Apply key derivation functions (KDFs) and verify passwords using
scrypt,bcrypt, andargon2 - Generate and check file hashes
- Work with JWTs (RFC7519) and other JOSE constructs
step oauth: Add an OAuth 2.0 single sign-on flow to any CLI application.- Supports OAuth authorization code, out-of-band (OOB), JWT bearer, and refresh token flows
- Get OAuth access tokens and OIDC identity tokens at the command line from any provider.
- Verify OIDC identity tokens (
step crypto jwt verify)
step ssh: Create and manage SSH certificates (requires an online or offlinestep-cainstance)- Generate SSH user and host key pairs and short-lived certificates
- Add and remove certificates to the SSH agent
- Inspect SSH certificates
- Login and use single sign-on SSH
Installation
See our installation docs here.
Example
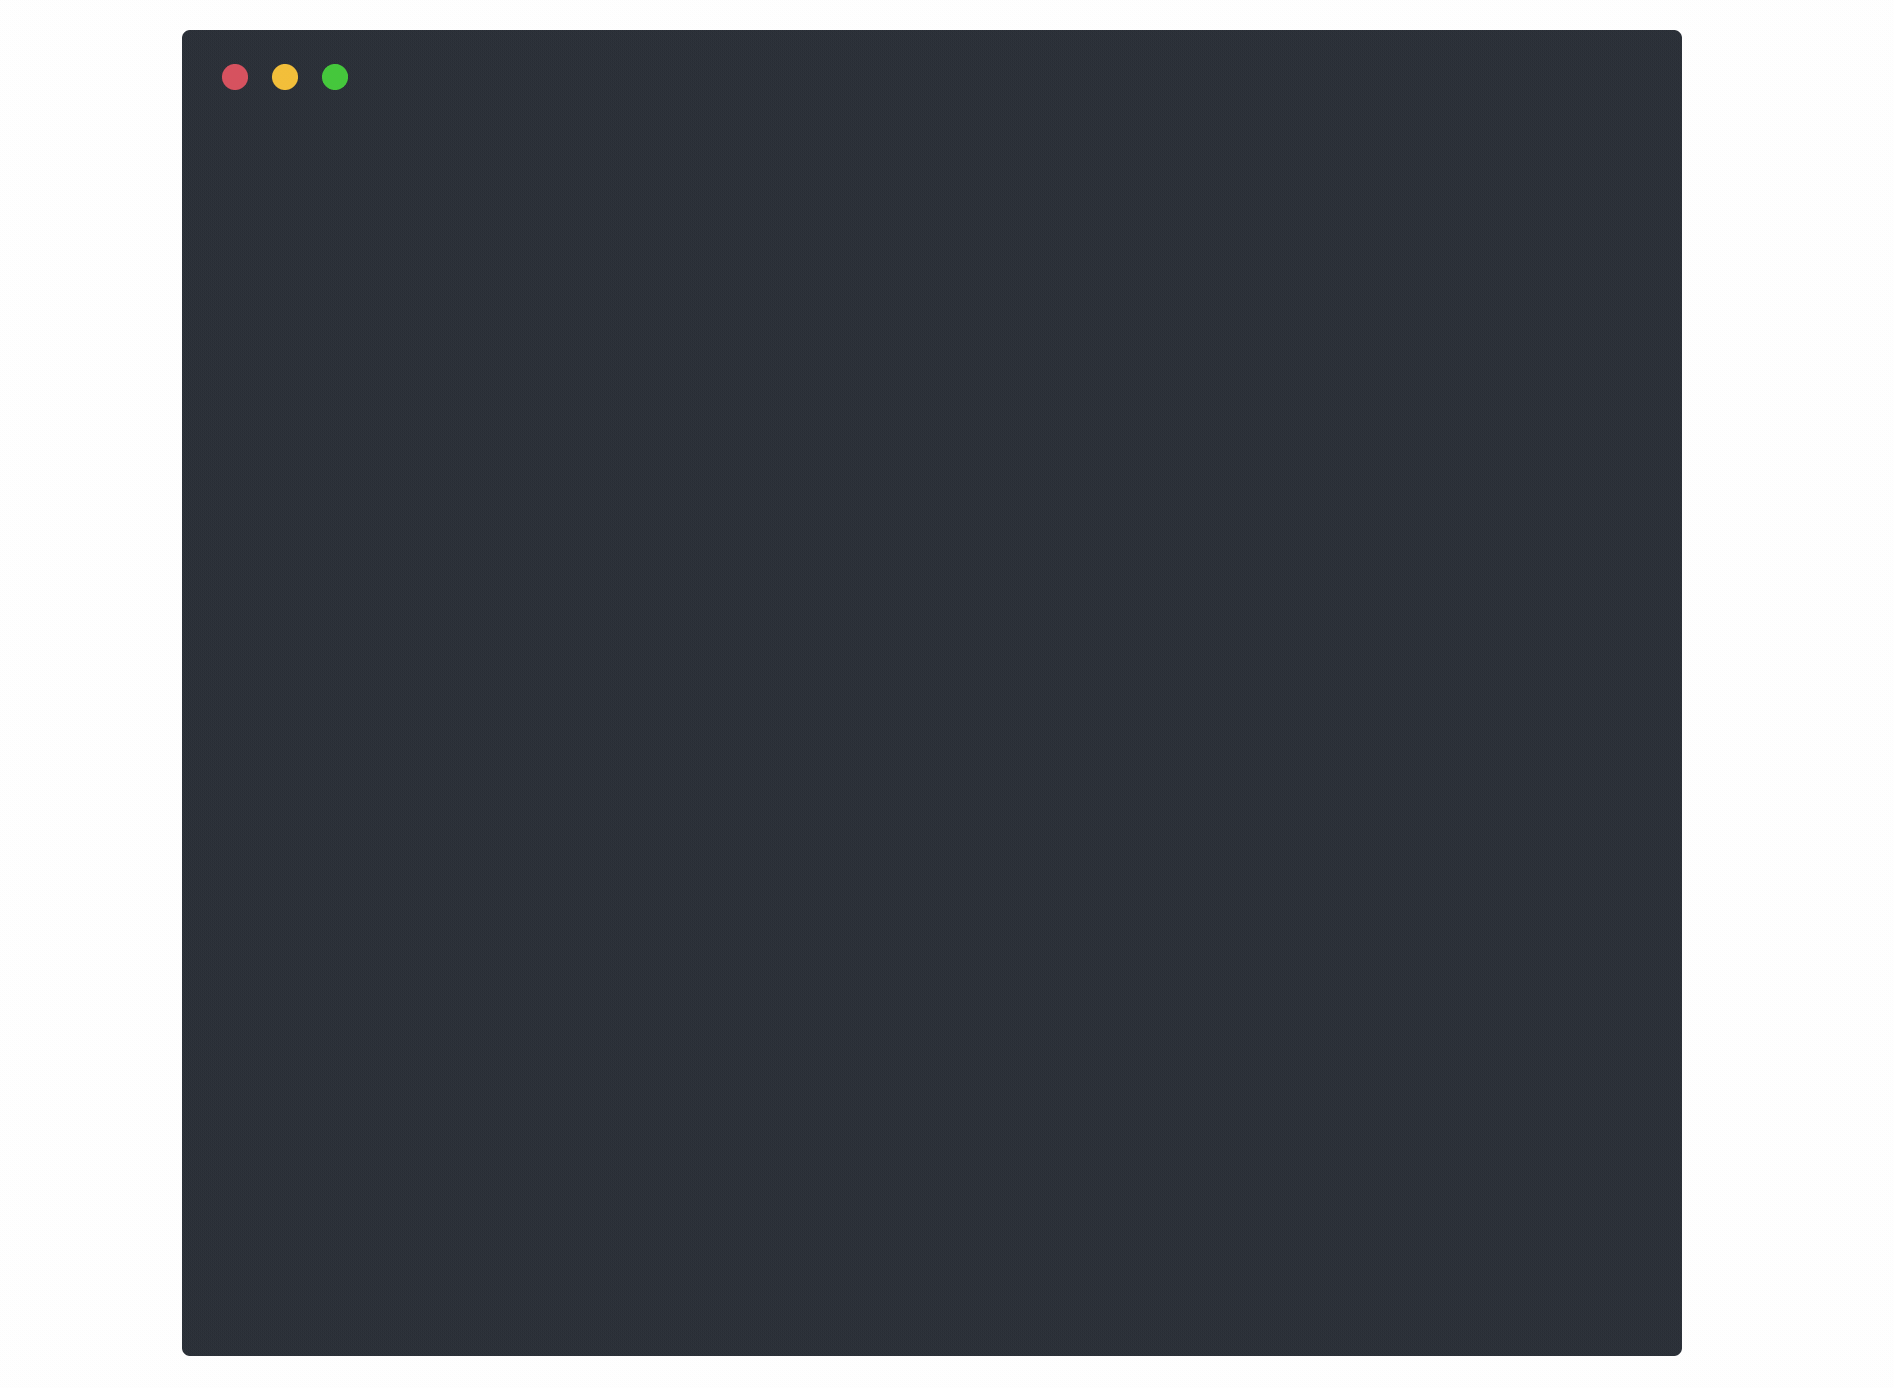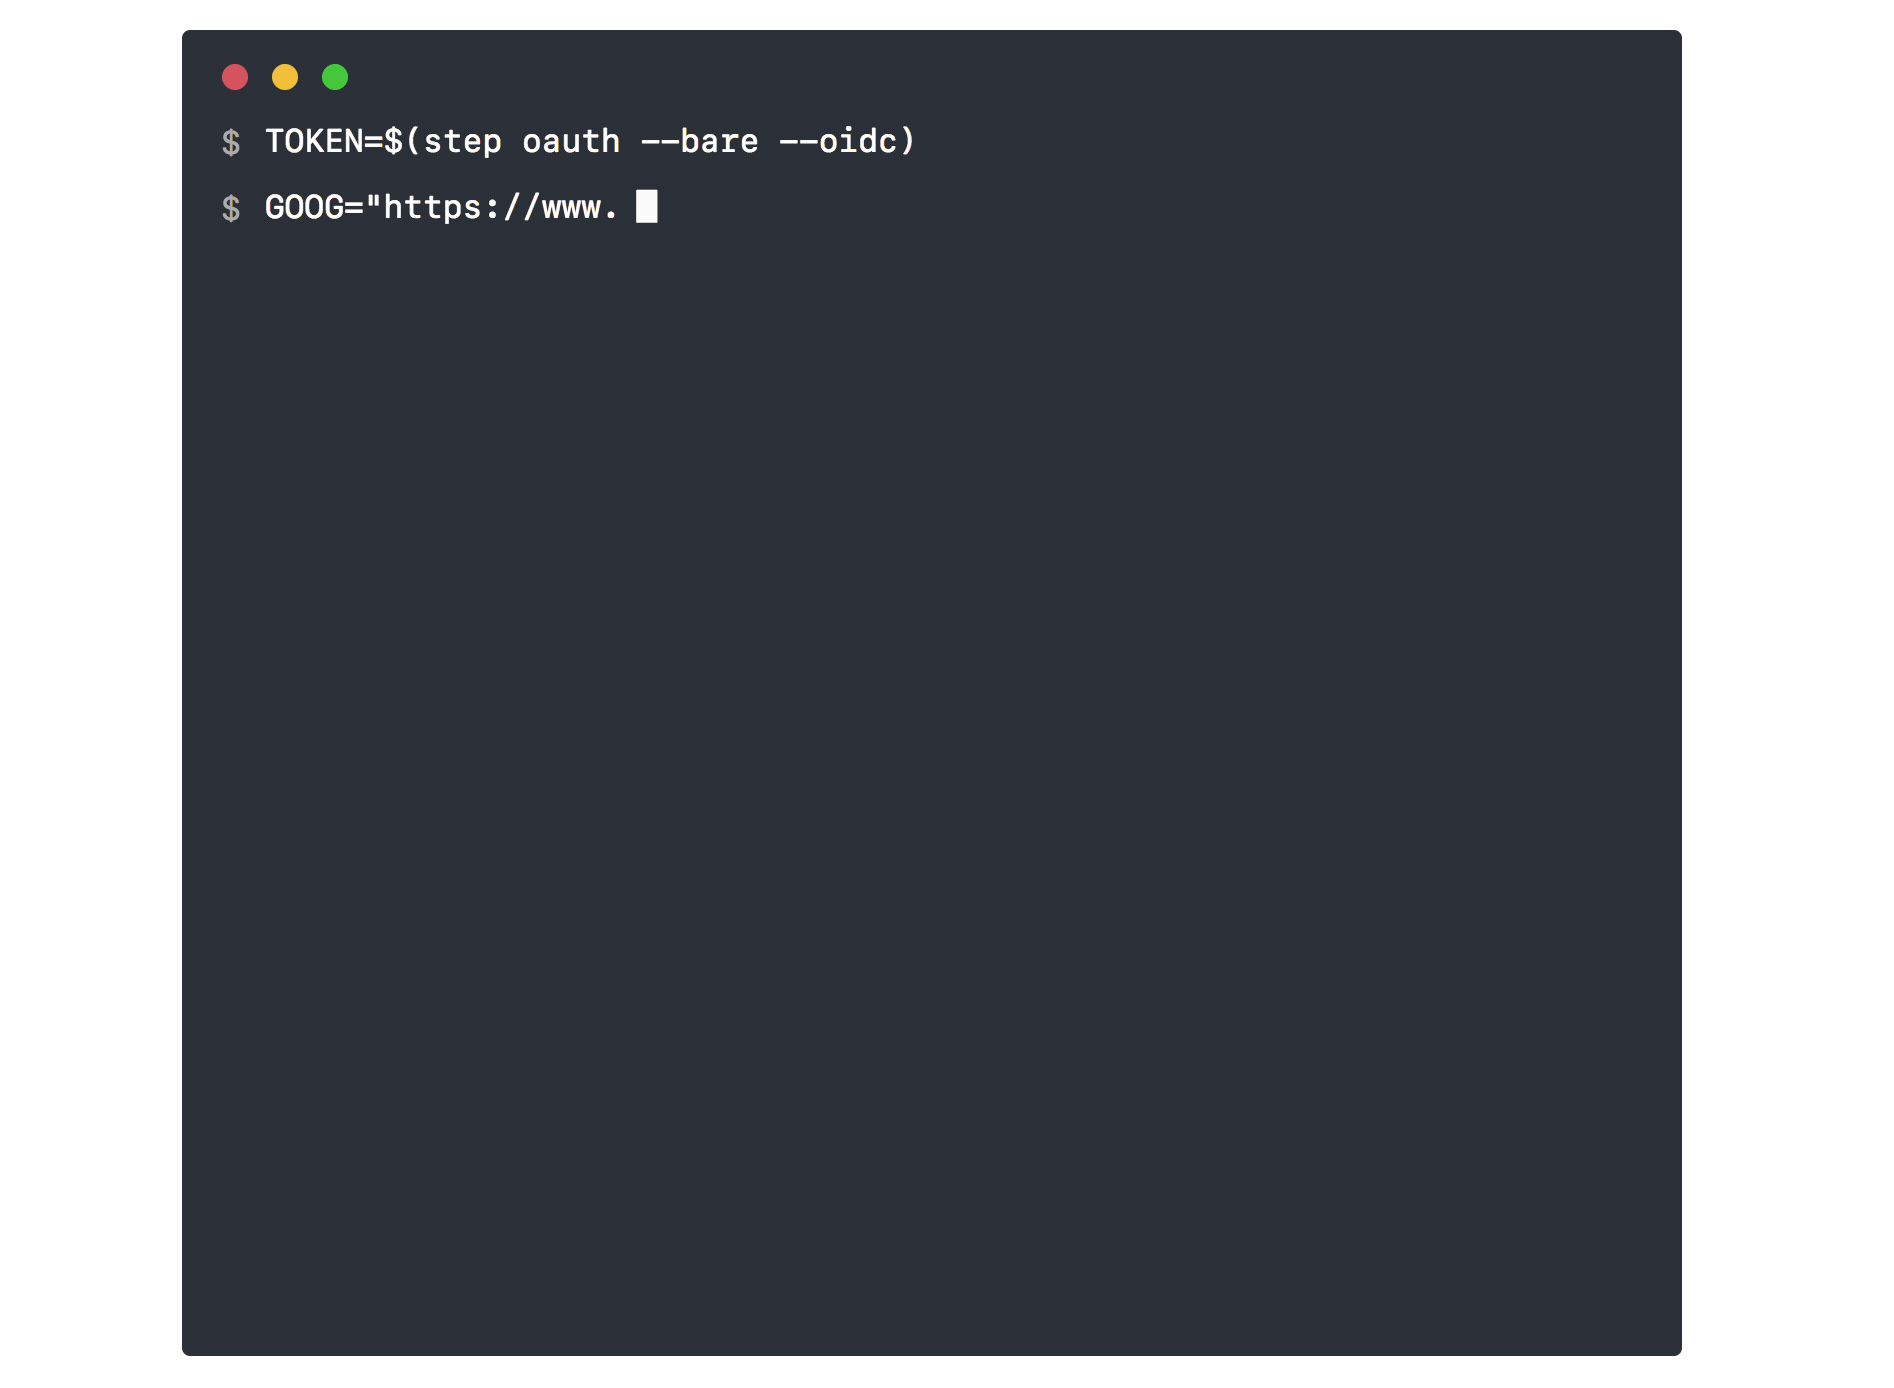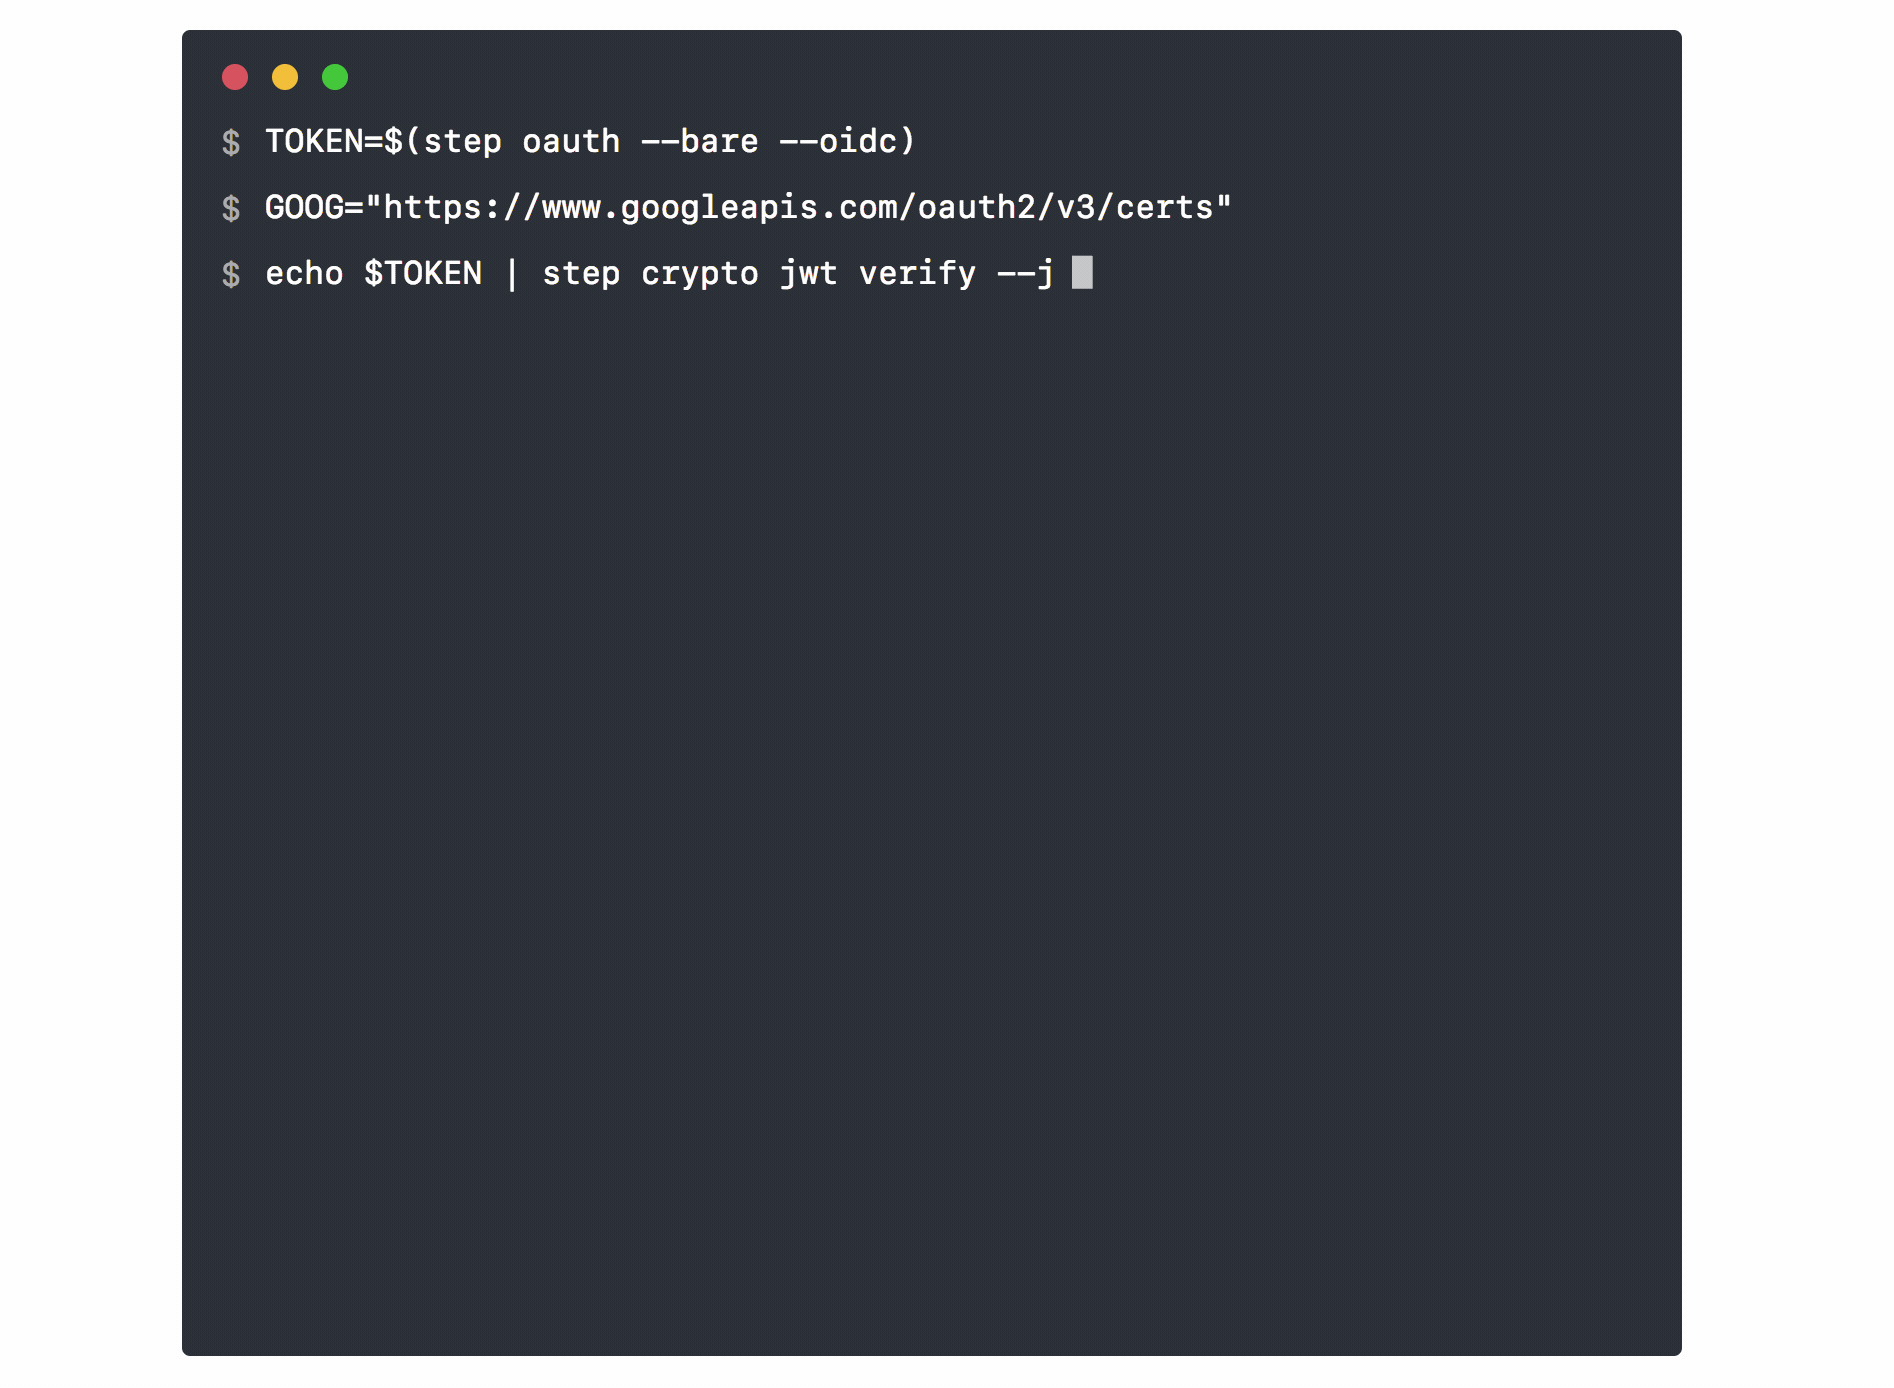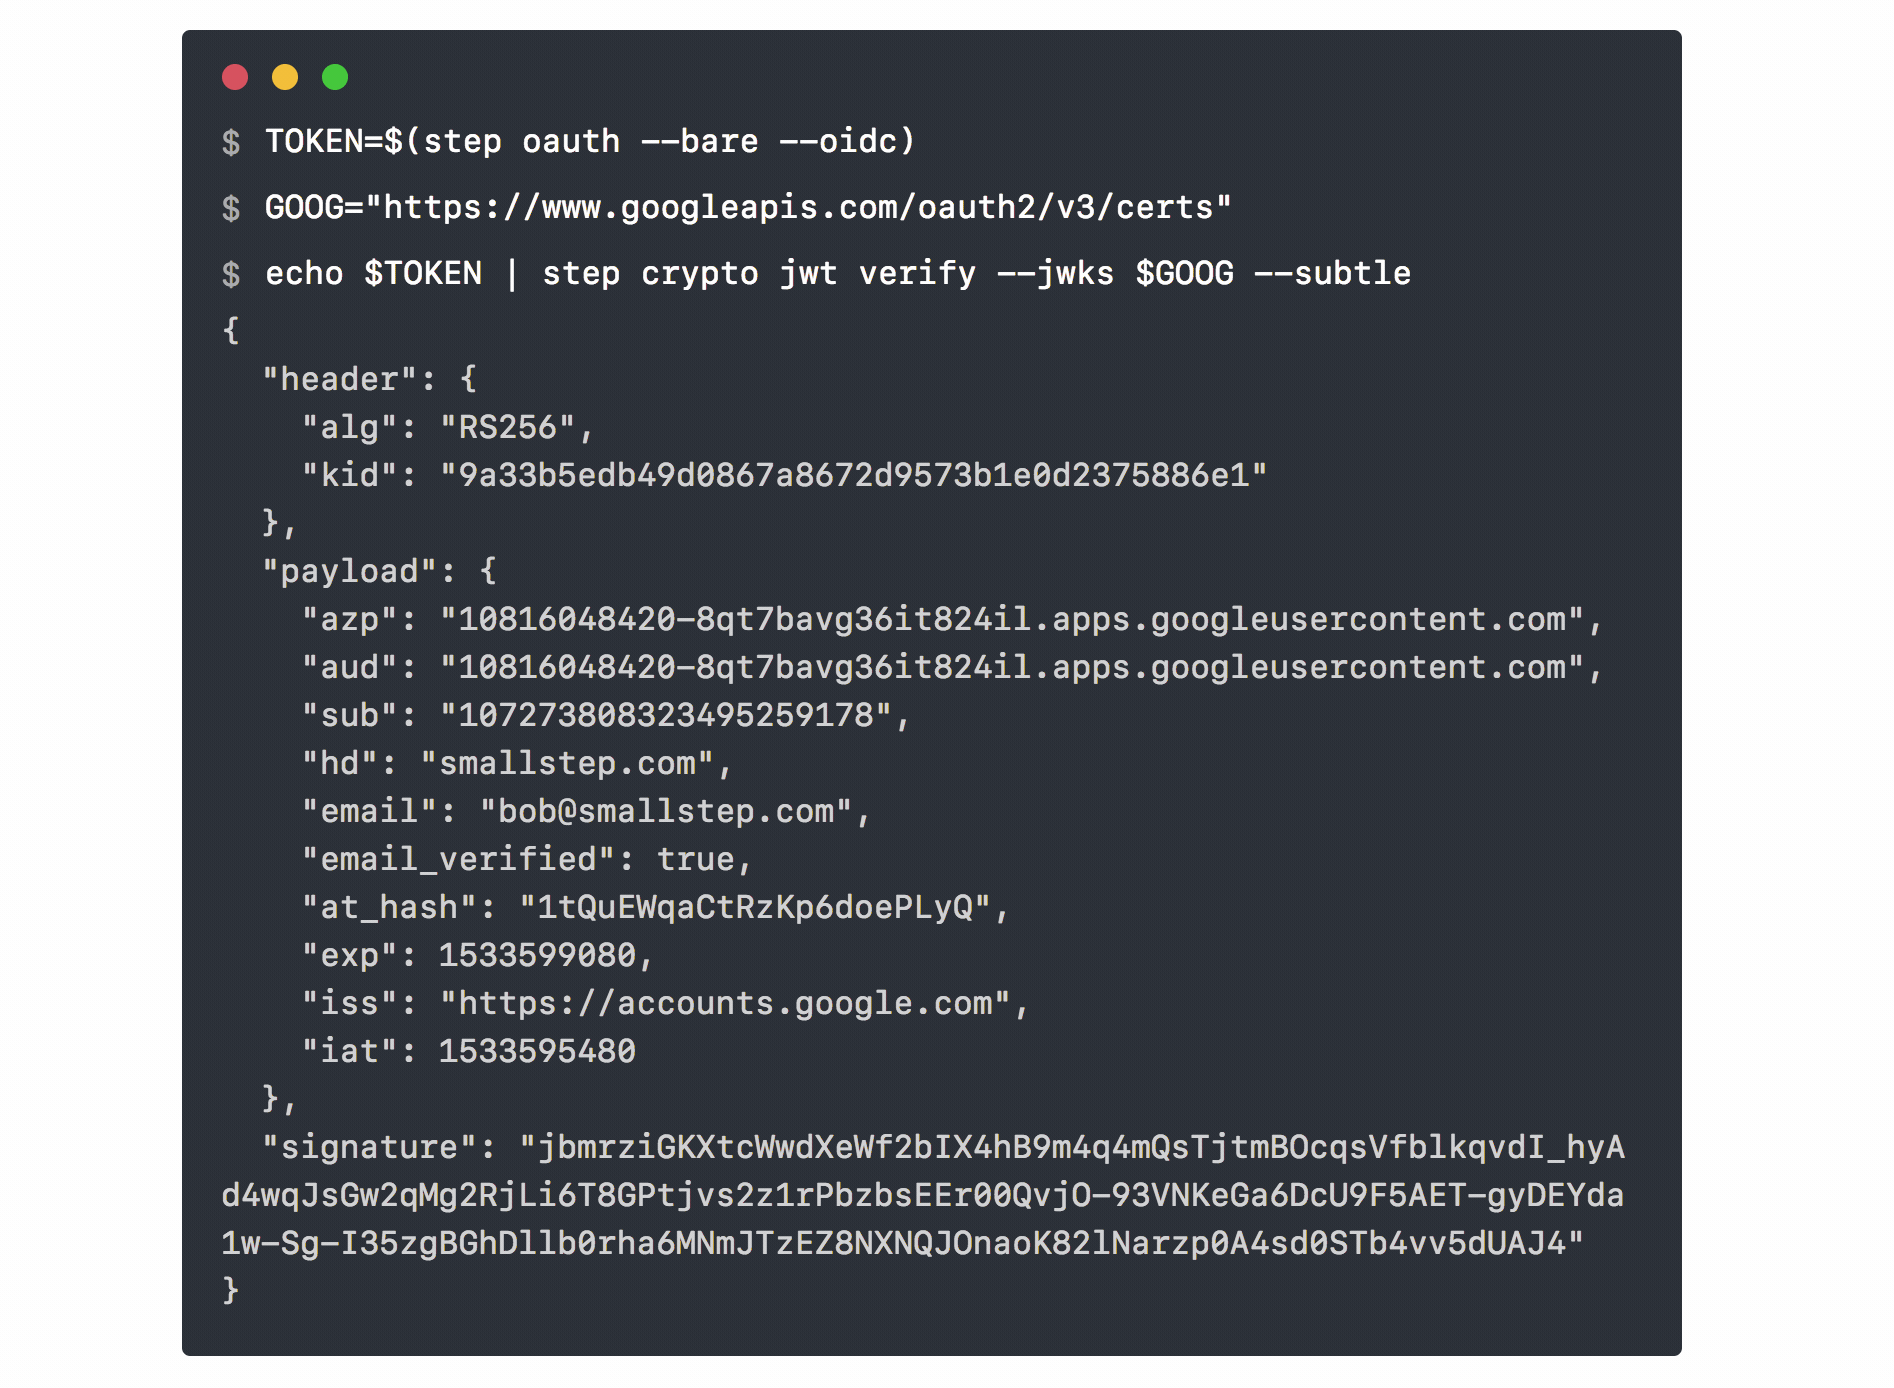
Here's a quick example, combining step oauth and step crypto to get and verify the signature of a Google OAuth OIDC token:
Plugins
A plugin is an executable file named using the format step-<name>-plugin.
Plugins must be available in your $PATH or in the $STEPPATH/plugins
directory (that's $HOME/.step/plugins, by default).
When you run step <name>, the CLI will automatically execute the corresponding
plugin, if found.
Some known plugins include:
- step-kms-plugin: Manage keys and certificates stored in a KMS, including HSMs, TPMs, YubiKeys, the macOS Keychain, and cloud KMSs.
- step-kmsproxy-plugin: Provides an HSM/KMS-backed authenticating proxy for mTLS services. Thanks to @andsens for creating and maintaining this plugin!
step-kms-plugin is also integrated directly into step to create
certificates, generate CSRs, sign tokens, and more using KMS-backed keys.
Community
- Connect with
stepusers on GitHub Discussions or Discord - Open an issue and tell us what features you'd like to see
- Contribute to the
stepcodebase - Follow Smallstep on Twitter
Further Reading
- Full documentation for
step - We have more examples of
stepandstep-cain action on the Smallstep blog. - If you're new to PKI and X.509 certificates, or you want a refresher on the core concepts, you may enjoy Everything PKI.
관련 프로젝트 살펴보기
trimstray/the-book-of-secret-knowledge
영감을 주는 목록, 매뉴얼, 치트시트, 블로그, 팁, 원라이너, CLI/웹 도구 등을 모은 컬렉션.
256,017 스타Hack-with-Github/Awesome-Hacking
해커, 펜테스터, 보안 연구자를 위한 다양한 Awesome 목록 모음.
124,649 스타swisskyrepo/PayloadsAllTheThings
웹 애플리케이션 보안과 모의 침투 테스트/CTF에 유용한 페이로드 및 우회 방법 목록.
82,393 스타caddyserver/caddy
빠르고 확장 가능한 멀티플랫폼 HTTP/1-2-3 웹 서버이며, 자동 HTTPS를 지원합니다
78,786 스타