
seebom-labs/BOMHort
seebom-labs/BOMHort has 62 GitHub stars and 15 forks. Star changes are not measured yet. Last checked 2026-11-11 01:13 UTC. Last push 2026-11-05.
About standalone, Kubernetes-native Software Bill of Materials (SBOM) visualization and governance platform
측정된 스타 증가
- in 24h
- 업데이트 지연
- in 7 days
- 기록 수집 중
- in 15 days
- 기록 수집 중
- in 1 month
- 기록 수집 중
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
README.md
Original
Kubernetes-native Software Bill of Materials (SBOM) Visualization & Governance Platform

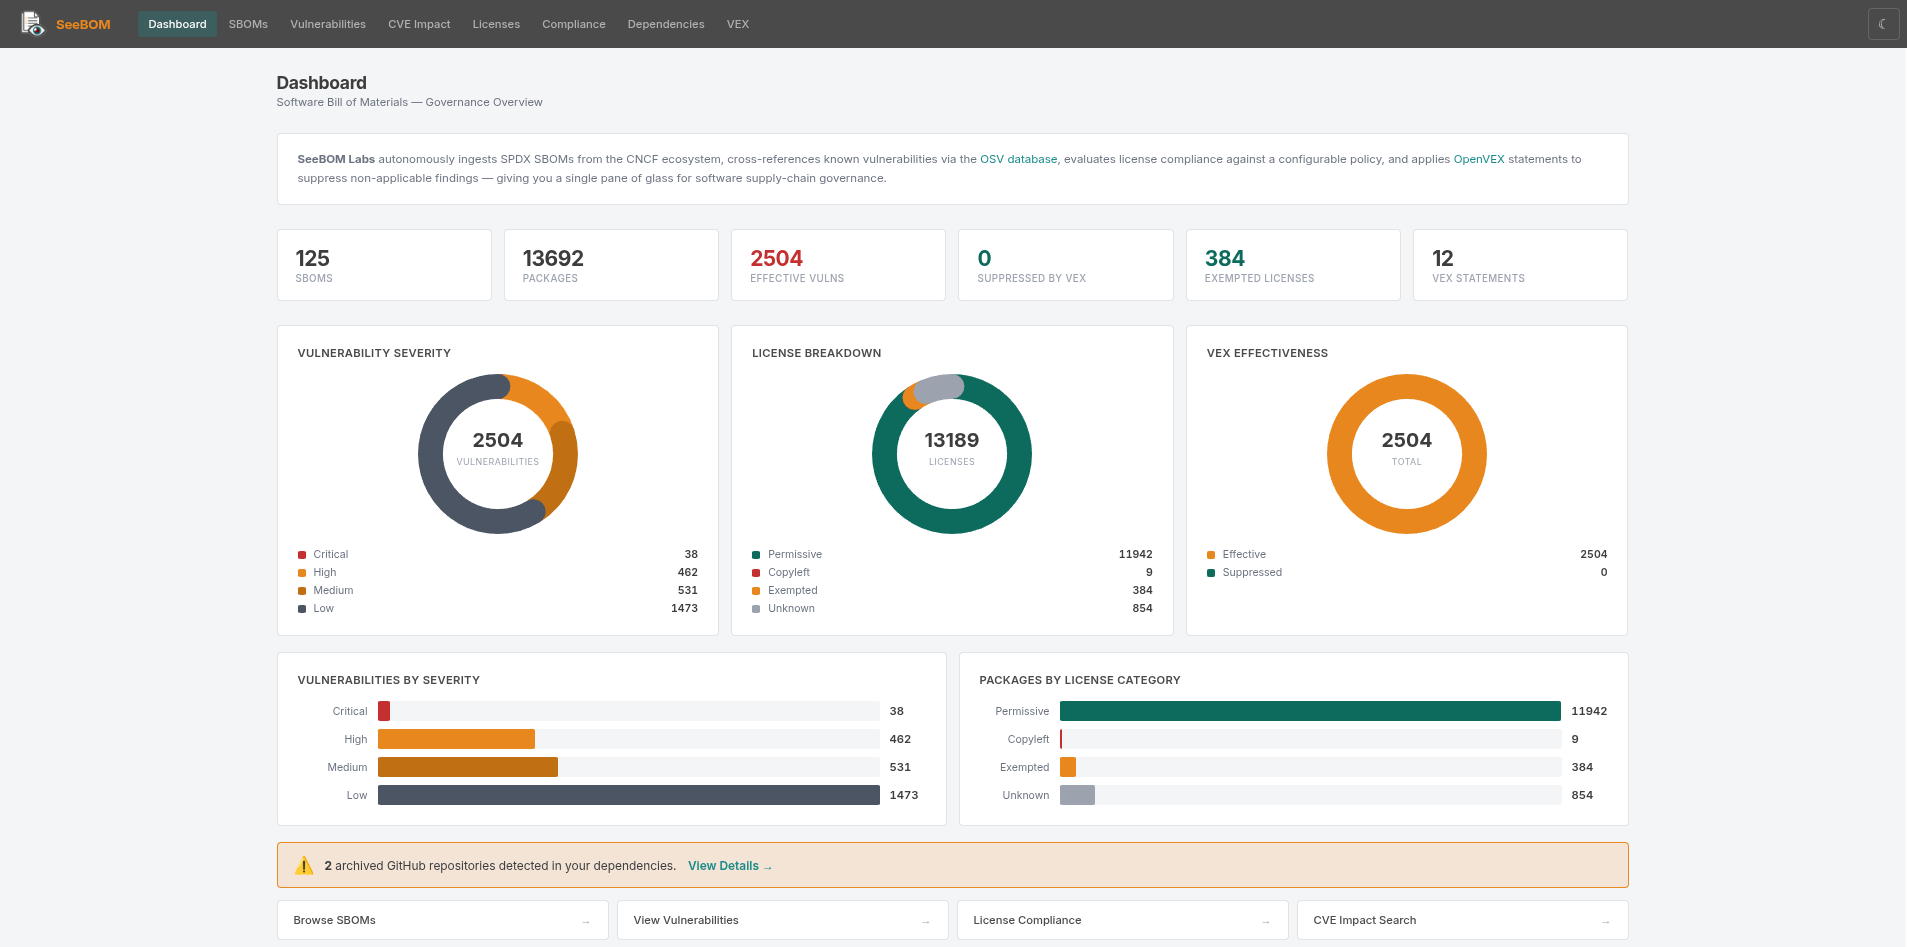
Ingest 1000+ SPDX and CycloneDX SBOMs, scan for vulnerabilities via OSV, enforce license compliance, and apply VEX statements — all visualized in a fast Angular dashboard backed by ClickHouse analytics.
BOMHort (formerly known as SeeBOM) is the same project with a new name. Read more: Why we renamed SeeBOM to BOMHort.
Getting Started · Deployment · API Reference · Architecture · Roadmap · Contributing
What it does
- Ingests at scale — SPDX 2.x JSON, SPDX 3 JSON-LD, CycloneDX 1.0–1.7 and in-toto attestation envelopes, auto-detected, from S3-compatible buckets, a directory, or
POST /api/v1/sboms/upload. Deduplicated by SHA-256, retained forever. - Finds vulnerabilities — OSV batch lookups at ingest, plus a daily refresher that checks every known package URL for newly disclosed CVEs without re-scanning a single SBOM. Findings carry their CVE id and all aliases.
- Applies VEX — OpenVEX statements scoped to the SBOM whose product they describe, with provenance; order of arrival does not matter.
- Enforces license policy — an externalized permissive/copyleft policy, SPDX expression evaluation, and reviewed exceptions that reload live and apply retroactively to every SBOM already ingested. Unknown licenses are resolved from GitHub, npm, NuGet, deps.dev, Packagist and PyPI, and every package records where its license came from — or why it is still unknown.
- Shows ownership — every record is tagged with cluster, namespace and project (from configuration or the ingestion path) and free-form tags, so a fleet reads as a tree, not a list.
- Serves agents — an optional read-only MCP server exposes the same REST contract to AI assistants, without database credentials.
Quick Start
git clone https://github.com/seebom-labs/BOMHort.git && cd BOMHort
cp .env.example .env            # optional: SBOM source, GitHub token, worker count
# drop your SBOMs (and *.openvex.json files) into sboms/, then
make dev                        # ClickHouse + API + workers + UI via Docker Compose
Open http://localhost:8090. The API is on localhost:8080, ClickHouse on localhost:9000.
| Want to… | Run | Details |
|---|---|---|
| Try it on a local Kubernetes cluster | make kind-up |
Kind example |
| Iterate on the code with hot reload | make ch-only && make ch-migrate, then make api / make worker / make ui-dev |
Development |
| Deploy to Kubernetes | helm install bomhort oci://ghcr.io/seebom-labs/bomhort/charts/bomhort |
Deployment guide, example values |
make help lists every target.
Configuration
Everything is configured through environment variables (locally: .env; in Kubernetes: Helm values rendered into a ConfigMap) and three JSON files. Nothing is downloaded or approved silently.
| What | Where | Documentation |
|---|---|---|
| SBOM sources — S3 buckets, directory, push uploads | S3_BUCKETS, SBOM_SOURCE_DIR |
Deployment → SBOMs |
| Ownership — cluster, namespace, project, tags | CLUSTER_NAME, NAMESPACE, PROJECT, INGEST_PATH_LAYOUT, TAGS |
Fleet Views |
| License policy — which SPDX IDs are permissive or copyleft, how expressions fold | license-policy.json, LICENSE_EXPRESSION_MODE |
Deployment → License Policy |
| License exceptions — reviewed approvals from Helm values, your own ConfigMap, or an https / S3 source; reloaded live, applied retroactively | license-exceptions.json, EXCEPTIONS_SOURCE, EXCEPTIONS_REFRESH_INTERVAL |
License Exceptions, example |
| License resolution — registry resolvers, normalization, provenance | GITHUB_TOKEN, SKIP_*_RESOLVE |
License Resolution |
| UI branding — theme CSS, texts, logo | CUSTOM_THEME, UI_CONFIG, ui.siteConfig |
Deployment → Custom Theme / Site Configuration |
| API authentication, query limits, upload size | AUTH_ENABLED, SERVICE_TOKEN, API_KEYS, CLICKHOUSE_MAX_*, MAX_UPLOAD_SIZE_MB |
Deployment → API Authentication |
The complete variable reference with defaults is in Getting Started → Configuration; .env.example documents the same set inline.
Architecture
  S3 buckets / directory / POST upload
                │
                ▼
   ┌──────────────────────┐   CronJob: lists sources, deduplicates by
   │  Ingestion Watcher   │   SHA-256, enqueues jobs in ClickHouse
   └──────────┬───────────┘
              ▼
   ┌──────────────────────┐   N stateless replicas: parse, resolve
   │  Parsing Workers     │   licenses, batch-insert, OSV lookup,
   └──────────┬───────────┘   license check, VEX, exception re-check
              ▼
   ┌──────────────────────┐   ┌──────────────────────┐
   │  ClickHouse          │◄──│  CVE Refresher       │  daily: new CVEs
   └──────────┬───────────┘   └──────────────────────┘  for known PURLs
              ▼
   ┌──────────────────────┐   stateless REST API
   │  API Gateway         │◄──────────────┐
   └──────────┬───────────┘               │
              ▼                           │
   ┌──────────────────────┐   ┌───────────┴──────────┐
   │  Angular UI          │   │  MCP Server (opt.)   │  read-only tools,
   └──────────────────────┘   └──────────────────────┘  no DB credentials
Five Go binaries, one Angular UI, one ClickHouse database, one Helm chart, one repository. The parsing pipeline resolves licenses before inserting, so the stored packages carry the resolved values from the start. Details: Architecture, ARCHITECTURE_PLAN.md.
Documentation
| Page | Covers |
|---|---|
| Getting Started | Docker Compose, Kind, hot reload, every environment variable |
| Deployment | Helm chart: SBOM sources, ownership, license policy, theming, authentication, ingress, upgrades |
| License Exceptions | Exception sources, live reload, retroactive application, Argo CD |
| License Resolution | How a package gets its license, and the decision log behind every heuristic |
| Fleet Views | Cluster → namespace → project, tags, a runnable demo |
| API Reference | All REST endpoints with request and response examples |
| MCP Server | Running the MCP server and what an agent can ask |
| Architecture | Components, data model, parsing pipeline |
| Release | Support policy, release branches, backports |
| Development | Code style, tests, parsers, contributor ladder, AI policy |
| FAQ | Common questions and troubleshooting |
In-repo: DEPLOYMENT_GUIDE.md · RELEASE.md · TESTING.md · examples/
Tech Stack
| Layer | Technology |
|---|---|
| Backend | Go 1.26, net/http (stdlib), seven direct dependencies |
| Database | ClickHouse (MergeTree family), managed by the ClickHouse Operator in Kubernetes |
| Frontend | Angular, standalone components, CDK virtual scrolling |
| Vulnerabilities | OSV.dev API |
| VEX | OpenVEX |
| Deployment | Helm 3, Docker Compose |
Subprojects
The seebom-labs organization hosts additional BOMHort subprojects:
- BOMcompare — Lightweight SBOM comparison tool.
- bomhort-website — Public website and landing pages for BOMHort.
See all repositories: https://github.com/seebom-labs
Contributing
We welcome contributions! See the Contributing Guide for how to get started.
License
관련 프로젝트 살펴보기
trimstray/the-book-of-secret-knowledge
영감을 주는 목록, 매뉴얼, 치트시트, 블로그, 팁, 원라이너, CLI/웹 도구 등을 모은 컬렉션.
257,462 스타Hack-with-Github/Awesome-Hacking
해커, 펜테스터, 보안 연구자를 위한 다양한 Awesome 목록 모음.
125,103 스타swisskyrepo/PayloadsAllTheThings
웹 애플리케이션 보안과 모의 침투 테스트/CTF에 유용한 페이로드 및 우회 방법 목록.
82,542 스타caddyserver/caddy
빠르고 확장 가능한 멀티플랫폼 HTTP/1-2-3 웹 서버이며, 자동 HTTPS를 지원합니다
78,935 스타