
nextcloud/twofactor_totp
nextcloud/twofactor_totp has 321 GitHub stars and 58 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-14 05:46 UTC. Last push 2026-11-13.
측정된 스타 증가
- in 24h
- 0
- in 7 days
- 기록 수집 중
- in 15 days
- 기록 수집 중
- in 1 month
- 기록 수집 중
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
소개
🔑 Second factor TOTP (RFC 6238) provider for Nextcloud
보안README.md
OriginalTwo Factor Totp


Tested with the following apps:
- Aegis (open source) Available via F-Droid and Google Play. It features a built-in QR-code reader.
- FreeOTPPlus (open source) Available via F-droid and Google Play.
- OTP Authenticator (open source) Available via F-Droid and Google Play. It features a built-in QR-code reader.
- Google Authenticator (proprietary)
- KeePassXC (Linux, Windows, macOS) (open-source) Available via download, package repositories or GitHub (Keepass also provides a plugin and Keepass2Android allows you to use a TOTP token)
- SailOTP (SailfishOS) (open source) Available via JollaStore or Openrepos.net
- OTP Auth (proprietary) Available via Apple's App Store
- Authy (Twilio Authy) (proprietary) for Android and IOS. Available via Google Play and Apple's App Store
Tested with the following hardware devices:
Installation
Nextcloud 25 and newer
The app is shipped and comes with the installation of Nextcloud Server. No additional steps are necessary, besides activating it.
Nextcloud 24 and older
The app is available through the app store. It can be installed through Nextcloud's app management UI.
Enabling TOTP 2FA for your account

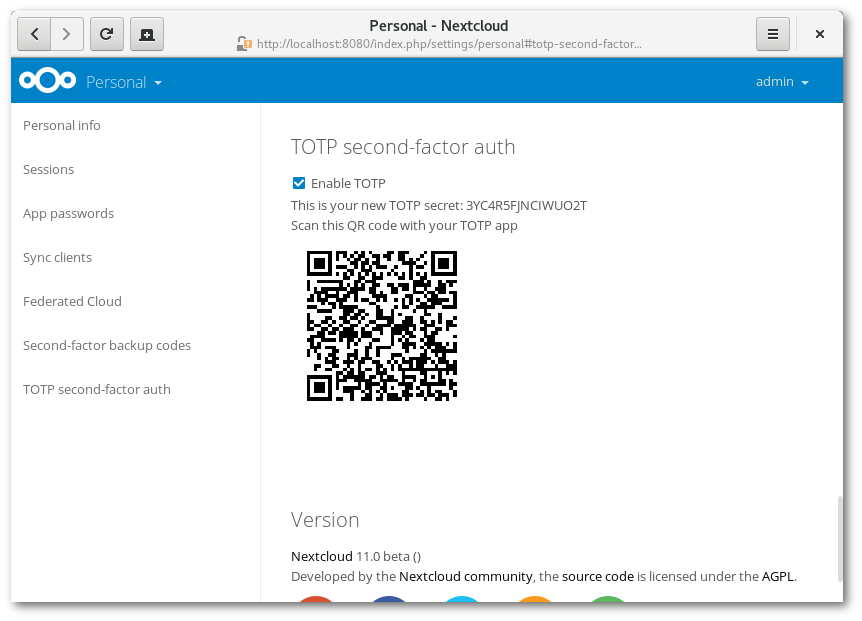
Admin configuration
Administrators can harden TOTP settings via occ. Changes only affect newly enrolled secrets; existing enrollments continue to work with the algorithm they were created with.
Hash algorithm
The default algorithm is SHA1 as required by RFC 6238. Stricter environments may prefer SHA256 or SHA512, provided all users' authenticator apps support the chosen algorithm.
| Value | Algorithm |
|---|---|
sha1 |
SHA1 (default) |
sha256 |
SHA256 |
sha512 |
SHA512 |
occ config:app:set twofactor_totp --type=string algorithm --value=sha256
Secret length
The generated TOTP secret defaults to 32 Base32 characters (160 bits), which meets the recommendation in RFC 4226. Administrators can increase this for higher entropy requirements.
| Characters | Bits | |
|---|---|---|
| Minimum | 26 | 130 |
| Default | 32 | 160 |
| Maximum | 128 | 640 |
occ config:app:set twofactor_totp --type=integer secret_length --value=64
Login with external apps
Once you enable OTP with Two Factor Totp, your applications (for example your Android app or your GNOME app) will need to login using device passwords. To manage it, know more here
Development setup
composer inpm cinpm run buildornpm run devmore info
관련 프로젝트 살펴보기
trimstray/the-book-of-secret-knowledge
영감을 주는 목록, 매뉴얼, 치트시트, 블로그, 팁, 원라이너, CLI/웹 도구 등을 모은 컬렉션.
258,353 스타Hack-with-Github/Awesome-Hacking
해커, 펜테스터, 보안 연구자를 위한 다양한 Awesome 목록 모음.
125,477 스타swisskyrepo/PayloadsAllTheThings
웹 애플리케이션 보안과 모의 침투 테스트/CTF에 유용한 페이로드 및 우회 방법 목록.
82,667 스타caddyserver/caddy
빠르고 확장 가능한 멀티플랫폼 HTTP/1-2-3 웹 서버이며, 자동 HTTPS를 지원합니다
79,026 스타