
netbirdio/netbird
netbirdio/netbird has 30,714 GitHub stars and 1,829 forks. GitHot measured +27 stars in 24 hours, +343 in 7 days, and +572 in 15 days. Last checked 2026-11-06 00:48 UTC. Last push 2026-11-01.
NetBird는 신원 기반의 단일 제로 트러스트 플랫폼으로 모든 네트워크의 사람, 머신, AI 에이전트를 안전하게 연결합니다. 피어 투 피어 WireGuard®를 기반으로 합니다.
What you can do
- ✓ Kernel WireGuard - ✓ Admin Web UI - ✓ SSO & MFA support - ✓ Public API - ✓ Linux
- ✓ Peer-to-peer connections - ✓ Auto peer discovery and configuration - ✓ Access control: groups & rules - ✓ Setup keys for bulk provisioning - ✓ macOS
- ✓ Connection relay fallback - ✓ IdP integrations - ✓ Activity logging - ✓ Self-hosting quickstart script - ✓ Windows
- ✓ Routes to external networks - ✓ Private DNS - ✓ Traffic events - ✓ IdP groups sync with JWT - ✓ Android
측정된 스타 증가
- in 24h
- +27
- in 7 days
- +343
- in 15 days
- +572
- in 1 month
- 업데이트 지연
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
README.md
Original


Start using NetBird at netbird.io
See Documentation
Join our Slack channel or our Community forum
🚀 We are hiring! Join us at https://netbird.io/careers
🤖 NetBird Agent Network (Beta)
Identity-aware access control for AI agents — keyless access to LLM APIs and private resources over the encrypted NetBird tunnel. See
agent-network/or read the docs at netbird.ai.
NetBird combines a configuration-free peer-to-peer private network and a centralized access control system in a single platform, making it easy to create secure private networks for your organization or home.
Connect. NetBird creates a WireGuard-based overlay network that automatically connects your machines over an encrypted tunnel, leaving behind the hassle of opening ports, complex firewall rules, VPN gateways, and so forth.
Secure. NetBird enables secure remote access by applying granular access policies while allowing you to manage them intuitively from a single place. Works universally on any infrastructure.
https://github.com/user-attachments/assets/10cec749-bb56-4ab3-97af-4e38850108d2
Self-host NetBird (video)
Key features
Quickstart with NetBird Cloud
- Download and install NetBird at https://app.netbird.io/install.
- Follow the steps to sign up with Google, Microsoft, GitHub or your email address.
- Check the NetBird admin UI.
Quickstart with self-hosted NetBird
This is the quickest way to try self-hosted NetBird. It should take around 5 minutes to get started if you already have a public domain and a VM. Follow the Advanced guide with a custom identity provider for installations with different IdPs.
Infrastructure requirements:
- A Linux VM with at least 1 CPU and 2 GB of memory.
- The VM should be publicly accessible on TCP ports 80 and 443 and UDP port 3478.
- A public domain name pointing to the VM.
Software requirements:
- Docker with the Compose plugin (Compose v2 or higher). See the Docker installation guide.
Steps
- Download and run the installation script:
export NETBIRD_DOMAIN=netbird.example.com; curl -fsSL https://github.com/netbirdio/netbird/releases/latest/download/getting-started.sh | bash
A bit on NetBird internals
- Every machine in the network runs the NetBird agent, which manages WireGuard.
- Every agent connects to the Management Service, which holds network state, manages peer IPs, and distributes updates to agents.
- Agents use ICE (via pion/ice) to discover connection candidates for peer-to-peer connections.
- Candidates are discovered with the help of STUN servers.
- Agents negotiate a connection through the Signal Service, exchanging end-to-end encrypted messages with candidates.
- When NAT traversal fails (e.g. mobile carrier-grade NAT) and a direct p2p connection isn't possible, the system falls back to a Relay Service and a secure WireGuard tunnel is established through it.
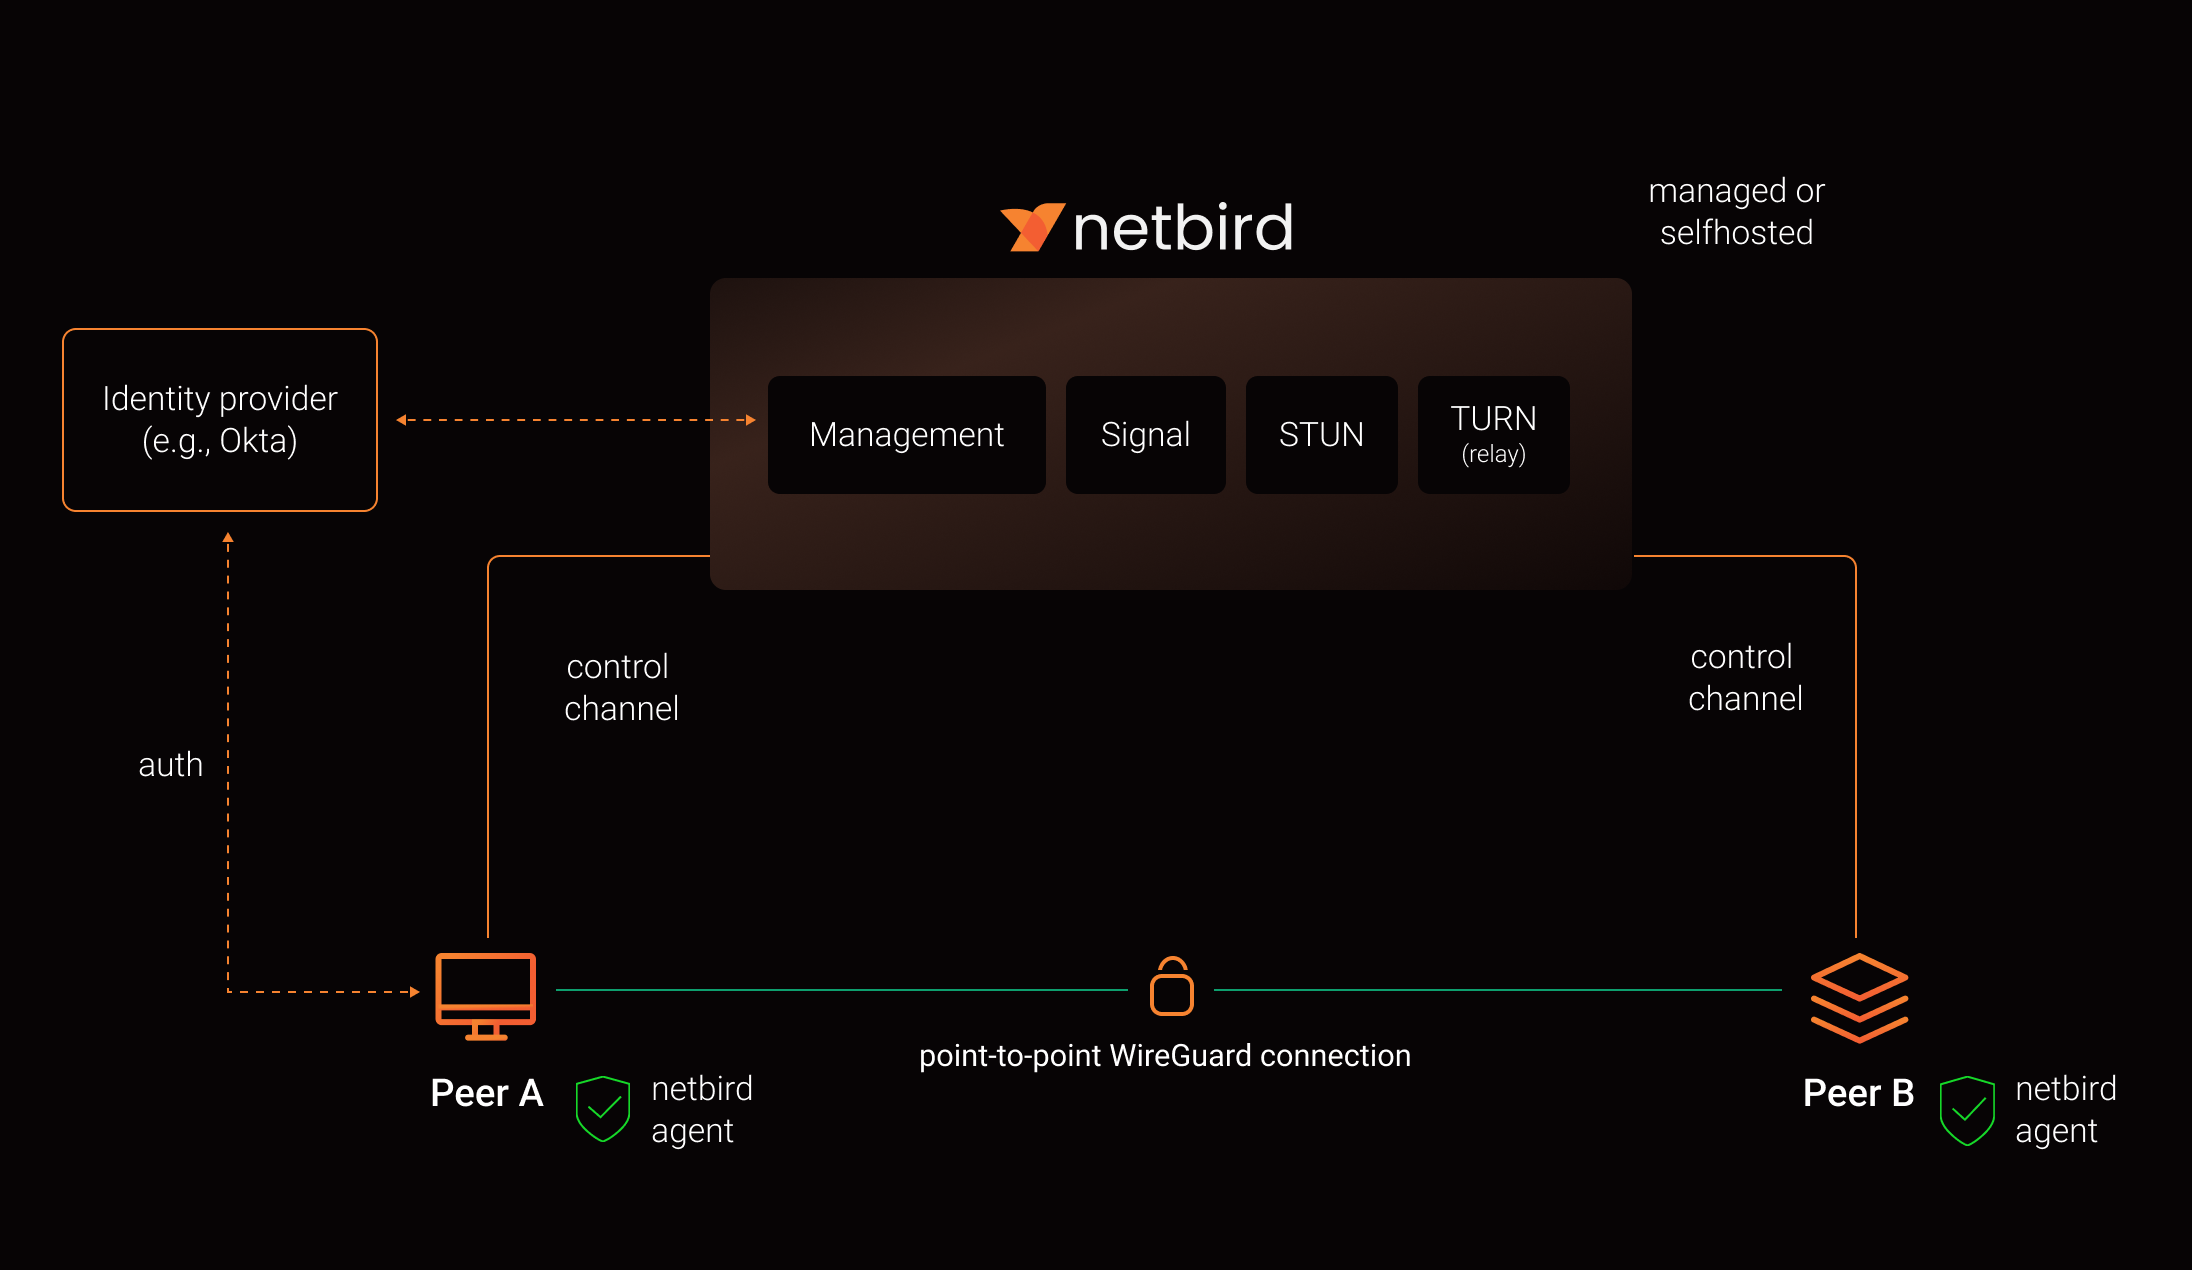
See a complete architecture overview for details.
Reporting bugs and requesting features
NetBird uses a discussion-first workflow. Bug reports and feature requests start in Discussions, not as issues.
| What you want to do | Where to go |
|---|---|
| Report a bug, regression, or unexpected behavior | Issue Triage |
| Request a feature or share an idea | Ideas & Feature Requests |
| Ask about setup, configuration, or self-hosting | Q&A / Support |
| Report a security vulnerability | Security policy, never a public thread |
Our team and maintainers triage discussions, ask follow-up questions, check for duplicates, and reproduce bugs. Validated reports are promoted to issues. This keeps the issue tracker a clear answer to one question: what is the team working on.
Please search existing discussions and issues first, including closed ones. If something similar already exists, upvote it and add your details there instead of opening a duplicate.
For bug reports, include your NetBird version, operating system, deployment type (Cloud, self-hosted, Kubernetes, or Docker), reproduction steps, expected and actual behavior, and a debug bundle where relevant:
netbird version
netbird status -d -A
netbird debug for 1m -A -S -U
-U uploads the bundle and prints a file key you can paste instead of attaching the archive.
-A anonymizes the output, which matters on a public thread. It masks most identifying details
but is not full redaction, so read the bundle before posting it. Two levels are available:
| Level | How to select | What it masks |
|---|---|---|
default |
-A / --anonymize |
Public IP addresses, IPv6 ULA addresses, MAC addresses, and domains other than netbird.io, netbird.cloud, netbird.selfhosted, and netbird.stage. IPv4 private, CGNAT, and link-local ranges are kept |
strict |
--anonymize-level strict (implies -A) |
The above, plus IPv4 private, CGNAT, and link-local ranges, peer names in front of netbird.cloud, netbird.selfhosted, and netbird.stage, and WireGuard public keys. Labels under netbird.io are kept, since it only hosts infrastructure |
See collecting a debug bundle and the CLI reference for details.
See How to use Discussions, Issues, and Pull Requests for the full workflow, or SUPPORT.md for a shorter version.
Contributing
Contributions are welcome. Read CONTRIBUTING.md first. NetBird works ticket first, anything that changes behavior needs an issue the team has agreed on before you open a pull request.
Community projects
- NetBird installer script
- netbird-tui - terminal UI for managing NetBird peers, routes, and settings
- caddy-netbird - Caddy plugin that embeds a NetBird client for proxying HTTP and TCP/UDP traffic through NetBird networks
Note: The main branch may be in an unstable or even broken state during development.
For stable versions, see releases.
Support acknowledgement
In November 2022, NetBird joined the StartUpSecure program sponsored by the Federal Ministry of Education and Research of the Federal Republic of Germany. Together with the CISPA Helmholtz Center for Information Security, NetBird brings security best practices and simplicity to private networking.

Acknowledgements
We build on open source technologies like WireGuard®, Pion ICE, and Rosenpass. We greatly appreciate the work these projects are doing, and we'd love it if you could support them too (e.g., by starring or contributing).
Legal
This repository is licensed under the BSD-3-Clause license, which applies to all parts of the repository except for the directories management/, signal/ and relay/. Those directories are licensed under the GNU Affero General Public License version 3.0 (AGPLv3). See the respective LICENSE files inside each directory.
WireGuard and the WireGuard logo are registered trademarks of Jason A. Donenfeld.
관련 프로젝트 살펴보기
affaan-m/ECC
에이전트 실행·제어 프레임워크를 위한 성능 최적화 시스템. Claude Code, Codex, Opencode, Cursor 등을 위한 스킬, 본능, 메모리, 보안, 연구 우선 개발을 제공합니다.
298,330 스타NousResearch/hermes-agent
당신과 함께 성장하는 에이전트
261,097 스타multica-ai/andrej-karpathy-skills
Andrej Karpathy가 관찰한 LLM 코딩의 함정을 바탕으로 Claude Code의 동작을 개선하는 단일 CLAUDE.md 파일입니다.
230,134 스타firecrawl/firecrawl
웹과 그 너머의 데이터로 AI 에이전트를 강화합니다. 초지능을 위한 라이브러리를 구축하고 있습니다. 🔥
199,027 스타