
chaitin/SafeLine
chaitin/SafeLine has 23,239 GitHub stars and 1,605 forks. GitHot measured +17 stars in 24 hours and +76 in 7 days. Last checked 2026-11-10 04:43 UTC. Last push 2026-10-22.
SafeLine은 웹 앱을 공격과 취약점 악용으로부터 보호하는 자체 호스팅형 WAF(Web Application Firewall)/리버스 프록시입니다.
What you can do
- It defenses for all of web attacks, such as SQL injection, XSS, code injection, os command injection, CRLF injection, XXE, SSRF, path traversal and so on.
- Defend your web apps against DoS attacks, bruteforce attempts, traffic surges, and other types of abuse by throttling traffic that exceeds defined limits.
- Anti-Bot challenges to protect your website from bot attacks, human users will be allowed, crawlers and bots will be blocked.
- When authentication challenge turned on, visitors need to enter the password, otherwise they will be blocked.
측정된 스타 증가
- in 24h
- +17
- in 7 days
- +76
- in 15 days
- 기록 수집 중
- in 1 month
- 기록 수집 중
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
README.md
Original

SafeLine - Make your web apps secure
🏠 Website | 📖 Docs | 🔍 Live Demo | 🙋♂️ Discord | 中文版
🏆 Achievements
👋 INTRODUCTION
SafeLine is a self-hosted WAF(Web Application Firewall) to protect your web apps from attacks and exploits.
A web application firewall helps protect web apps by filtering and monitoring HTTP traffic between a web application and the Internet. It typically protects web apps from attacks such as SQL injection, XSS, code injection, os command injection, CRLF injection, ldap injection, xpath injection, RCE, XXE, SSRF, path traversal, backdoor, bruteforce, http-flood, bot abused, among others.
💡 How It Works

By deploying a WAF in front of a web application, a shield is placed between the web application and the Internet. While a proxy server protects a client machine’s identity by using an intermediary, a WAF is a type of reverse-proxy, protecting the server from exposure by having clients pass through the WAF before reaching the server.
A WAF protects your web apps by filtering, monitoring, and blocking any malicious HTTP/S traffic traveling to the web application, and prevents any unauthorized data from leaving the app. It does this by adhering to a set of policies that help determine what traffic is malicious and what traffic is safe. Just as a proxy server acts as an intermediary to protect the identity of a client, a WAF operates in similar fashion but acting as a reverse proxy intermediary that protects the web app server from a potentially malicious client.
its core capabilities include:
- Defenses for web attacks
- Proactive bot abused defense
- HTML & JS code encryption
- IP-based rate limiting
- Web Access Control List
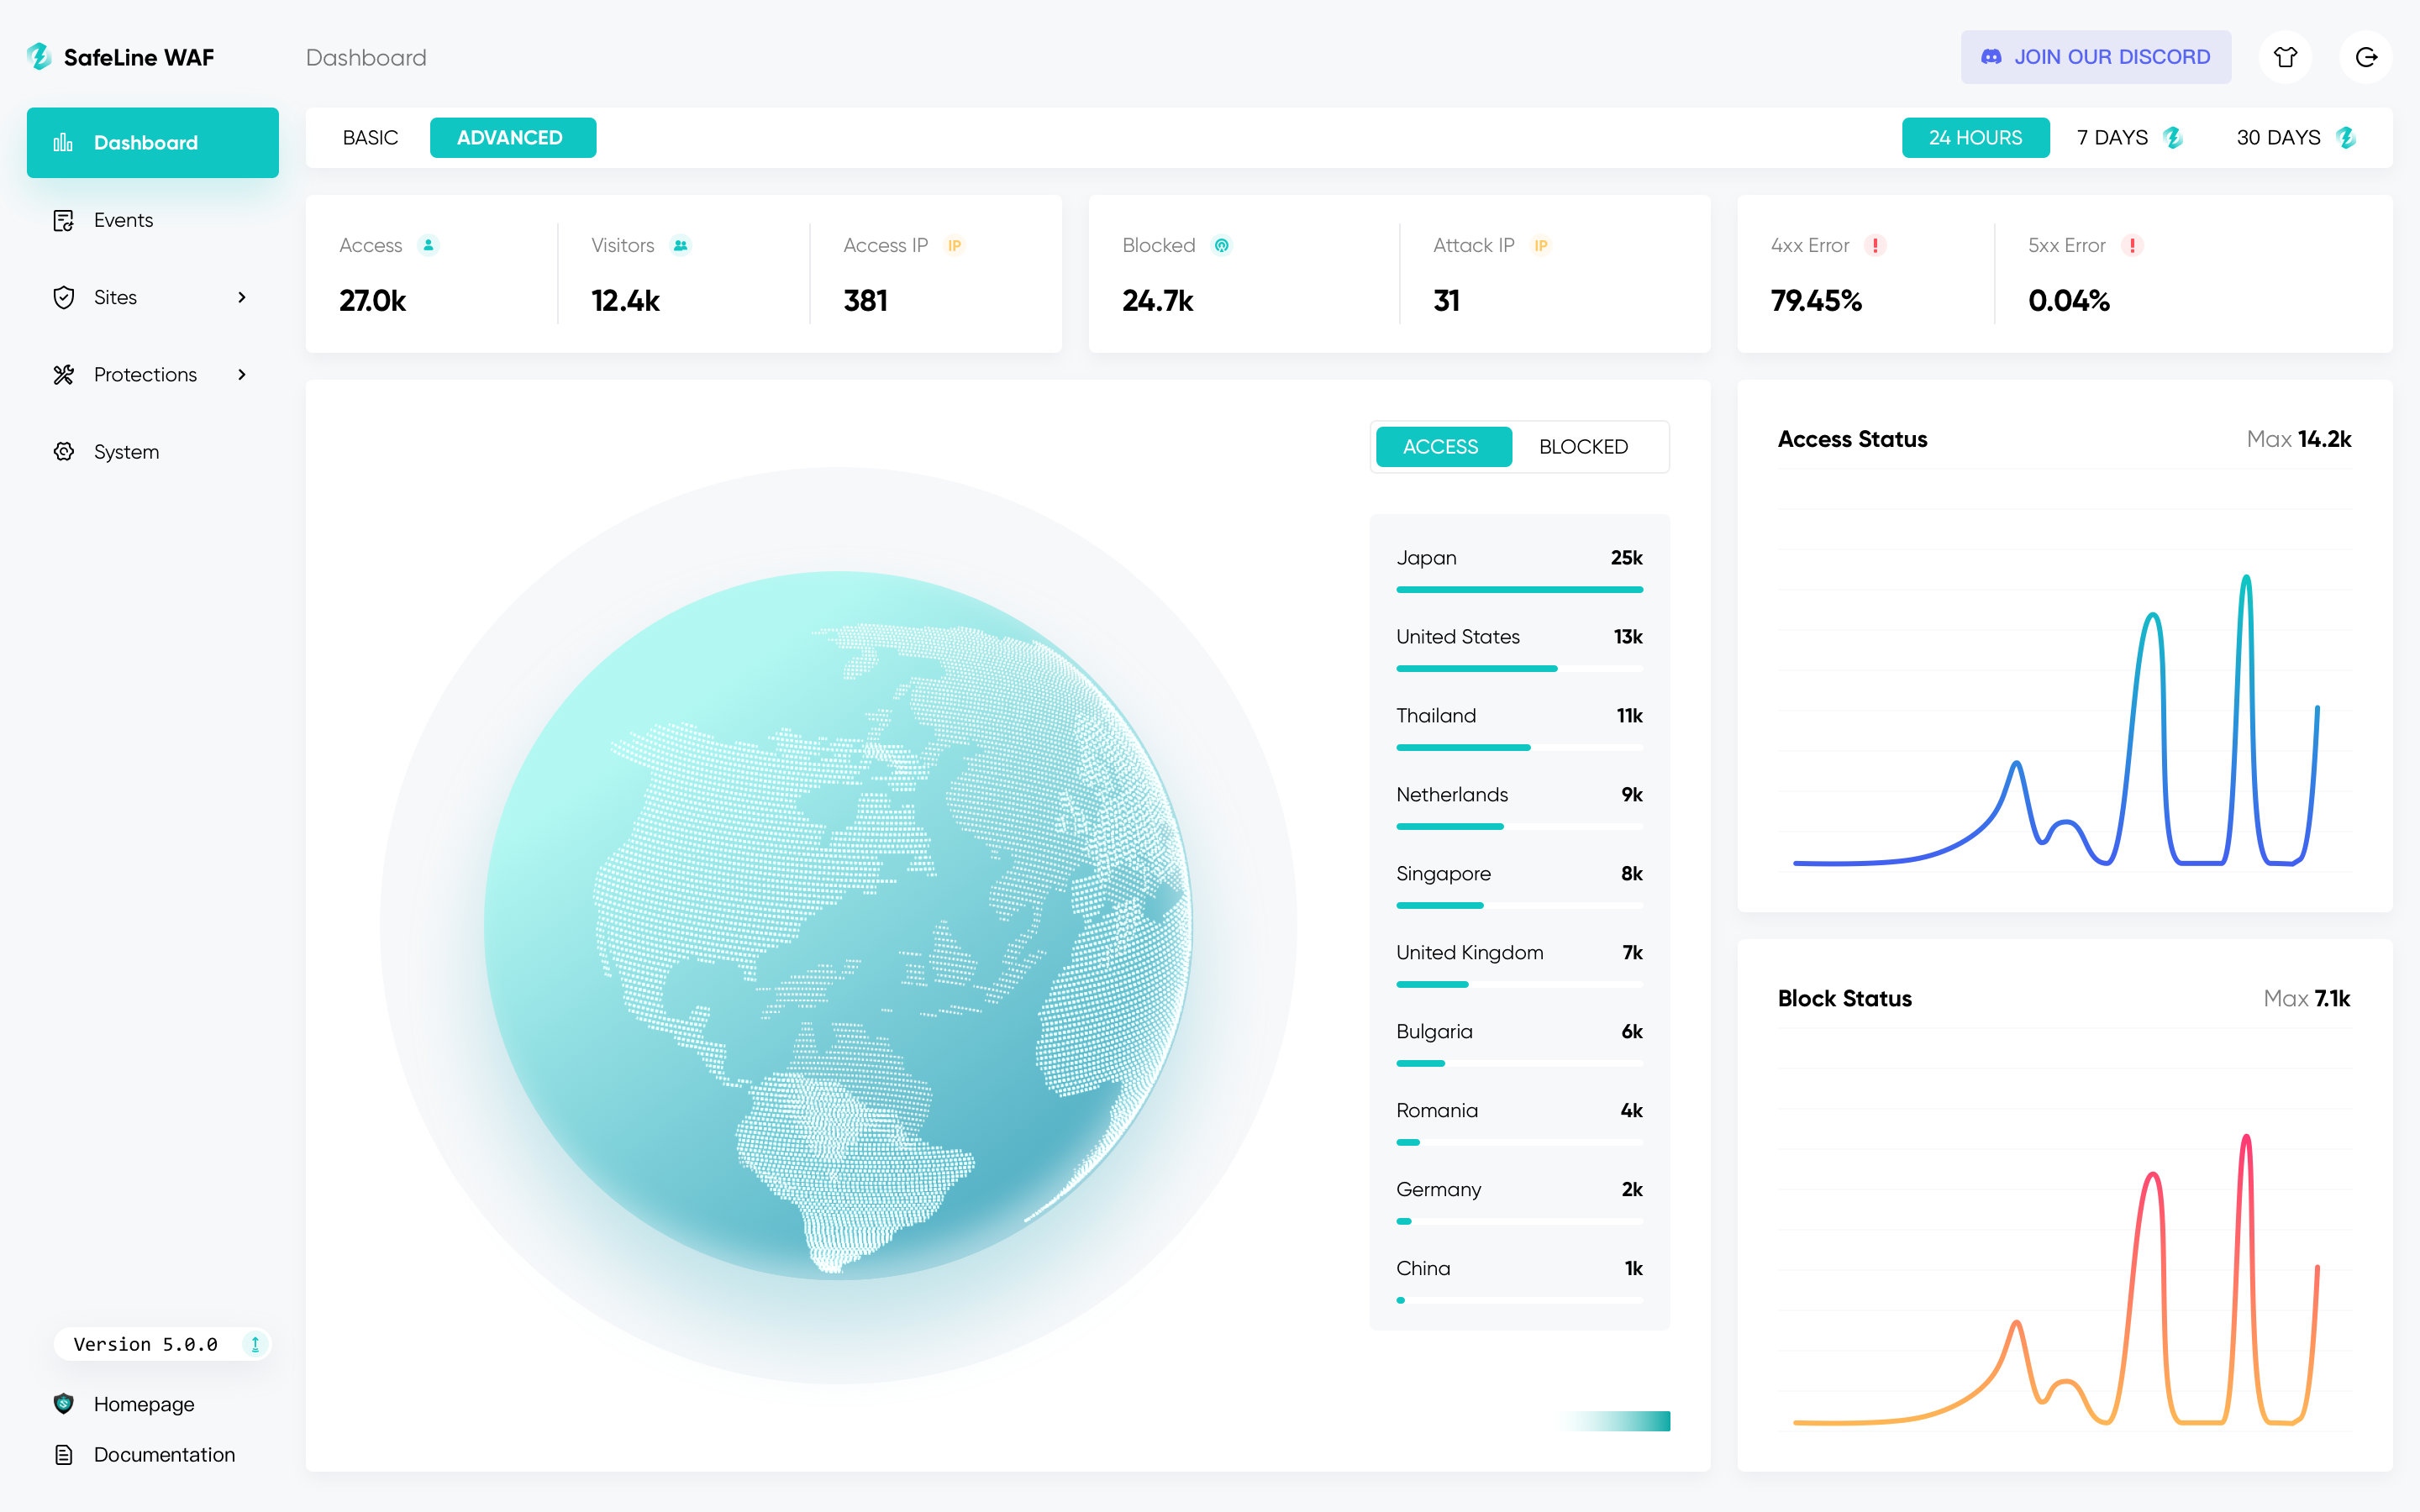
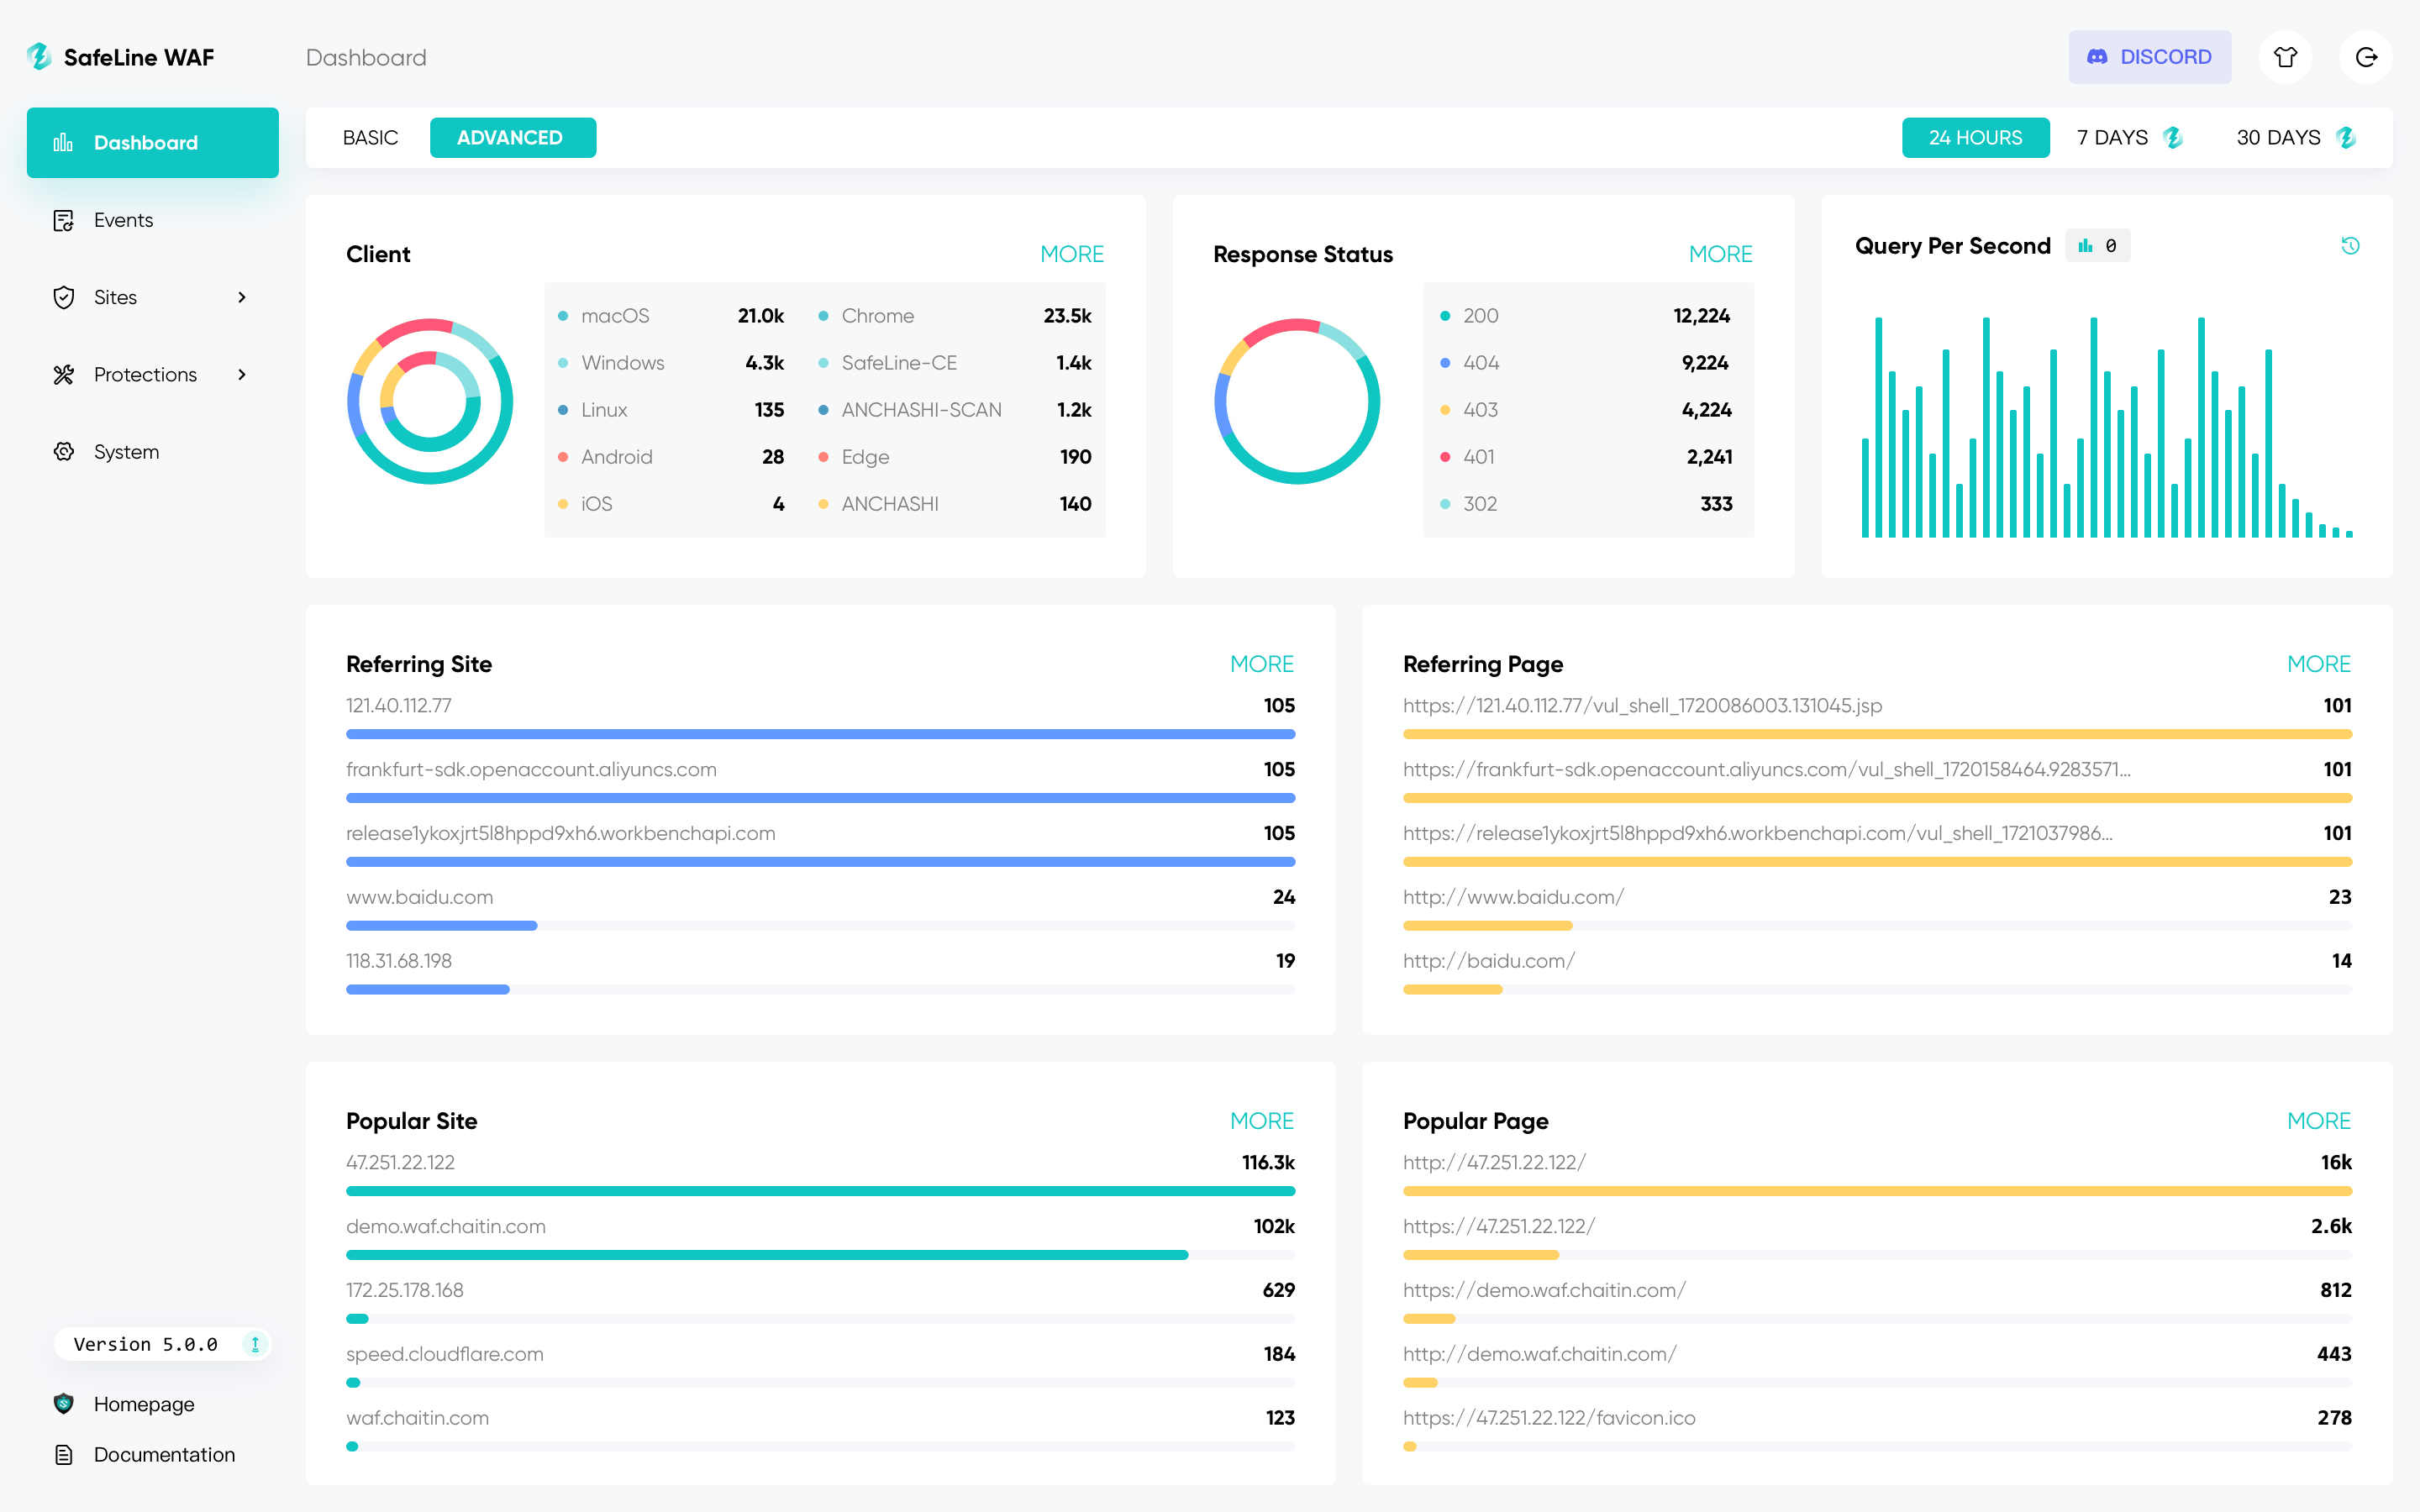
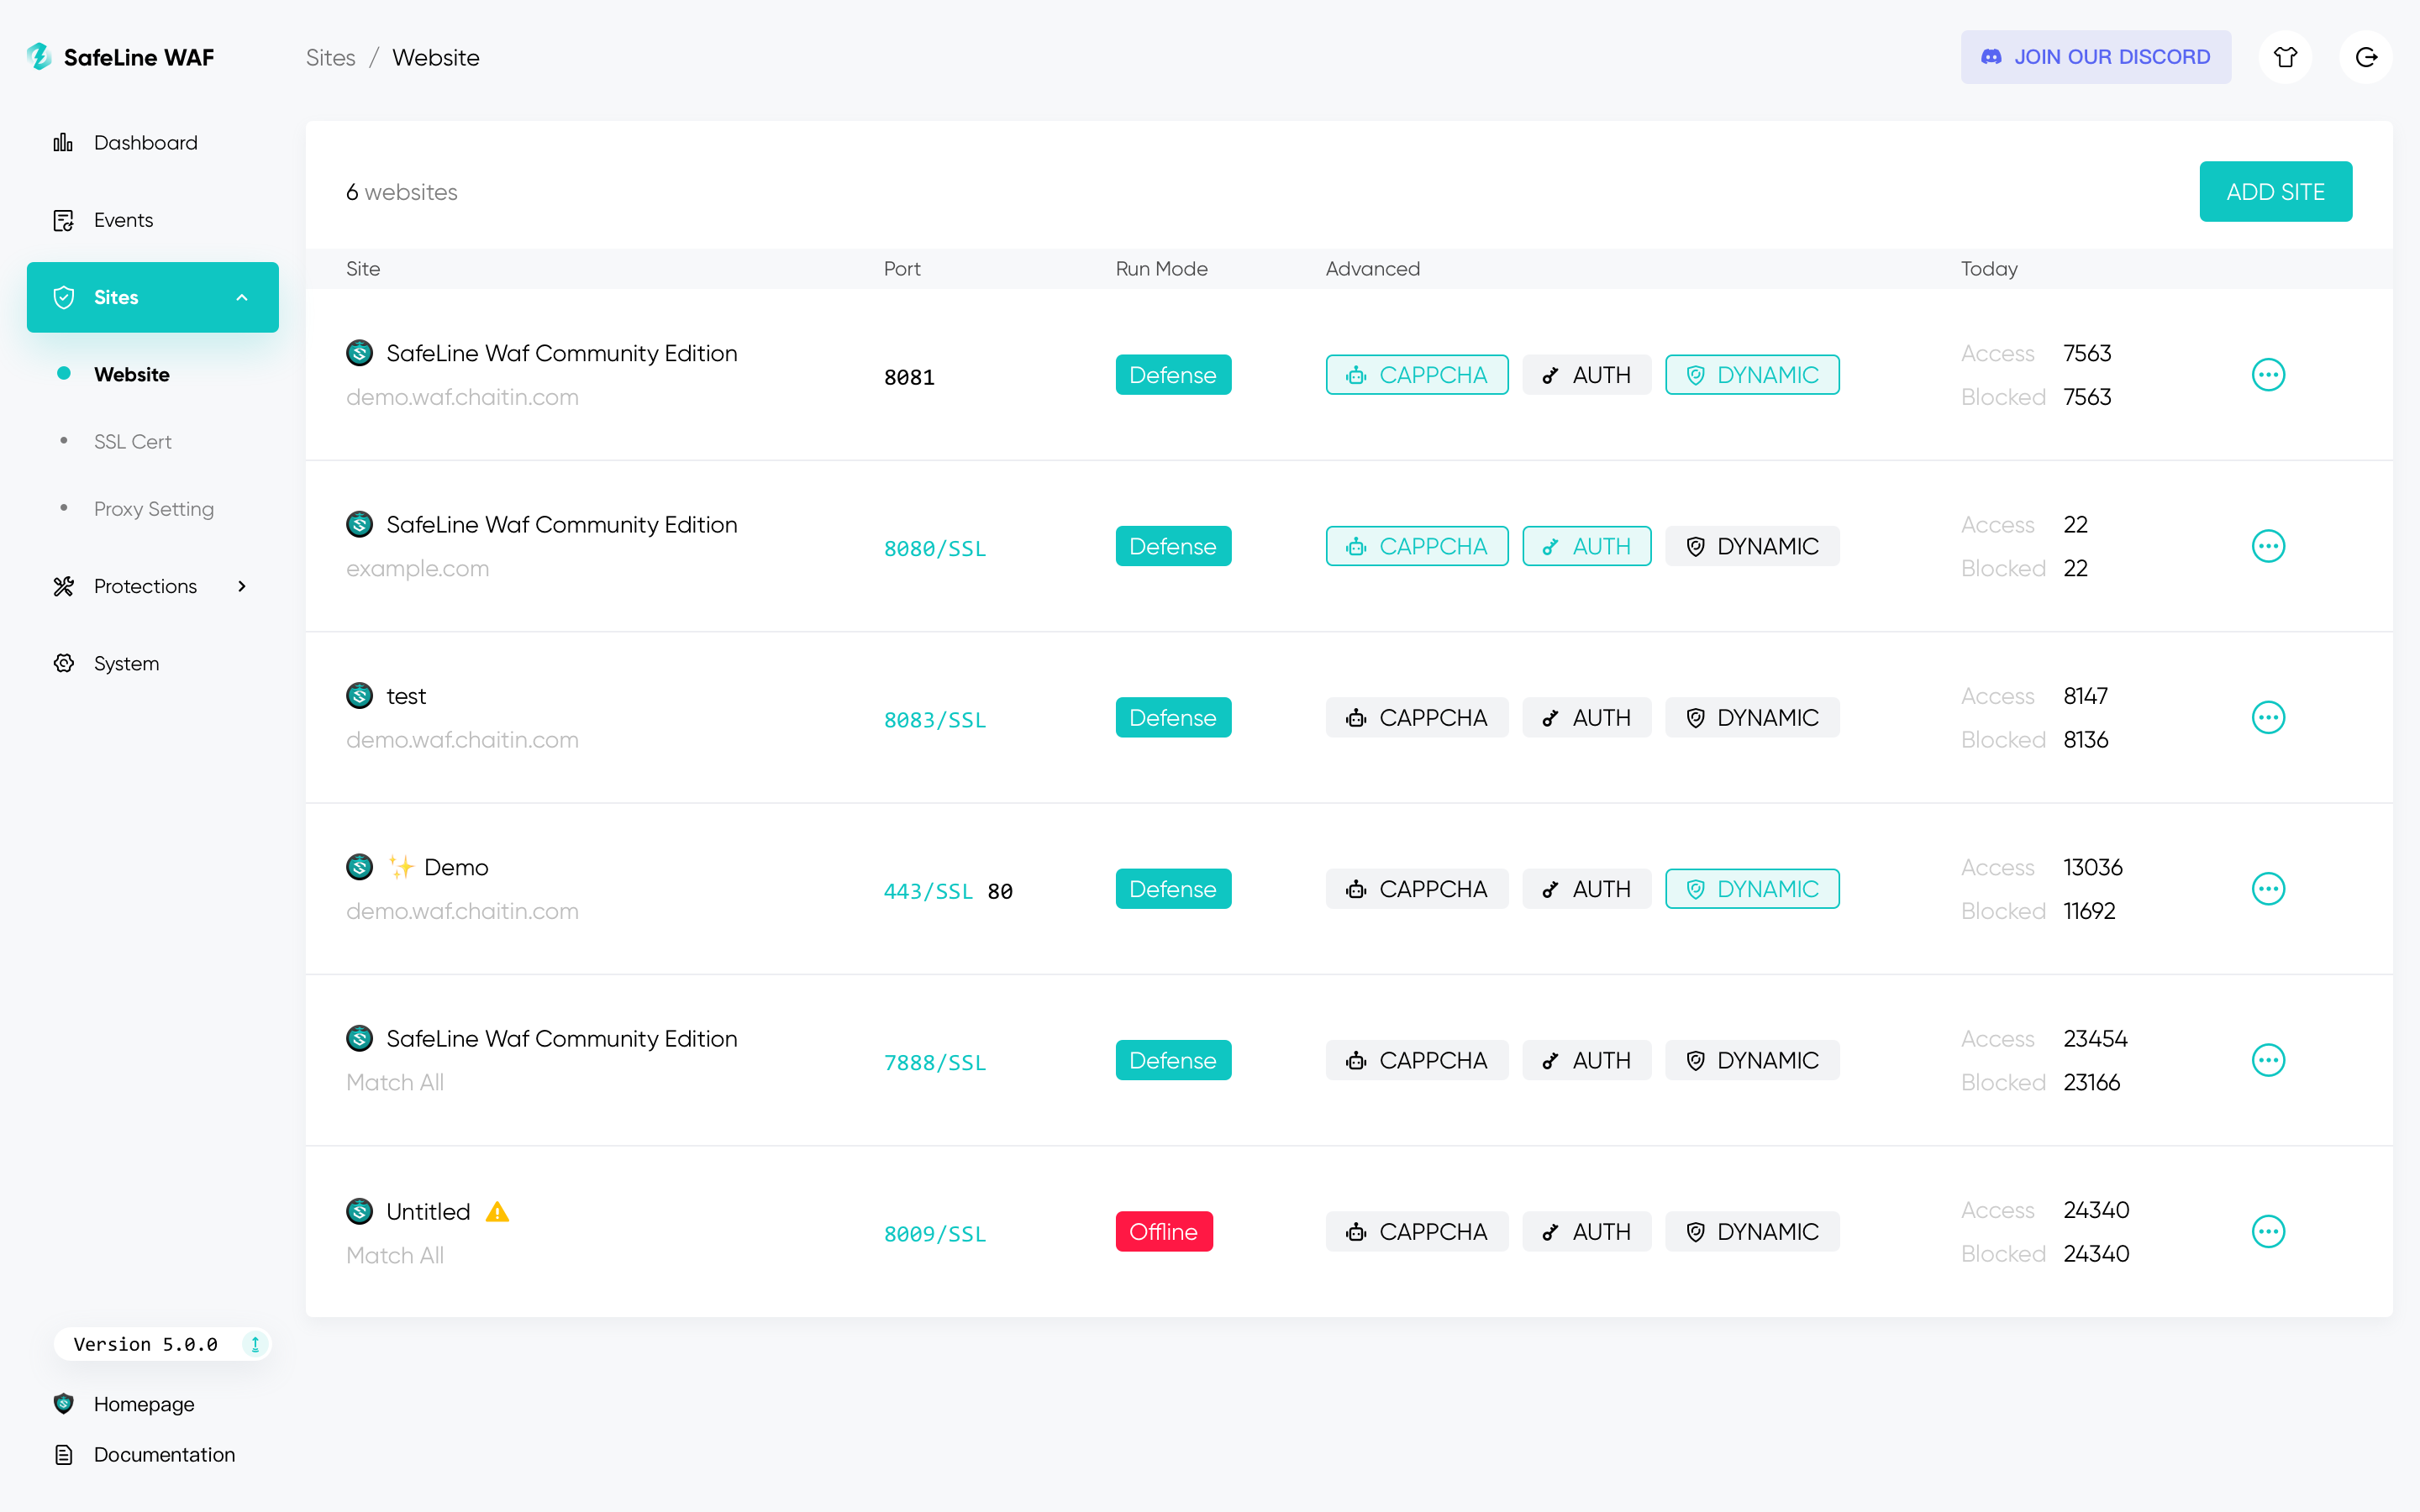
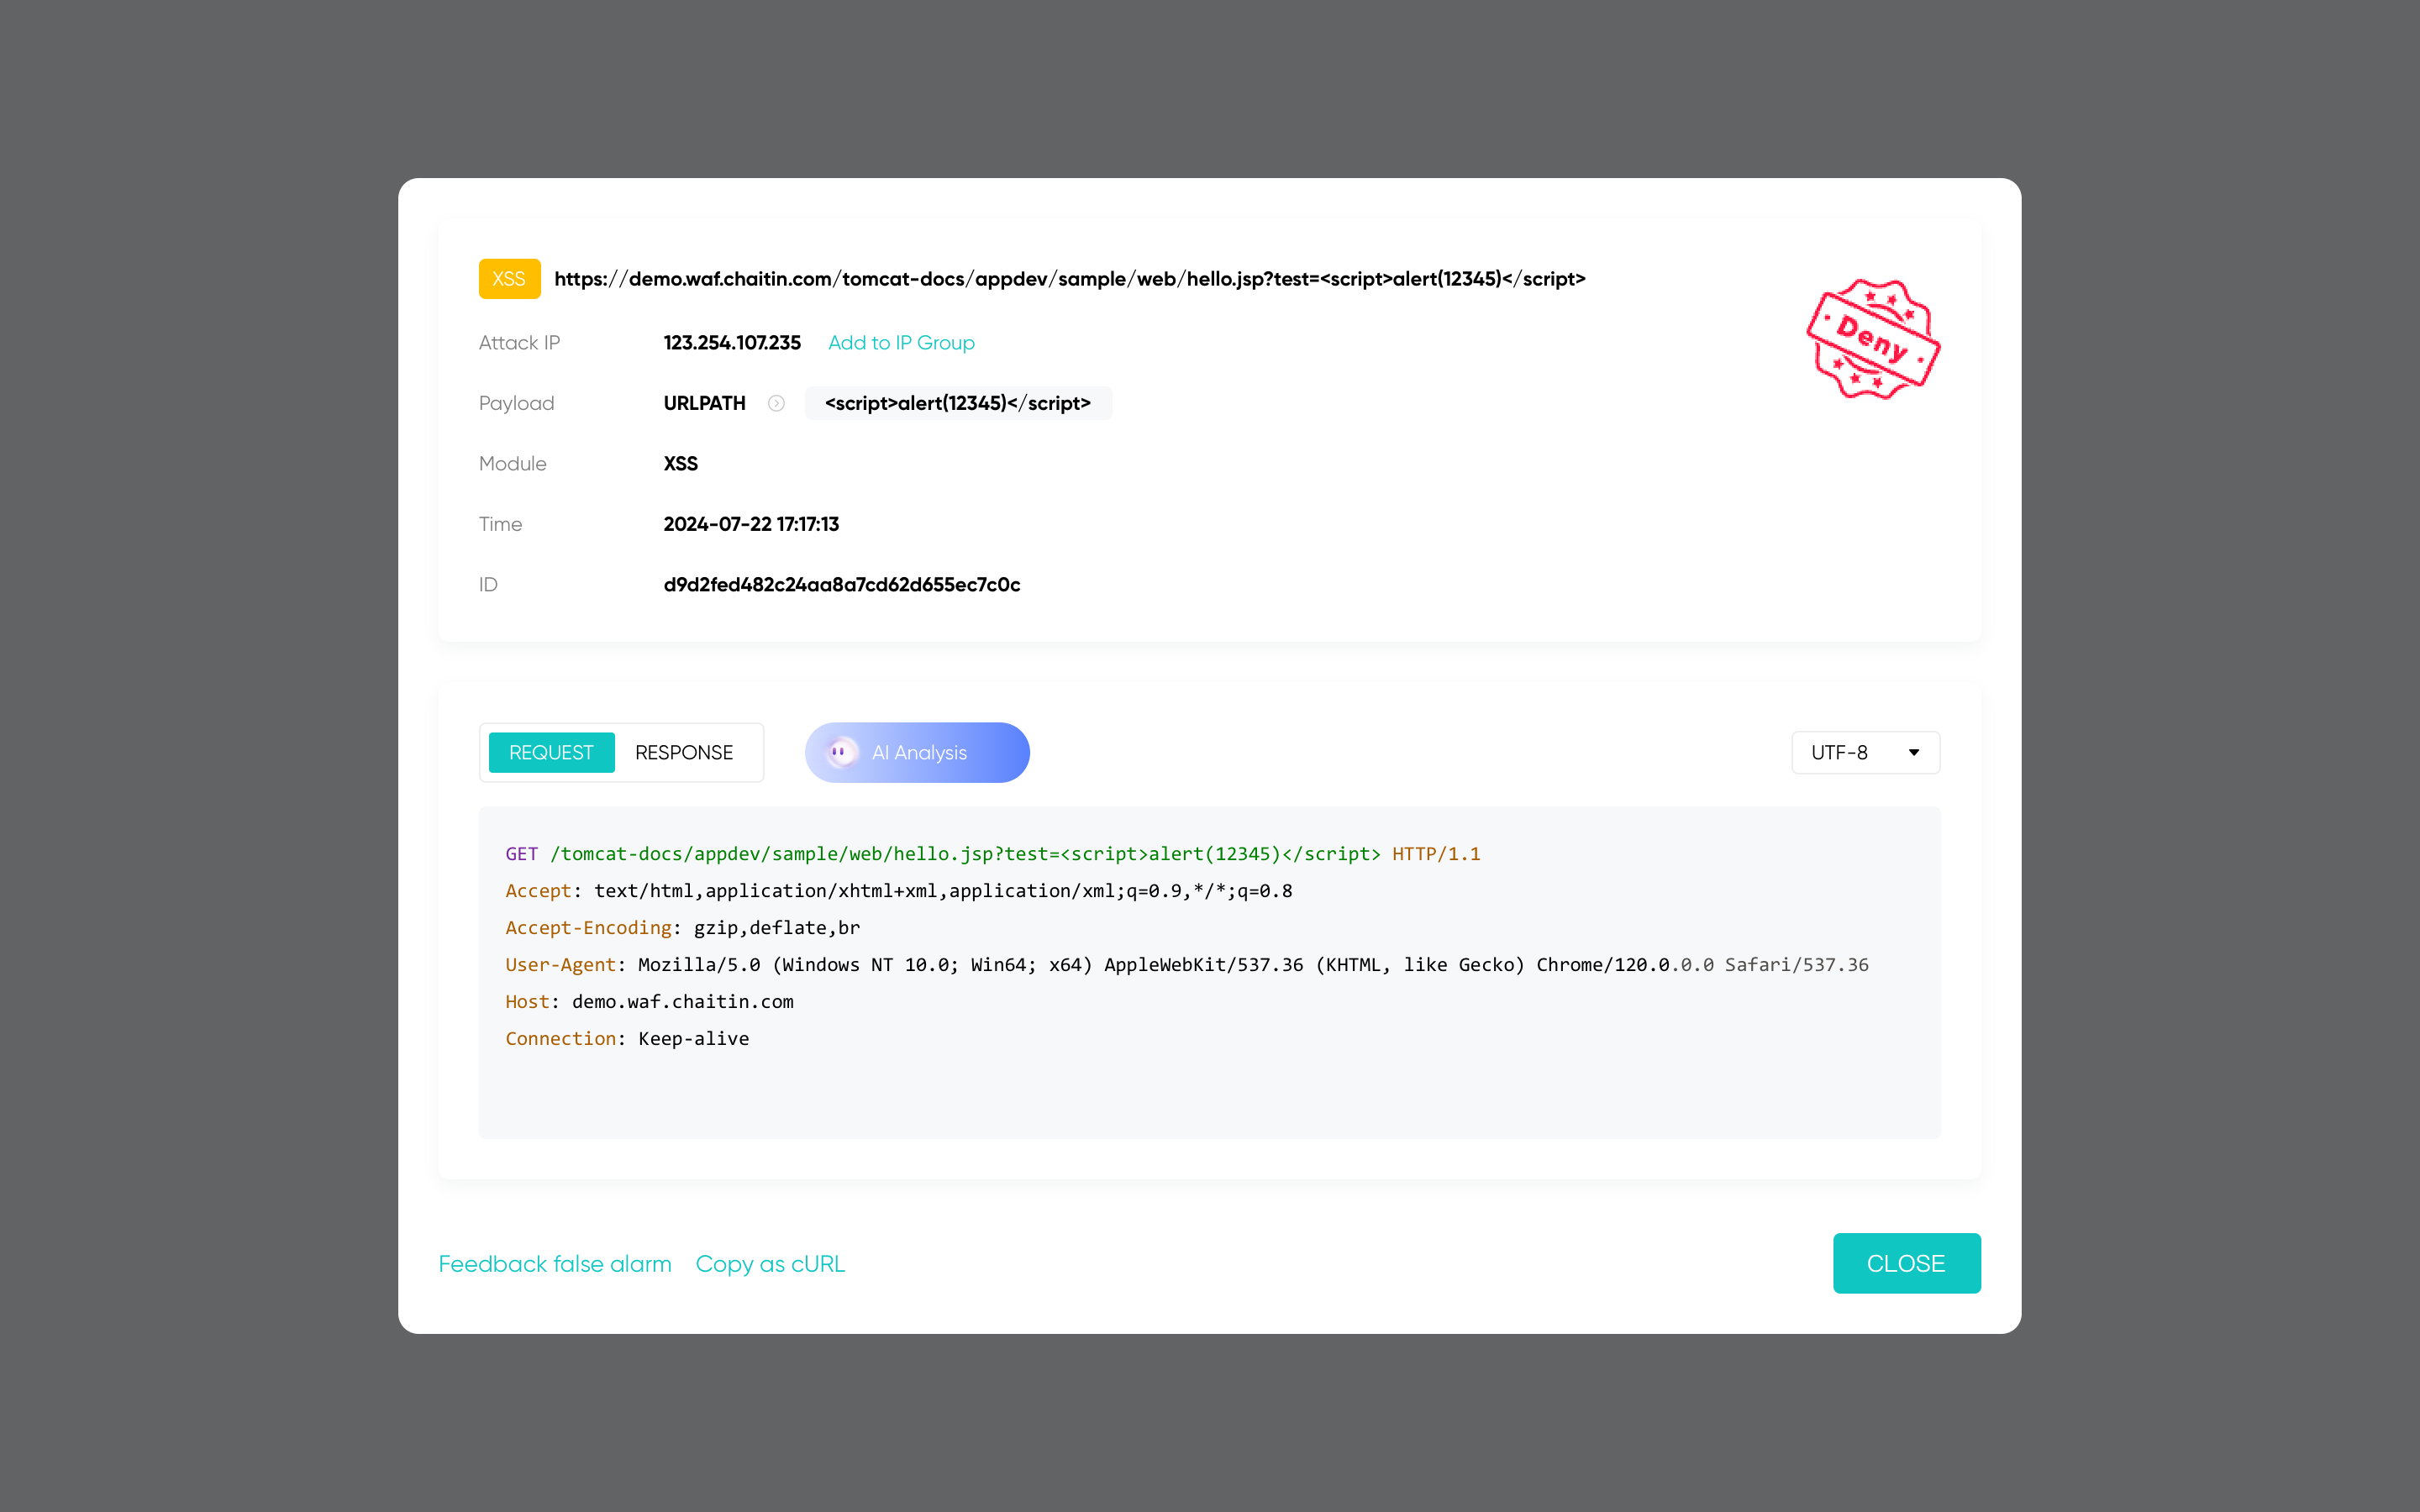
⚡️ Screenshots
 |
 |
|---|---|
 |
 |
Get Live Demo
🔥 FEATURES
List of the main features as follows:
Block Web Attacks- It defenses for all of web attacks, such as
SQL injection,XSS,code injection,os command injection,CRLF injection,XXE,SSRF,path traversaland so on.
- It defenses for all of web attacks, such as
Rate Limiting- Defend your web apps against
DoS attacks,bruteforce attempts,traffic surges, and other types of abuse by throttling traffic that exceeds defined limits.
- Defend your web apps against
Anti-Bot Challenge- Anti-Bot challenges to protect your website from
bot attacks, human users will be allowed, crawlers and bots will be blocked.
- Anti-Bot challenges to protect your website from
Authentication Challenge- When authentication challenge turned on, visitors need to enter the password, otherwise they will be blocked.
Dynamic Protection- When dynamic protection turned on, html and js codes in your web server will be dynamically encrypted by each time you visit.
🧩 Showcases
| Legitimate User | Malicious User | |
|---|---|---|
Block Web Attacks |
 |
 |
Rate Limiting |
|
 |
Anti-Bot Challenge |
 |
 |
Auth Challenge |
 |
 |
HTML Dynamic Protection |
 |
 |
JS Dynamic Protection |
 |
 |
🚀 Quickstart
[!WARNING] 中国大陆用户安装国际版可能会导致无法连接云服务,请查看 中文版安装文档
📦 Installing
Information on how to install SafeLine can be found in the Install Guide
⚙️ Protecting Web Apps
to see Configuration
📋 More Information
Effect Evaluation
| Metric | ModSecurity, Level 1 | CloudFlare, Free | SafeLine, Balance | SafeLine, Strict |
|---|---|---|---|---|
| Total Samples | 33669 | 33669 | 33669 | 33669 |
| Detection | 69.74% | 10.70% | 71.65% | 76.17% |
| False Positive | 17.58% | 0.07% | 0.07% | 0.22% |
| Accuracy | 82.20% | 98.40% | 99.45% | 99.38% |
Is SafeLine Production-Ready?
Yes, SafeLine is production-ready.
- Over 700,000 installations worldwide
- Protecting over 2,000,000 Websites
- Handling over 50,000,000,000 HTTP Requests Daily
🌟 Community Recognition
- Rated 10.0/10 by HelloGitHub
- Listed in awesome-selfhosted
- Featured on Product Hunt
- Recognized by Cyber Press as the most popular open-source web firewall on GitHub
🔌 Ecosystem Integrations
- SafeLine MCP Server for AI-assisted management and control
- Ingress-NGINX plugin for protecting Kubernetes ingress traffic
- Kong Gateway plugin for protecting APIs and services
🙋♂️ Community
Join our Discord to get community support, the core team members are identified by the STAFF role in Discord.
- channel #feedback: for new features discussion.
- channel #FAQ: for FAQ.
- channel #general: for any other questions.
Several contact options exist for our community, the primary one being Discord. These are in addition to GitHub issues for creating a new issue.


💪 PRO Edition
SafeLine PRO is now available! Explore plans and pricing or start a 7-day trial.
📝 License
See LICENSE for details.
관련 프로젝트 살펴보기
trimstray/the-book-of-secret-knowledge
영감을 주는 목록, 매뉴얼, 치트시트, 블로그, 팁, 원라이너, CLI/웹 도구 등을 모은 컬렉션.
257,250 스타Hack-with-Github/Awesome-Hacking
해커, 펜테스터, 보안 연구자를 위한 다양한 Awesome 목록 모음.
125,103 스타swisskyrepo/PayloadsAllTheThings
웹 애플리케이션 보안과 모의 침투 테스트/CTF에 유용한 페이로드 및 우회 방법 목록.
82,542 스타caddyserver/caddy
빠르고 확장 가능한 멀티플랫폼 HTTP/1-2-3 웹 서버이며, 자동 HTTPS를 지원합니다
78,935 스타