
TW4RDYDEV/NEXUS
TW4RDYDEV/NEXUS has 35 GitHub stars and 0 forks. Star changes are not measured yet. Last checked 2026-11-14 12:29 UTC. Last push 2026-10-04.
측정된 스타 증가
- in 24h
- 기록 수집 중
- in 7 days
- 기록 수집 중
- in 15 days
- 기록 수집 중
- in 1 month
- 기록 수집 중
서로 겹치는 기간의 순증가량이며 일별 합계가 아닙니다. 측정값이 없으면 비워 둡니다. 스타는 관심도를 나타내며 품질을 보장하지 않습니다.
소개
Local-first offensive security engagement platform for mapping assets, credentials, sessions, pivots, findings, evidence, and attack paths.
보안README.md
Original
NEXUS
Offensive Security Engagement Platform
Map assets. Track access. Understand the path.




by TWARDY.exe / TW4RDYDEV
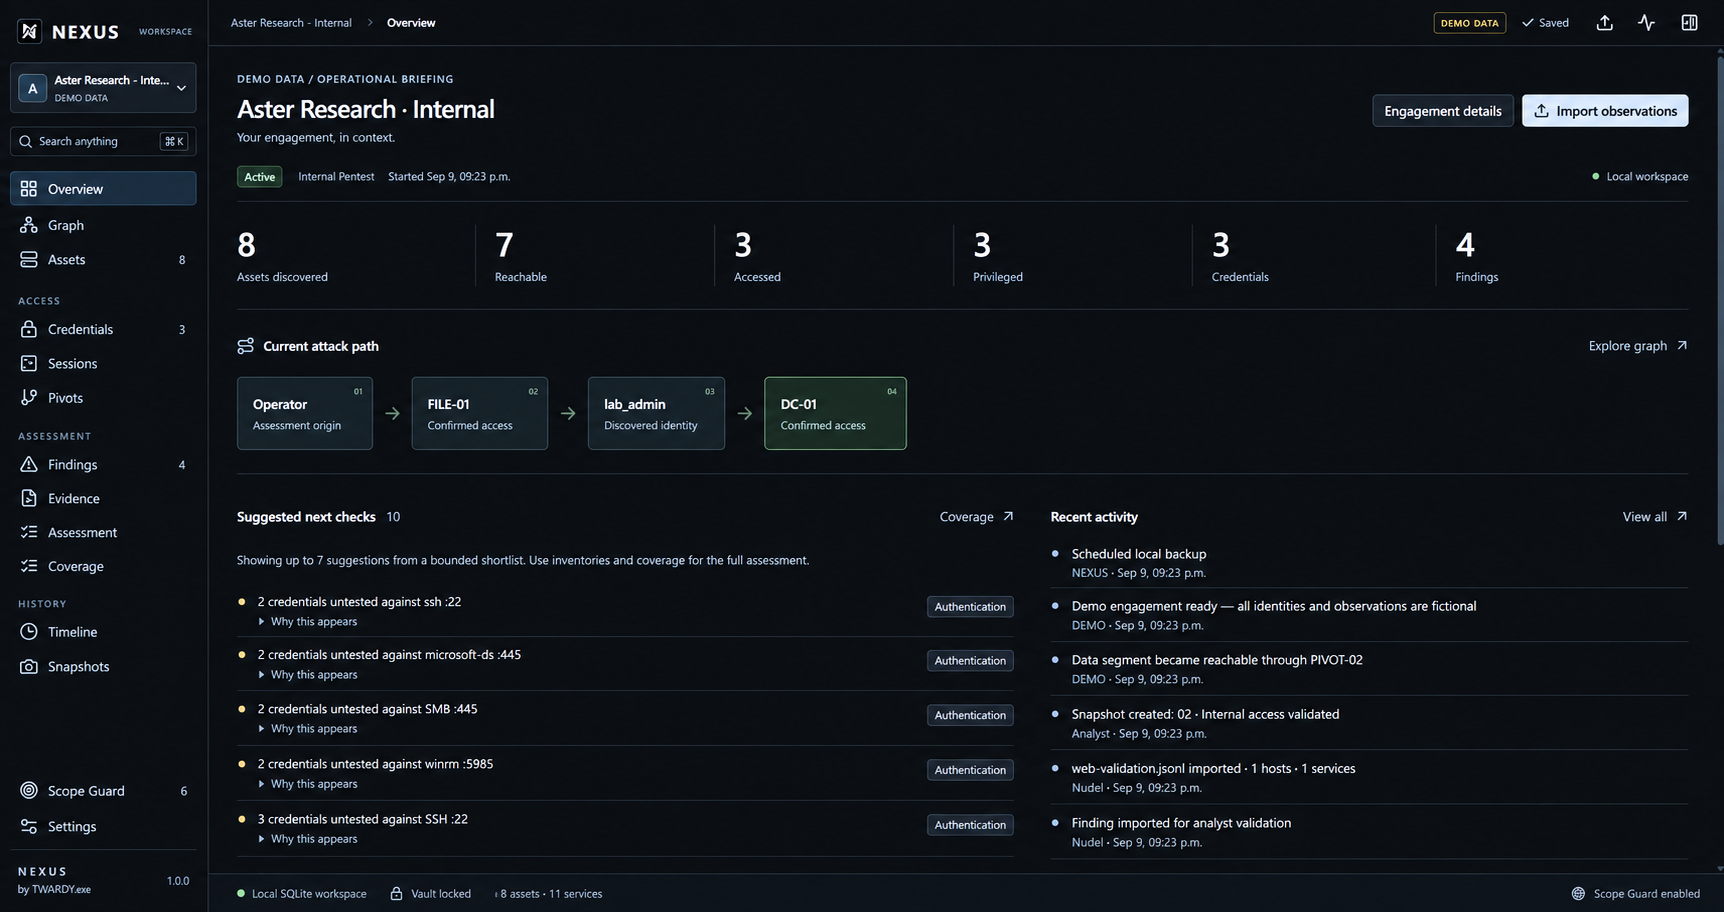
NEXUS is a local-first offensive-security workspace that turns scattered assessment data into one connected operational view. It correlates assets, services, credentials, sessions, pivots, findings, evidence, coverage, and historical changes so an operator can understand not only what exists, but what is reachable, what access is confirmed, what has been tested, and what still needs attention.
NEXUS does not try to replace Nmap, Nuclei, httpx, NetExec, Burp, or other established tools. It acts as the engagement layer above them.
TOOLS → NORMALIZED STATE → RELATIONSHIPS → COVERAGE → ATTACK PATH → EVIDENCE
Preview
Operational overview
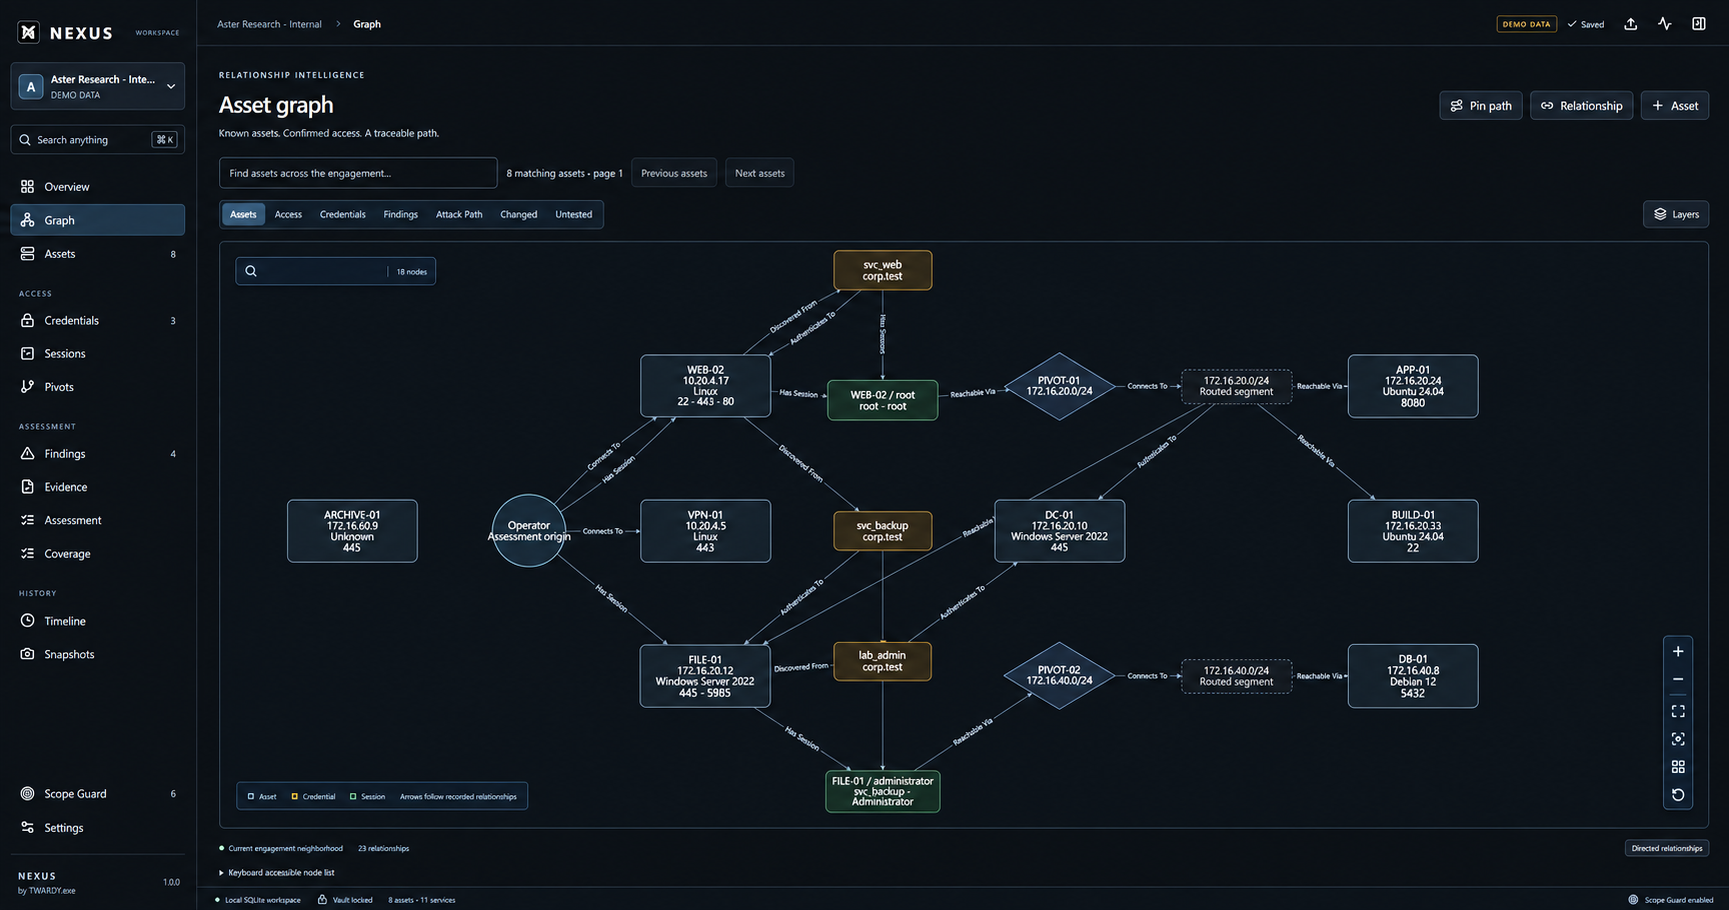
Asset graph
More screenshots
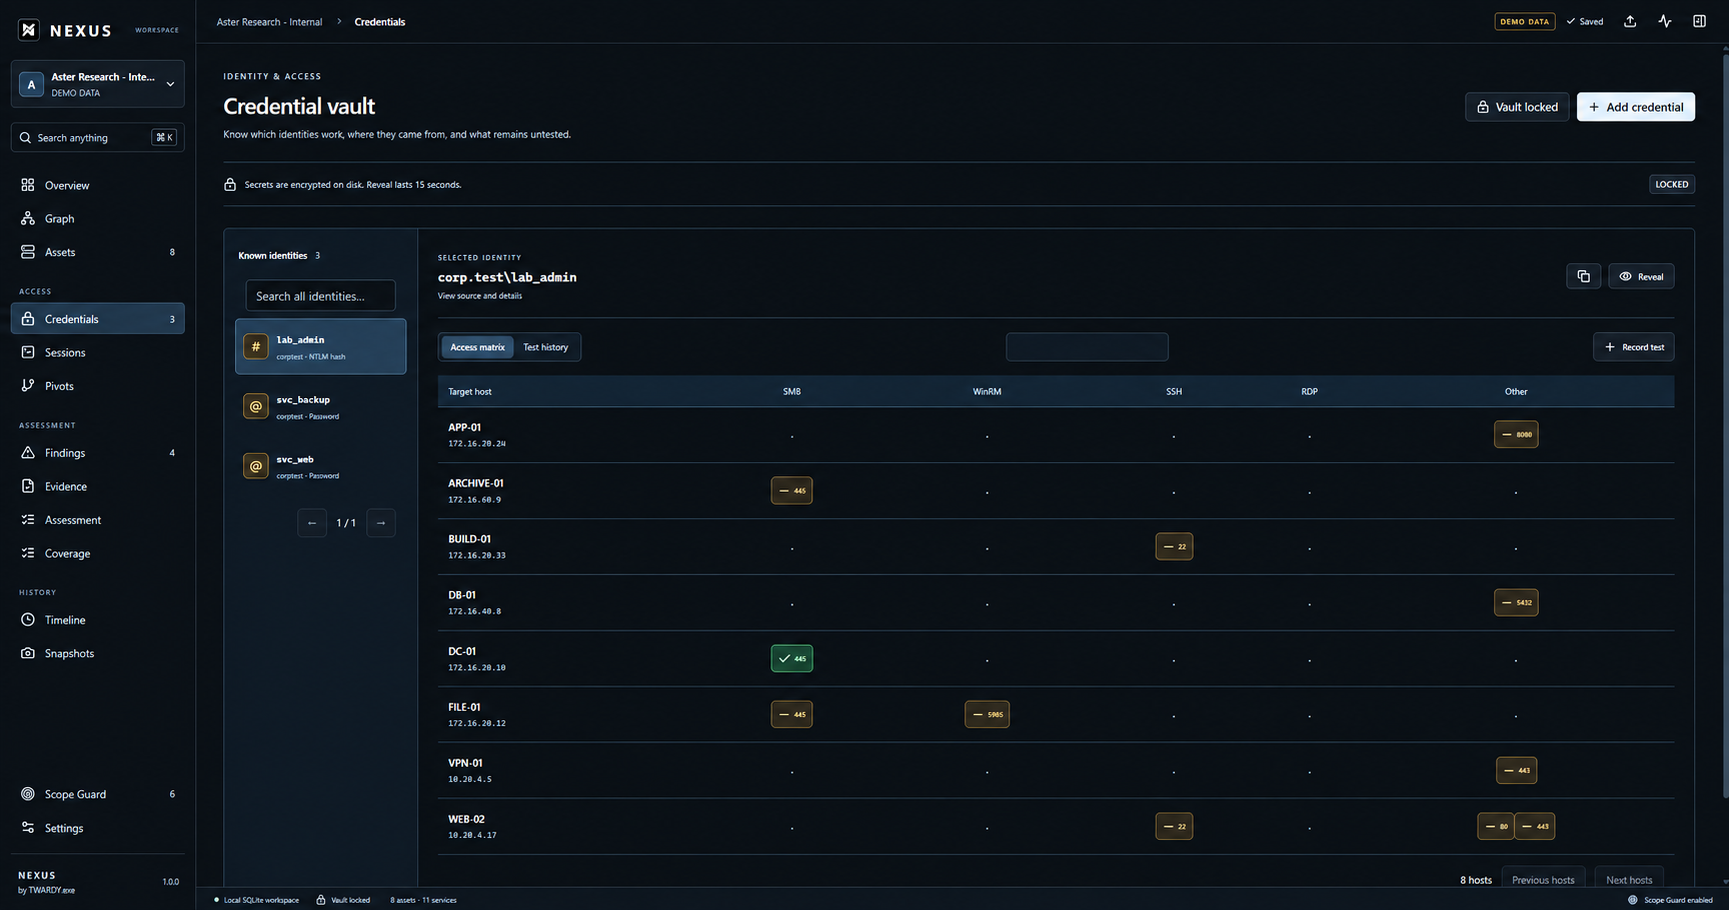
Credential access matrix
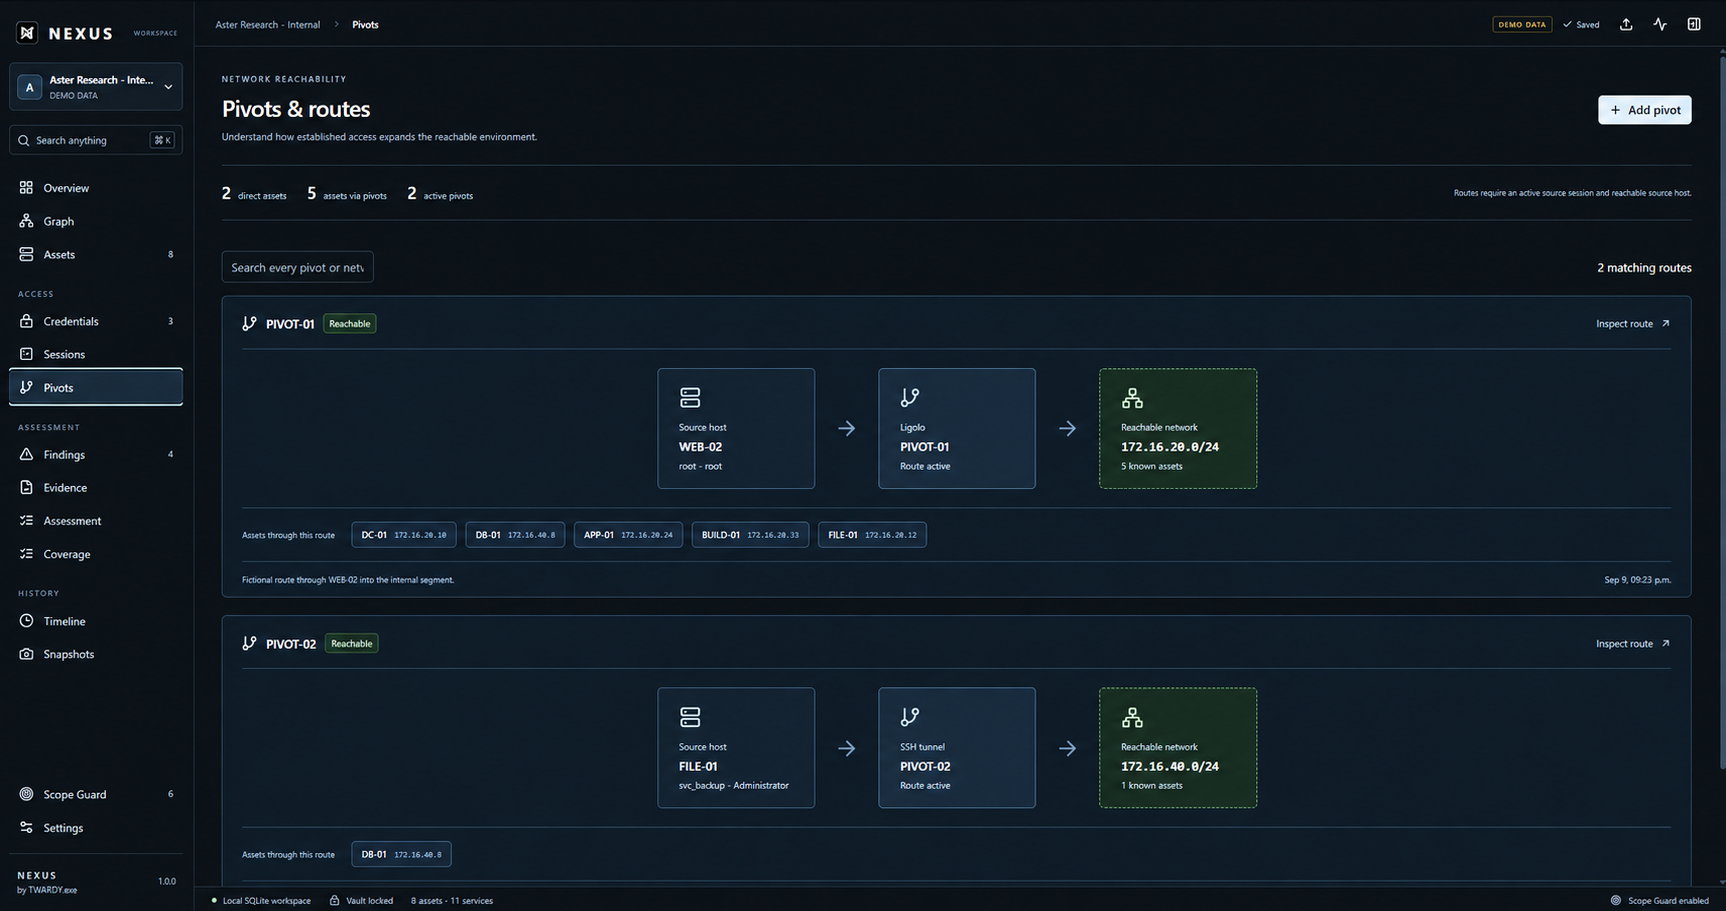
Pivots & routes
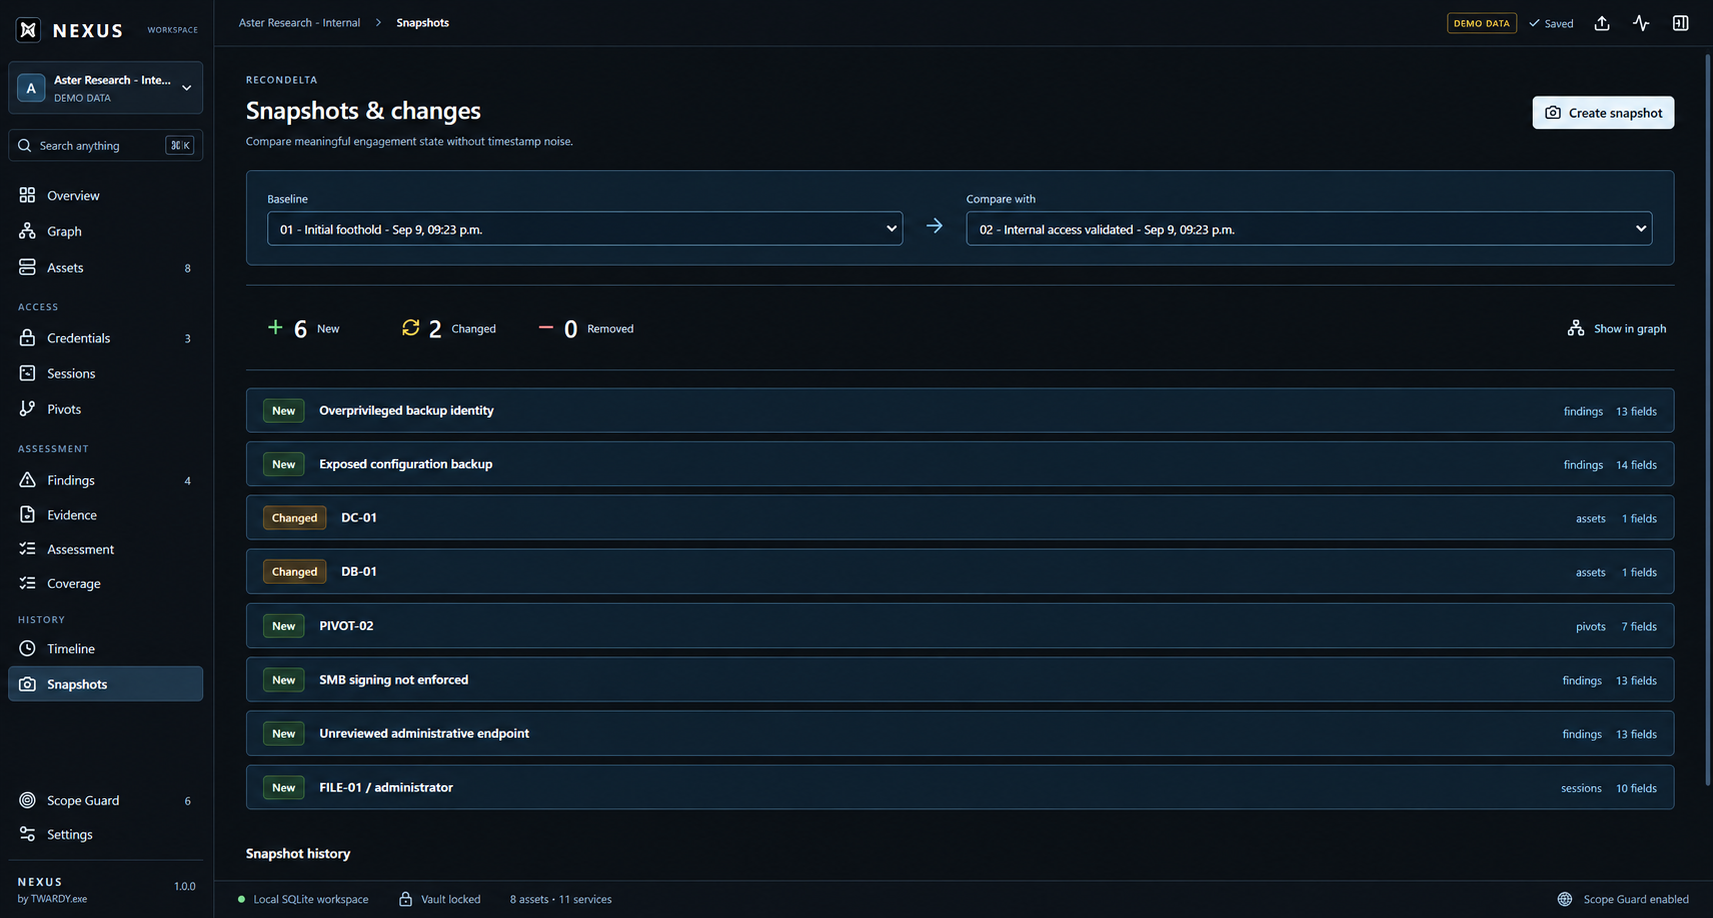
ReconDelta snapshots
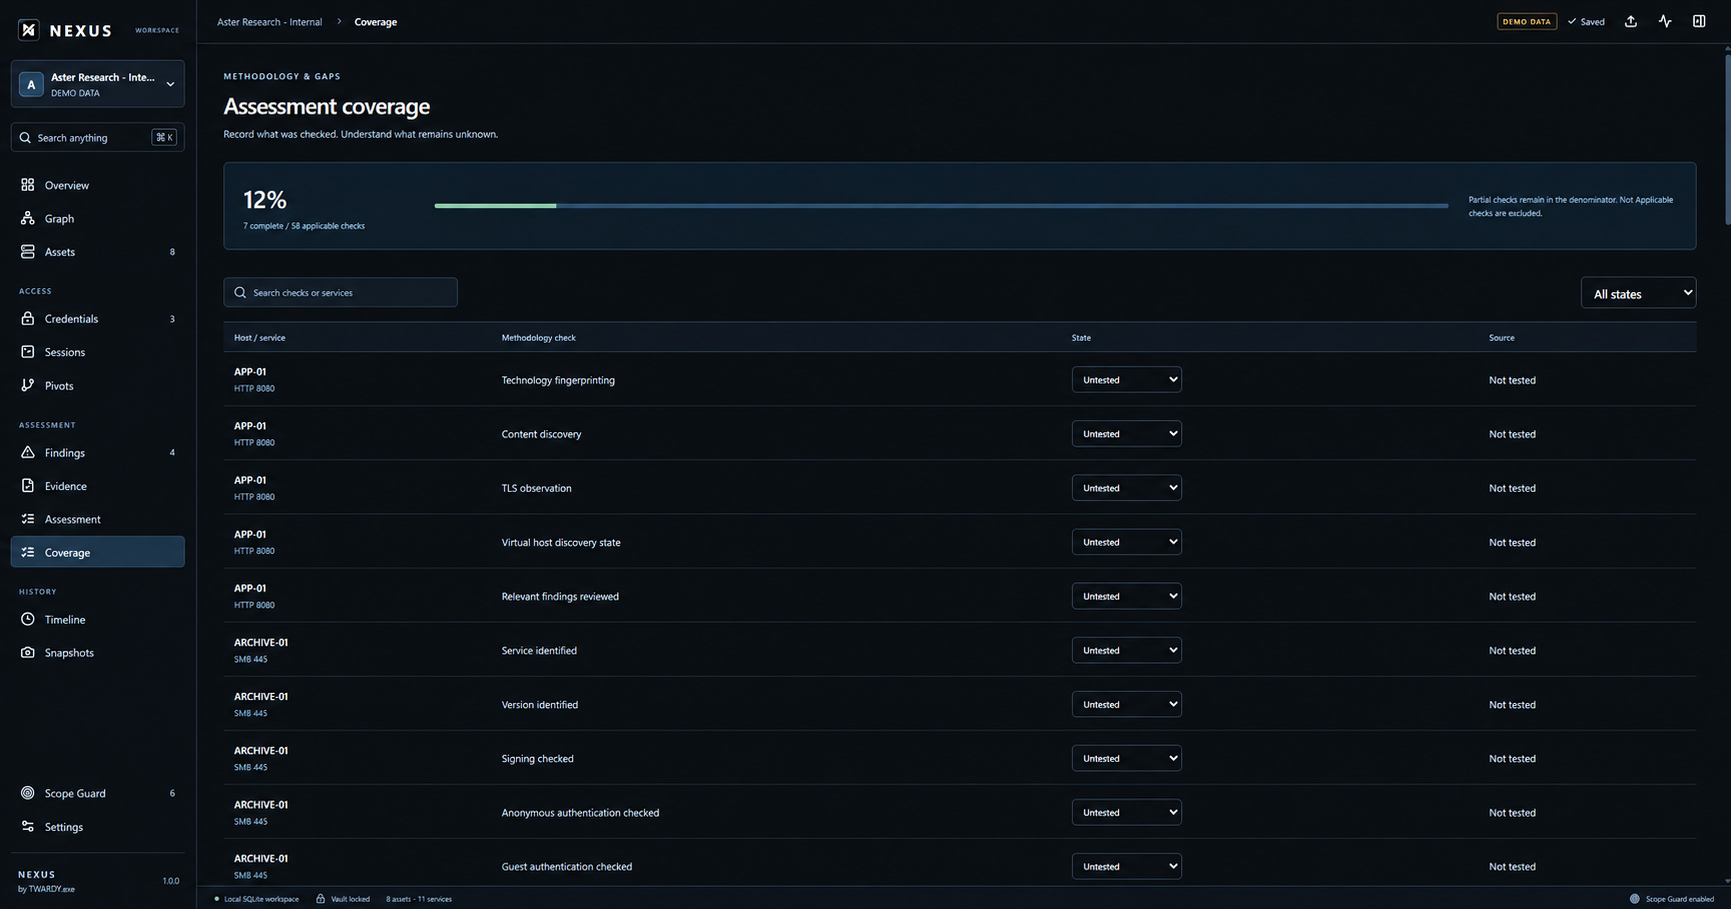
Assessment coverage
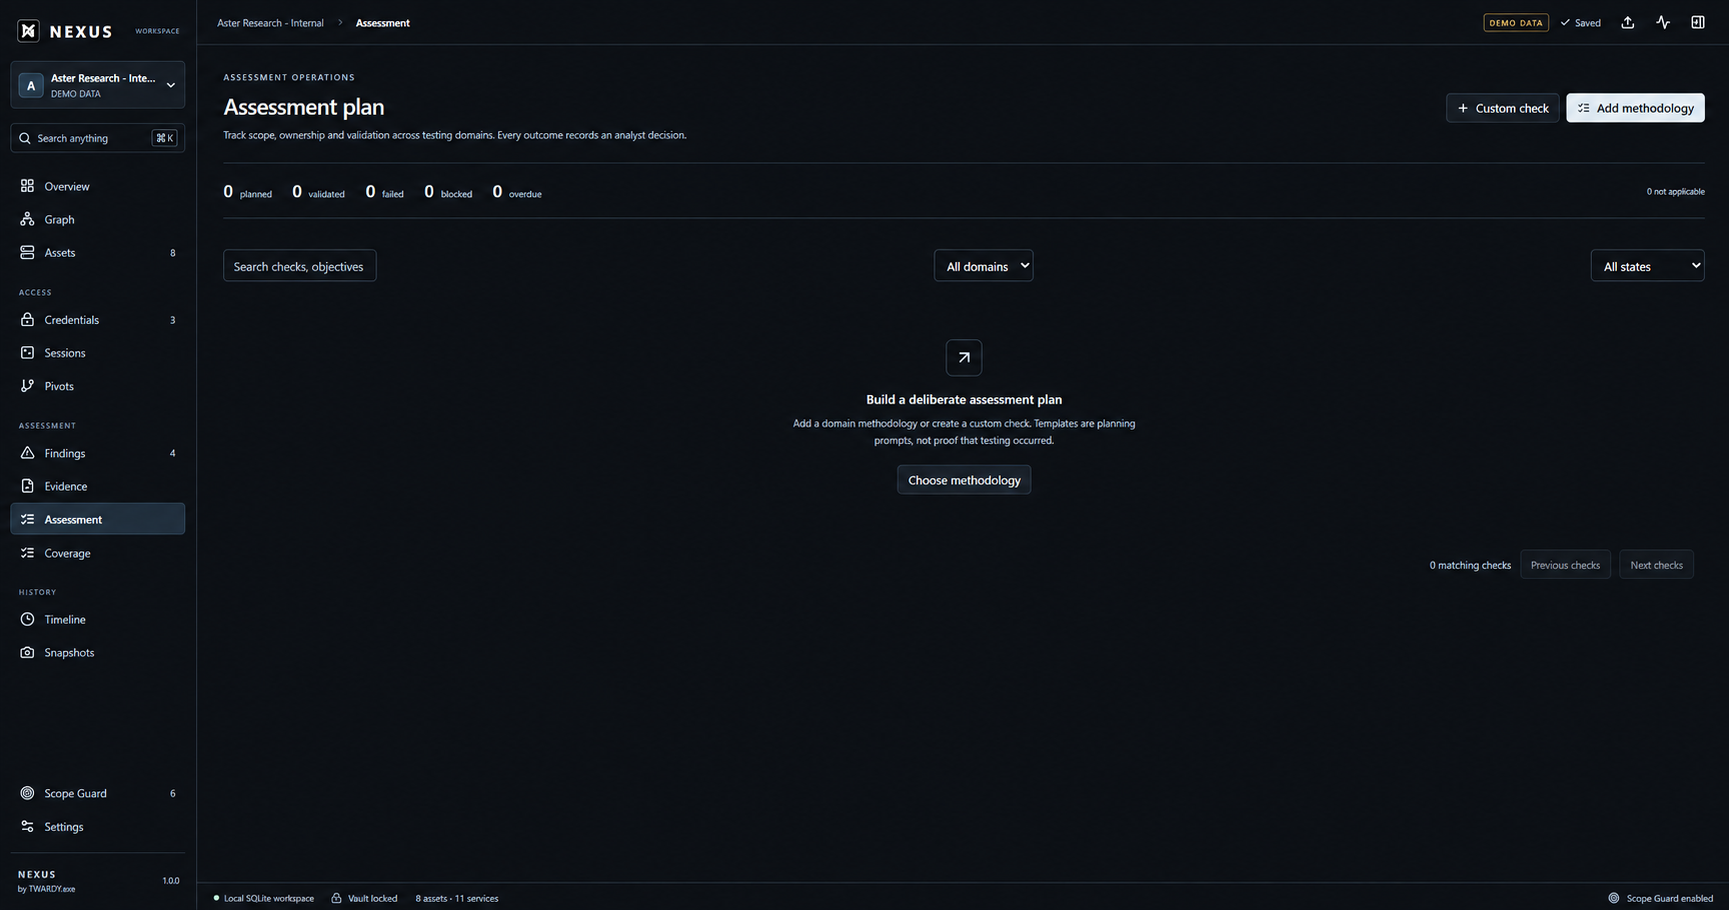
Assessment planning
Why NEXUS
A real engagement quickly becomes more than a folder of scan outputs. Hosts appear under different names, credentials work on some services but not others, pivots change network reachability, scanner findings need evidence, and repeated recon changes the known attack surface.
NEXUS keeps that state connected and explainable.
- One engagement model for assets, identities, access, findings, evidence, and scope.
- Interactive relationship graph instead of disconnected scanner output.
- Encrypted credential vault with a host/service access matrix.
- Sessions and pivots modeled as first-class operational state.
- Deterministic coverage and opportunities based only on recorded facts.
- ReconDelta snapshot comparison for new, changed, and removed state.
- Data provenance so important observations retain their source.
- Local-first architecture with no account, cloud backend, telemetry, analytics, or LLM dependency.
Core capabilities
Engagement intelligence
- Separate assessment workspaces with explicit include/exclude scope rules.
- Hosts, networks, domains, users, web applications, services, aliases, tags, and analyst notes.
- Field-level provenance and confidence-aware observation handling.
- Fast search, filtering, pagination, and keyboard-first navigation.
Graph & attack path
- Cytoscape-based operational graph.
- Assets, services, identities, credentials, sessions, pivots, findings, and relationships.
- Subnet grouping, focus mode, neighborhood filtering, and graph layers.
- Confirmed-access path highlighting based on recorded state rather than speculative AI output.
Credentials & access
- Argon2id-derived vault key.
- XChaCha20-Poly1305 authenticated encryption.
- Secrets masked by default with deliberate temporary reveal.
- Credential → host → service authentication history.
- Valid / invalid / untested access matrix.
- Active sessions, privilege state, and confirmed-access relationships.
Pivots & reachability
- Ligolo, SOCKS, SSH tunnel, port-forward, and generic pivot modeling.
- Session-backed routes.
- Recursive network reachability calculation.
- Explicit
reachable viacontext instead of treating discovery as access.
Findings & evidence
- Finding status, severity, affected asset/service, impact, remediation, CWE/CVE/CVSS metadata.
- Text, screenshot, terminal output, HTTP, and file evidence.
- Evidence integrity verification.
- Markdown and client-safe HTML report export.
Assessment & coverage
- Built-in assessment planning with original methodology checks across multiple domains.
- Custom checks, ownership, deadlines, outcomes, evidence, and finding links.
- Coverage states: Complete, Partial, Untested, Not Applicable.
- Explainable opportunity engine for missing recorded work.
Snapshots / ReconDelta
- Named engagement snapshots.
- Added / changed / removed comparisons.
- Field-level diff inspection.
- Graph overlays for meaningful changes between snapshots.
Recovery & portability
- SQLite WAL-backed local storage.
- Transactional imports.
- Automatic and pre-import backups.
- Recovery into a separate workspace.
- Complete workspace bundle export with attachment manifests and integrity verification.
Supported imports
| Tool / format | Support |
|---|---|
| Nmap XML | Import + reviewed normalization |
| httpx JSON / JSONL | Import + service enrichment |
| Nuclei JSONL | Import + draft findings |
| NetExec output | Import + access observations |
Nessus v2 .nessus |
Import |
| Burp Issues XML | Import |
NEXUS also detects local installations of Nmap, httpx, Nuclei, and NetExec. The built-in active runner is intentionally limited to a fixed, scope-validated Nmap workflow.
Typical workflow
Create engagement
      ↓
Define authorized scope
      ↓
Import / run reconnaissance
      ↓
Review assets & services
      ↓
Record credentials and authentication results
      ↓
Create sessions
      ↓
Model pivots and new reachability
      ↓
Track findings and evidence
      ↓
Review coverage and untested opportunities
      ↓
Capture snapshots / compare changes
      ↓
Export report or verified workspace bundle
Installation
NEXUS supports Windows x64 and Linux x86_64.
Download the latest release from:
Release artifacts include SHA-256 checksums for verification.
Windows
Available packages:
- Windows installer
- Standalone executable
- Portable ZIP
Community builds may be unsigned. Windows can therefore display an Unknown Publisher / SmartScreen warning until code signing is introduced.
Linux
Available packages:
- AppImage — recommended for Arch Linux and other distributions
- DEB — Debian / Ubuntu
- RPM — Fedora / RHEL-compatible distributions
AppImage
chmod +x NEXUS-1.1.1-x86_64.AppImage
./NEXUS-1.1.1-x86_64.AppImage
NEXUS v1.1.1 includes an AppImage compatibility fix for newer Mesa/EGL/Wayland environments, including current Arch Linux systems.
Debian / Ubuntu
sudo apt install ./NEXUS-1.1.1-amd64.deb
Fedora / RHEL
sudo dnf install ./NEXUS-1.1.1-x86_64.rpm
Nmap and optional external integrations such as httpx, Nuclei, and NetExec must be installed separately.
Run from source
Common requirements:
- Node.js 24.x
- Rust stable
Windows additionally requires:
- Microsoft C++ Build Tools + Windows SDK
- Microsoft Edge WebView2 Runtime
Linux requires the native GTK/WebKit dependencies used by Tauri.
git clone https://github.com/TW4RDYDEV/NEXUS.git
cd NEXUS
npm ci
npm run desktop
This launches the real Tauri desktop application backed by the Rust core and SQLite database.
Development & verification
npm run format:check
npm run lint
npm run typecheck
npm test
cargo fmt --manifest-path src-tauri/Cargo.toml -- --check
cargo clippy --manifest-path src-tauri/Cargo.toml --all-targets -- -D warnings
cargo test --manifest-path src-tauri/Cargo.toml
npm run test:e2e
npm run build
npm run fingerprint:test
npm run authorship:check
Windows release build
Run on Windows:
npm ci
npm run release:check
npm run release:build
The Windows release builder remaps local Rust/Cargo paths, stages the Windows x64 artifacts, checks embedded NEXUS identity markers, rejects known local build-path leakage, and creates SHA-256 sums.
Linux release build
Run on Linux x86_64:
npm ci
npm run release:check
npm run release:linux
The Linux release builder produces AppImage, DEB, and RPM packages, performs release validation and deterministic artifact staging, sanitizes the AppImage against known Mesa/EGL/Wayland display-stack conflicts, verifies the final AppImage library policy, and generates SHA-256 checksums.
The repository also includes a GitHub Actions Linux build workflow using Ubuntu 22.04. The workflow builds the Linux release packages, validates the sanitized AppImage, and performs an automated AppImage launch smoke test before artifacts are uploaded.
See Verification, Architecture, and Security for more detail.
Architecture
React + TypeScript / Cytoscape
          │
          │ validated Tauri IPC
          ▼
      Rust core
          │
          ├── SQLite + migrations
          ├── parser adapters
          ├── encrypted vault
          ├── graph / paths
          ├── reachability
          ├── coverage
          ├── snapshots
          ├── evidence / backups
          └── scoped Nmap runner
NEXUS keeps core domain rules in Rust and keeps the React renderer focused on presentation and interaction.
Privacy & security model
NEXUS is local-first.
- No user account.
- No cloud synchronization.
- No telemetry or analytics.
- No hidden network callbacks.
- No LLM dependency.
- Credential secrets are encrypted at rest.
- Imported files are treated as untrusted input.
- Attachments are never automatically executed.
- Active Nmap execution is explicitly initiated and checked against engagement scope.
The rest of the engagement database is not fully encrypted, so hostnames, findings, notes, and evidence should be treated as sensitive assessment data. Full-disk encryption and proper filesystem permissions are strongly recommended.
Read the complete security model.
Responsible use
NEXUS is intended for authorized penetration testing, security research, CTFs, labs, and defensive assessment workflows.
Only assess systems and networks that you own or have explicit permission to test.
The presence of a target in NEXUS does not constitute authorization.
License
NEXUS is source-available, not OSI open-source software.
Under the NEXUS Source-Available License 1.0, you may use NEXUS free of charge, inspect the source, and make private modifications for your own or your organization's internal use.
Professional security use — including paid authorized assessments — is permitted. What is not permitted without prior written authorization is redistributing or mirroring copies of NEXUS, selling it, publishing modified builds, rebranding it, sublicensing it, or offering NEXUS itself as a paid/hosted product.
A limited public-fork exception exists for good-faith contributions to the official project. See LICENSE for the complete terms.
Contributing
Bug reports, documentation improvements, parser fixes, tests, and carefully scoped feature contributions are welcome.
Please read CONTRIBUTING.md before submitting changes.
Support the project
If NEXUS is useful to you, the simplest ways to support development are:
- star the repository;
- report reproducible bugs;
- improve documentation or tests;
- submit focused pull requests;
- sponsor development through the repository Sponsor button when available.
Author
TWARDY.exe / TW4RDYDEV
Cybersecurity · Offensive Security · Networking · Software Development
Map assets. Track access. Understand the path.