
zksync
matter-labs
4,914スター
zkSync: trustless scaling and privacy engine for Ethereum
脆弱性の検出、システム保護、プライバシー対策のツールを探せます。
matter-labs
zkSync: trustless scaling and privacy engine for Ethereum

miaoermua
↩️ 更合理 AdGuard 规则,轻松改善你的使用体验 - 专注于拦截追踪器和 HTTPDNS

mindersec
Software Supply Chain Security Platform

mitchellkrogza
Nginx Block Bad Bots, Spam Referrer Blocker, Vulnerability Scanners, User-Agents, Malware, Adware, Ransomware, Malicious Sites, with anti-DDOS, Wordpress Theme Detector Blocking and Fail2Ban Jail for Repeat Offenders

n5za
86-tool OSINT MCP server with private evidence graphs, image analysis, reverse search, and person dossiers.

nano-rs
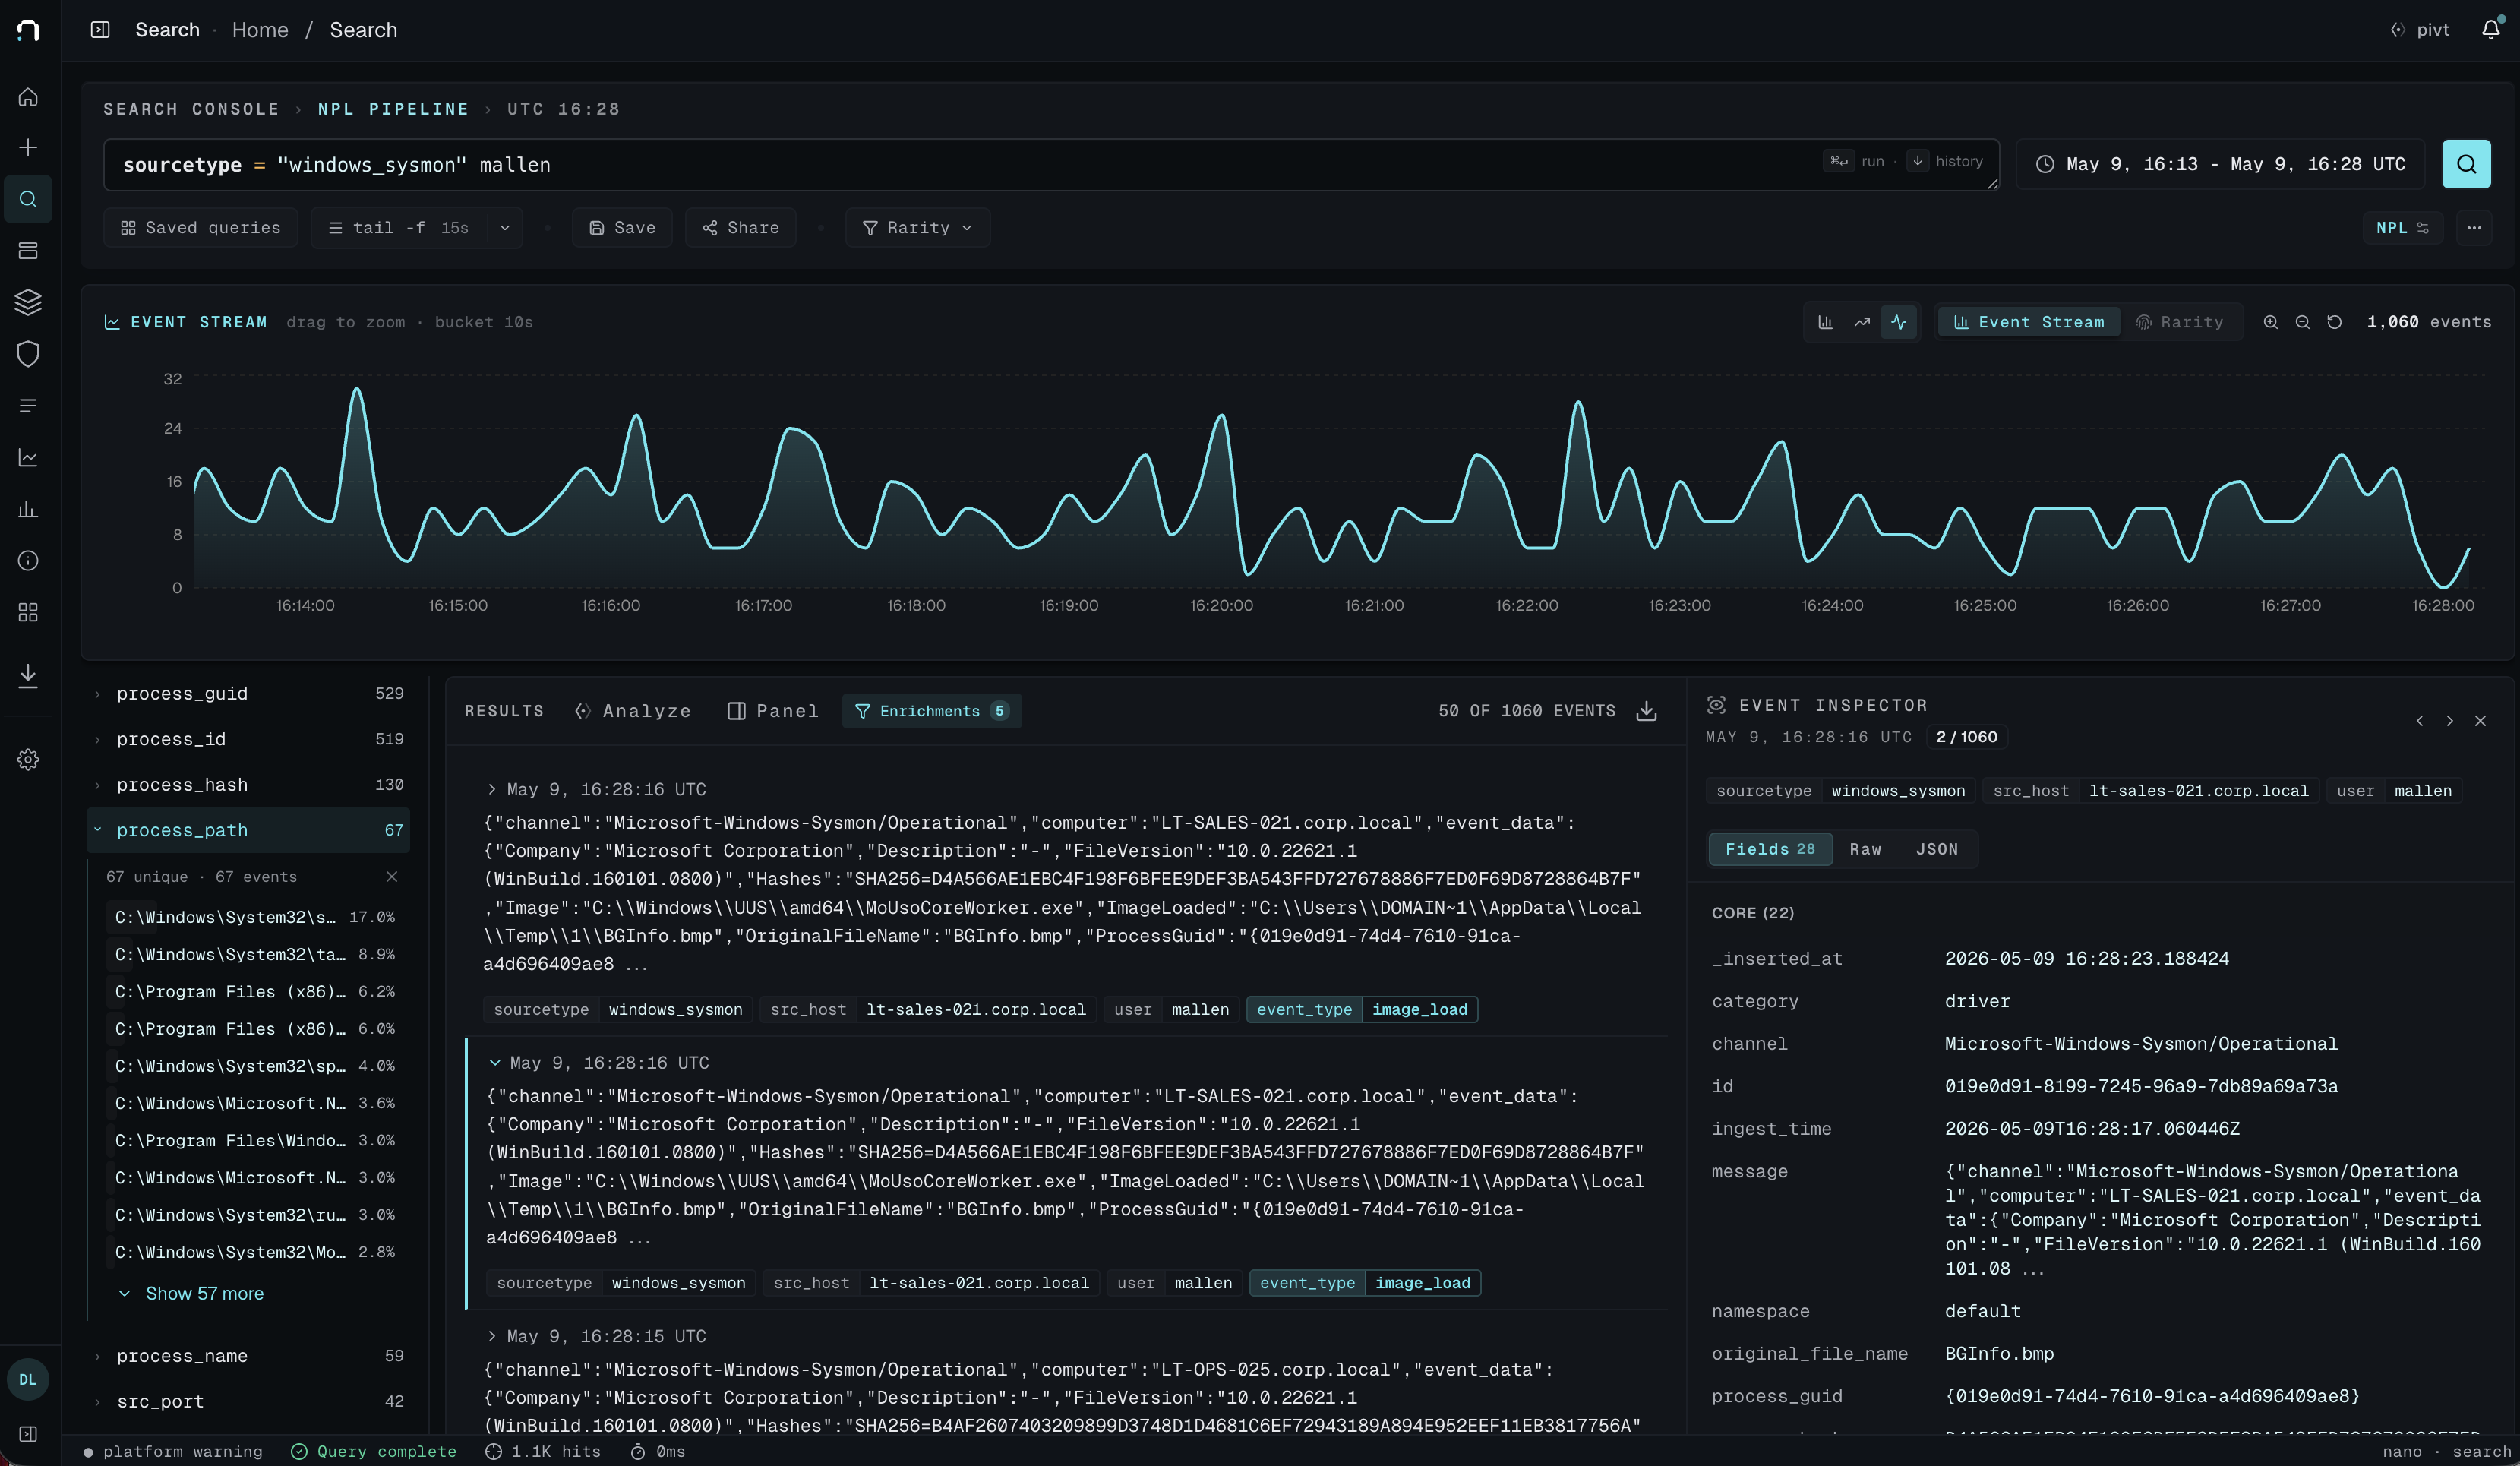
Lightweight open-core SIEM in Rust — S3-compatible for logs, Postgres for state.

nestho
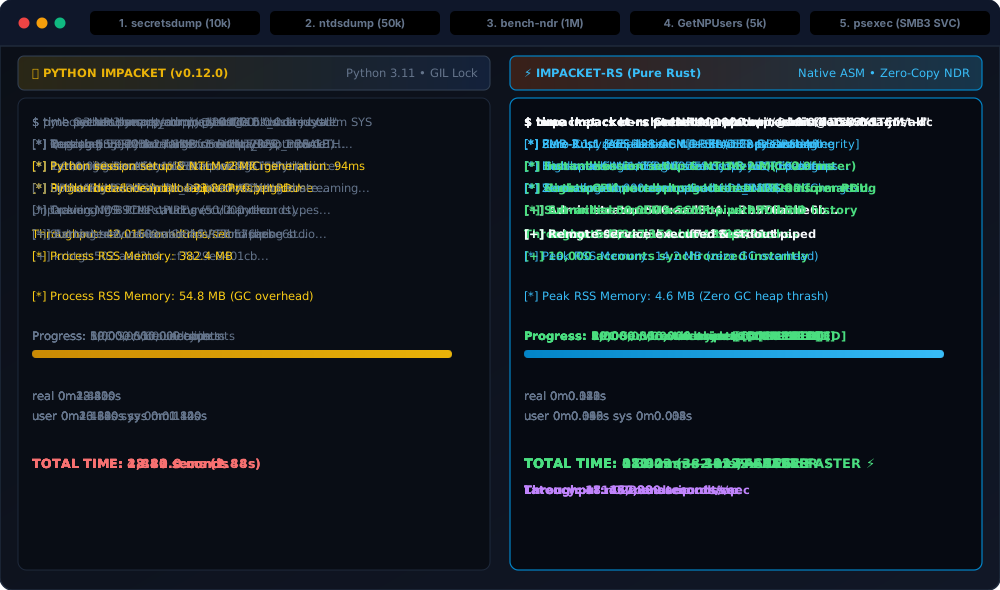
High-performance, memory-safe pure-Rust redesign of Impacket protocols and Active Directory tools for Linux, macOS, and Windows.

nix-community
Vulnerability (CVE) scanner for Nix/NixOS [maintainer=@henrirosten]

noel-mugisha
A comprehensive security repo for modern Java backend applications. The only identity provider you’ll ever need.

NoMoreFood
Windows administration utility for process privileges, registry and API overrides, application compatibility testing, diagnostics, and local account rights management.

NyxFoundation
A Lean backend framework whose authorization safety is formally proven. The developer writes only a Cedar schema and policies; handlers are built on Supabase Auth and PostgreSQL.

openguardrails
A firewall for the agents your agents spawn.

opentrap
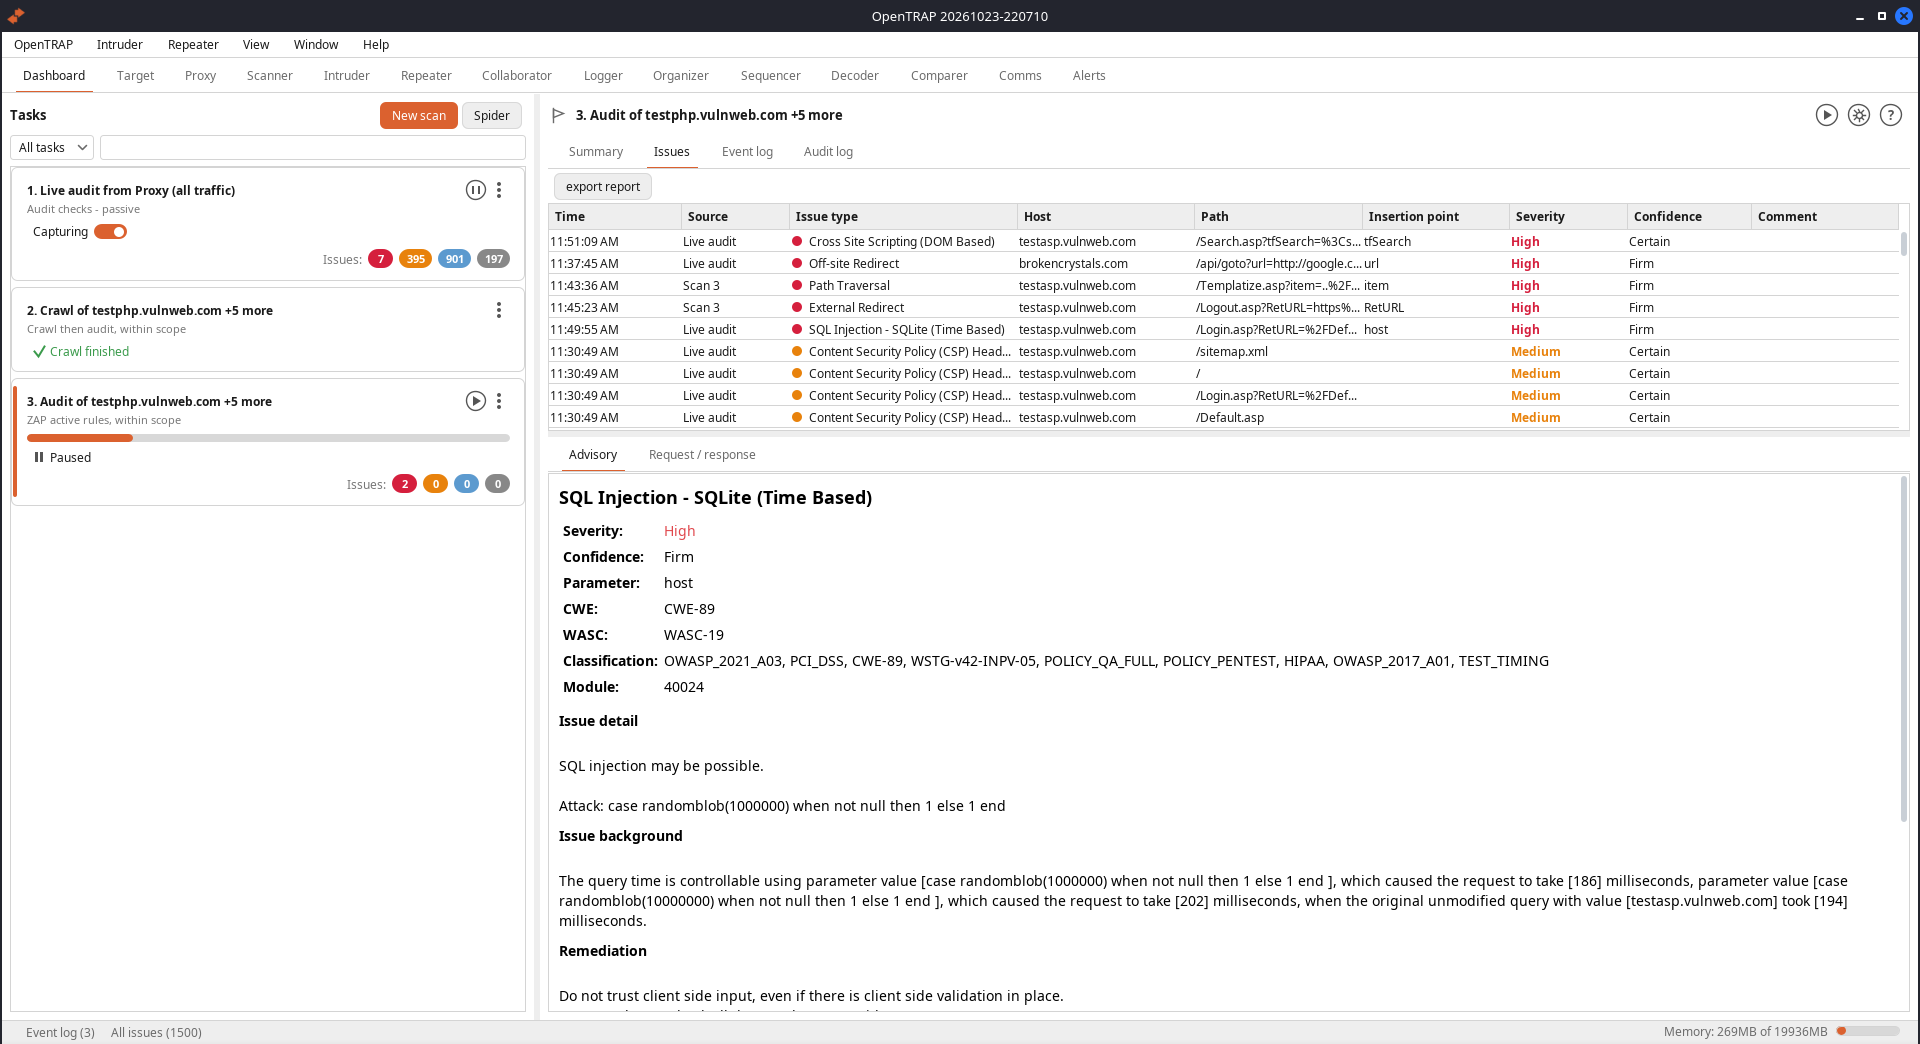
A free, open-source alternative to Burp Suite: an intercepting proxy and web app security testing suite with Repeater, Intruder, Collaborator and a built-in OWASP ZAP scanner. Linux, AGPL-3.0.

OrangeLab-space
Private infrastructure on consumer hardware based on K3s, Tailscale, Pulumi and Longhorn
Runtime defense against memory poisoning in AI agents (OWASP ASI06). Drop-in for LangChain, OpenAI Agents, AutoGen, CrewAI and mem0.
Play Scala demo to test the play-pac4j security library

pando85
Kubernetes operator for managing Kanidm

pentestershell
Python scanner for CVE-2026-109618, CVE-2026-109619 and the php2shell session chains (handler mismatch + LFI). No external dependencies.

phishdestroy
ShortDot registry abuse investigation across seven TLDs: zone analysis, phishing evidence, classified IOC feeds and STIX exports.

profullstack
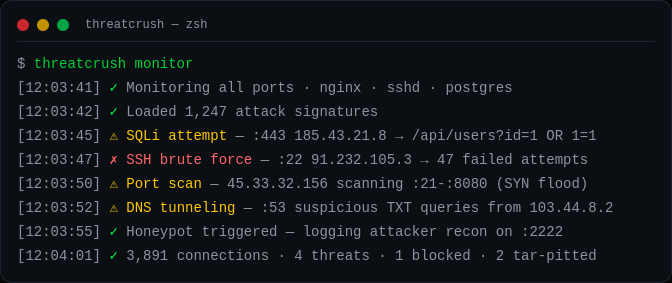
Real-time threat intelligence platform with threat feeds, vulnerability tracking, attack surface monitoring, and threat actor intelligence.

project-dalec
📦 Produce secure packages and containers with declarative configurations

projectdiscovery
Community curated list of search queries for various products across multiple search engines.

psalm

Security-focused Laravel static analyser

pwndoc-ng

Pentest Report Generator

