
ultrasecurity/Storm-Breaker
ultrasecurity/Storm-Breaker has 6,285 GitHub stars and 2,014 forks. GitHot measured +12 stars in 24 hours and +22 in 7 days. Last checked 2026-11-09 21:08 UTC. Last push 2026-11-01.
Full-featured Social Engineering Framework with Page Cloning, MITM Proxy, Credential Capture, Session Extraction, and Real-time Monitoring.
できること
- Page Cloning — Headless Chrome rendering with cURL fallback; strips original scripts, injects payloads, resolves assets via <base href>
- MITM Proxy — transparent reverse proxy that relays requests to the real target, rewrites all URLs, and patches fetch/XHR/WebSocket/history so the entire session stays routed through the operator
- Credential Sniffing — smart extraction from POST bodies: form-urlencoded, multipart, JSON, GraphQL, Livewire RPC, Inertia.js, and nested structures
- Credential Verification — auto-detects login success or failure from HTTP status codes, redirects, JSON responses, and HTML re-renders
計測したスター増加
- 24時間
- +12
- 7日間
- +22
- 15日間
- 履歴を収集中
- 1か月
- 履歴を収集中
期間ごとの純増数です。期間は重複しており、日別の値ではありません。未計測の値は空欄です。スター数は注目度の指標であり、品質の保証ではありません。
README.md
オリジナル
Storm Breaker v3
Advanced Phishing & Social Engineering Framework with MITM Proxy, Credential Harvesting, Session Hijacking, and Browser-Based Tracking.


What is Storm Breaker?
Storm Breaker clones a target web page and injects capture modules (camera, microphone, geolocation, device-info, form credentials) that run in the visitor's browser, collecting data back to the operator's panel.
This is a lab tool for authorized security testing. Use responsibly and within legal boundaries.
Features
- Page Cloning — Headless Chrome rendering with cURL fallback; strips original scripts, injects payloads, resolves assets via
<base href> - MITM Proxy — transparent reverse proxy that relays requests to the real target, rewrites all URLs, and patches fetch/XHR/WebSocket/history so the entire session stays routed through the operator
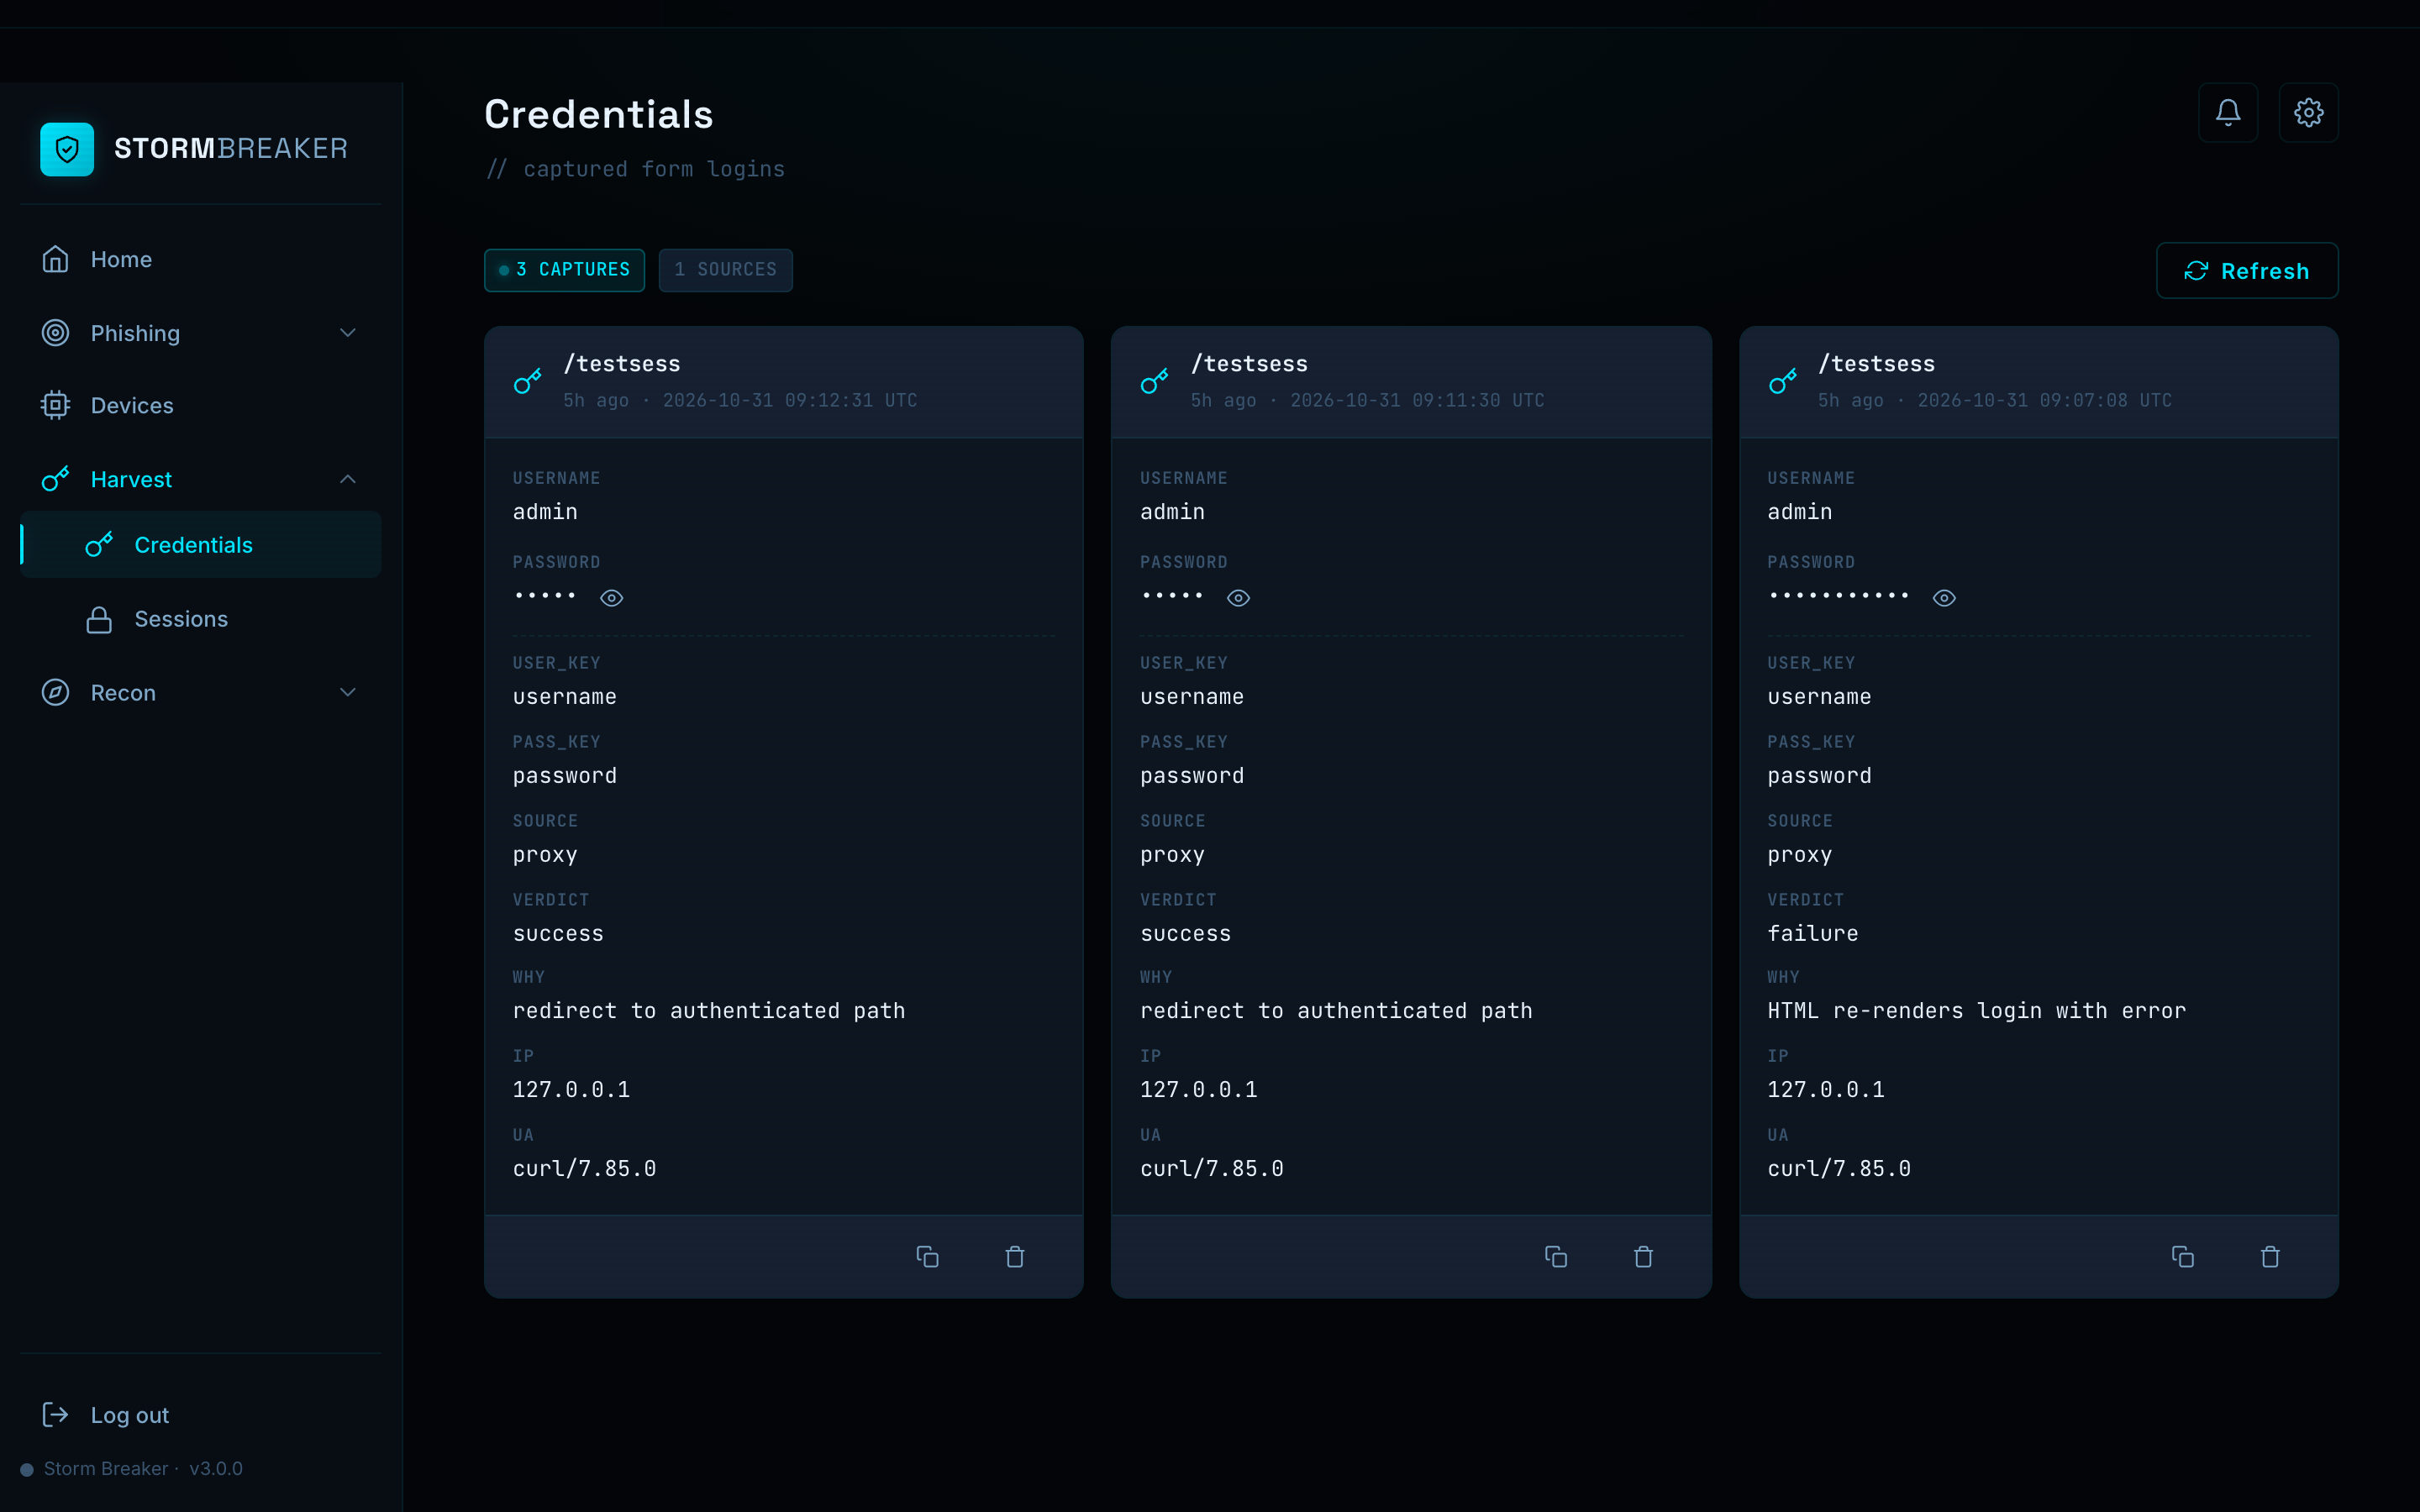
- Credential Sniffing — smart extraction from POST bodies: form-urlencoded, multipart, JSON, GraphQL, Livewire RPC, Inertia.js, and nested structures
- Credential Verification — auto-detects login success or failure from HTTP status codes, redirects, JSON responses, and HTML re-renders
- Session Hijacking — snapshots the victim's cookie jar on verified login and exports Cookie-Editor JSON for instant session replay
- Camera Capture — periodic snapshots from the visitor's webcam with proper cleanup on revoke/pagehide
- Microphone Recording — audio clip capture from the visitor's mic
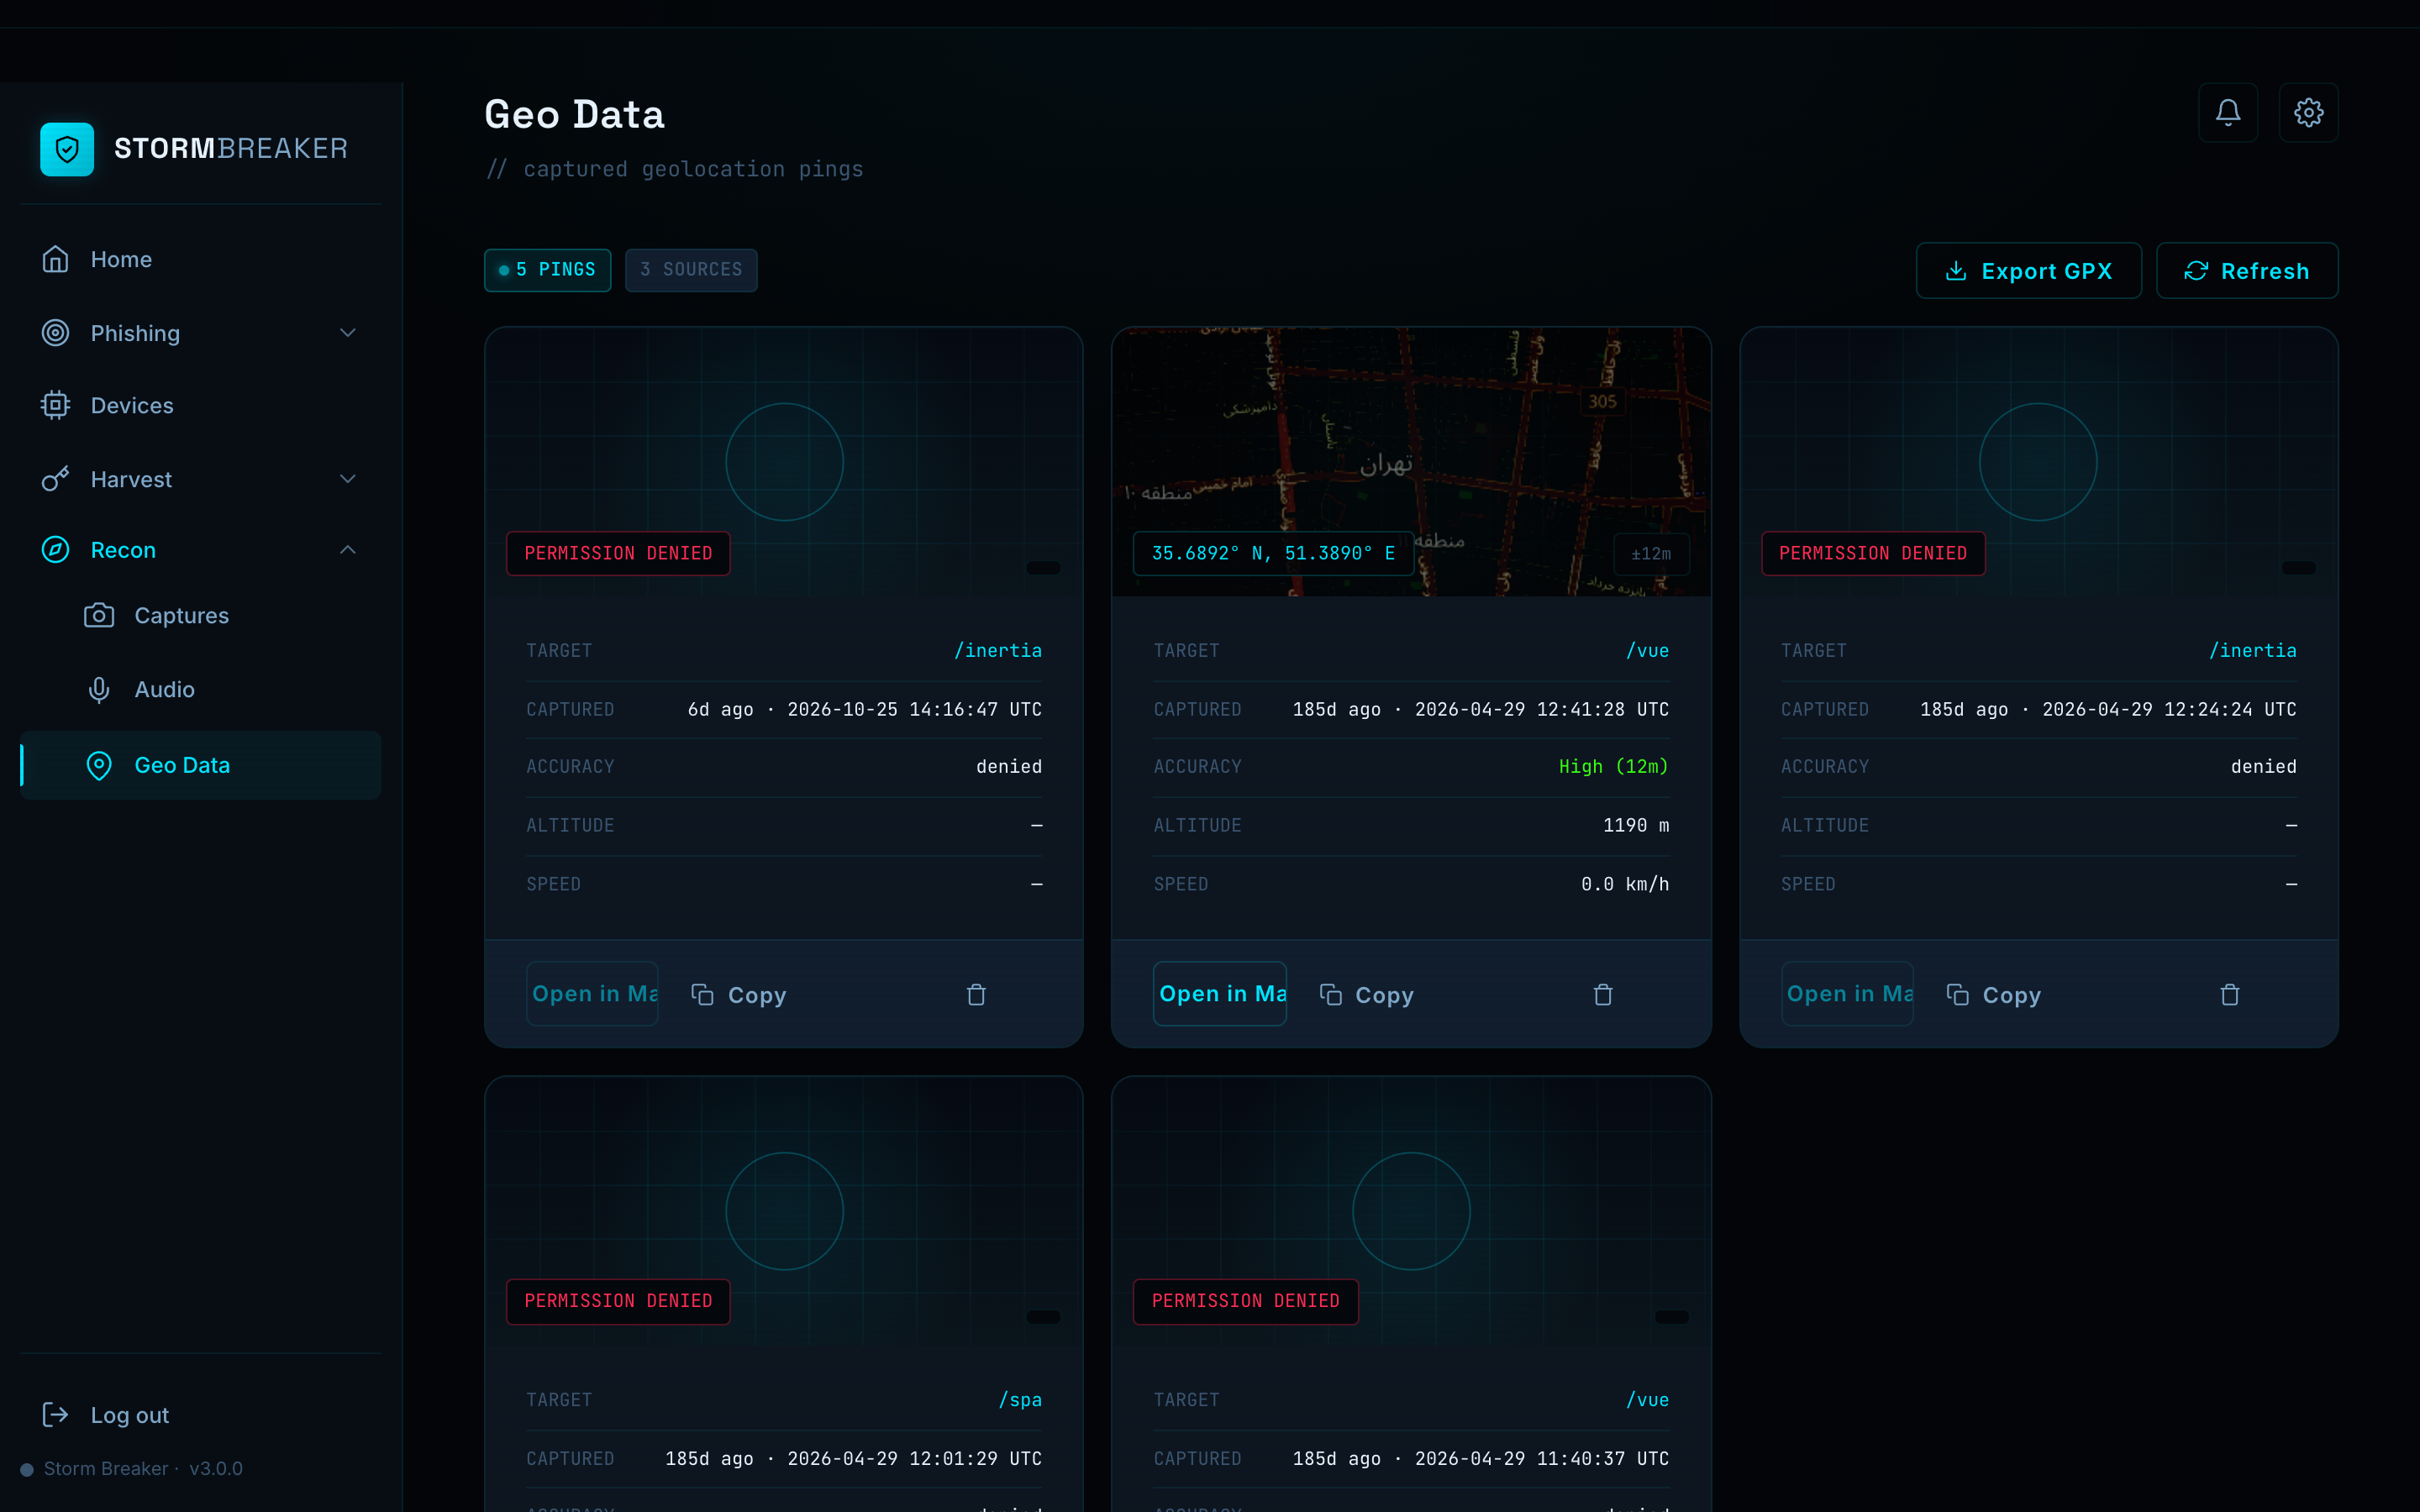
- Geolocation Tracking — GPS location pings with coordinates and accuracy
- Device Fingerprinting — browser, OS, screen, and hardware info (always on)
- Custom JS Injection — inject your own JavaScript into cloned pages; runs after all built-in payloads with access to the Storm Breaker runtime API
- Homograph Domain Generator — 9 confusion categories: Cyrillic, Armenian, Greek, mixed-script, diacritics, digit swap, bigram swap, edit distance, and TLD swap with RDAP availability check
- Real-time SSE Stream — Server-Sent Events push for live credential and session notifications
Screenshots
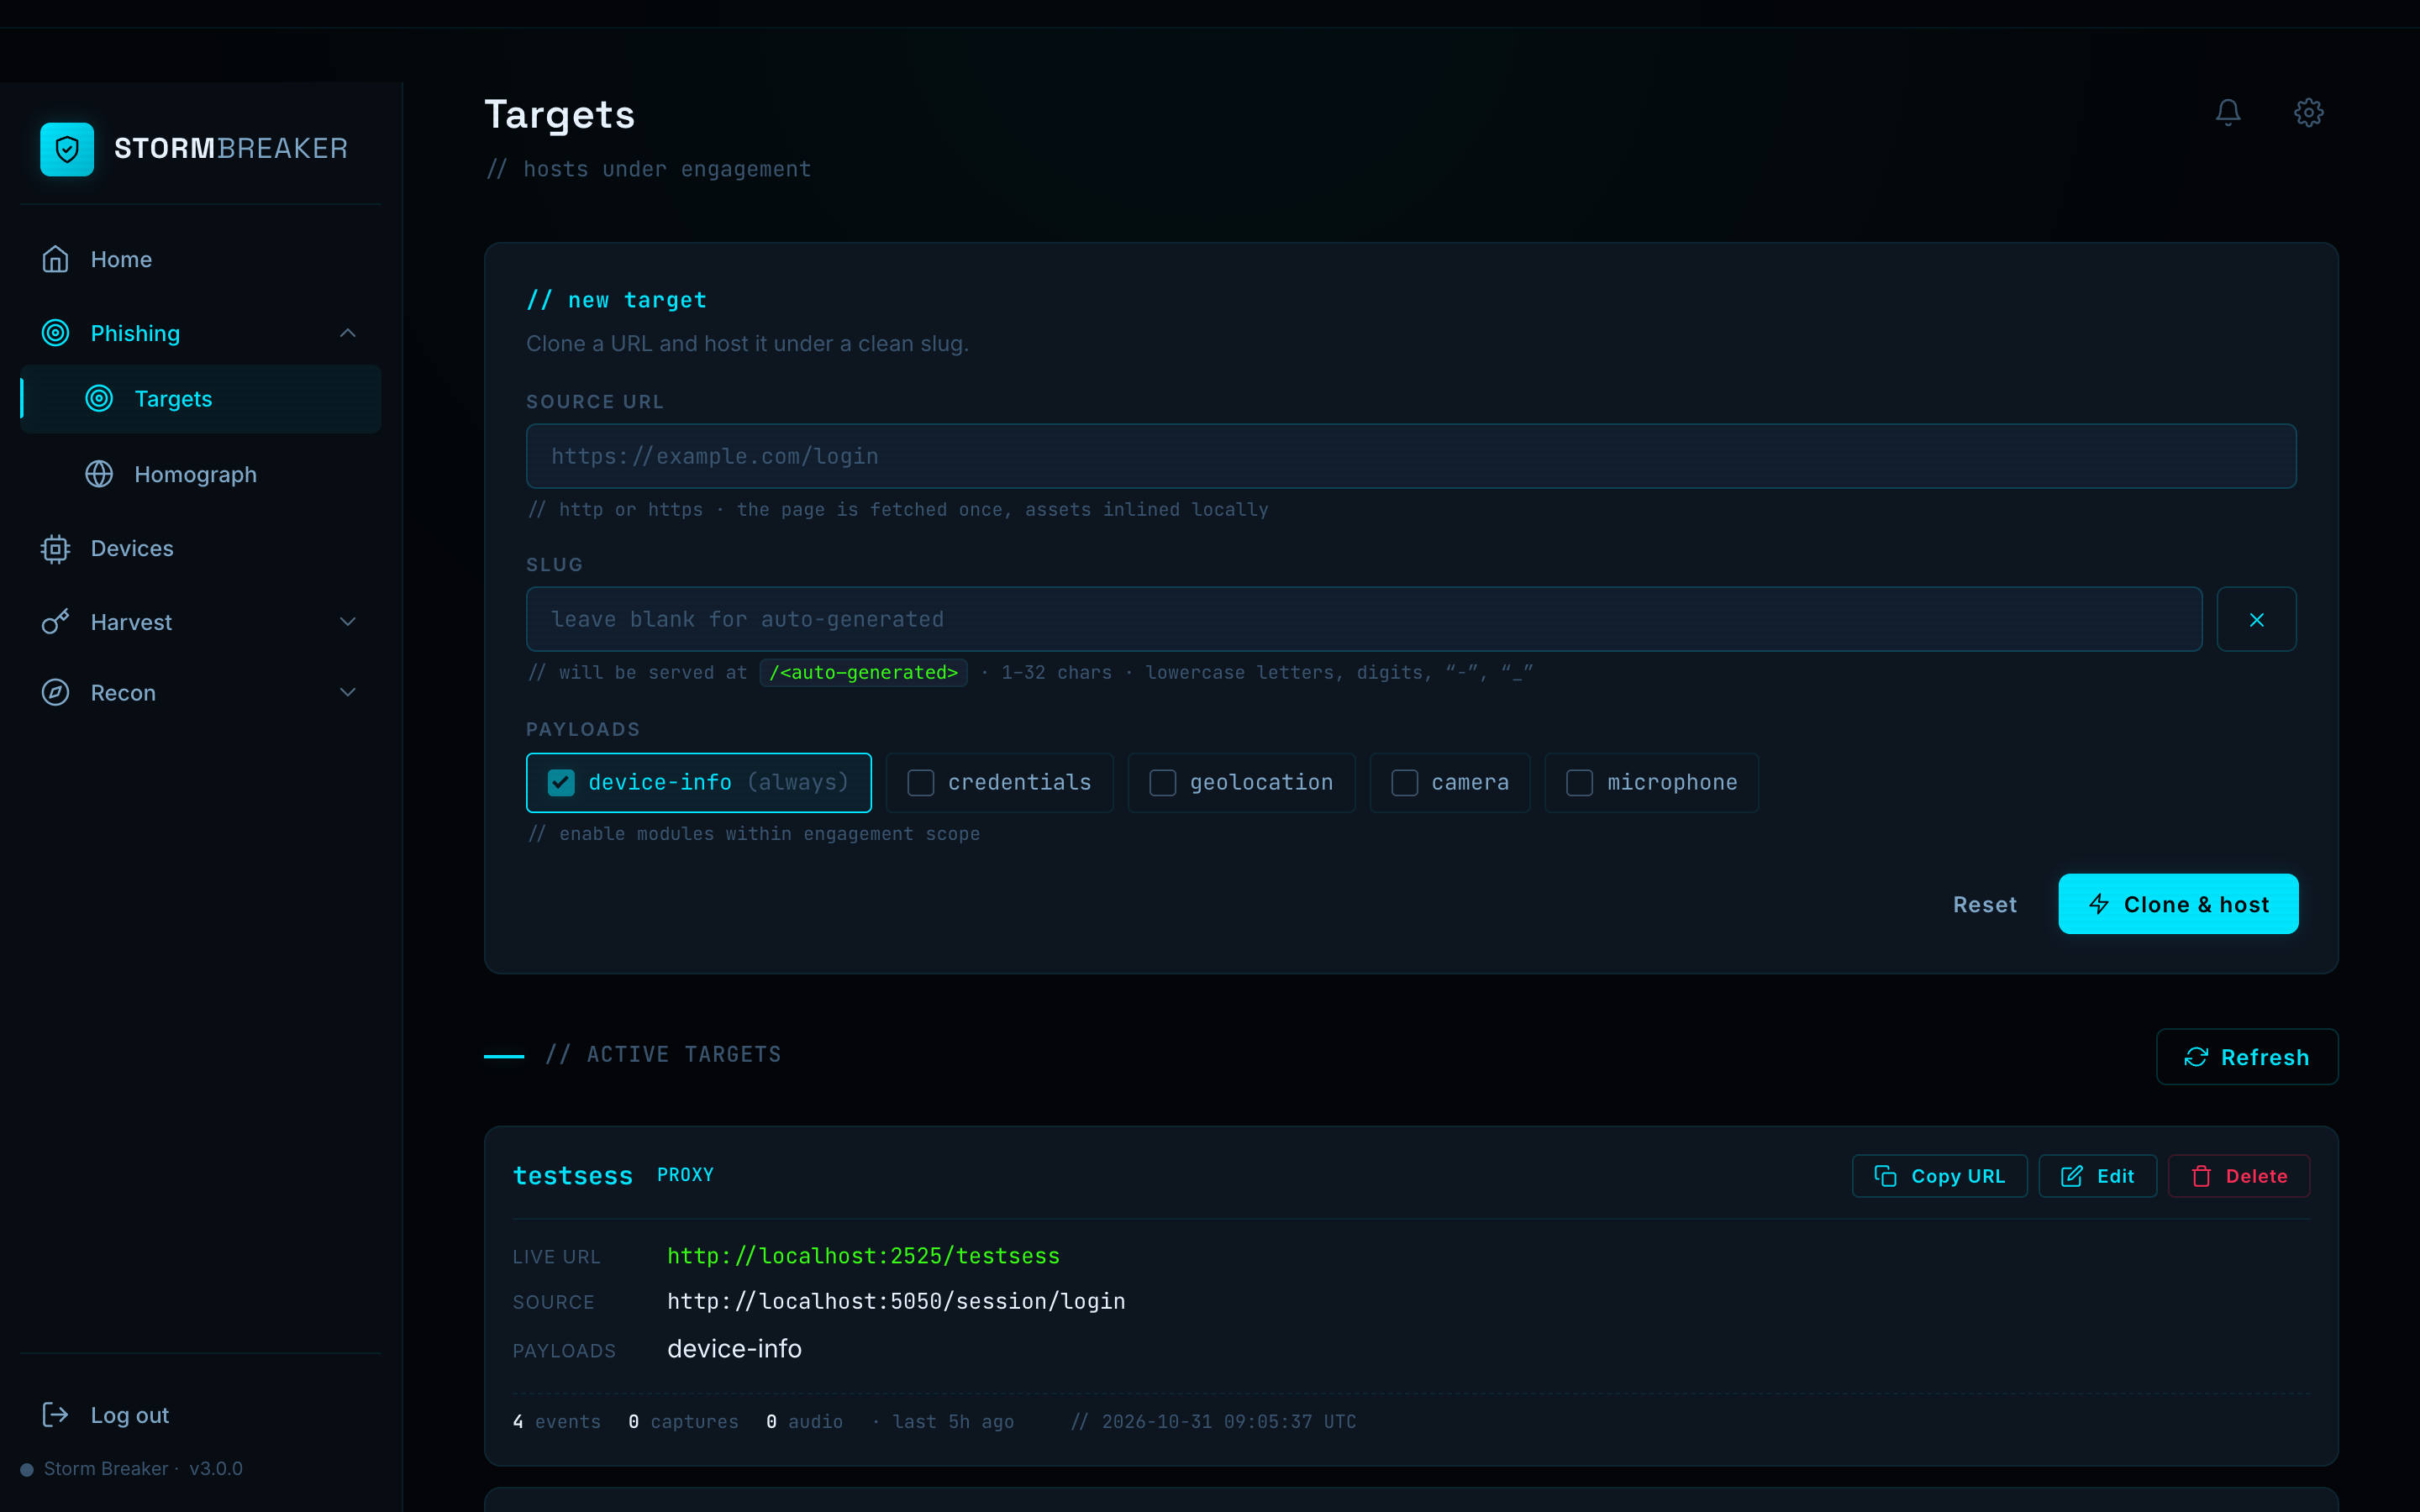
Targets — Clone & Host
Credentials — Captured Logins
Geo Data — Location Pings
Quick Start
git clone https://github.com/ultrasecurity/Storm-Breaker.git
cd Storm-Breaker
php run-local.php
Open http://localhost:2525 — default credentials: admin / admin.
Requirements: PHP 7.4+ with ext-sqlite3, ext-curl, ext-json, ext-session. Headless Chrome optional (enables full SPA cloning).
Server Deployment
sudo bash deploy.sh
The setup wizard walks you through everything: server IP, HTTPS certificate, and admin credentials. It handles Debian/Ubuntu and RHEL/CentOS/Fedora automatically.
If you have a domain, the wizard can set up a free HTTPS certificate from Let's Encrypt — just have your domain and email ready.
HTTPS is required — camera, microphone, and geolocation APIs only work in secure contexts.
Advanced: skip the wizard with flags
sudo bash deploy.sh --ip 1.2.3.4 --domain panel.example.com --email [email protected]
| Flag | Description |
|---|---|
--ip |
Server IP (auto-detected by default) |
--domain |
Domain for Let's Encrypt TLS |
--email |
Email for Let's Encrypt |
--php-port |
Internal PHP port (default: 9874) |
--user |
Service user (default: stormbreaker) |
--uninstall |
Remove service + nginx config |
Usage
- Go to Targets → enter a URL → select payloads → Clone & host
- Send the generated
https://your-domain.com/<slug>link to the target - View captured data in Devices, Credentials, Captures, Audio, Geo Data
Security Notes
- Change default credentials — the deploy script prompts for this; do it.
capture.phpis intentionally public — it has slug validation, path-traversal guards, and size/rate caps.data/is protected —router.phpblocks direct access;.htaccessas backup.- systemd hardening —
NoNewPrivileges,PrivateTmp,ProtectSystem=full,UMask=0077.
Migrating from v2
php storm-web/tools/migrate-to-sqlite.php
Imports result.txt, meta.json, captures/, and audio/ from each target into SQLite. Safe to re-run.
License
MIT License — see LICENSE for details.