
google/oss-fuzz has 12,949 GitHub stars and 2,992 forks. GitHot measured +4 stars in 24 hours and +30 in 7 days. Last checked 2026-11-12 17:13 UTC. Last push 2026-11-04.
OSS-Fuzz - オープンソースソフトウェア向けの継続的なファジング。
計測したスター増加
- 24時間
- +4
- 7日間
- +30
- 15日間
- 履歴を収集中
- 1か月
- 履歴を収集中
期間ごとの純増数です。期間は重複しており、日別の値ではありません。未計測の値は空欄です。スター数は注目度の指標であり、品質の保証ではありません。
README.md
オリジナルOSS-Fuzz: Continuous Fuzzing for Open Source Software
Fuzz testing is a well-known technique for uncovering programming errors in software. Many of these detectable errors, like buffer overflow, can have serious security implications. Google has found thousands of security vulnerabilities and stability bugs by deploying guided in-process fuzzing of Chrome components, and we now want to share that service with the open source community.
In cooperation with the Core Infrastructure Initiative and the OpenSSF, OSS-Fuzz aims to make common open source software more secure and stable by combining modern fuzzing techniques with scalable, distributed execution. Projects that do not qualify for OSS-Fuzz (e.g. closed source) can run their own instances of ClusterFuzz or ClusterFuzzLite.
We support the libFuzzer, AFL++, and Honggfuzz fuzzing engines in combination with Sanitizers, as well as ClusterFuzz, a distributed fuzzer execution environment and reporting tool.
Currently, OSS-Fuzz supports C/C++, Rust, Go, Python, Java/JVM, JavaScript and Lua code. Other languages supported by LLVM may work too. OSS-Fuzz supports fuzzing x86_64 and i386 builds.
Overview
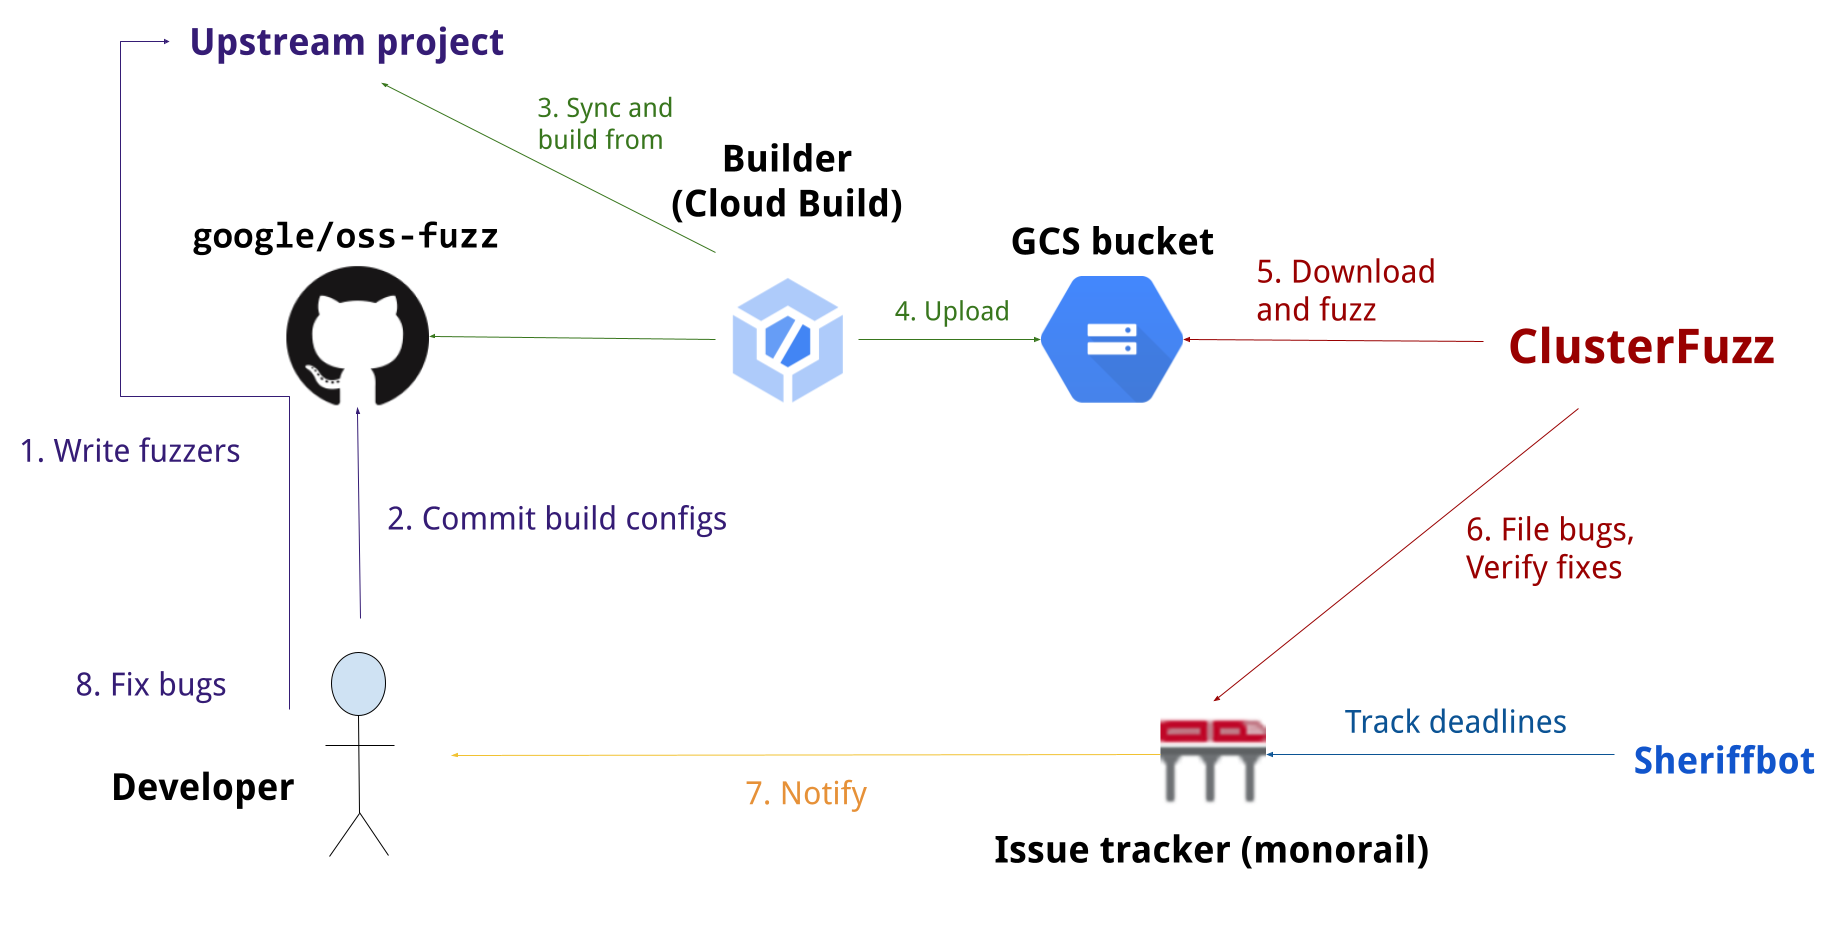
Documentation
Read our detailed documentation to learn how to use OSS-Fuzz.
Trophies
As of May 2025, OSS-Fuzz has helped identify and fix over 13,000 vulnerabilities and 50,000 bugs across 1,000 projects.
Blog posts
- 2024-11-20 - Leveling Up Fuzzing: Finding more vulnerabilities with AI
- 2023-08-16 - AI-Powered Fuzzing: Breaking the Bug Hunting Barrier
- 2023-02-01 - Taking the next step: OSS-Fuzz in 2023
- 2022-09-08 - Fuzzing beyond memory corruption: Finding broader classes of vulnerabilities automatically
- 2021-12-16 - Improving OSS-Fuzz and Jazzer to catch Log4Shell
- 2021-03-10 - Fuzzing Java in OSS-Fuzz
- 2020-12-07 - Improving open source security during the Google summer internship program
- 2020-10-09 - Fuzzing internships for Open Source Software
- 2018-11-06 - A New Chapter for OSS-Fuzz
- 2017-05-08 - OSS-Fuzz: Five months later, and rewarding projects
- 2016-12-01 - Announcing OSS-Fuzz: Continuous fuzzing for open source software
関連プロジェクトを探す
trimstray/the-book-of-secret-knowledge
インスピレーションを与えるリスト、マニュアル、チートシート、ブログ、ハック、ワンライナー、CLI/Web ツールなどを集めたコレクション。
257,996 スターHack-with-Github/Awesome-Hacking
ハッカー、ペンテスター、セキュリティ研究者向けのさまざまな Awesome リスト集。
125,360 スターswisskyrepo/PayloadsAllTheThings
Web アプリケーションセキュリティおよびペネトレーションテスト/CTF 向けの、実用的なペイロードとバイパスの一覧。
82,623 スターcaddyserver/caddy
高速で拡張しやすい、マルチプラットフォーム対応の HTTP/1-2-3 Web サーバー。自動 HTTPS に対応
79,020 スター