
ThalesGroup/secure-ml
ThalesGroup/secure-ml has 26 GitHub stars and 6 forks. GitHot measured 0 stars in 24 hours and 0 in 7 days. Last checked 2026-11-12 12:38 UTC. Last push 2026-08-26.
Explore ThalesGroup's comprehensive framework for secure machine learning systems on this repository. Developed by Thales experts, this framework encompasses essential security requirements, guidelines, tools, and privacy recommendations tailored specifically for machine learning applications.
計測したスター増加
- 24時間
- 0
- 7日間
- 0
- 15日間
- 履歴を収集中
- 1か月
- 履歴を収集中
期間ごとの純増数です。期間は重複しており、日別の値ではありません。未計測の値は空欄です。スター数は注目度の指標であり、品質の保証ではありません。
README.md
オリジナルThis repository provides a wealth of information on securing machine learning projects, including, but not limited to, the following items.
Table of Contents
- Security Policy for Machine Learning Systems
- Machine Learning Privacy-Preserving Techniques
- Tools for Securing Machine Learning
- Security Threats to Machine Learning
- ML Security Regulations and Standards
- Agentic AI Threat Comparison
- Agentic AI Lifecycle
Security Policy for Machine Learning Systems
A ThalesGroup policy framework to secure machine learning datasets, models, underlying platform, compliance with internal and external regulations, and to humans involved.
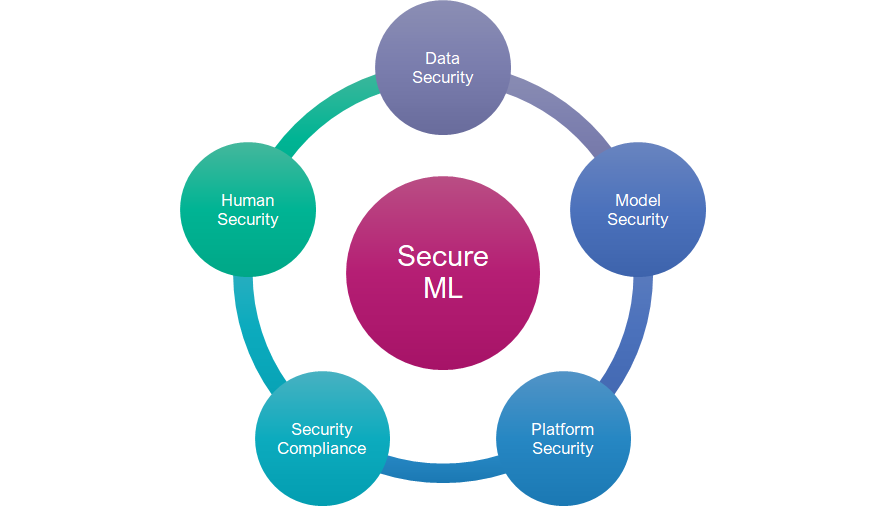
The purpose of this security policy (SecPol) is to provide a framework for ensuring the security and privacy of machine learning (ML) systems within the organization. This policy outlines activities, responsibilities, and guidelines to protect ML models, data, and infrastructure from unauthorized access, malicious attacks, and privacy breaches.
Available at ML Security Policy with ML Security Requirements and ML Security Guidelines
Machine Learning Privacy-Preserving Techniques
Learn about cutting-edge privacy-preserving techniques for machine learning including Differential Privacy, Federated Learning, Homomorphic Encryption, Secure Multi-Party Computation (SMPC), and Privacy-Preserving Data Synthesis in this comprehensive GitHub repository. Explore how these methods safeguard sensitive data while enabling collaborative analysis and model training.
Available at ML privacy-preserving techniques
Tools for Securing Machine Learning
Discover a comprehensive collection of 40+ open-source security tools specifically curated for securing machine learning systems across the entire ML lifecycle. This curated list covers critical security domains including:
- Threat Modeling & Code Security: AI system threat modeling, source code quality analysis, and third-party library vulnerability scanning
- Adversarial Security: Attack and defense tools, backdoor detection, vulnerability benchmarking, and model robustness testing
- LLM Security: Specialized vulnerability scanners and robustness assessment tools for Large Language Models
- Privacy & Compliance: Differential privacy libraries, privacy risk quantification, and compliance toolkits
- Bias & Fairness: Detection and mitigation tools for ensuring fairness in ML models
- Model Explainability: Interpretability frameworks for understanding model predictions and decisions
- Data Quality & Validation: Tools for data validation, label error detection, and quality profiling
- Monitoring & Drift Detection: Continuous model validation, data drift detection, and post-deployment monitoring
- Data Version Control: Version control systems for ML datasets and experiment tracking
Each tool is carefully categorized and includes direct links to repositories, making it easy to integrate security best practices into your ML workflow. Whether you're securing Jupyter notebooks, scanning models for unsafe code, or implementing privacy-preserving techniques, this comprehensive toolkit provides essential resources for robust ML security.
Available at ML security tools
Security Threats to Machine Learning
Available at ML Security Threats
Presentation on ML Security Risks, Policy, Tools, Privacy techniques and more
- Conference: OWASP LASCON 2024
- Agenda: ML lifecycle/workflow, AI for Cyber vs Cyber for AI, Cyber Attacks, Risks, Threats, Thales Security Framework, Recommendations and more.
You can access the presentation deck (PDF) at View Documentation (PDF) and other interesting documents for your reading.
License

This project is licensed under the Creative Commons Attribution-NoDerivs 4.0 International (CC BY-ND 4.0) License. You can view the full license text here.
Project Contacts
For further information or to contribute to this project, you can reach out to the following contacts:
- Project Leader and Key contributor: Viswanath S Chirravuri
LinkedIn
関連プロジェクトを探す
trimstray/the-book-of-secret-knowledge
インスピレーションを与えるリスト、マニュアル、チートシート、ブログ、ハック、ワンライナー、CLI/Web ツールなどを集めたコレクション。
257,871 スターHack-with-Github/Awesome-Hacking
ハッカー、ペンテスター、セキュリティ研究者向けのさまざまな Awesome リスト集。
125,254 スターswisskyrepo/PayloadsAllTheThings
Web アプリケーションセキュリティおよびペネトレーションテスト/CTF 向けの、実用的なペイロードとバイパスの一覧。
82,583 スターcaddyserver/caddy
高速で拡張しやすい、マルチプラットフォーム対応の HTTP/1-2-3 Web サーバー。自動 HTTPS に対応
78,959 スター