
google/oss-fuzz
google/oss-fuzz has 12,950 GitHub stars and 2,996 forks. GitHot measured +1 stars in 24 hours and +23 in 7 days. Last checked 2026-11-14 00:12 UTC. Last push 2026-11-13.
Progression mesurée des étoiles
- in 24h
- +1
- in 7 days
- +23
- in 15 days
- Historique en cours
- in 1 month
- Historique en cours
Variations nettes sur des périodes qui se chevauchent, pas des totaux quotidiens. Les mesures absentes restent vides. Les étoiles indiquent l’intérêt, pas la qualité.
À propos
OSS-Fuzz – fuzzing continu pour les logiciels libres.
SécuritéREADME.md
OriginalOSS-Fuzz: Continuous Fuzzing for Open Source Software
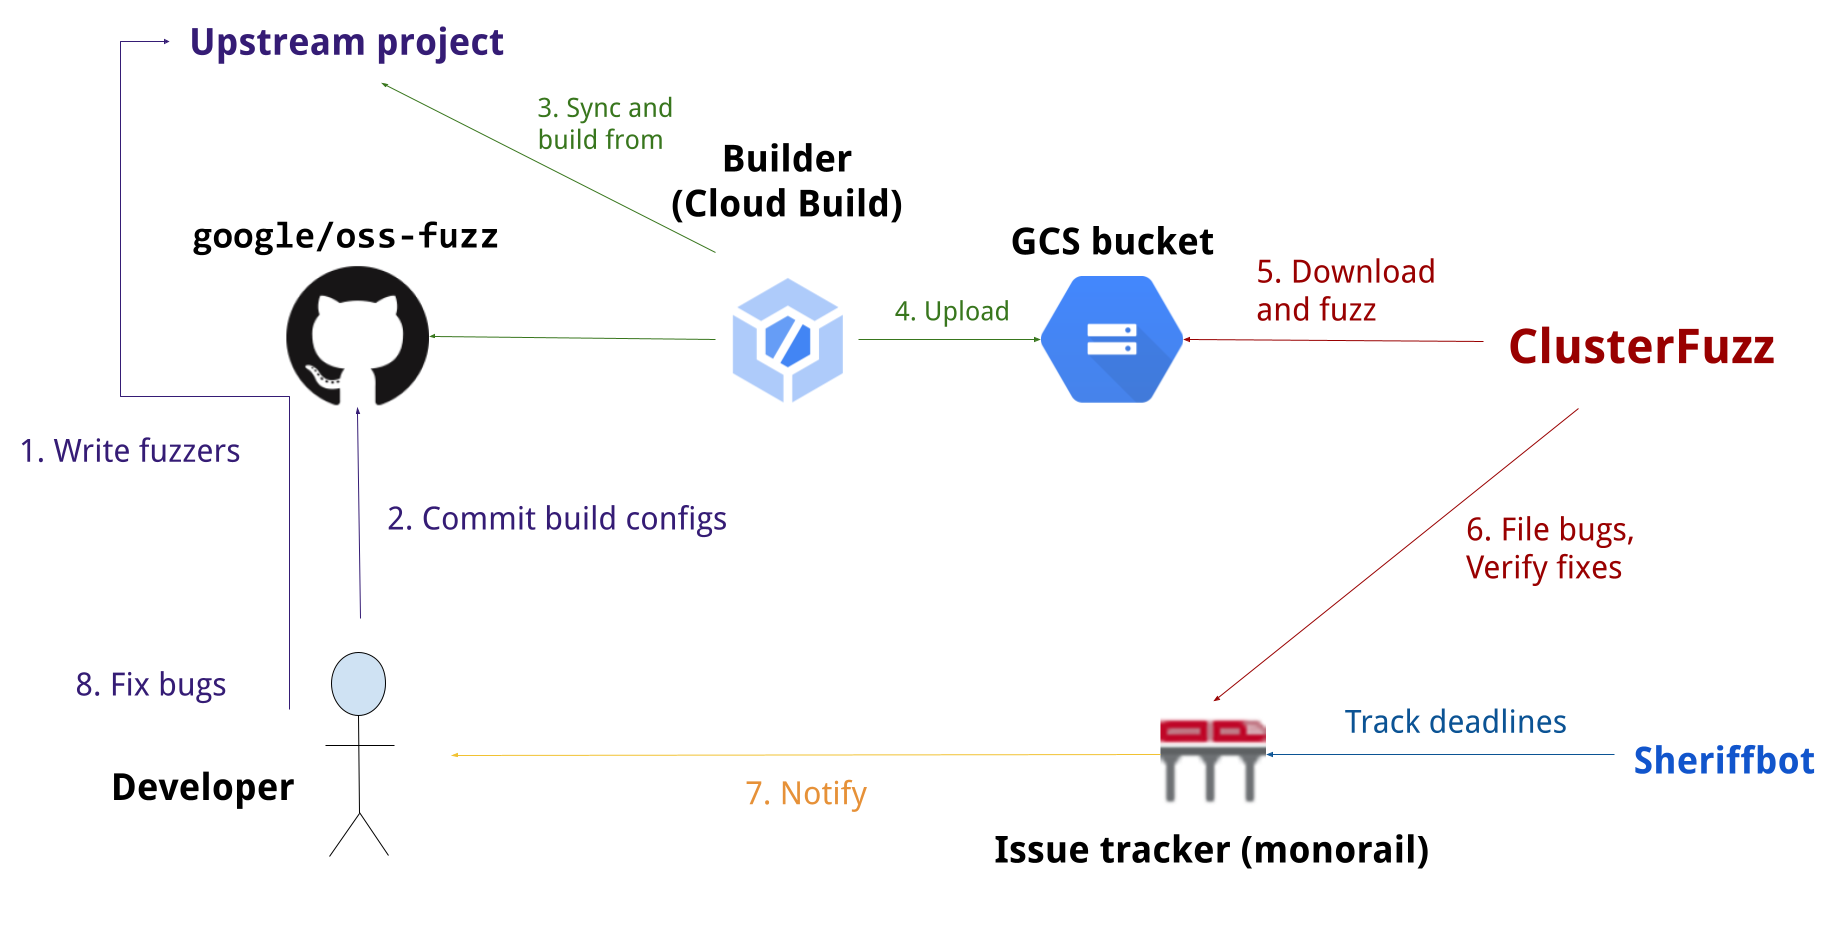
Fuzz testing is a well-known technique for uncovering programming errors in software. Many of these detectable errors, like buffer overflow, can have serious security implications. Google has found thousands of security vulnerabilities and stability bugs by deploying guided in-process fuzzing of Chrome components, and we now want to share that service with the open source community.
In cooperation with the Core Infrastructure Initiative and the OpenSSF, OSS-Fuzz aims to make common open source software more secure and stable by combining modern fuzzing techniques with scalable, distributed execution. Projects that do not qualify for OSS-Fuzz (e.g. closed source) can run their own instances of ClusterFuzz or ClusterFuzzLite.
We support the libFuzzer, AFL++, and Honggfuzz fuzzing engines in combination with Sanitizers, as well as ClusterFuzz, a distributed fuzzer execution environment and reporting tool.
Currently, OSS-Fuzz supports C/C++, Rust, Go, Python, Java/JVM, JavaScript and Lua code. Other languages supported by LLVM may work too. OSS-Fuzz supports fuzzing x86_64 and i386 builds.
Overview
Documentation
Read our detailed documentation to learn how to use OSS-Fuzz.
Trophies
As of May 2025, OSS-Fuzz has helped identify and fix over 13,000 vulnerabilities and 50,000 bugs across 1,000 projects.
Blog posts
- 2024-11-20 - Leveling Up Fuzzing: Finding more vulnerabilities with AI
- 2023-08-16 - AI-Powered Fuzzing: Breaking the Bug Hunting Barrier
- 2023-02-01 - Taking the next step: OSS-Fuzz in 2023
- 2022-09-08 - Fuzzing beyond memory corruption: Finding broader classes of vulnerabilities automatically
- 2021-12-16 - Improving OSS-Fuzz and Jazzer to catch Log4Shell
- 2021-03-10 - Fuzzing Java in OSS-Fuzz
- 2020-12-07 - Improving open source security during the Google summer internship program
- 2020-10-09 - Fuzzing internships for Open Source Software
- 2018-11-06 - A New Chapter for OSS-Fuzz
- 2017-05-08 - OSS-Fuzz: Five months later, and rewarding projects
- 2016-12-01 - Announcing OSS-Fuzz: Continuous fuzzing for open source software
Explorer des projets similaires
trimstray/the-book-of-secret-knowledge
Une collection de listes inspirantes, de manuels, d’antisèches, de blogs, d’astuces, de commandes en une ligne, d’outils CLI et web, et plus encore.
258,285 étoilesHack-with-Github/Awesome-Hacking
Une collection de diverses listes awesome pour les hackers, les pentesters et les chercheurs en sécurité.
125,454 étoilesswisskyrepo/PayloadsAllTheThings
Une liste de payloads et de méthodes de contournement utiles pour la sécurité des applications web et le pentest/CTF.
82,661 étoilescaddyserver/caddy
Serveur web HTTP/1-2-3 rapide, extensible et multiplateforme, avec HTTPS automatique
79,027 étoiles