
ThalesGroup/secure-ml
ThalesGroup/secure-ml has 26 GitHub stars and 6 forks. GitHot measured 0 stars in 24 hours and 0 in 7 days. Last checked 2026-11-11 07:24 UTC. Last push 2026-08-26.
Comment ces chiffres sont mesurés
Explore ThalesGroup's comprehensive framework for secure machine learning systems on this repository. Developed by Thales experts, this framework encompasses essential security requirements, guidelines, tools, and privacy recommendations tailored specifically for machine learning applications.
Progression mesurée des étoiles
- in 24h
- 0
- in 7 days
- 0
- in 15 days
- Mise à jour retardée
- in 1 month
- Mise à jour retardée
Variations nettes sur des périodes qui se chevauchent, pas des totaux quotidiens. Les mesures absentes restent vides. Les étoiles indiquent l’intérêt, pas la qualité.
README.md
OriginalThis repository provides a wealth of information on securing machine learning projects, including, but not limited to, the following items.
Table of Contents
- Security Policy for Machine Learning Systems
- Machine Learning Privacy-Preserving Techniques
- Tools for Securing Machine Learning
- Security Threats to Machine Learning
- ML Security Regulations and Standards
- Agentic AI Threat Comparison
- Agentic AI Lifecycle
Security Policy for Machine Learning Systems
A ThalesGroup policy framework to secure machine learning datasets, models, underlying platform, compliance with internal and external regulations, and to humans involved.
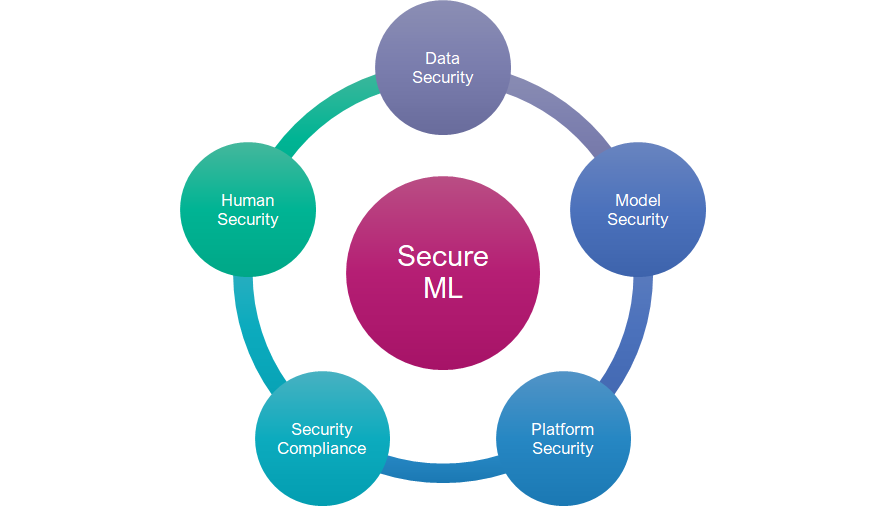
The purpose of this security policy (SecPol) is to provide a framework for ensuring the security and privacy of machine learning (ML) systems within the organization. This policy outlines activities, responsibilities, and guidelines to protect ML models, data, and infrastructure from unauthorized access, malicious attacks, and privacy breaches.
Available at ML Security Policy with ML Security Requirements and ML Security Guidelines
Machine Learning Privacy-Preserving Techniques
Learn about cutting-edge privacy-preserving techniques for machine learning including Differential Privacy, Federated Learning, Homomorphic Encryption, Secure Multi-Party Computation (SMPC), and Privacy-Preserving Data Synthesis in this comprehensive GitHub repository. Explore how these methods safeguard sensitive data while enabling collaborative analysis and model training.
Available at ML privacy-preserving techniques
Tools for Securing Machine Learning
Discover a comprehensive collection of 40+ open-source security tools specifically curated for securing machine learning systems across the entire ML lifecycle. This curated list covers critical security domains including:
- Threat Modeling & Code Security: AI system threat modeling, source code quality analysis, and third-party library vulnerability scanning
- Adversarial Security: Attack and defense tools, backdoor detection, vulnerability benchmarking, and model robustness testing
- LLM Security: Specialized vulnerability scanners and robustness assessment tools for Large Language Models
- Privacy & Compliance: Differential privacy libraries, privacy risk quantification, and compliance toolkits
- Bias & Fairness: Detection and mitigation tools for ensuring fairness in ML models
- Model Explainability: Interpretability frameworks for understanding model predictions and decisions
- Data Quality & Validation: Tools for data validation, label error detection, and quality profiling
- Monitoring & Drift Detection: Continuous model validation, data drift detection, and post-deployment monitoring
- Data Version Control: Version control systems for ML datasets and experiment tracking
Each tool is carefully categorized and includes direct links to repositories, making it easy to integrate security best practices into your ML workflow. Whether you're securing Jupyter notebooks, scanning models for unsafe code, or implementing privacy-preserving techniques, this comprehensive toolkit provides essential resources for robust ML security.
Available at ML security tools
Security Threats to Machine Learning
Available at ML Security Threats
Presentation on ML Security Risks, Policy, Tools, Privacy techniques and more
- Conference: OWASP LASCON 2024
- Agenda: ML lifecycle/workflow, AI for Cyber vs Cyber for AI, Cyber Attacks, Risks, Threats, Thales Security Framework, Recommendations and more.
You can access the presentation deck (PDF) at View Documentation (PDF) and other interesting documents for your reading.
License

This project is licensed under the Creative Commons Attribution-NoDerivs 4.0 International (CC BY-ND 4.0) License. You can view the full license text here.
Project Contacts
For further information or to contribute to this project, you can reach out to the following contacts:
- Project Leader and Key contributor: Viswanath S Chirravuri
LinkedIn
Explorer des projets similaires
trimstray/the-book-of-secret-knowledge
Une collection de listes inspirantes, de manuels, d’antisèches, de blogs, d’astuces, de commandes en une ligne, d’outils CLI et web, et plus encore.
257,807 étoilesHack-with-Github/Awesome-Hacking
Une collection de diverses listes awesome pour les hackers, les pentesters et les chercheurs en sécurité.
125,254 étoilesswisskyrepo/PayloadsAllTheThings
Une liste de payloads et de méthodes de contournement utiles pour la sécurité des applications web et le pentest/CTF.
82,583 étoilescaddyserver/caddy
Serveur web HTTP/1-2-3 rapide, extensible et multiplateforme, avec HTTPS automatique
78,959 étoiles