
OWASP/joomscan
OWASP/joomscan has 1,196 GitHub stars and 249 forks. GitHot measured 0 stars in 24 hours and 0 in 7 days. Last checked 2026-11-13 03:33 UTC. Last push 2024-09-11.
Comment ces chiffres sont mesurés
OWASP Joomla Vulnerability Scanner Project https://www.secologist.com/
Progression mesurée des étoiles
- in 24h
- 0
- in 7 days
- 0
- in 15 days
- Historique en cours
- in 1 month
- Historique en cours
Variations nettes sur des périodes qui se chevauchent, pas des totaux quotidiens. Les mesures absentes restent vides. Les étoiles indiquent l’intérêt, pas la qualité.
README.md
Original



======
OWASP JoomScan Project
OWASP Joomla! Vulnerability Scanner (JoomScan) is an open source project, developed with the aim of automating the task of vulnerability detection and reliability assurance in Joomla CMS deployments. Implemented in Perl, this tool enables seamless and effortless scanning of Joomla installations, while leaving a minimal footprint with its lightweight and modular architecture. It not only detects known offensive vulnerabilities, but also is able to detect many misconfigurations and admin-level shortcomings that can be exploited by adversaries to compromise the system. Furthermore, OWASP JoomScan provides a user-friendly interface and compiles the final reports in both text and HTML formats for ease of use and minimization of reporting overheads.
OWASP JoomScan is included in Kali Linux distributions.
WHY OWASP JOOMSCAN ?
Automated ...
*Version enumerator
*Vulnerability enumerator (based on version)
*Components enumerator (1209 most popular by default)
*Components vulnerability enumerator (based on version)(+1030 exploit)
*Firewall detector
*Reporting to Text & HTML output
*Finding common log files
*Finding common backup files
INSTALL
git clone https://github.com/rezasp/joomscan.git
cd joomscan
perl joomscan.pl
For Docker installation and usage
# Build the docker image
docker build -t rezasp/joomscan .

# Run a new docker container with reports directory mounted at the host
docker run -it -v /path/to/reports:/home/joomscan/reports --name joomscan_cli rezasp/joomscan

# For accessing the docker container you can run the following command
docker run -it -v /path/to/reports:/home/joomscan/reports --name joomscan_cli --entrypoint /bin/bash rezasp/joomscan
JOOMSCAN ARGUMENTS
Usage:	joomscan.pl [options]

--url | -u <URL>                |   The Joomla URL/domain to scan.
--enumerate-components | -ec    |   Try to enumerate components.

--cookie <String>               |   Set cookie.
--user-agent | -a <user-agent>  |   Use the specified User-Agent.
--random-agent | -r             |   Use a random User-Agent.
--timeout <time-out>            |   set timeout.
--about                         |   About Author
--update                        |   Update to the latest version.
--help | -h                     |   This help screen.
--version                       |   Output the current version and exit.
OWASP JOOMSCAN USAGE EXAMPLES
Do default checks...
perl joomscan.pl --url www.example.com
or
perl joomscan.pl -u www.example.com
Enumerate installed components...
perl joomscan.pl --url www.example.com --enumerate-components
or
perl joomscan.pl -u www.example.com --ec
Set cookie
perl joomscan.pl --url www.example.com --cookie "test=demo;"
Set user-agent
perl joomscan.pl --url www.example.com --user-agent "Googlebot/2.1 (+http://www.googlebot.com/bot.html)"
or
perl joomscan.pl -u www.example.com -a "Googlebot/2.1 (+http://www.googlebot.com/bot.html)"
Set random user-agent
perl joomscan.pl -u www.example.com --random-agent
or
perl joomscan.pl --url www.example.com -r
Set proxy
perl joomscan.pl --url www.example.com --proxy http://127.0.0.1:8080
or
perl joomscan.pl -u www.example.com --proxy https://127.0.0.1:443
Update Joomscan...
perl joomscan.pl --update
OWASP PAGE
https://www.owasp.org/index.php/Category:OWASP_Joomla_Vulnerability_Scanner_Project
GIT REPOSITORY
https://github.com/rezasp/joomscan
ISSUES
https://github.com/rezasp/joomscan/issues
PROJECT LEADERS
- Mohammad Reza Espargham [ reza[dot]espargham[at]owasp[dot]org ]
- Ali Razmjoo [ ali[dot]razmjoo[at]owasp[dot]org ]
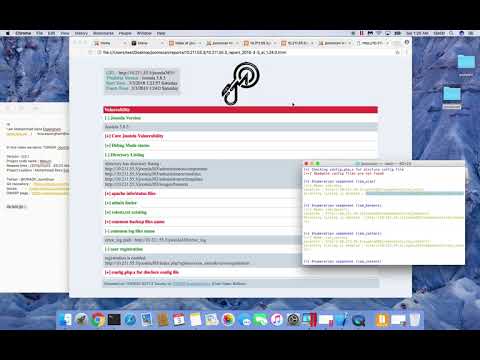
OWASP JoomScan introduction (Youtube)
Explorer des projets similaires
trimstray/the-book-of-secret-knowledge
Une collection de listes inspirantes, de manuels, d’antisèches, de blogs, d’astuces, de commandes en une ligne, d’outils CLI et web, et plus encore.
258,131 étoilesHack-with-Github/Awesome-Hacking
Une collection de diverses listes awesome pour les hackers, les pentesters et les chercheurs en sécurité.
125,360 étoilesswisskyrepo/PayloadsAllTheThings
Une liste de payloads et de méthodes de contournement utiles pour la sécurité des applications web et le pentest/CTF.
82,623 étoilescaddyserver/caddy
Serveur web HTTP/1-2-3 rapide, extensible et multiplateforme, avec HTTPS automatique
79,020 étoiles