
agentsh
canyonroad
411estrellas
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
Encuentra herramientas para detectar vulnerabilidades y proteger sistemas y privacidad.
canyonroad
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

capitalone
What's in your data? Extract schema, statistics and entities from datasets
capitalone
Agentic AI security tool that applies proactive, attacker-first analysis directly to source code.

capitan0n
Offline Android security audit tool. 90+ read-only checks across multiple privilege levels (base, ADB, Shizuku, root), 0–100 score and saved reports. Privacy-oriented, no internet permission, zero telemetry, fully local.

capnspacehook
Automate management of firewall rules for Docker containers

CapSoftware
Add a hacker to your team.

capstone-engine
Capstone es un framework de desensamblado y un desensamblador para ARM, ARM64 (ARMv8), Alpha, BPF, Ethereum VM, HPPA, LoongArch, M68K, M680X, Mips, MOS65XX, PPC, RISC-V(rv32G/rv64G), SH, Sparc, SystemZ, TMS320C64X, TriCore, Webassembly, XCore y X86.

cardano-foundation

privacy voting blockchain node

CaringCaribou
A friendly car security exploration tool for the CAN bus

carrythroughsystems
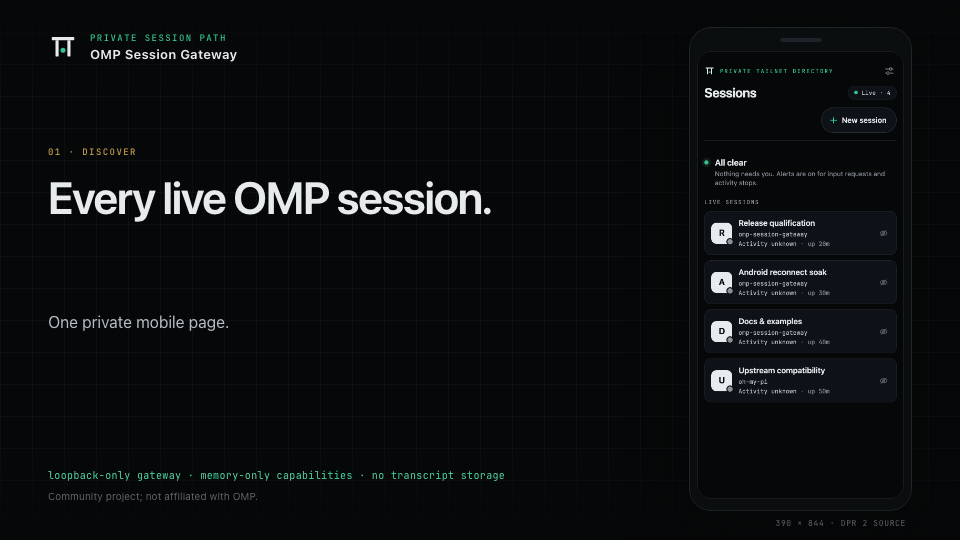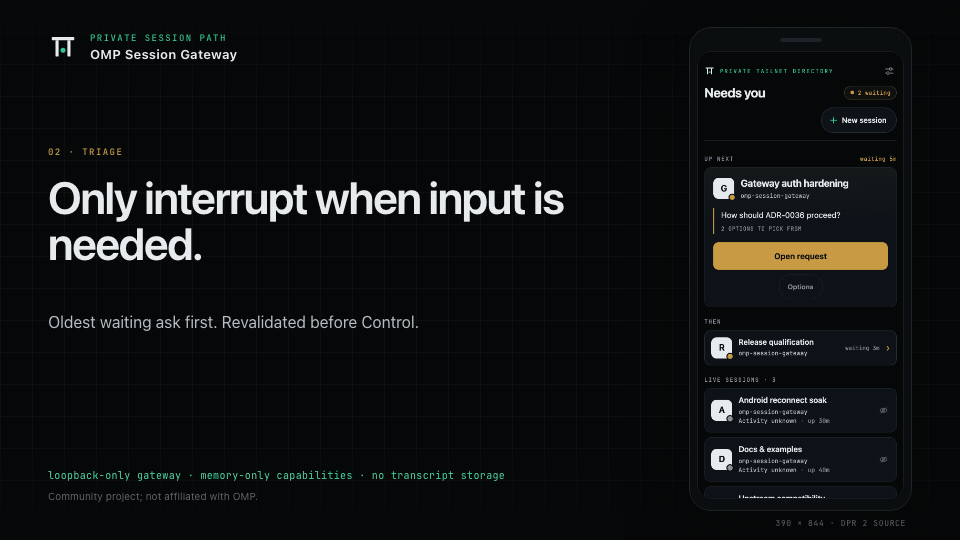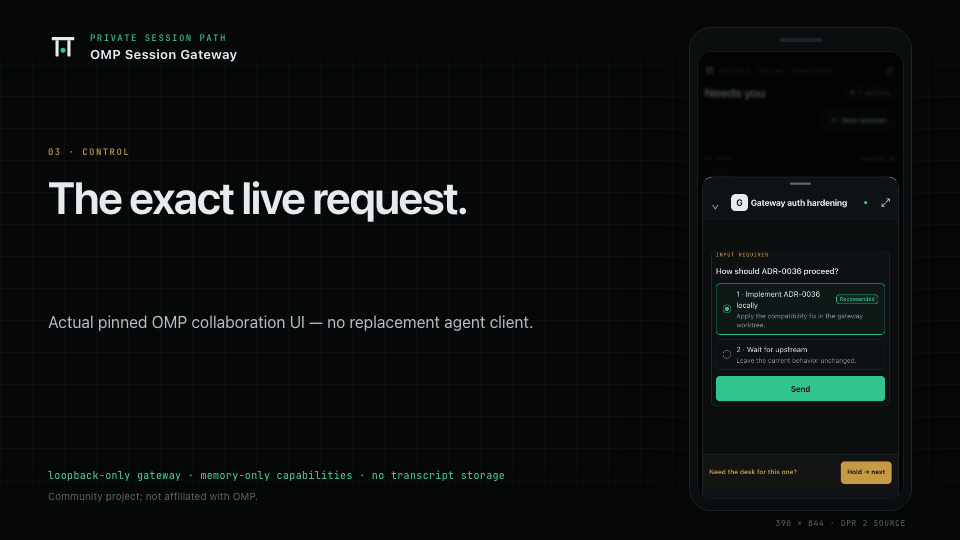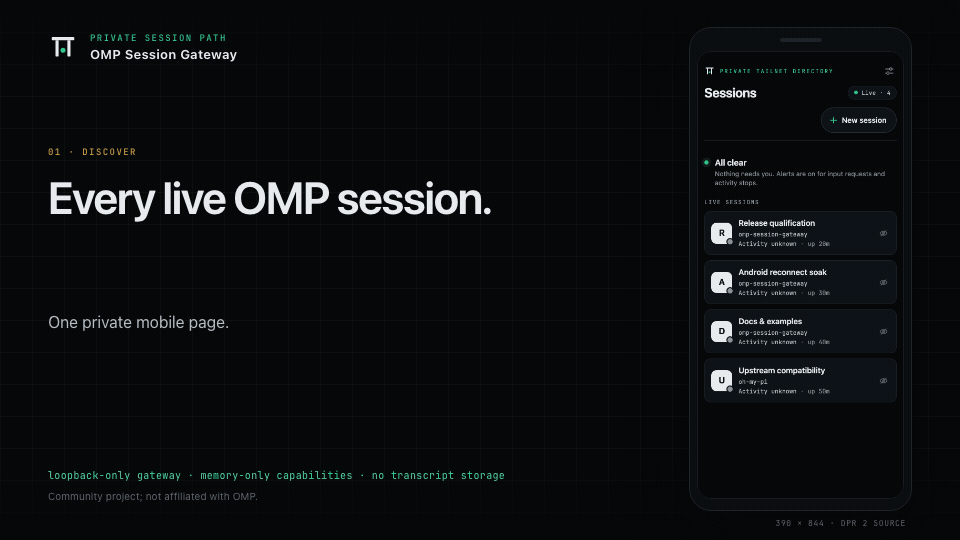
Every live OMP session. One private page, in any modern browser.

cartalyst
A framework agnostic authentication & authorization system.

cashubtc
A Cashu wallet for Android and iOS 🥜🐿️
cashubtc
Chaumian ecash wallet and mint for Bitcoin

caster0x00

Network Security Sniffer

castlabs
Castlabs Electron for Content Security

Casualtek
Building a consolidated RSS feed for articles about cyberattacks

CatchZeng
DingTalk(dingding) 是钉钉机器人的 go 实现。支持 Docker、Jenkinsfile、命令行模式,module 模式,加签安全设置,支持链式语法创建消息,支持文本、链接、Markdown、ActionCard、FeedCard消息类型; DingTalk (dingding) is the go implementation of the DingTalk robot. Support Docker, Jenkinsfile, command line mode, module mode, signature security settings, chain syntax to create messages, support text, link, markdown,ActionCard,FeedCard message types.

CaviraOSS
Akashic is an open-source Palantir alternative for connecting, exploring, and analyzing complex data. Fully self-hosted, privacy-first, and requiring no API keys.

cc1a2b
jshunter is a command-line tool designed for analyzing JavaScript files and extracting endpoints. This tool specializes in identifying sensitive data, such as API endpoints and potential security vulnerabilities, making it an essential resource for and bug bounty hunters and security researchers.
cc1a2b
Pen Hunter is a comprehensive vulnerability scanning tool designed for penetration testers, security researchers and bug bounties. it automates the process of collecting subdomains and URLs and tests them for various vulnerabilities including XSS, SQL Injection, Local File Inclusion, Open Redirect, Server-Side Request Forgery, CSRF, and RCE.

ccelikanil
Another FAFO project: Weaponizing MSI installers for fileless code execution
ccelikanil
A FAFO project: Command execution and data exfiltration of any kind through live streaming platforms

cckuailong
:snowman: Get the User:Password from Chrome(include version < 80 and version > 80)

CDCgov
Template repository with rules, practices, and privacy, license, records notices to help people use the CDCgov GitHub organization.