
otter-sec/rctf has 146 GitHub stars and 36 forks. Star changes are not measured yet. Last checked 2026-11-14 00:38 UTC. Last push 2026-10-23.
Crecimiento de estrellas medido
- in 24h
- Recopilando historial
- in 7 days
- Recopilando historial
- in 15 days
- Recopilando historial
- in 1 month
- Recopilando historial
Cambios netos en períodos que se solapan, no totales diarios. Los datos no disponibles se dejan en blanco. Las estrellas indican interés, no calidad.
Acerca de
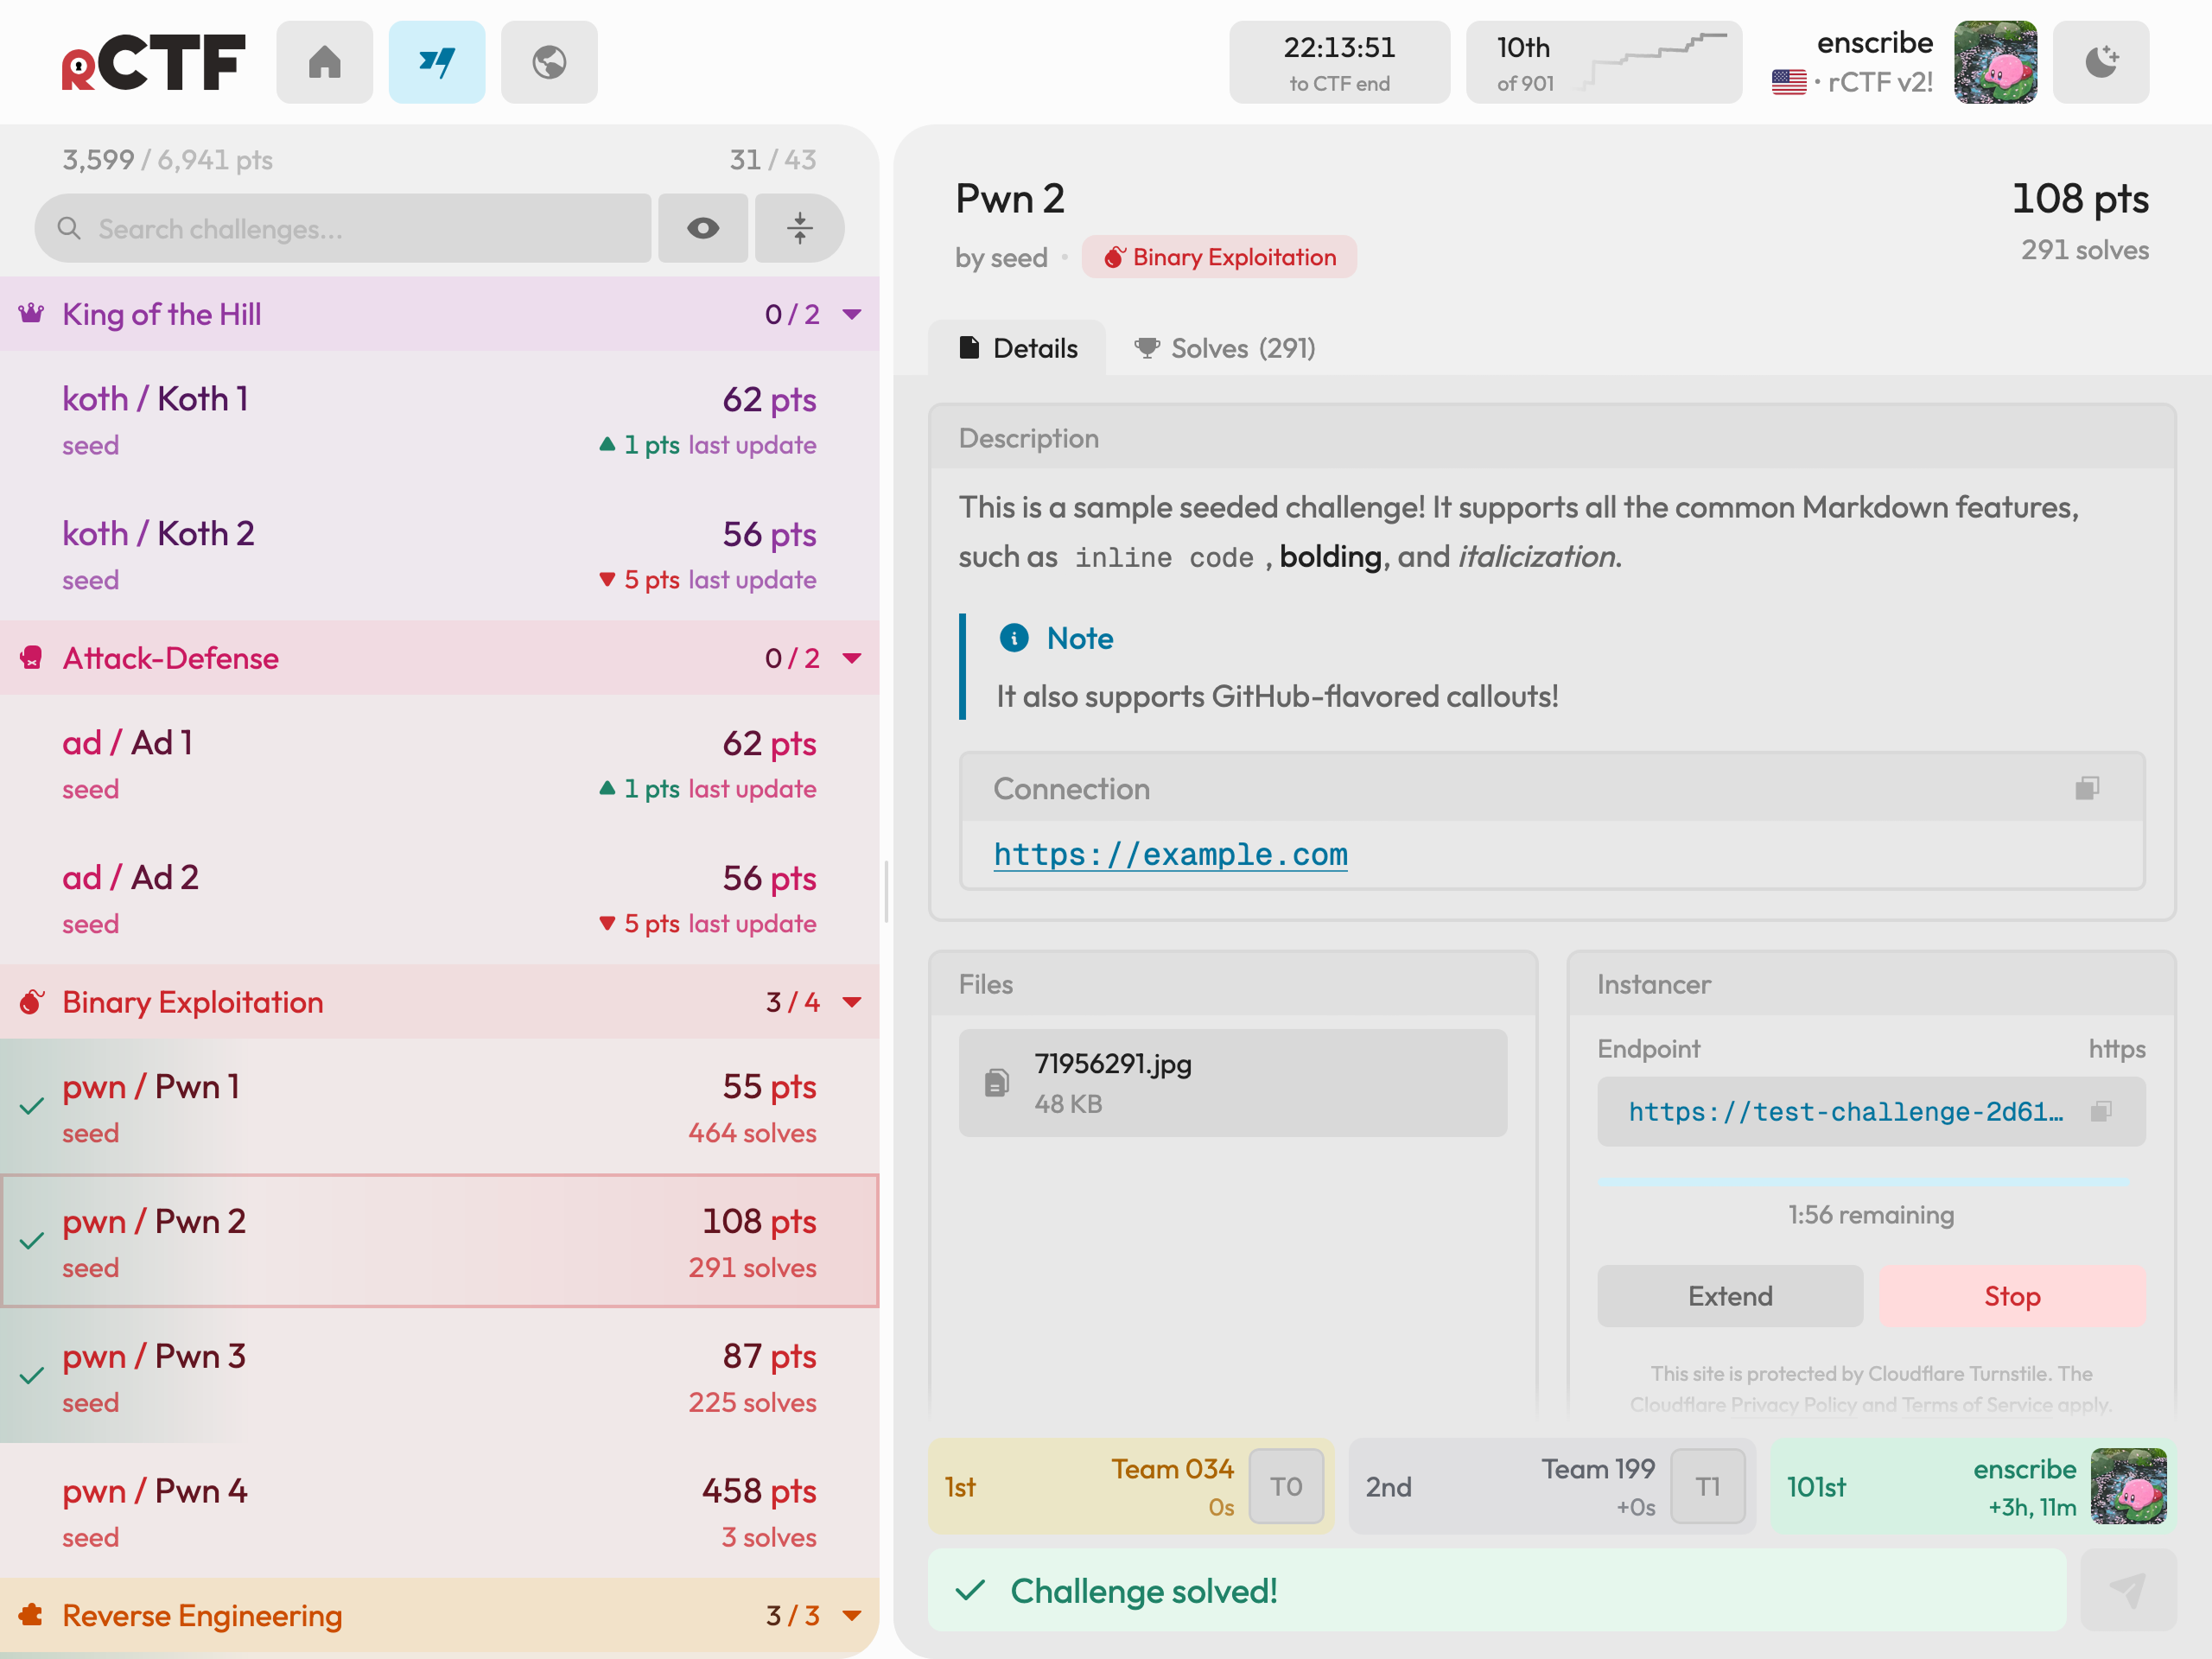
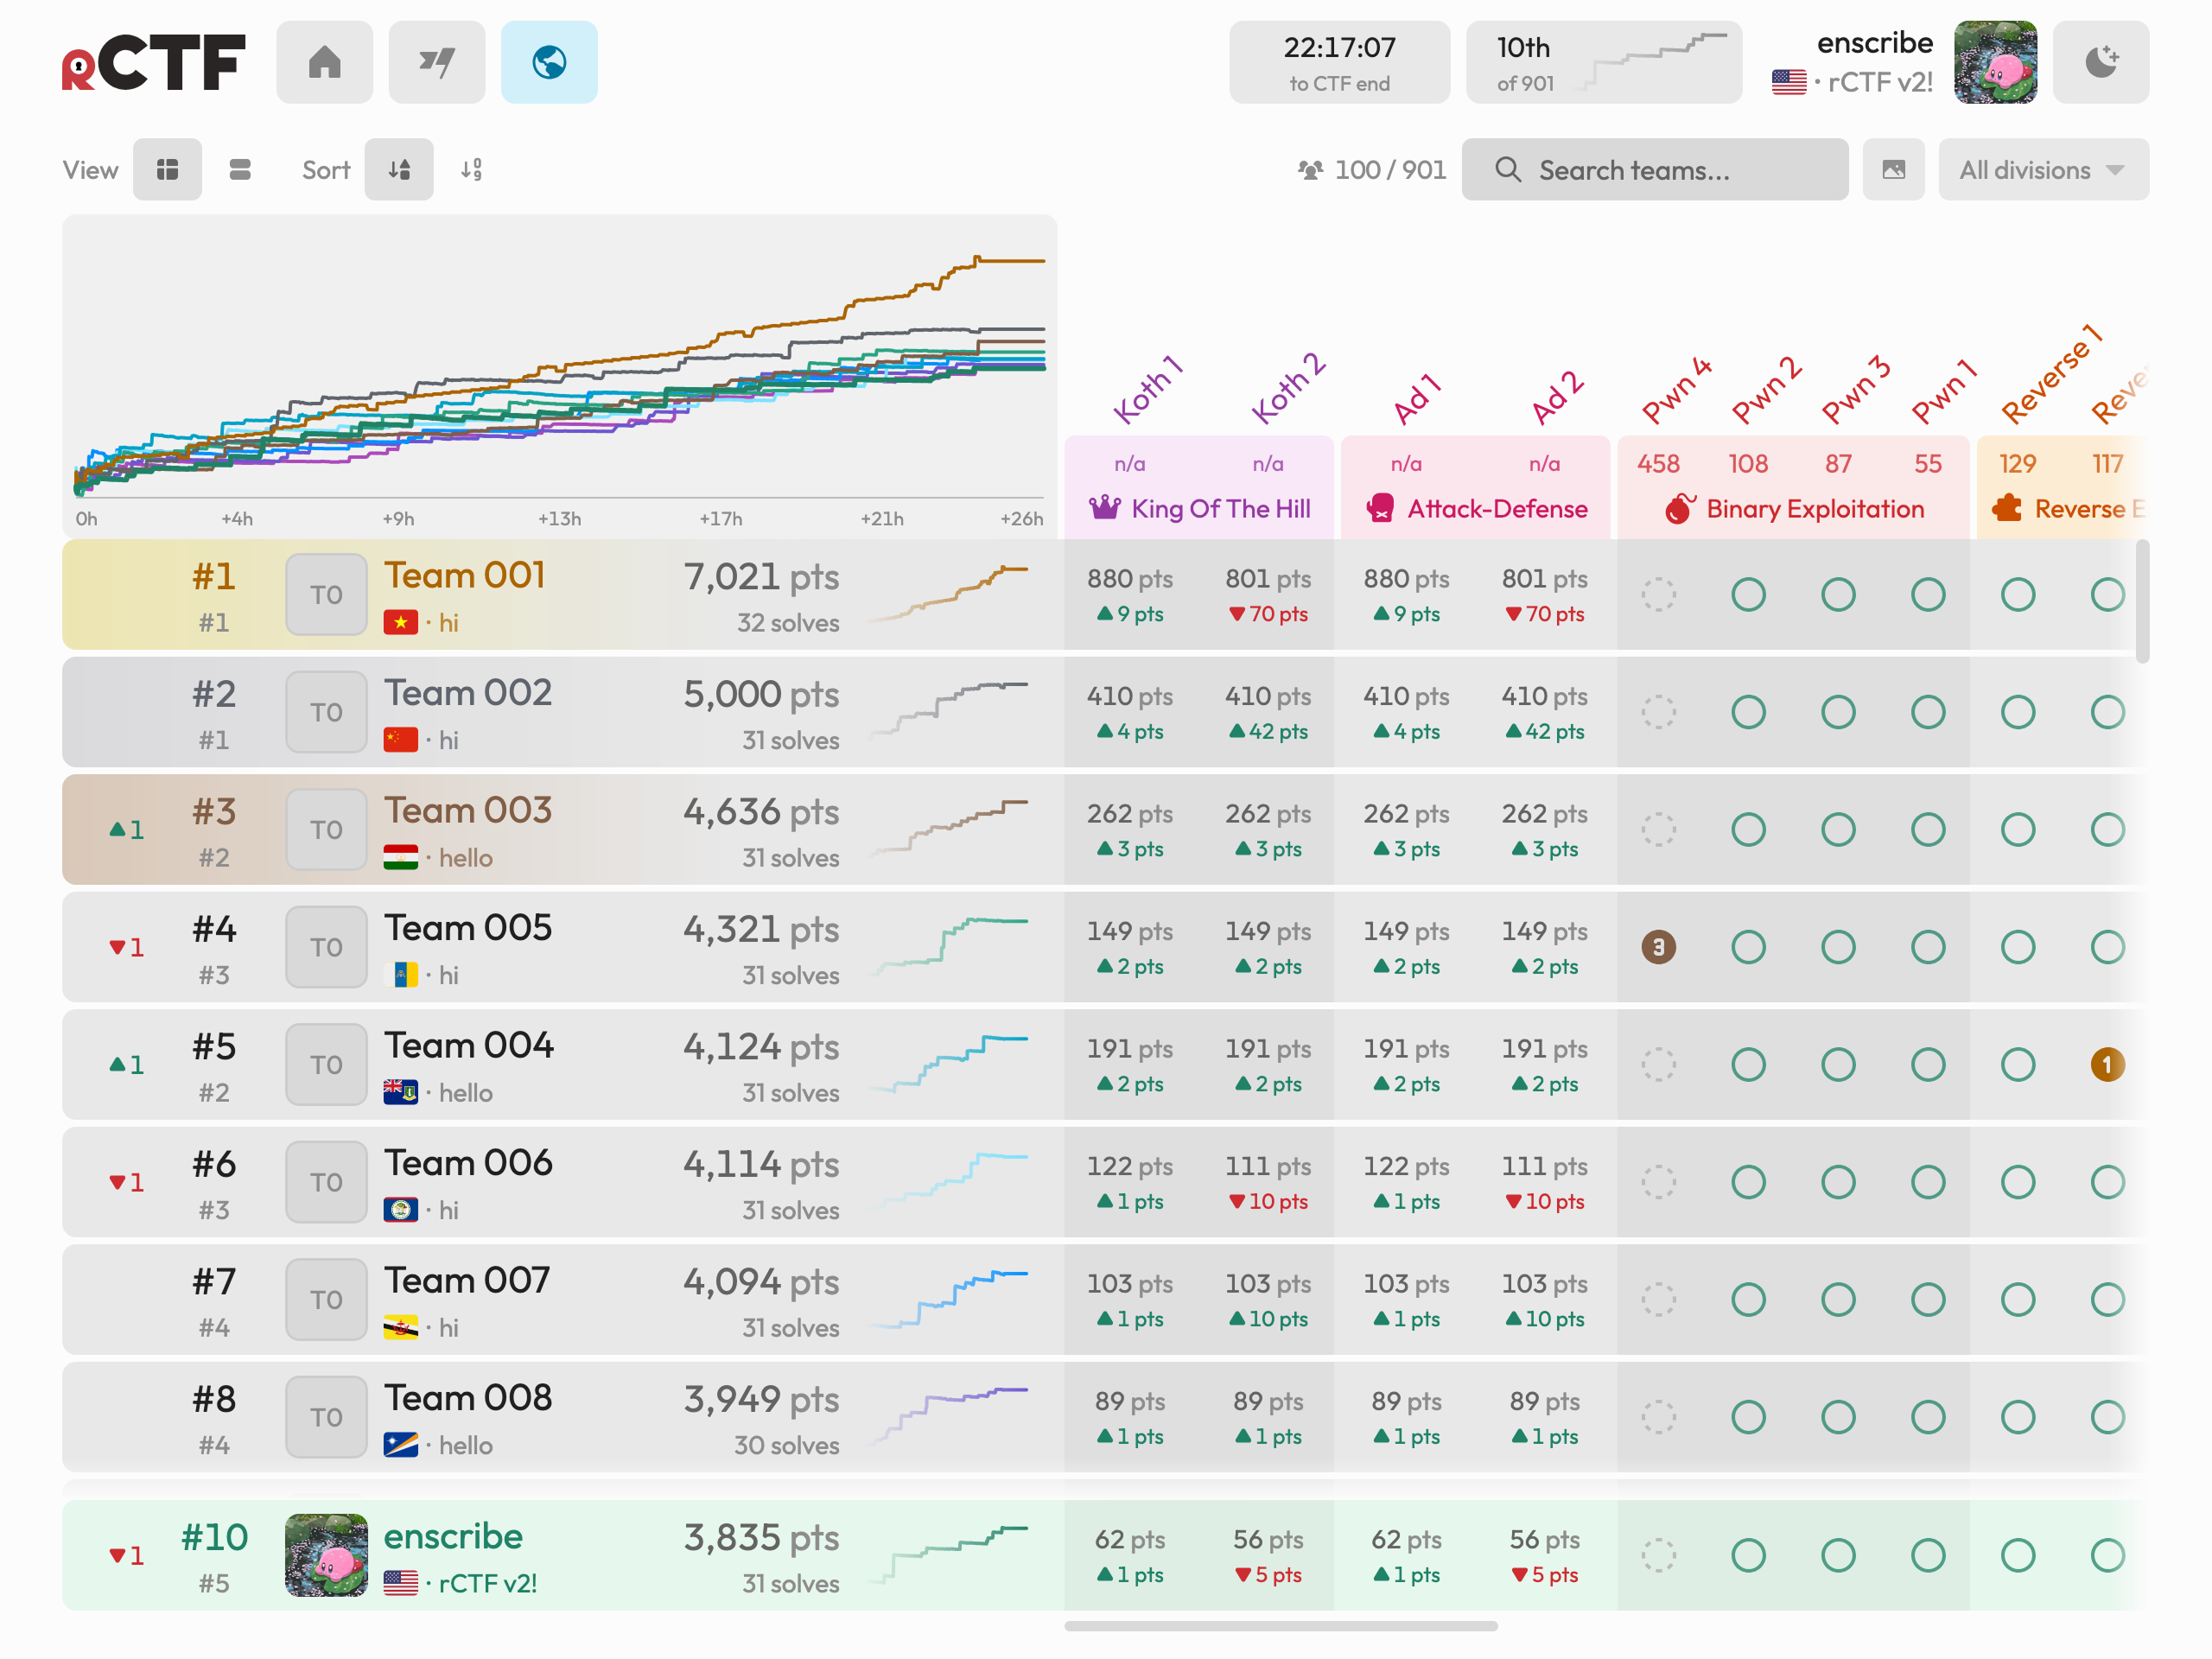
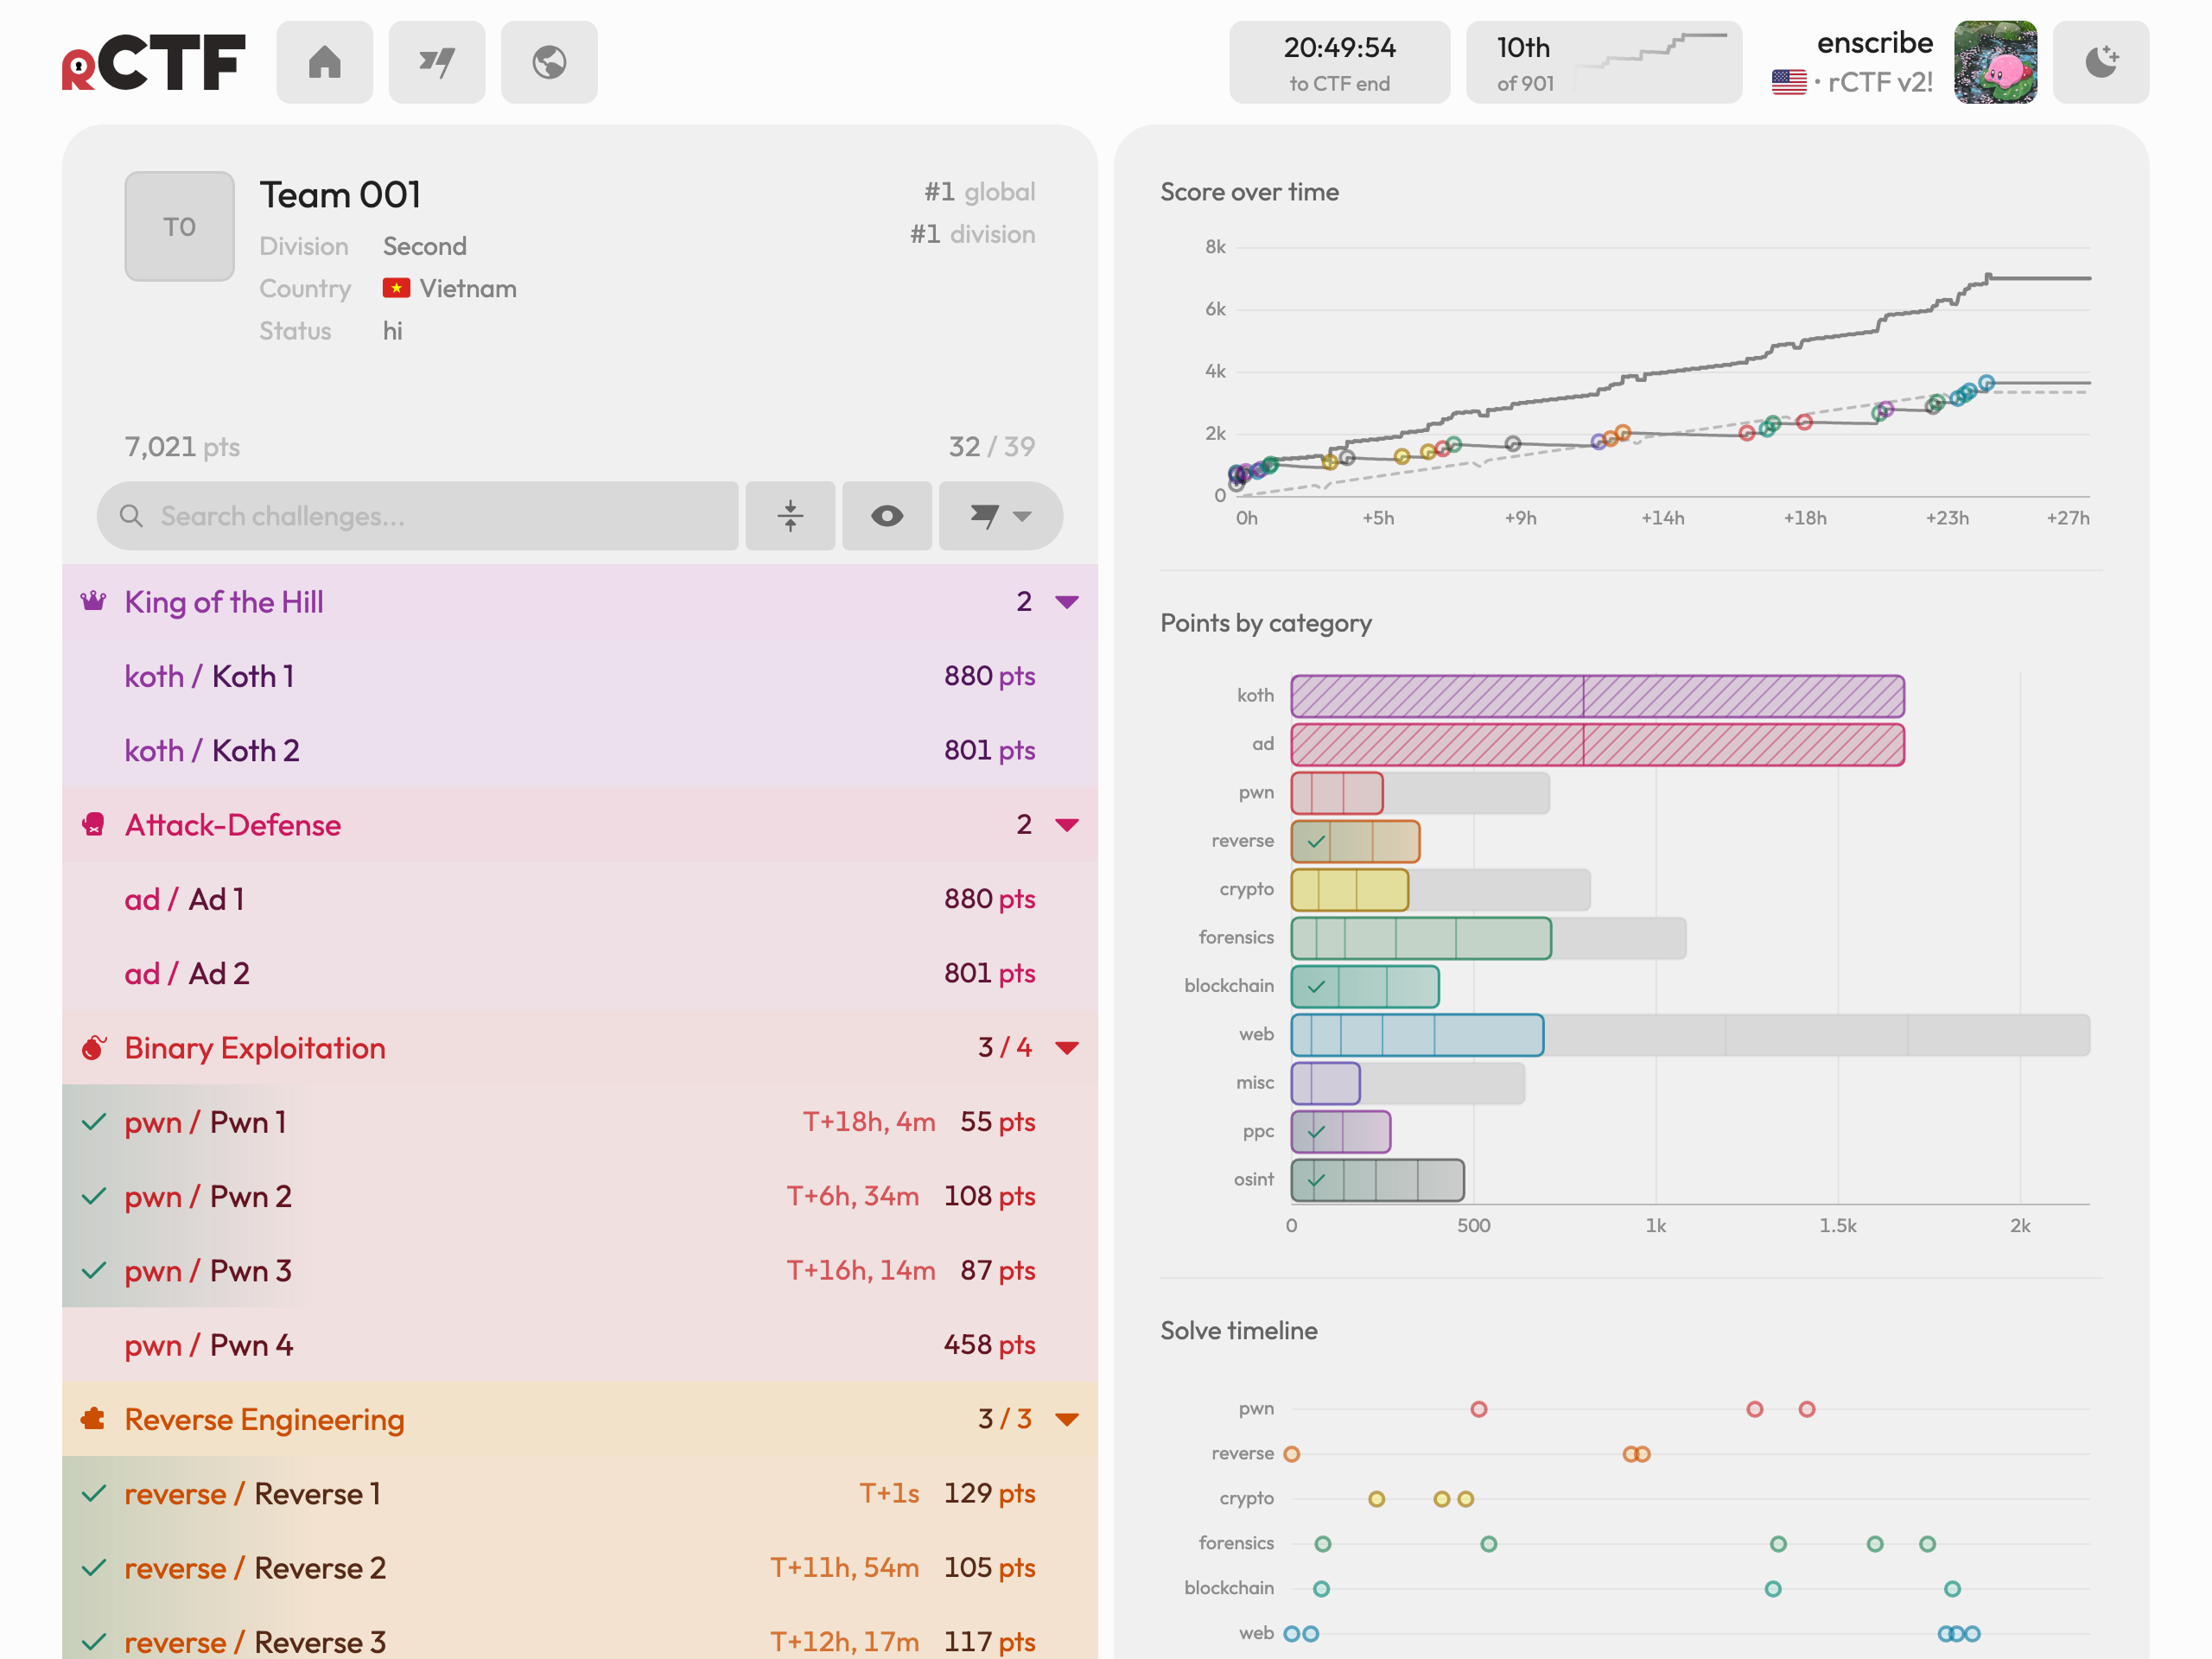
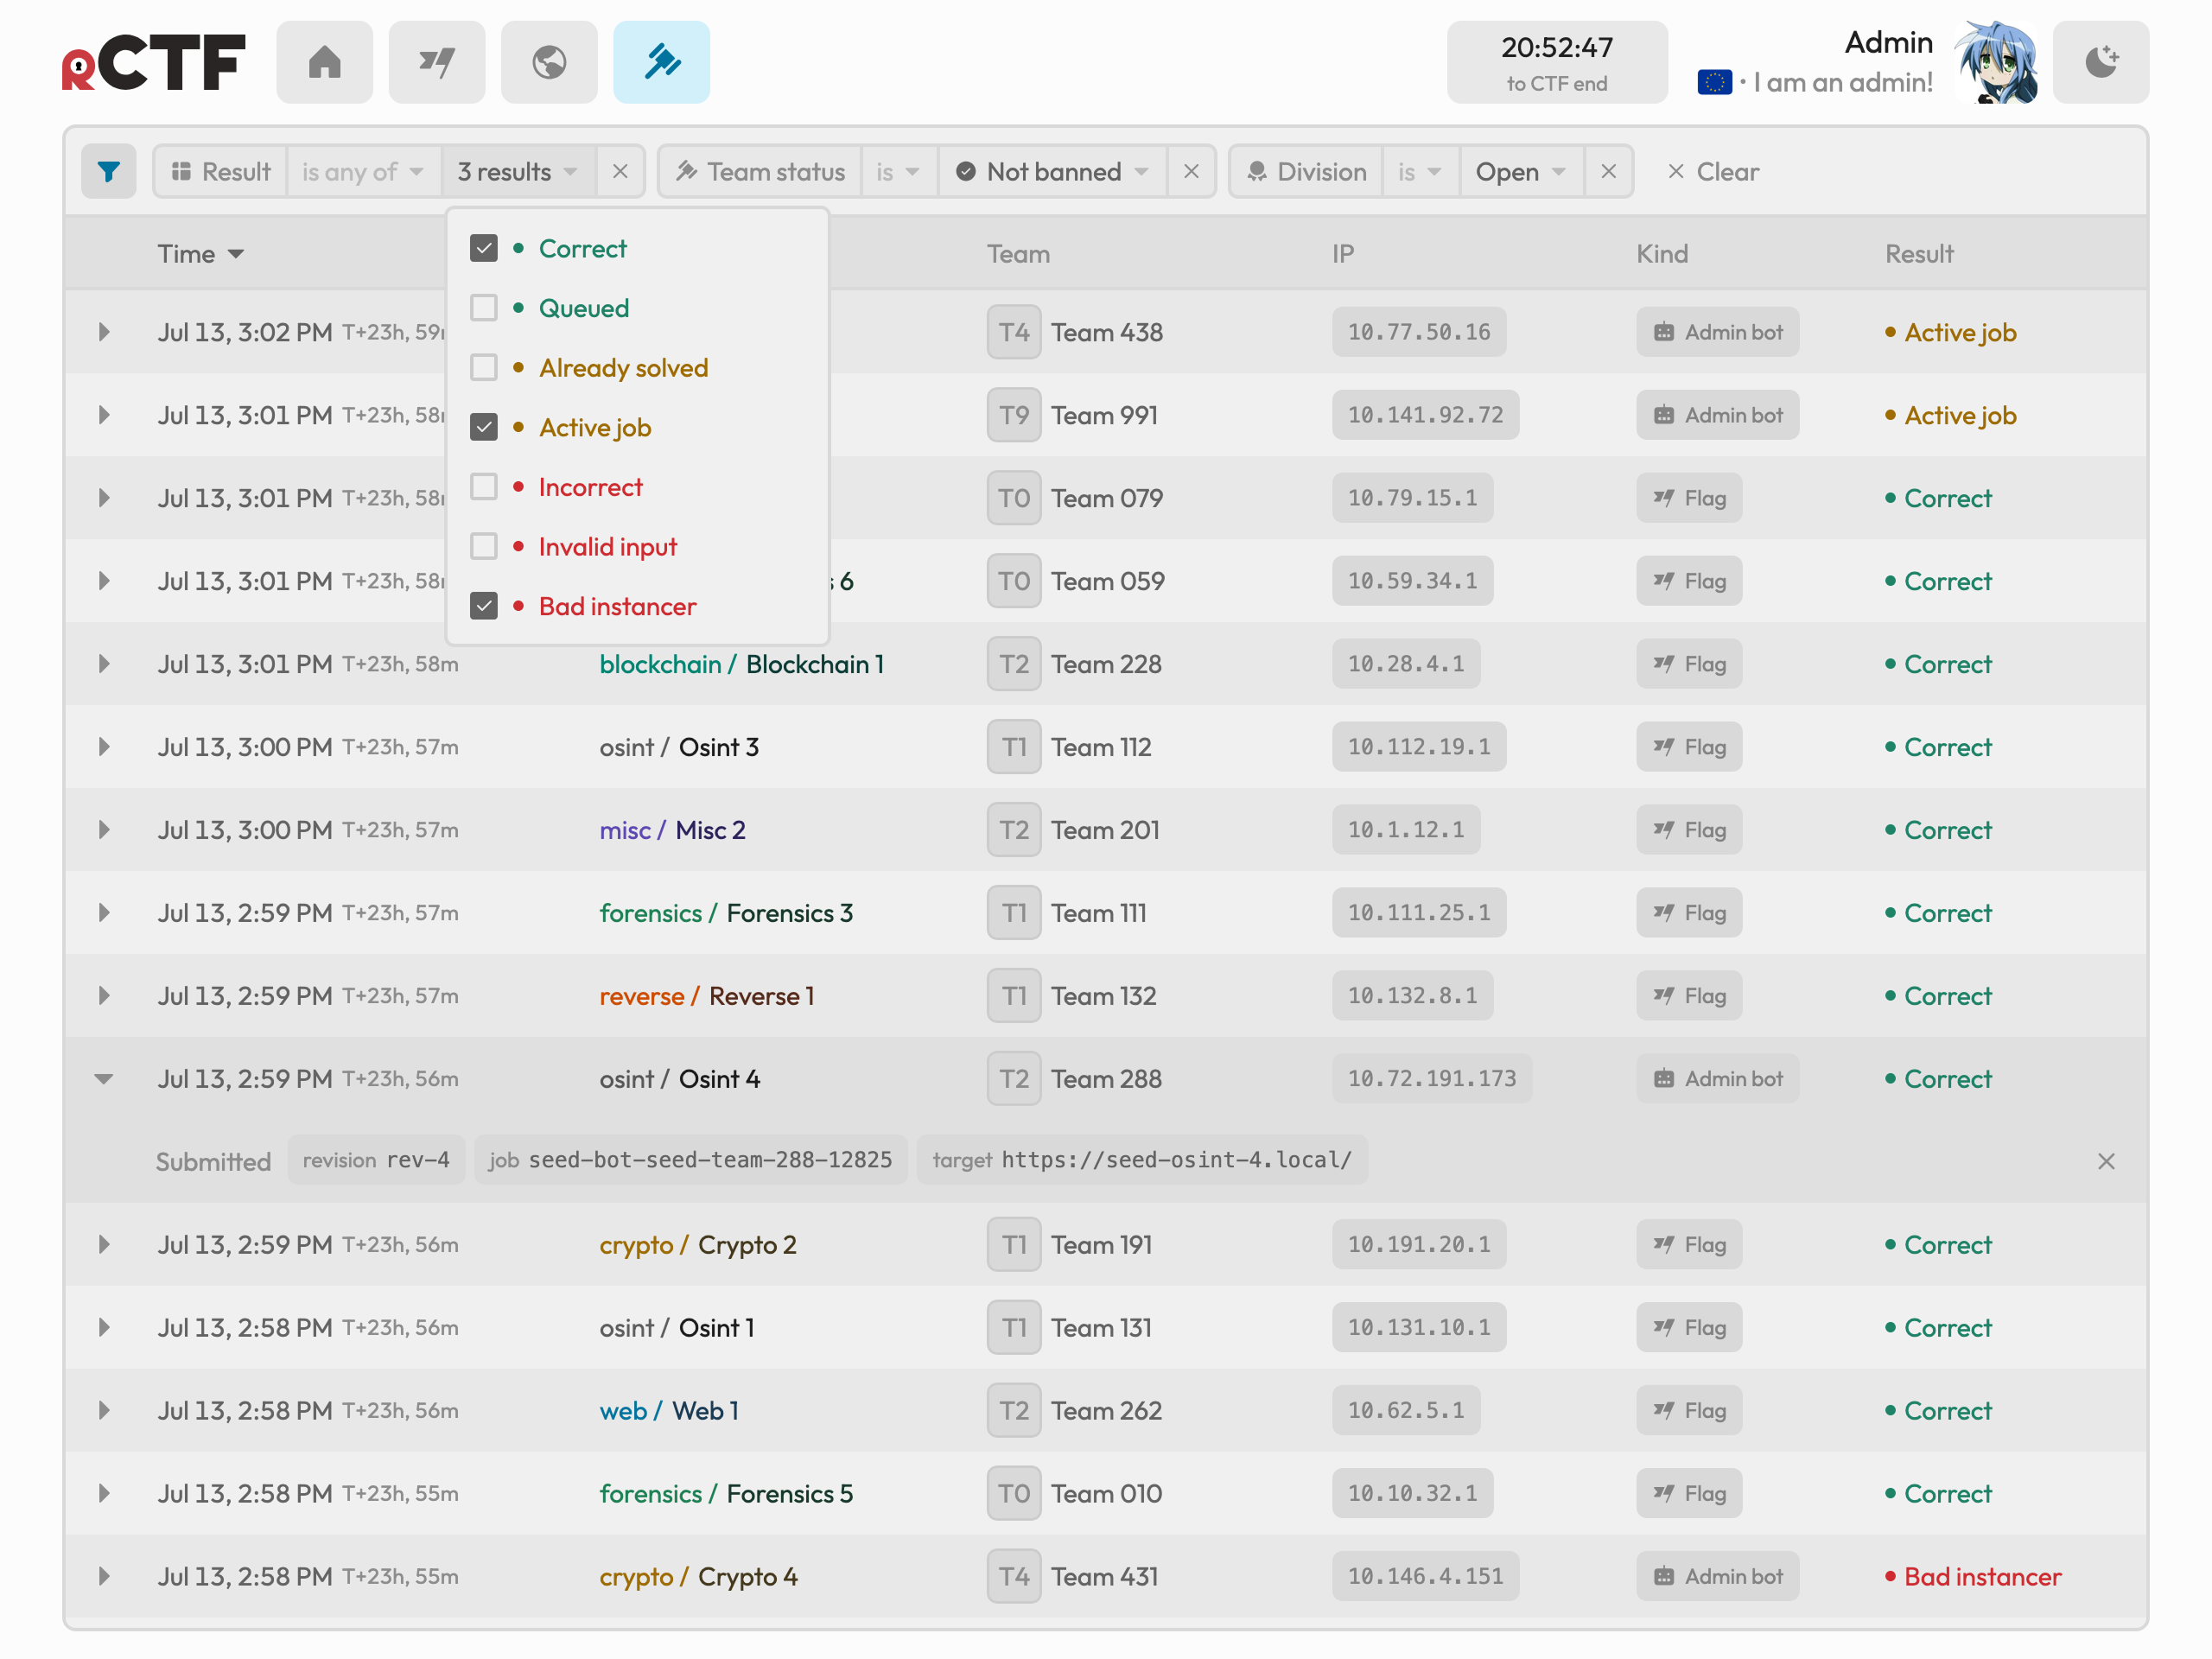
rCTF is a platform for hosting cybersecurity capture-the-flag competitions.
SeguridadREADME.md
Original


rCTF is a platform for hosting cybersecurity capture-the-flag competitions.
rCTF keeps deployment simple without locking organizers into one set of services. The platform runs as a single bundle, and its major integrations use replaceable providers with a common configuration format. An event can use only what it needs and change providers later without rewriting the platform.
To get started with rCTF, visit the documentation. A live demo is also available for viewing. If you need help with rCTF, start a discussion.
 |
 |
|---|---|
 |
 |
Development
rCTF requires Bun v1.0+.
Install dependencies:
bun iStart the development containers:
docker compose -f compose.dev.yml up -dCreate
rctf.d/00-development.yamland enter the following configuration:Open me!
ctfName: rCTF Development
meta:
  description: 'Example rCTF instance'
  imageUrl: 'https://example.com'
homeContent: "A description of your CTF. Markdown supported.\n\n<timer></timer>"

origin: http://127.0.0.1:5173
divisions:
  open: Open
tokenKey: AAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAAA=
startTime: 0
endTime: 99999999999999

database:
  sql:
    host: 127.0.0.1
    port: 5432
    # host: postgres
    user: rctf
    password: DO_NOT_USE_ME
    database: rctf
  redis:
    host: 127.0.0.1
    port: 6379
    # host: redis
    password: DO_NOT_USE_ME
  migrate: before

# email:
#   from: [email protected]
#   provider:
#     name: 'emails/smtp'
#     options:
#       smtpUrl: 'smtp://es3n1n%es3n1n.eu:[email protected]:587'

# ctftime:
#   clientId: 2288
#   clientSecret: secret

# instancers:
#   docker:
#     name: 'instancers/docker'
#     options:
#       authToken: 'changeme!'
#       apiUrl: 'http://tiny-instancer:1337'
# defaultInstancer: docker

# captcha:
#   provider:
#     name: 'captcha/hcaptcha'
#     options:
#       siteKey: 'key'
#       secretKey: 'secret'

# bloodBot:
#   bloodsCount: 1
#   destinations:
#     - provider:
#         name: 'messages/discord'
#         options:
#           url: 'webhook-url'
#     - provider:
#         name: 'messages/telegram'
#         options:
#           botToken: 'bot-token'
#           chatId: 1337

# adminBot:
#   provider:
#     name: 'admin-bots/rctf-ts'
#     options:
#       secretKey: beans
#       endpoint: 'http://admin-bot:21337'

# avatarsModeration:
#   provider:
#     name: 'moderation/openai'
#     options:
#         apiKey: 'key'

# globalSiteTag: 'G-1337'

# uploadProvider:
#   name: 'uploads/gcs'
#   options:
#     projectId: project-id
#     bucketName: bucket-name
#     credentials:
#       private_key: |-
#         key
#       client_email: [email protected]
Start the development server:
bun devFor frontend work, run
bun dev:mockto seed the database with a reproducible set of mock teams, challenges, and solves.
Explorar proyectos relacionados
trimstray/the-book-of-secret-knowledge
Una colección de listas inspiradoras, manuales, chuletas, blogs, trucos, comandos de una línea, herramientas de CLI y web, y más.
258,291 estrellasHack-with-Github/Awesome-Hacking
Una colección de diversas listas awesome para hackers, pentesters e investigadores de seguridad.
125,456 estrellasswisskyrepo/PayloadsAllTheThings
Una lista de payloads y métodos de bypass útiles para la seguridad de aplicaciones web y para pentesting/CTF.
82,661 estrellascaddyserver/caddy
Servidor web HTTP/1-2-3 rápido, extensible y multiplataforma con HTTPS automático
79,027 estrellas