
aquasecurity/trivy has 39,144 GitHub stars and 840 forks. GitHot measured +230 in 7 days, +433 in 15 days, and +830 in 30 days. Last checked 2026-11-09 08:23 UTC. Last push 2026-11-01.
Detecta vulnerabilidades, configuraciones incorrectas, secretos y SBOM en contenedores, Kubernetes, repositorios de código, la nube y más.
Crecimiento de estrellas medido
- in 24h
- Actualización retrasada
- in 7 days
- +230
- in 15 days
- +433
- in 1 month
- +830
Cambios netos en períodos que se solapan, no totales diarios. Los datos no disponibles se dejan en blanco. Las estrellas indican interés, no calidad.
README.md
Original


Trivy (pronunciation) is a comprehensive and versatile security scanner. Trivy has scanners that look for security issues, and targets where it can find those issues.
Targets (what Trivy can scan):
- Container Image
- Filesystem
- Git Repository (remote)
- Virtual Machine Image
- Kubernetes
Scanners (what Trivy can find there):
- OS packages and software dependencies in use (SBOM)
- Known vulnerabilities (CVEs)
- IaC issues and misconfigurations
- Sensitive information and secrets
- Software licenses
Trivy supports most popular programming languages, operating systems, and platforms. For a complete list, see the Scanning Coverage page.
To learn more, go to the Trivy homepage for feature highlights, or to the Documentation site for detailed information.
Quick Start
Get Trivy
Trivy is available in most common distribution channels. The full list of installation options is available in the Installation page. Here are a few popular examples:
brew install trivydocker run aquasec/trivy- Download binary from https://github.com/aquasecurity/trivy/releases/latest/
- See Installation for more
Trivy is integrated with many popular platforms and applications. The complete list of integrations is available in the Ecosystem page. Here are a few popular examples:
- GitHub Actions
- Kubernetes operator
- VS Code plugin
- See Ecosystem for more
Canary builds
There are canary builds (Docker Hub, GitHub, ECR images and binaries) generated with every push to the main branch.
Please be aware: canary builds might have critical bugs, so they are not recommended for use in production.
General usage
trivy <target> [--scanners <scanner1,scanner2>] <subject>
Examples:
trivy image python:3.4-alpine
trivy fs --scanners vuln,secret,misconfig myproject/
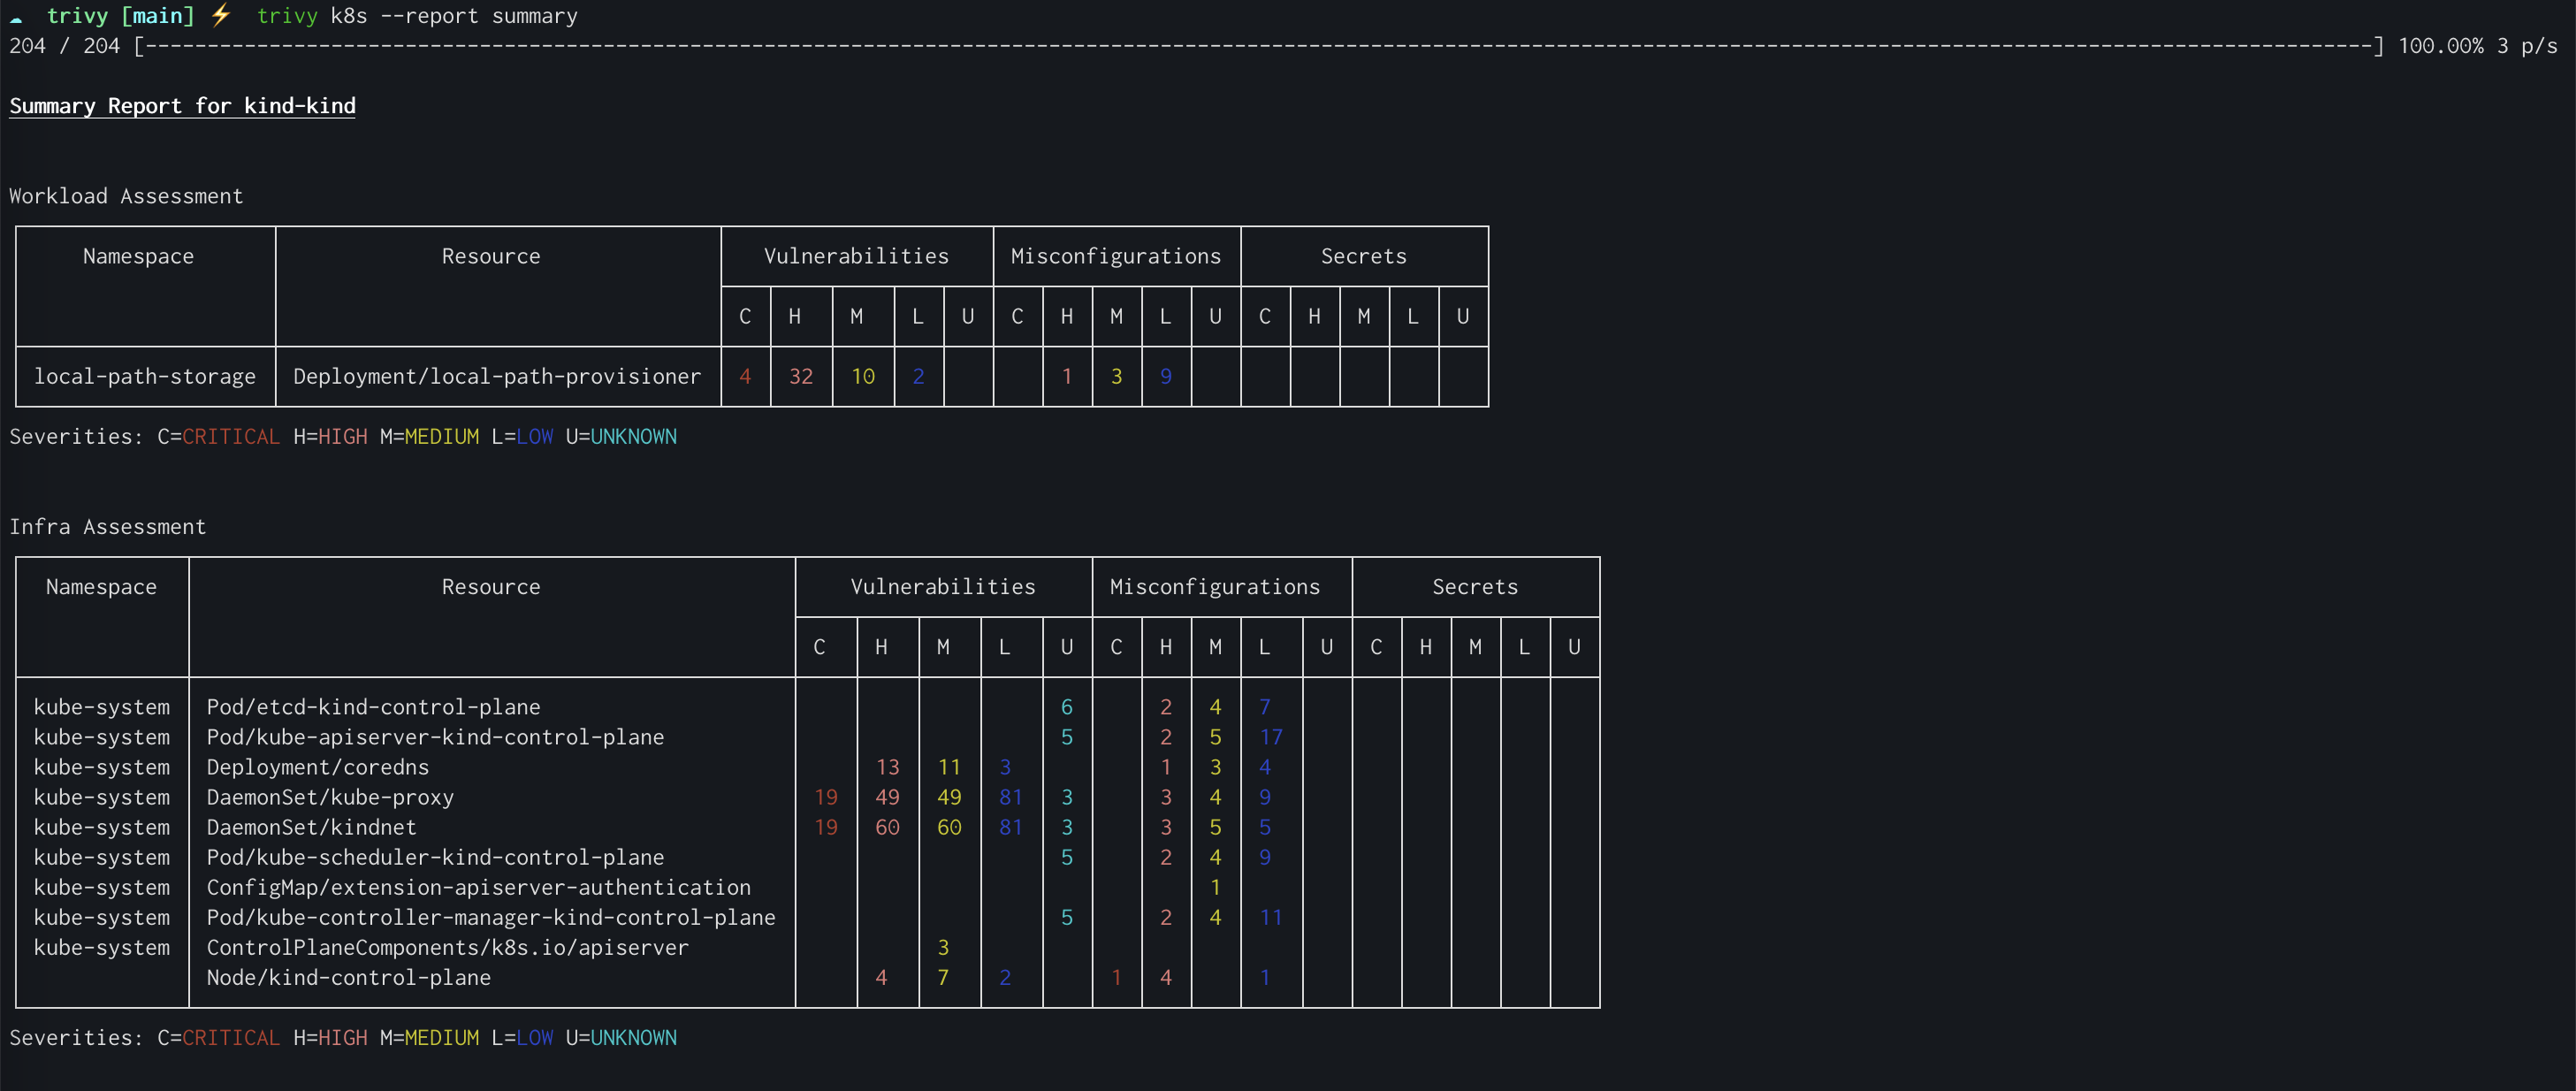
trivy k8s --report summary cluster
Result
FAQ
How to pronounce the name "Trivy"?
tri is pronounced like trigger, vy is pronounced like envy.
Want more? Check out Aqua
If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering.
You can find a high level comparison table specific to Trivy users here.
In addition check out the https://aquasec.com website for more information about our products and services.
If you'd like to contact Aqua or request a demo, please use this form: https://www.aquasec.com/demo
Community
Trivy is an Aqua Security open source project.
Learn about our open source work and portfolio here.
Contact us about any matter by opening a GitHub Discussion here
Please ensure to abide by our Code of Conduct during all interactions.
Explorar proyectos relacionados
trimstray/the-book-of-secret-knowledge
Una colección de listas inspiradoras, manuales, chuletas, blogs, trucos, comandos de una línea, herramientas de CLI y web, y más.
257,250 estrellasHack-with-Github/Awesome-Hacking
Una colección de diversas listas awesome para hackers, pentesters e investigadores de seguridad.
125,103 estrellasswisskyrepo/PayloadsAllTheThings
Una lista de payloads y métodos de bypass útiles para la seguridad de aplicaciones web y para pentesting/CTF.
82,542 estrellascaddyserver/caddy
Servidor web HTTP/1-2-3 rápido, extensible y multiplataforma con HTTPS automático
78,935 estrellas