
Trustpoint-Project/trustpoint
Trustpoint-Project/trustpoint has 45 GitHub stars and 11 forks. Star changes are not measured yet. Last checked 2026-11-11 06:07 UTC. Last push 2026-11-10.
The open source trust anchor software for machines and factories to manage digital identities
Crecimiento de estrellas medido
- in 24h
- Actualización retrasada
- in 7 days
- Actualización retrasada
- in 15 days
- Actualización retrasada
- in 1 month
- Actualización retrasada
Cambios netos en períodos que se solapan, no totales diarios. Los datos no disponibles se dejan en blanco. Las estrellas indican interés, no calidad.
README.md
Original
Trustpoint
Open-source machine identity management for industrial systems
Automate certificate onboarding, renewal, and lifecycle management for machines and industrial devices.
Trustpoint is an open-source PKI and machine identity platform built for operational technology (OT). It helps machine builders, operators, and integrators manage X.509 identities across long-lived, segmented, and heterogeneous industrial environments.
Get Started · Documentation · Latest Release · Website


Why Trustpoint?
Industrial systems increasingly depend on digital identities, but certificate management in OT is often still manual, fragmented, and difficult to automate.
Machines may remain in service for decades. Networks are segmented. Devices vary widely in capability. Existing IT-centric identity workflows do not always translate cleanly to the factory floor.
Trustpoint provides a unified, open platform for machine identity and certificate lifecycle management in OT.
| The challenge | With Trustpoint |
|---|---|
| Manual certificate provisioning | Automated onboarding, enrollment, renewal, and re-enrollment |
| Fragmented certificate silos | Centralized identity and certificate lifecycle management |
| Different device capabilities | Multiple enrollment protocols and authentication methods |
| Vendor-specific workflows | Open standards, APIs, and an open-source foundation |
| PKI complexity | Web-based workflows and abstractions for industrial users |
| Long-lived devices | Lifecycle-oriented certificate management and renewal automation |
Trustpoint is designed to help you:
- Onboard machines securely using zero-touch, semi-automated, or operator-driven workflows.
- Automate certificate lifecycles from initial enrollment through renewal, rekeying, and revocation.
- Integrate with existing PKI by operating as a Certificate Authority (CA) or Registration Authority (RA).
- Use open protocols including EST, CMP, and OPC UA GDS Push.
- Automate industrial workflows through REST APIs, agents, webhooks, and approval steps.
- Protect cryptographic keys with PKCS#11-compatible HSM integration.
- Avoid vendor lock-in through interoperable protocols and an MIT-licensed open-source codebase.
Quickstart
Deploy Trustpoint with Docker Compose on a Linux host. The web setup wizard configures the application.
Prerequisites
- Docker 20.10+
- Docker Compose 2.32.4+
- Git and Python 3
Start Trustpoint
[!IMPORTANT] Trustpoint 1.0.0 is the first stable version. Start with a fresh database and installation-specific secrets. Preserve the database, keys, and runtime state for subsequent updates and recovery. See the 1.0 release notes and upgrade guide.
git clone https://github.com/Trustpoint-Project/trustpoint.git
cd trustpoint
cp .env.example .env
# Set database credentials and TLS names in .env.
sudo python3 docker/init_secret.py --type all
docker compose up -d --build
The one-time initializer creates an installation-specific Django signing key and
an independent software database key-encryption key (KEK). Preserve
secrets/django_secret_key, secrets/trustpoint_software_kek, .env, and all
deployment volumes when updating a compatible 1.0 installation. A database backup
alone cannot recover encrypted credentials. PKCS#11 installations instead need
their original HSM KEK/token, provider configuration, and authentication material;
SoftHSM also needs its token/configuration volumes and original PIN files.
Then open:
http://localhost
The initial setup wizard generates a TLS certificate.
[!NOTE] You find the default initial credentials in the Docker logs.
Want the full setup flow? See the Quickstart Setup Guide.
What can Trustpoint do?
Machine identity lifecycle
Trustpoint manages digital identities and X.509 certificates across the device lifecycle:
Device / Machine
      │
      ▼
  Onboarding
      │
      ▼
Initial Device Identity
      │
      ▼
Application Certificates
      │
      ├──► Renewal / Rekeying
      │
      ├──► Revocation
      │
      └──► Decommissioning
Enrollment and onboarding protocols
| Method | Typical use | Authentication / trust | Lifecycle capabilities |
|---|---|---|---|
| AOKI (proof of concept) | Zero-touch industrial device onboarding | IDevID / DevOwnerID based trust | Initial device onboarding and identity establishment |
| EST | Standards-based certificate enrollment | Username/password, IDevID, client certificate | Onboarding, application certificates, renewal, re-enrollment |
| CMP | Flexible enrollment for industrial or constrained devices | Shared secret, IDevID, client certificate | Onboarding, enrollment, renewal, rekeying |
| SCEP | Certificate enrollment for industrial and other devices | Per-device challengePassword for initial enrollment, client certificate for renewal | Application certificate enrollment and renewal |
| OPC UA GDS Push | OPC UA certificate and trust-list distribution | Secure device registration and certificate authentication | Server certificate and trust-anchor distribution, cyclic updates |
| Manual / remote download | Operator-driven or browser-assisted issuance | Operator workflow / one-time password | PKCS#12 or PEM credential delivery |
Learn more:
- AOKI — Automated Onboarding Key Infrastructure
- EST API documentation
- CMP API documentation
- SCEP API documentation
- OPC UA GDS Push specification
Core capabilities
Automated certificate management
- Certificate enrollment and issuance
- Renewal and re-enrollment
- Rekeying
- Certificate revocation
- Cyclic CRL generation
- JSON-based certificate profiles
- Certificate discovery
Trustpoint Agents
Trustpoint Agents automate certificate lifecycle workflows on or near industrial devices.
Agents can:
- automate enrollment and renewal,
- communicate with Trustpoint using mTLS,
- execute reusable deployment workflows,
- deploy renewed certificates to target systems, and
- integrate with operational monitoring through structured logs.
See the Trustpoint Agents documentation.
PKI integration
Trustpoint supports multiple operating models:
Certificate Authority mode
- Import an existing issuing CA
- Create an auto-generated CA for testing
- Provide CA certificates to devices through EST or CMP
- Support CA rollover workflows
Registration Authority mode
- Forward EST enrollment requests to an external CA
- Integrate Trustpoint workflows with an existing PKI
HSM and key protection
Trustpoint supports PKCS#11-based HSM integration for cryptographic key storage and operations.
For local development, Trustpoint can use a dedicated SoftHSM container through the setup wizard.
APIs and headless integration
Trustpoint provides REST APIs for machine identity and certificate workflows, including:
- certificate enrollment,
- device and identity lifecycle operations,
- onboarding configuration,
- workflow definitions, and
- system integration.
This makes it possible to integrate Trustpoint into automation pipelines, MES/ERP systems, IAM processes, or custom industrial applications.
Workflow engine
The workflow engine supports industrial processes that require more than a simple certificate request:
- manual approval steps,
- reusable workflow definitions,
- webhook integrations,
- email notifications, and
- agent-driven certificate deployment.
Operations and observability
Trustpoint includes:
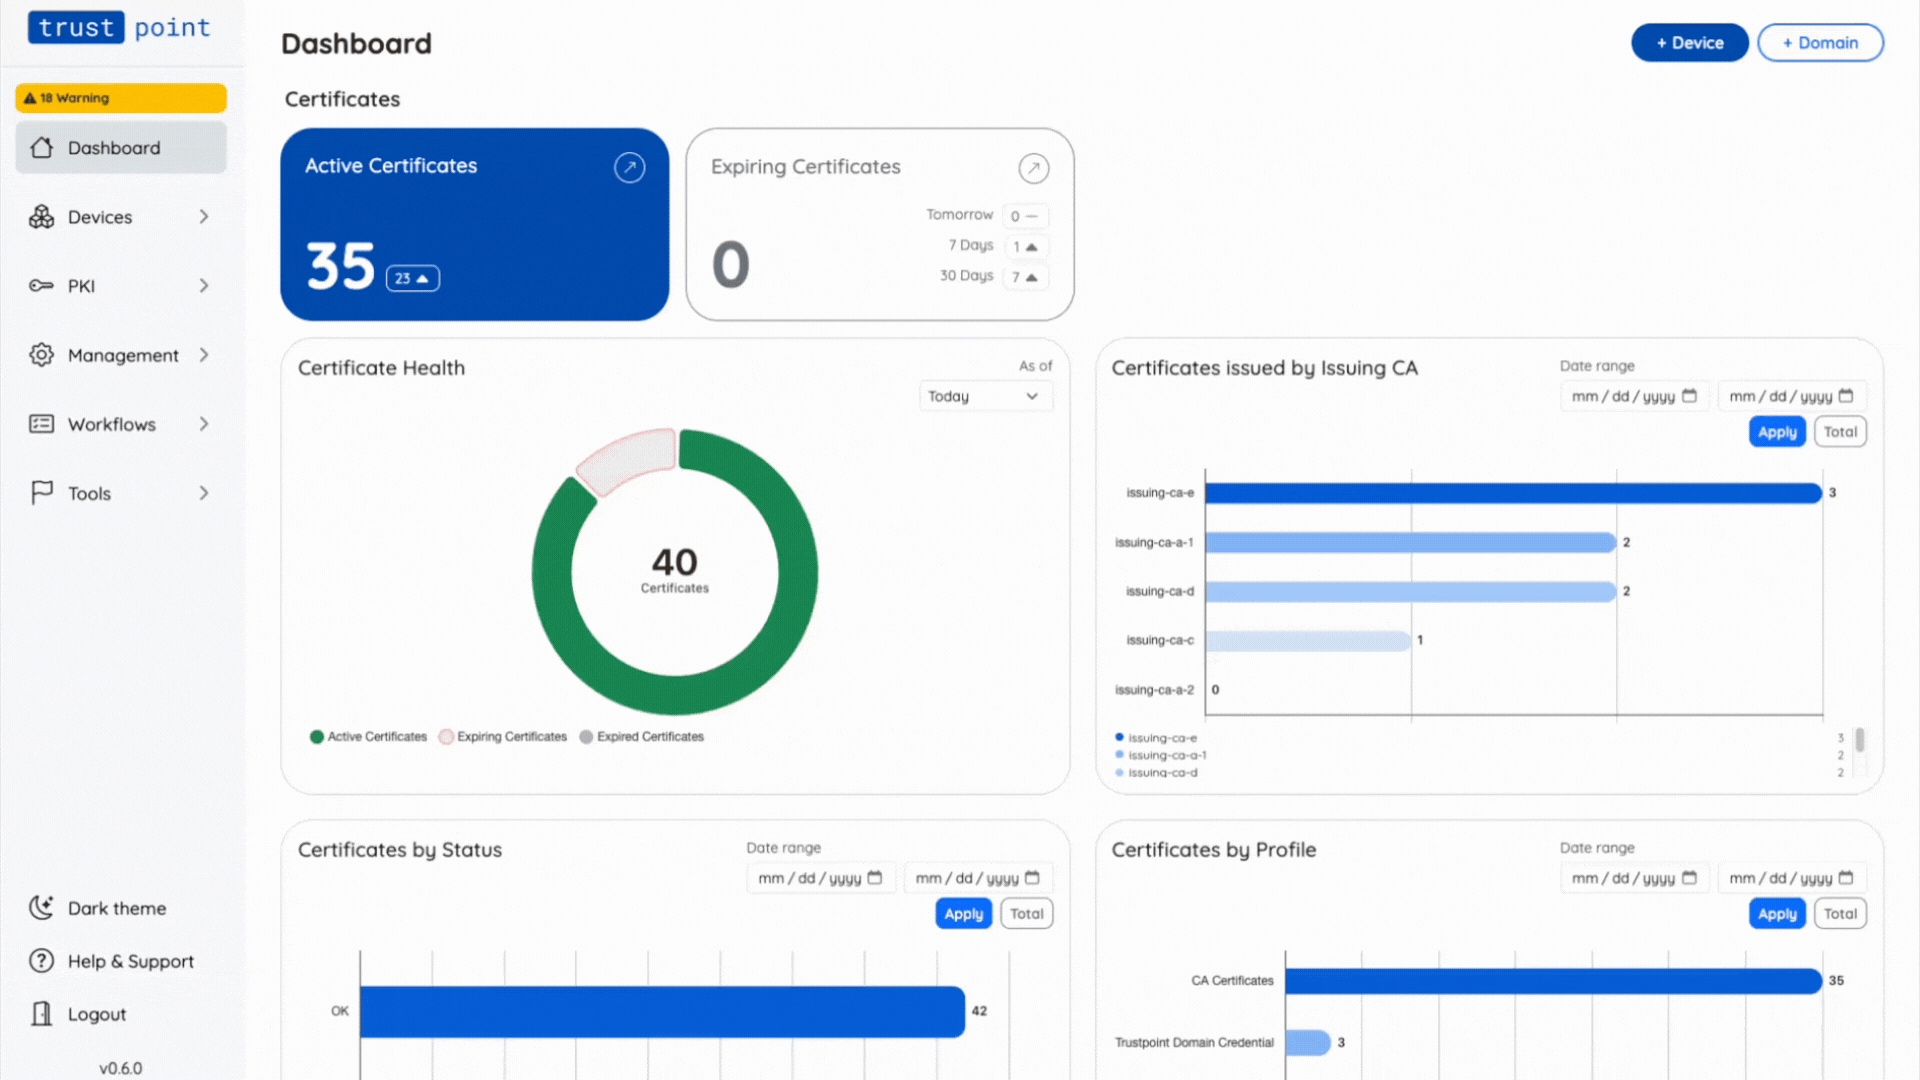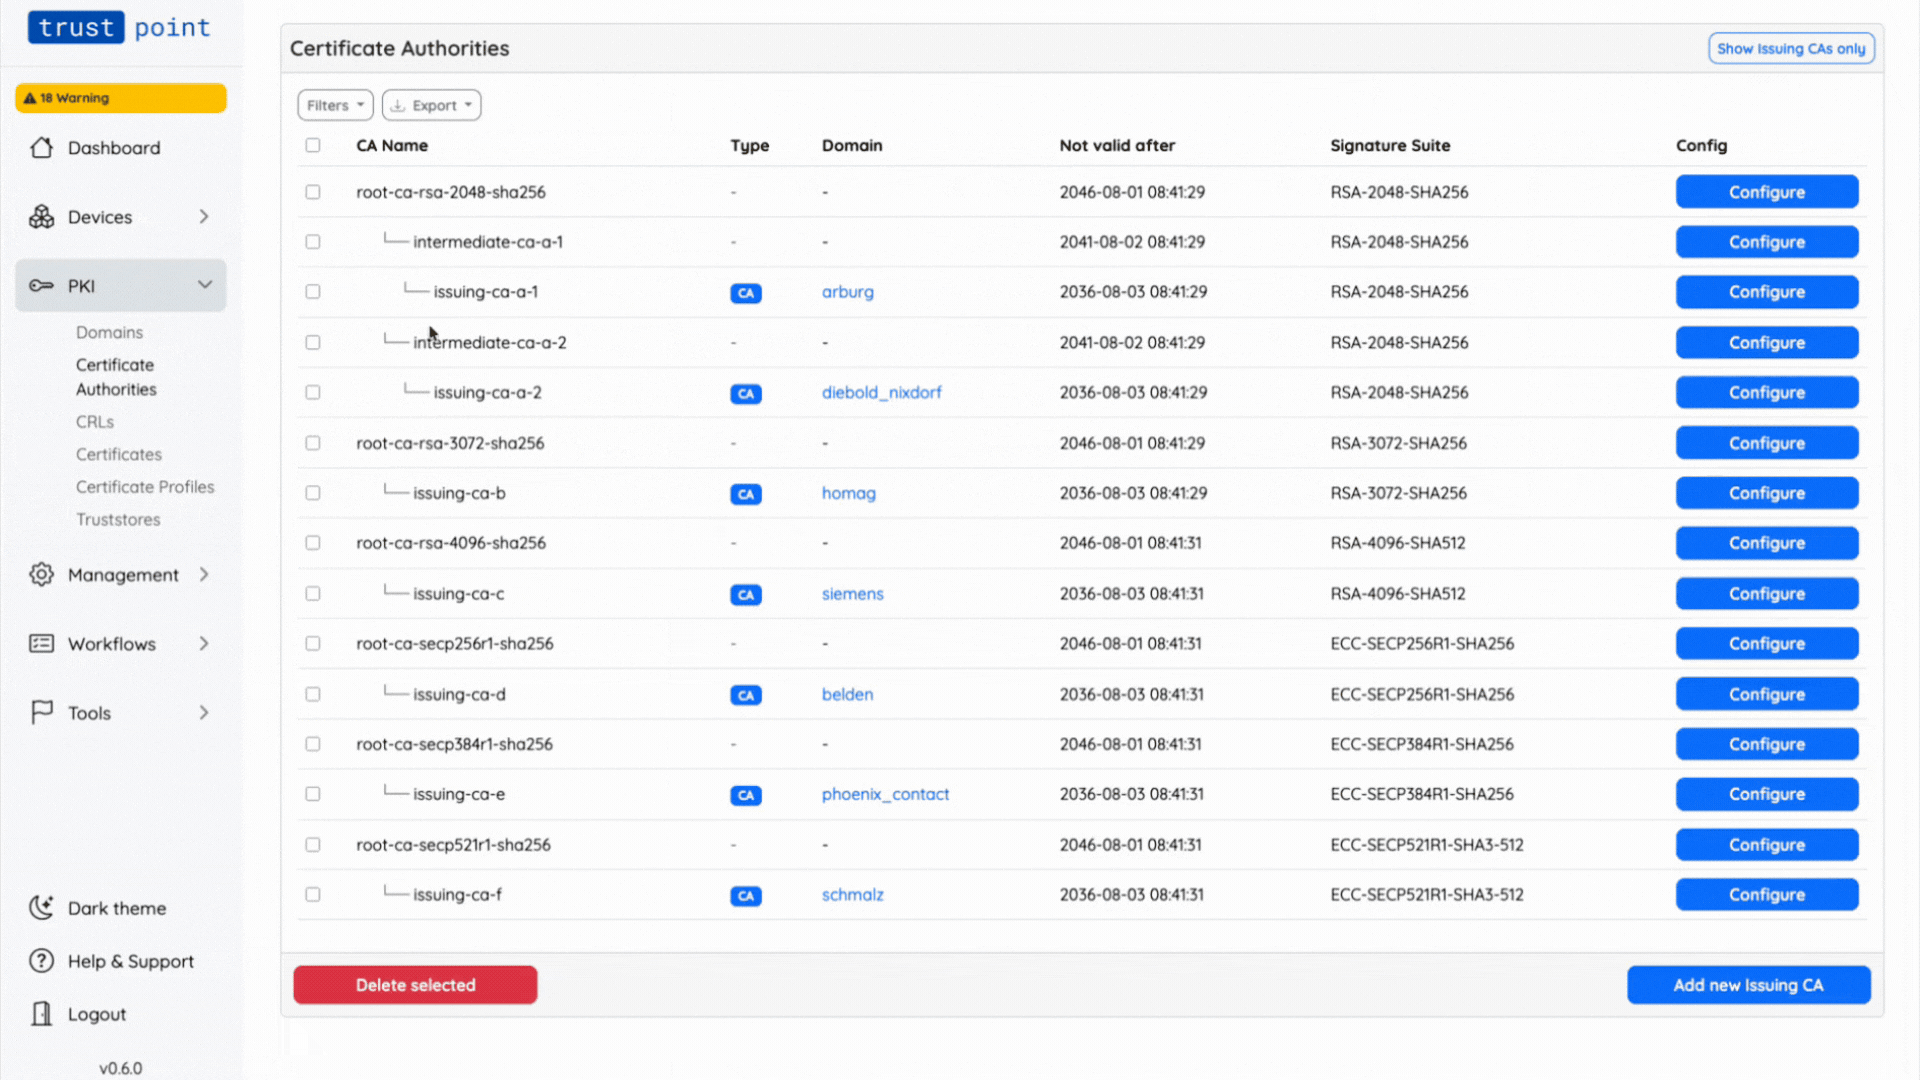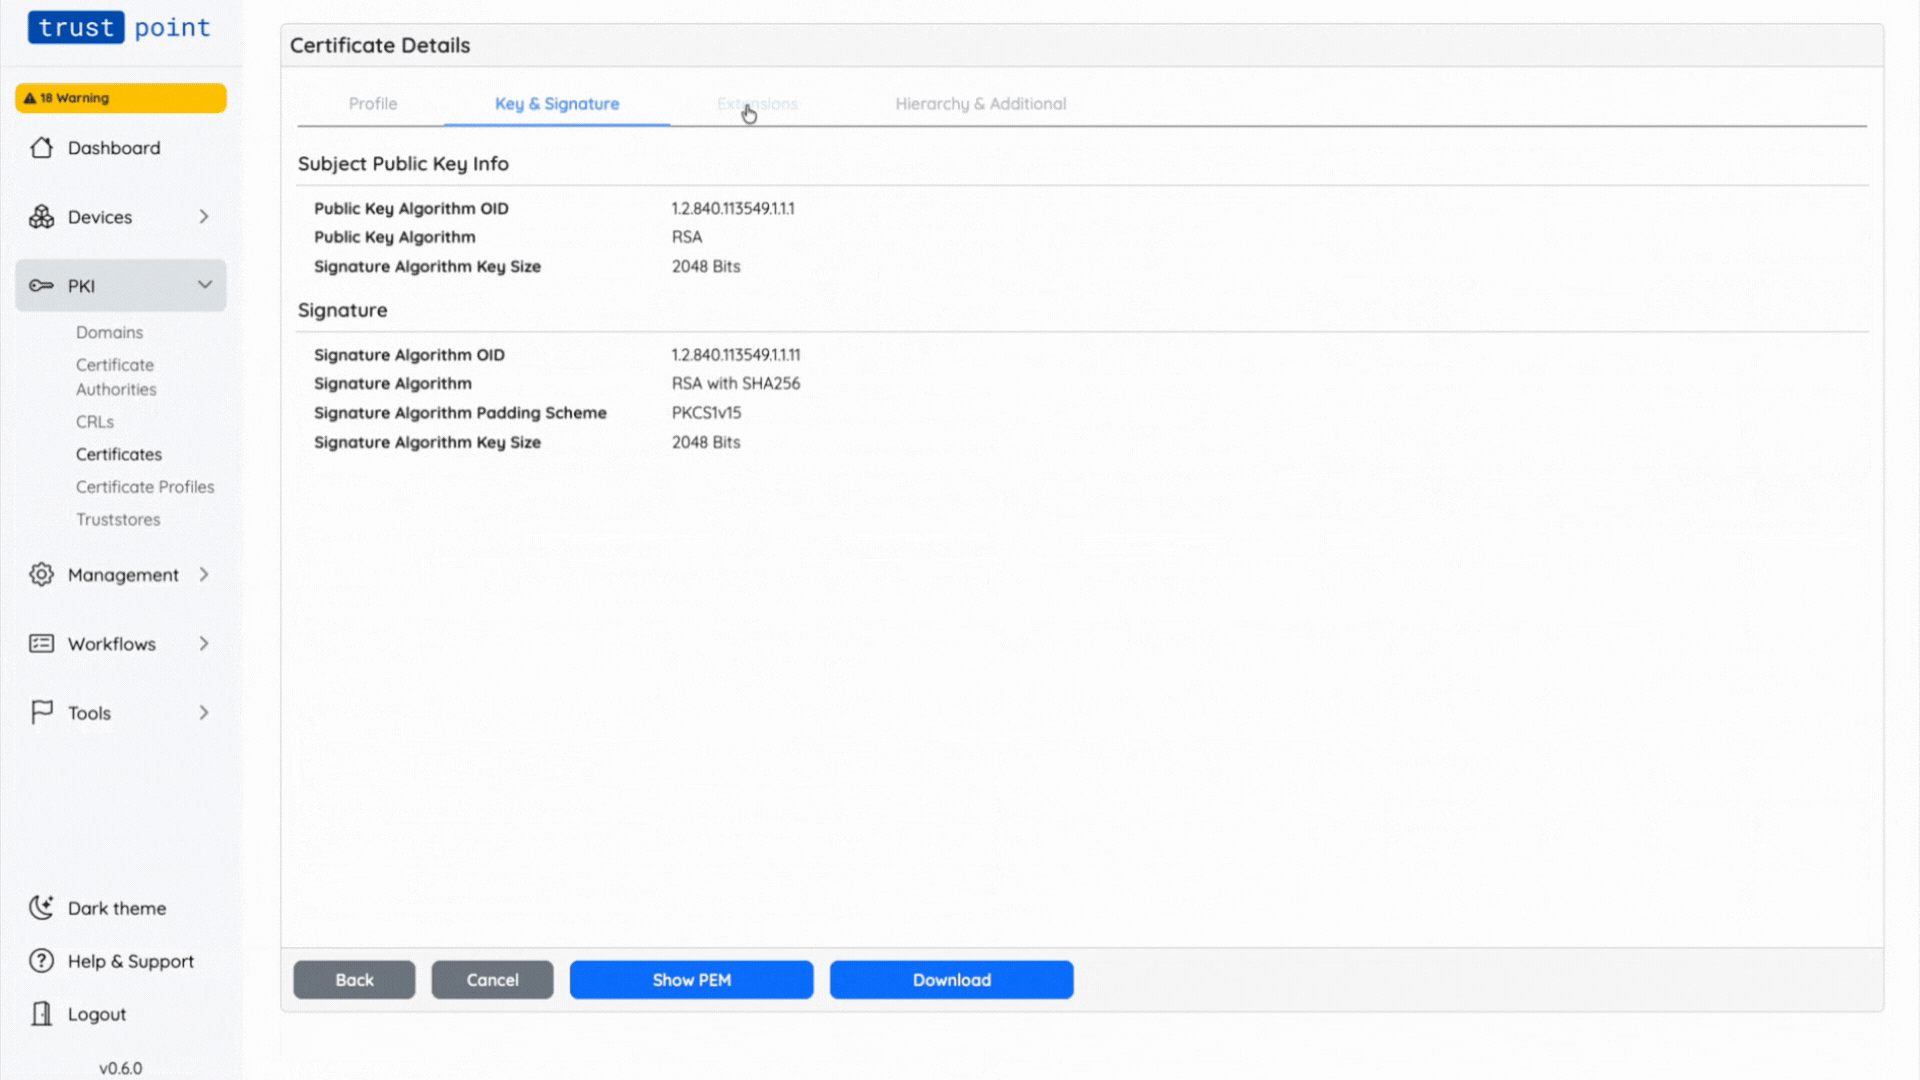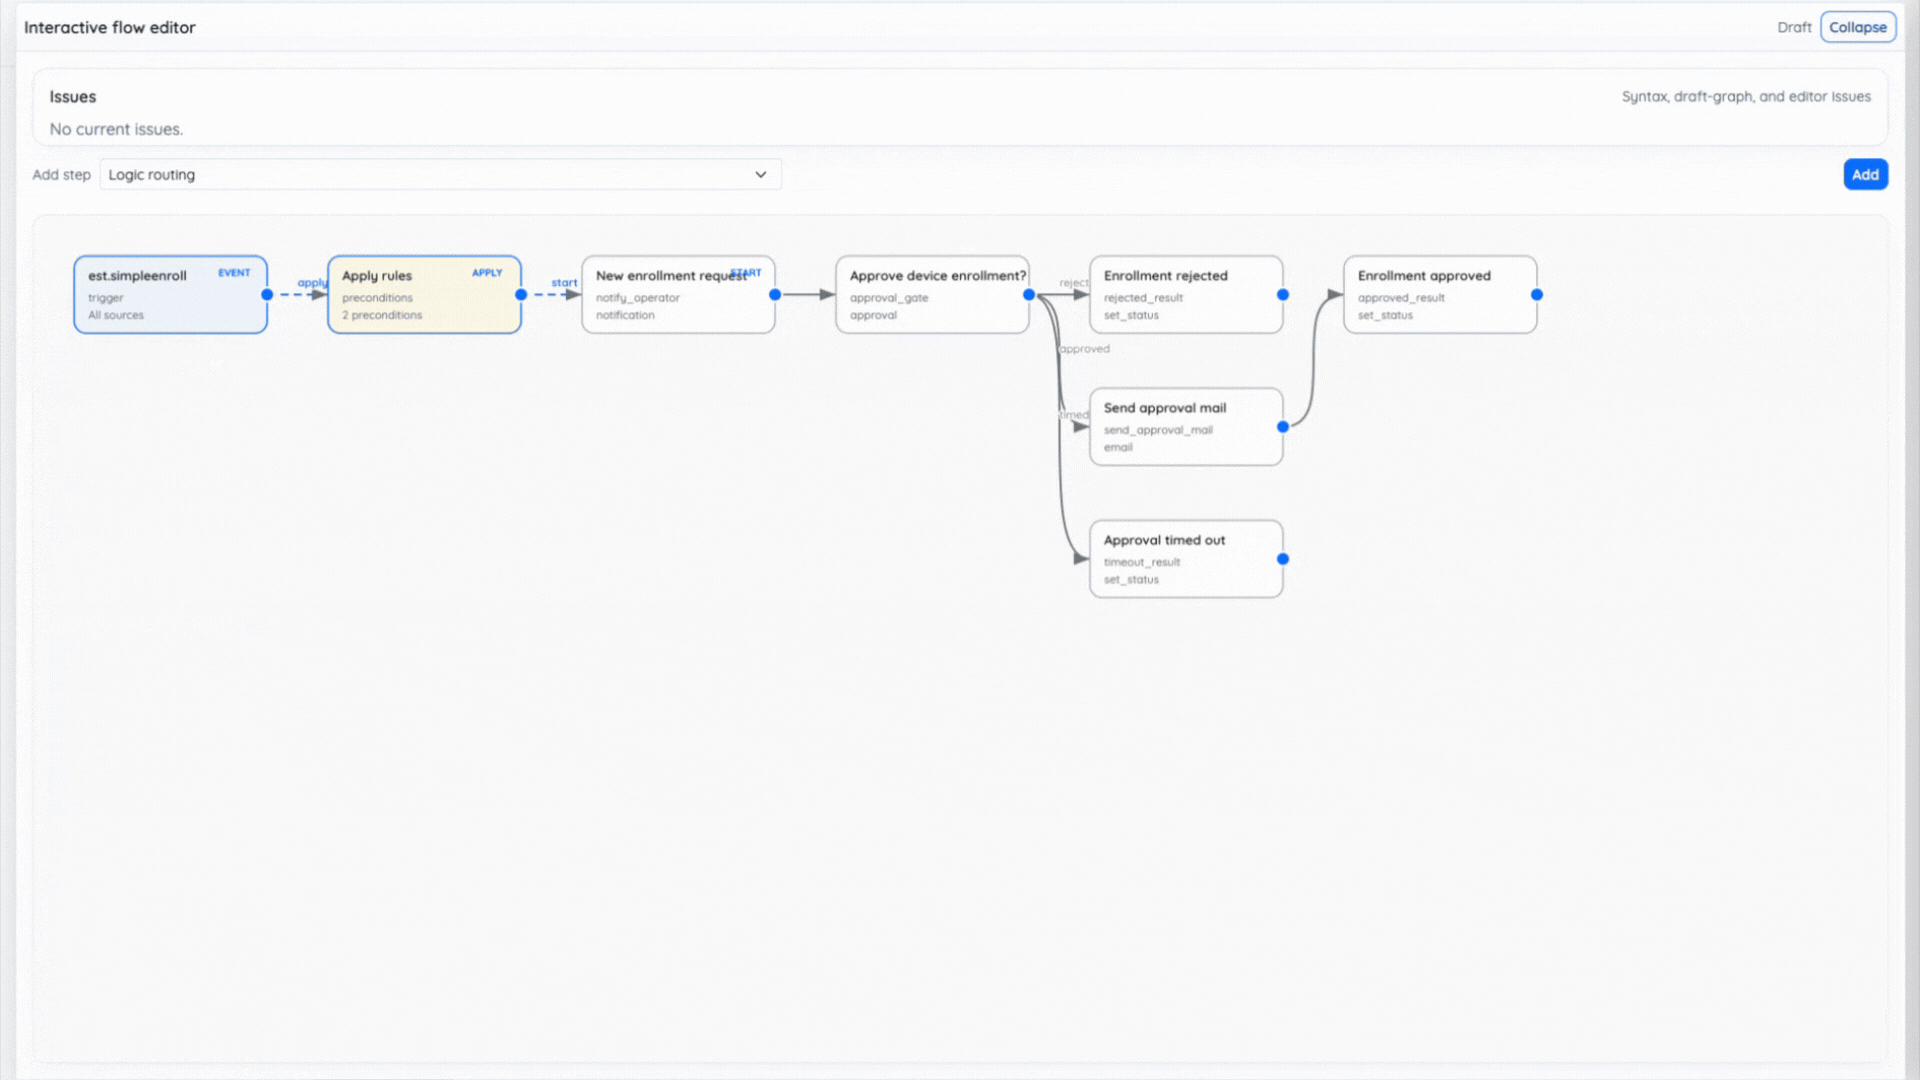
- web-based management UI,
- dashboards,
- audit logging,
- users, roles, and organizations,
- Prometheus metrics,
- mDNS-based local service discovery,
- Docker-based deployment, and
- multi-language support.
Built for industrial environments
Trustpoint focuses on the realities of operational technology:
- long machine and device lifecycles,
- segmented or locally connected networks,
- mixed generations of equipment,
- limited device resources,
- different levels of automation,
- existing enterprise PKI infrastructure, and
- the need to introduce machine identities without coupling them to a single vendor.
The goal is to make strong machine identities practical across brownfield and greenfield industrial environments.
Security and compliance engineering
Security is a core part of the project.
The repository includes:
- a Security Policy,
- OpenSSF Best Practices tracking,
- automated testing and static analysis,
- HSM integration,
- audit logging, and
- documentation related to the EU Cyber Resilience Act, including a CRA Conformity Assessment, Threat Model, Risk Register, and Security Controls.
See the Trustpoint documentation for the current security architecture and CRA-related material.
Documentation
| Resource | Description |
|---|---|
| Documentation | Complete Trustpoint documentation |
| Quickstart Setup | Install and start Trustpoint |
| Quickstart Operation | Explore Trustpoint and issue a first certificate |
| Trustpoint Agents | Automated certificate lifecycle management |
| AOKI | Zero-touch device onboarding |
| Docker Hub | Published Trustpoint container images |
| Releases | Release notes and project milestones |
Trustpoint 1.0.0
Trustpoint 1.0.0 is the first stable release. The release notes describe its capabilities, installation, key-recovery requirements, and known limitations. See the capability and limitations guide for available operations and backend-specific deployment requirements.
See GitHub Releases for published version notes.
Development
Contributions are welcome.
Start with:
If you are new to the project, check the current issues and discussions.
Community and support
Have a question, idea, use case, or integration proposal?
- Join the Trustpoint Discord
- Contact us at [email protected]
- Visit industrial-security.io
We are especially interested in feedback from machine builders, factory operators, system integrators, PKI teams, security researchers, and developers working on industrial identity.
License
Trustpoint is licensed under the MIT License.
Building machine identity infrastructure for the open industrial ecosystem.
If Trustpoint is useful to your work, star the repository to help other industrial security developers discover it.
Explorar proyectos relacionados
trimstray/the-book-of-secret-knowledge
Una colección de listas inspiradoras, manuales, chuletas, blogs, trucos, comandos de una línea, herramientas de CLI y web, y más.
257,833 estrellasHack-with-Github/Awesome-Hacking
Una colección de diversas listas awesome para hackers, pentesters e investigadores de seguridad.
125,254 estrellasswisskyrepo/PayloadsAllTheThings
Una lista de payloads y métodos de bypass útiles para la seguridad de aplicaciones web y para pentesting/CTF.
82,583 estrellascaddyserver/caddy
Servidor web HTTP/1-2-3 rápido, extensible y multiplataforma con HTTPS automático
78,959 estrellas