
GeoSpoof/geospoof
GeoSpoof/geospoof has 368 GitHub stars and 17 forks. GitHot measured +2 stars in 24 hours and +11 in 7 days. Last checked 2026-11-22 08:03 UTC. Last push 2026-11-18.
Gemessener Sternzuwachs
- in 24h
- +2
- in 7 days
- +11
- in 15 days
- Verlauf wird gesammelt
- in 1 month
- Verlauf wird gesammelt
Nettoänderungen in überlappenden Zeiträumen, keine Tagessummen. Fehlende Messwerte bleiben leer. Sterne zeigen Interesse, nicht Qualität.
Über uns
Browser extension and iOS app that spoofs your gps, geolocation & timezone, and auto-syncs to your VPN. Firefox, Chrome, Edge, Brave & Safari.
SicherheitREADME.md
Original
GeoSpoof
Your VPN changes your IP address. Your device is still telling websites where you actually are.



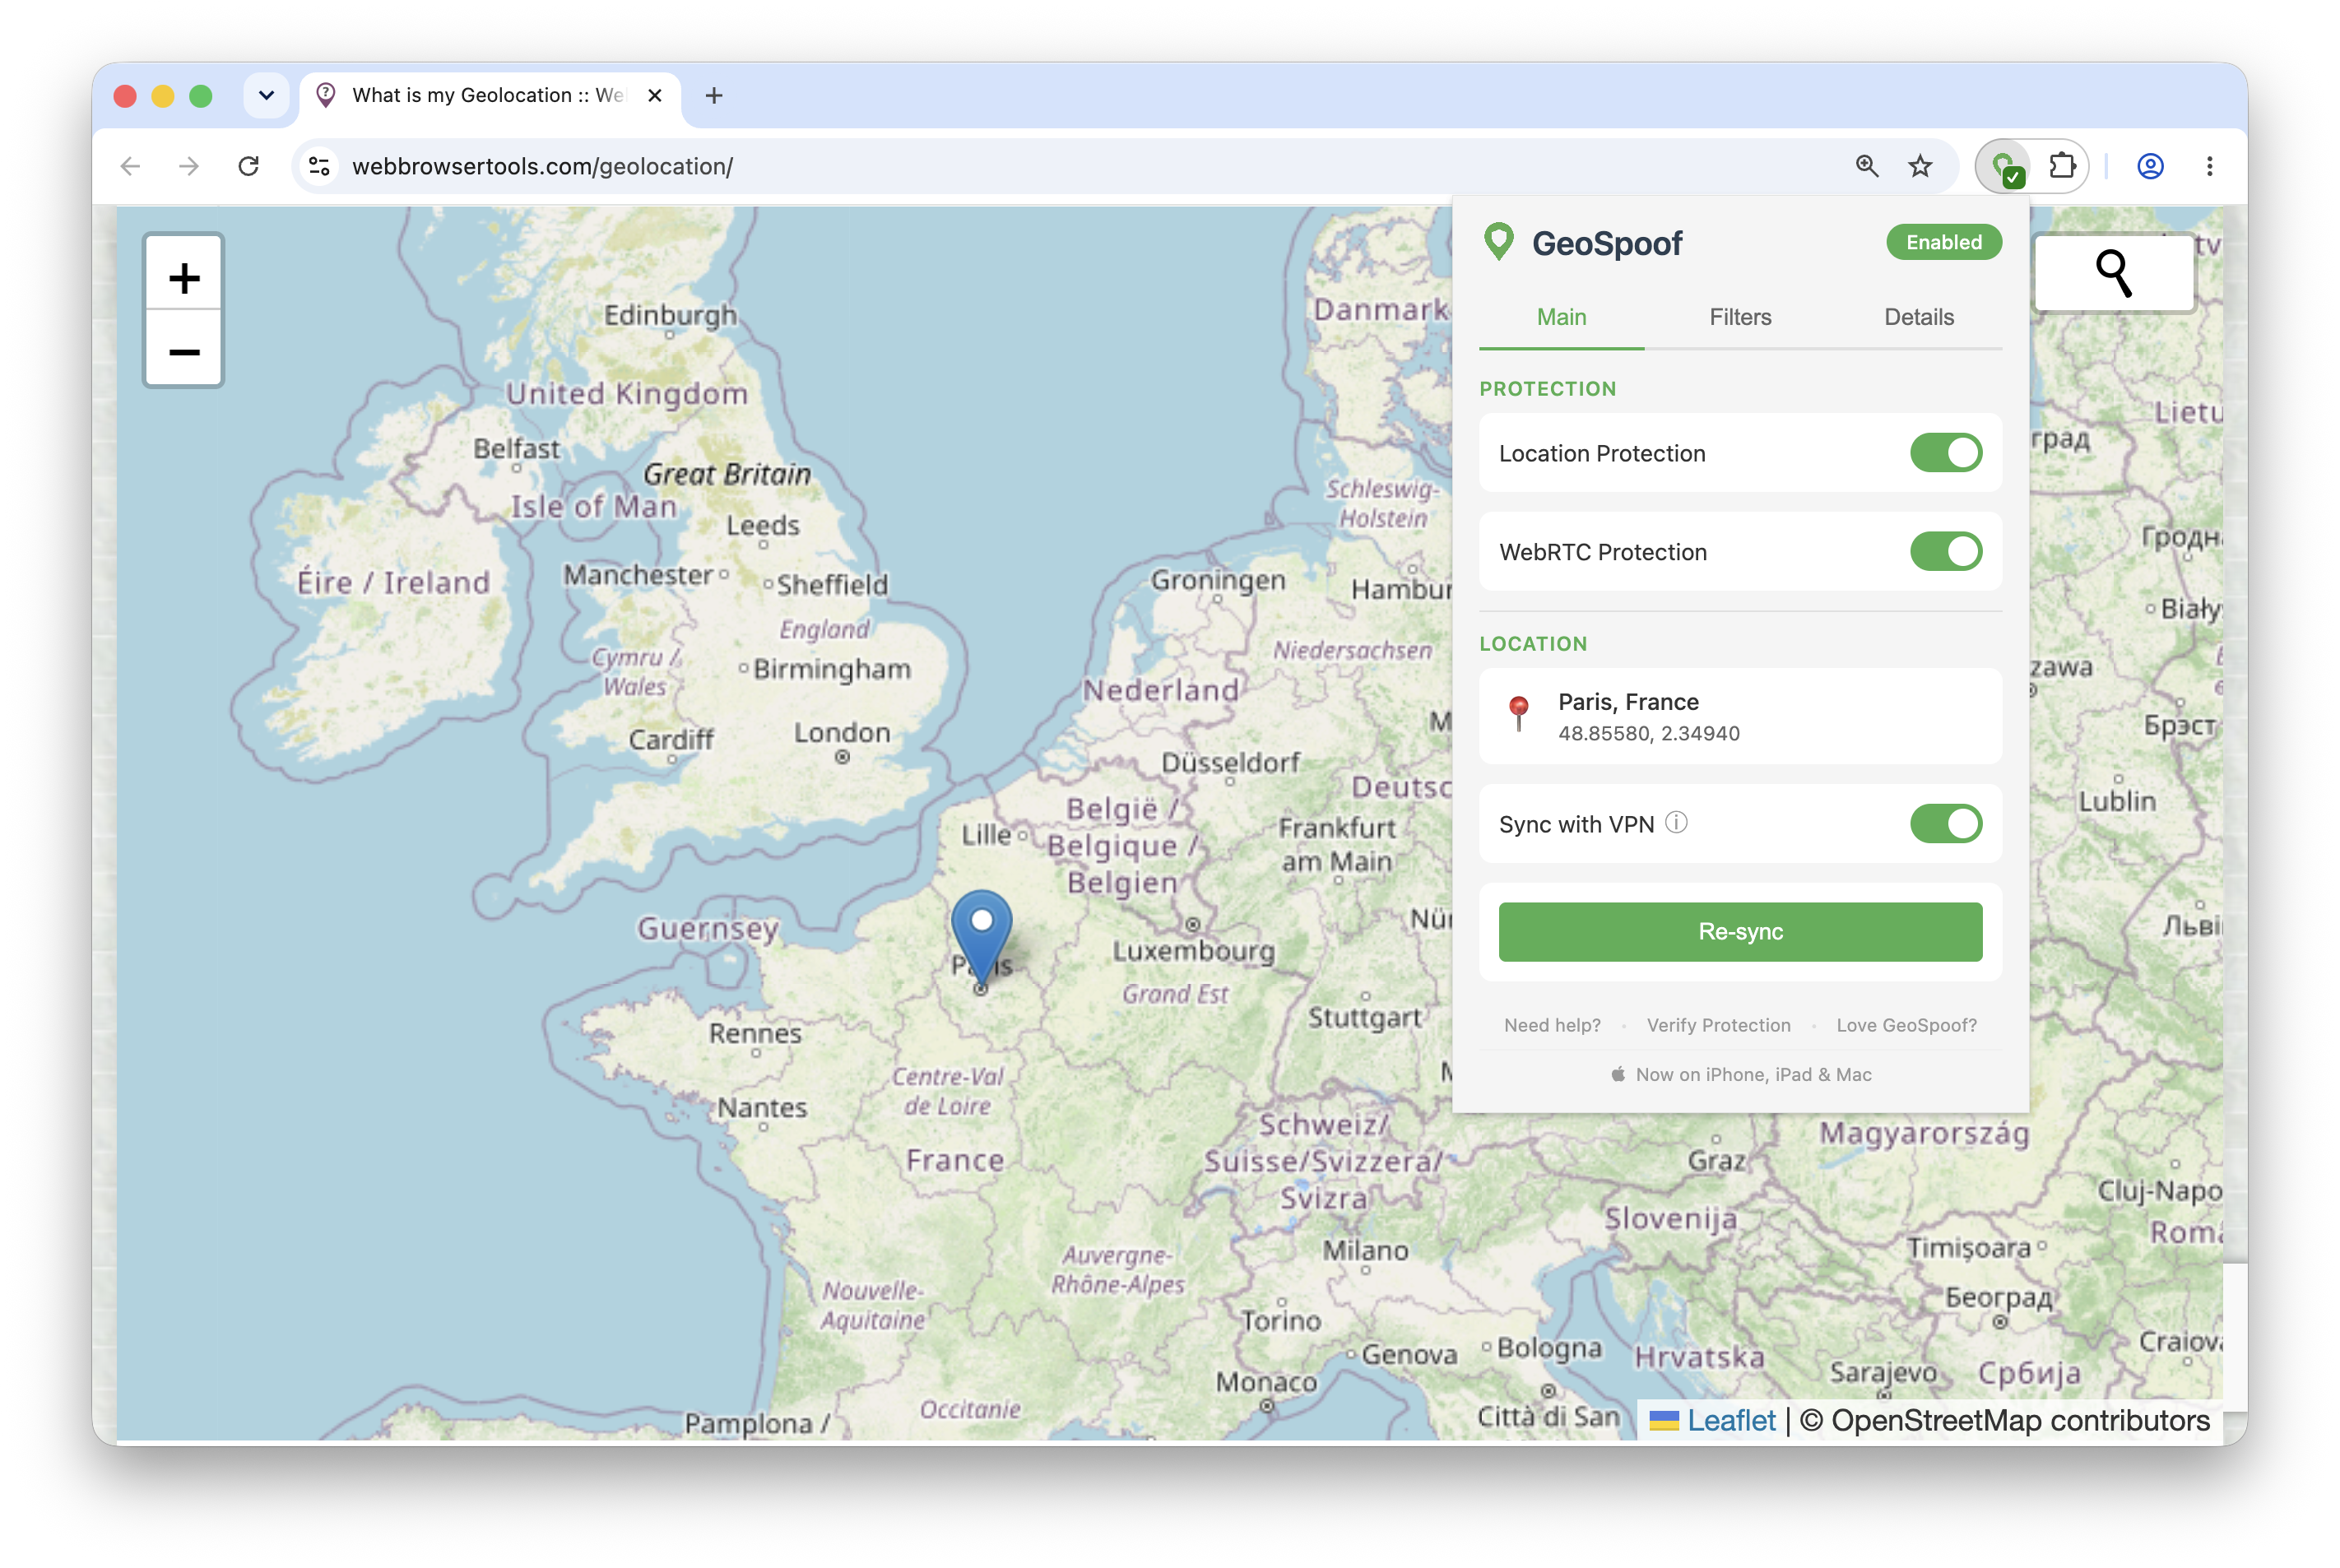
GeoSpoof now comes in two parts:
- Browser extension (free & open source) — stops websites from geolocating you by overriding the Geolocation API, timezone,
Intl, WebRTC, and every other signal, so your browser reports a location you choose. Firefox, Chrome, and Safari. - GeoSpoof GPS — moves your iPhone or iPad's real, system-level GPS to the location you pick, so location-aware apps across the whole device match it, not just the browser.
Contents
- Getting started — Install · Usage
- Why GeoSpoof? — What it does NOT do
- Reported Language — opt-in language & locale alignment
- GeoSpoof GPS — device-level location on iPhone & iPad
- Overridden APIs
- External Services
- Featured in
- Development
Getting started
Install
| Browser | Store | Works on |
|---|---|---|
 |
Firefox Add-ons | Firefox 140+ on desktop and Android |
 |
Chrome Web Store | Chrome, Brave, Edge, Opera, and other Chromium browsers |
 |
App Store | Safari on iOS, iPadOS, and macOS |
 |
GitHub Releases | Firefox self-hosted signed XPI — setup below |
Safari setup — enabling after install
After installing on Safari, tap the puzzle piece icon (or go to Safari Settings → Extensions) and enable GeoSpoof for the sites you want to protect. On iOS/iPadOS, you can also enable it per-site from the AA menu in the address bar.
Other install paths — self-hosted XPI, from source
From GitHub Releases (Firefox self-hosted)
Each release includes a self-hosted signed XPI alongside the AMO submission. The self-hosted XPI uses a 4-segment version (e.g., 1.18.0.42) to avoid collisions with the AMO listing.
- Go to the Releases page
- Download
geospoof-firefox-v<version>-signed.xpifrom the latest release - In Firefox, open
about:addons - Click the gear icon (⚙) and select Install Add-on From File…
- Select the downloaded
.xpifile
The signed XPI works on standard Firefox with no extra configuration. Once installed, Firefox automatically checks for and installs new versions via the self-hosted update manifest. If you later install from AMO, Firefox will auto-upgrade to it since AMO releases use a higher base version.
Note: An unsigned
geospoof-firefox-v<version>-unsigned.xpiis also included in each release for Firefox forks that don't support AMO signatures. Most users should use the signed version.
From source
See CONTRIBUTING.md for build instructions.
Usage
- Click the GeoSpoof icon in your toolbar
- Search for a city, enter coordinates manually, or use "Sync with VPN" to auto-detect your VPN exit region
- Enable "Location Protection", "WebRTC Protection", and "Sync with VPN" features
- Refresh open tabs to apply
- Confirm it's working at geospoof.com/verify
See docs/USER_GUIDE.md for details.
Why GeoSpoof?
A VPN changes your IP, but your browser still leaks your real location through the Geolocation API, timezone offsets, Intl.DateTimeFormat, WebRTC, and more. Sites cross-reference these signals against your IP — when they don't match, you're flagged.
GeoSpoof overrides every one of those channels so your browser reports a consistent, chosen location instead of your real one. Set it to match your VPN, mismatch it on purpose, or pick anywhere in the world.
- VPN Region Sync — detects your VPN exit IP and sets your location to match. One click, and it re-syncs automatically as you switch exit servers.
- Manual control — search for a city or enter coordinates directly.
- Full signal alignment — geolocation, timezone, Date APIs, Intl, Temporal, and WebRTC all report the same place.
- Reported Language (opt-in) — optionally report a language to match, so
navigator.language, everyIntlformat, and theAccept-Languageheader agree instead of announcing where you actually come from. - Per-site locations — give specific sites their own location (say,
twitch.tvin one place andchatgpt.comin another) while every other site keeps your main location, if you've set one. Set it under Per-site locations at the bottom of the popup's Sites tab. Free on Firefox and Chrome; part of GeoSpoof Pro on Safari. See the User Guide. - Site groups in the Allowlist and Denylist — add a whole service or region in one entry (Google, Netflix, OpenAI, "Sites outside China", about 1,500 v2fly
geositelists), an exact address (=mail.example.com), or your own proxy list from a link. Use them in the Allowlist, the Denylist or per-site locations; a more specific entry beats a broader one. Matched on your device and kept up to date weekly. Free on Firefox and Chrome; part of GeoSpoof Pro in Safari and the GeoSpoof app, like the rest of Filters there. See Site groups. - Anti-fingerprinting — overrides are disguised to pass native code checks used by real-world fingerprinting scripts.
- Cross-browser — Firefox, Chrome, Brave, Edge, and Safari. Single codebase, MV3.
Note: Use of this tool may violate the Terms of Service of certain websites. Use responsibly.
What This Does NOT Do
GeoSpoof is designed to work alongside a VPN, not replace one.
- Does NOT spoof your IP address (use a VPN for that)
- Does NOT change your browser's language by default — that's opt-in (see Reported Language), and it does NOT change GeoSpoof's own interface language
- Does NOT bypass server-side detection (IP, payment info, account history)
- Does NOT give a site a different IP, account region, or legal residence through per-site locations — it changes only what that site's pages read from your browser
- Does NOT track your browsing activity, collect telemetry, or store data on external servers. Some features (city search, VPN sync) call third-party APIs to function. See the Privacy Policy for exactly what's sent and to whom.
- Does NOT provide forensic-level anti-fingerprinting. Engine-level API tampering is also detectable by dedicated tools. For extreme threat models, use Tor Browser or Mullvad Browser instead.
Reported Language (opt-in)
Your VPN and your spoofed location can say Paris while your browser still says navigator.language === "en-US" and sends Accept-Language: en-US with every request. Reported Language closes that gap.
Turn it on in Settings (the ⚙ gear in the popup header) → Reported Language and pick either:
- Match my location — use the dominant language of the place you're already spoofing, resolved offline from your spoofed timezone.
- Choose language… — name any language tag your browser supports, like
fr-FR,ja, orpt-BR. The field suggests common ones as you type but accepts any valid tag.
It's off by default, because it visibly changes browsing: many sites will switch language outright.
When it's on, these move together:
navigator.languageandnavigator.languages, in the page and inside Workers- The default locale of every
Intlconstructor, plus eachresolvedOptions() toLocaleStringonDate/Number/BigInt/Array,localeCompare, and locale-sensitive case mapping- The
Accept-Languagerequest header
They move together on purpose. A browser claiming fr-FR in script while sending Accept-Language: en-US is obviously tampered with — a stronger fingerprint than not spoofing at all — so both surfaces are derived from one resolver and can't disagree. Formats aren't faked either: the chosen locale is handed to the browser's own Intl engine, so separators, month names, collation order, and hour cycle are genuinely correct for the language you report.
Limits, stated plainly:
- Locale entropy outside an extension's reach is not covered: installed fonts, text-rendering metrics, and
speechSynthesisvoice lists still reflect your real system. - What's advertised is shaped per engine to match what that browser natively sends — Firefox and Chromium expose the tag plus a bare-language fallback with different quality values, and Safari exposes a single language — so the output doesn't look like a different browser's.
- The
Accept-Languageheader is rewritten on Firefox and Chromium. On Safari it depends on the engine honoringdeclarativeNetRequestheader modification, which has historically been unreliable; where it doesn't, coverage degrades to the JavaScript surfaces only. - If you pick a language your browser has no data for, GeoSpoof reports your real one rather than half-applying the change — the control tells you when that happens.
This is separate from the Language setting further down the same panel, which only changes GeoSpoof's own interface language and is never sent to websites.
GeoSpoof GPS (device-level location)
The browser extension keeps your browser private. GeoSpoof GPS goes a level deeper: it moves your iPhone or iPad's real, system-level GPS to the location you choose, so location-aware apps across the whole device match it — not just Safari.
- Whole-device, not just the browser — sets the OS-level location every app reads, driven from a companion app for Mac.
- Secure one-time pairing — set up from your Mac over a secure pairing. No jailbreak.
- Fully reversible — reverts to your real GPS the moment you turn it off.
- Private by design — same no-account, no-tracking stance as the extension. Built for privacy and for testing location-based features; not designed for AR games.
GeoSpoof GPS is an optional Pro feature — browser and Safari spoofing stay free. It ships as a signed, notarized macOS app.
Download it at geospoof.com/gps.
GeoSpoof GPS is a separate, closed-source product and is not part of this repository — this repo is the open-source browser extension. See the Privacy Policy for exactly what each surface sends and to whom.
Overridden APIs
When protection is enabled, GeoSpoof overrides browser APIs synchronously at document_start before any page JavaScript runs. Covered APIs include:
- Geolocation —
navigator.geolocation.getCurrentPosition/watchPosition,navigator.permissions.query - Date & Timezone —
Dateconstructor,Date.parse, allDate.prototypegetters and formatters,getTimezoneOffset - Intl —
Intl.DateTimeFormatconstructor andresolvedOptions - Temporal —
Temporal.Now.*(feature-detected) - XSLT / EXSLT —
XSLTProcessor.prototype.transformToFragment/transformToDocumentrewrite EXSLTdate:date-time()output (Firefox, where available) - Workers —
Worker,SharedWorker, andnavigator.serviceWorker.registerwrapped to propagate the spoofed timezone into worker scopes (URL-based worker coverage is the FirefoxwebRequest.filterResponseDatapath; inline/blob workers are covered on every engine) - WebRTC — via browser privacy API, no script injection needed
- Locale (opt-in, see Reported Language) —
navigator.language,navigator.languages, the default locale of everyIntlconstructor (DateTimeFormat,NumberFormat,Collator,RelativeTimeFormat,ListFormat,PluralRules,DisplayNames,Segmenter,DurationFormat) plus theirresolvedOptions(),toLocaleStringonDate/Number/BigInt/Array,String.prototype.localeCompare/toLocaleUpperCase/toLocaleLowerCase, and theAccept-Languagerequest header - Anti-fingerprinting —
Function.prototype.toStringreturns[native code]for all overrides; iframes patched on insertion - Engine-level Spoofing (Chrome/Chromium, opt-in) — an optional mode that also sets the timezone in the browser engine through the Chrome DevTools Protocol (
chrome.debugger→Emulation.setTimezoneOverride), keeping the page-world injection as the fallback. It covers the URL and module workers in the page's process (and, measured on CreepJS, its service worker), narrowing the worker timezone leak the content-script path can't close on Chromium MV3. In a tab it already holds, a page runs its first script with the spoofed zone when that zone is the same as the previous page's; a tab's first page still runs its first scripts with the real zone, and a page reached from one with a different zone runs them with that zone (Known Limitations 3 and 15 indocs/API.md). Cross-origin iframes running in their own process use the injected timezone and, on Chrome 125+, get the engine zone through a child debugger session for the workers they start (their own first script can still read the real zone), anddocument.lastModifiedfollows the spoofed zone (seedocs/API.mdfor what it still doesn't cover). Off by default; while on, Chrome shows a "started debugging this browser" notice. Geolocation stays on the injected path.
For the full API reference, see docs/API.md. For the VPN sync and auto-resync architecture, see docs/VPN_SYNC.md.
External Services
The extension runs no backend application and sends no data to the developer for collection or analytics. Some features — city search and the optional "Sync with VPN" — make requests directly from your device to third-party services. Timezone resolution downloads boundary data from the developer's own CDN (cdn.geospoof.com, hosted on AWS), which transmits your IP as part of that request. The developer does not use these requests for analytics, tracking, profiling, advertising, or user accounts, and stores no personal data from them. Exactly what is sent, when, and to whom (for both the Safari extension and the companion apps) is documented in the Privacy Policy.
The website, geospoof.com, does run a backend. It receives Apple's App Store purchase notifications, keeps a running tally of them, and posts a daily sales summary. Those purchase records come from Apple, not from the extension or the apps, and the Privacy Policy describes what they contain and how long they're kept.
Featured in
- Privacy Guides community forum — "GeoSpoof: a Firefox add-on for convenient geolocation privacy"
- Korben — "GeoSpoof - Le VPN cache votre IP mais le navigateur vous trahit" (FR)
Development
See CONTRIBUTING.md for setup, scripts, testing, and the release pipeline.
Legal
Using location spoofing may violate terms of service of streaming, financial, or e-commerce platforms. You are responsible for compliance. See PRIVACY_POLICY.md for full details.
License
Everything in this repository (the browser extension, its docs, and its assets) is licensed under the Apache License 2.0. See LICENSE and NOTICE. Use, modify, and redistribute freely, including commercially. Keep the NOTICE file and mark files you change.
Releases up to and including v2.2.3 were MIT-licensed, and copies obtained under those terms keep them.
Three GeoSpoof products are developed separately, are not part of this repository, and are proprietary (all rights reserved by GeoSpoof LLC):
- The native iOS and macOS apps. These previously lived in a
safari/directory here, MIT-licensed until 2026-09-13. That history remains, taggedpre-safari-extraction. - The geospoof.com website, including its marketing copy, translations, and imagery. This previously lived in a
site/directory here; that history remains, taggedpre-site-extraction. - The GeoSpoof GPS desktop core (the Rust/Swift device product).
In each case, copies obtained under MIT before the directory was removed keep those rights. Nothing here revokes a grant already made.
Trademarks: GeoSpoof™ is a trademark of GeoSpoof LLC. The license covers the code, not the brand; Section 6 of Apache 2.0 says so explicitly. You're free to fork the code, but don't brand a fork or derivative product as "GeoSpoof" in a way that could confuse users about its source.
Links
- Website — geospoof.com
- GeoSpoof GPS — geospoof.com/gps
- Verify your protection — geospoof.com/verify
- Community — r/GeoSpoof
- User Guide
- API Documentation
- VPN Sync & Auto-Resync
- How Browsers Track Location
- Privacy Policy
- Contributing
- Report Issues
- Buy me a coffee
Star History
Acknowledgments
- Nominatim for geocoding
- browser-geo-tz for timezone boundary-data lookup
- BrowserLeaks for testing tools
- arkenfox TZP for timezone/geolocation fingerprint testing
- CreepJS for fingerprint testing
- webbrowsertools for testing tools
Contributors
Thanks to everyone who has contributed to GeoSpoof.
Ähnliche Projekte entdecken
Wird geladen…